
AWR
Let your AI team keep complex projects moving—from goal to verified delivery.
The open-source project delivery platform for people and AI.
Website · Documentation · 简体中文 · Release notes
AWR connects goals, workstreams, dependencies, context and acceptance into one project delivery workflow. Keep the project's intent, constraints and verified progress when you change sessions or agents. People set direction and review outcomes; agents work through the same project using CLI or MCP.
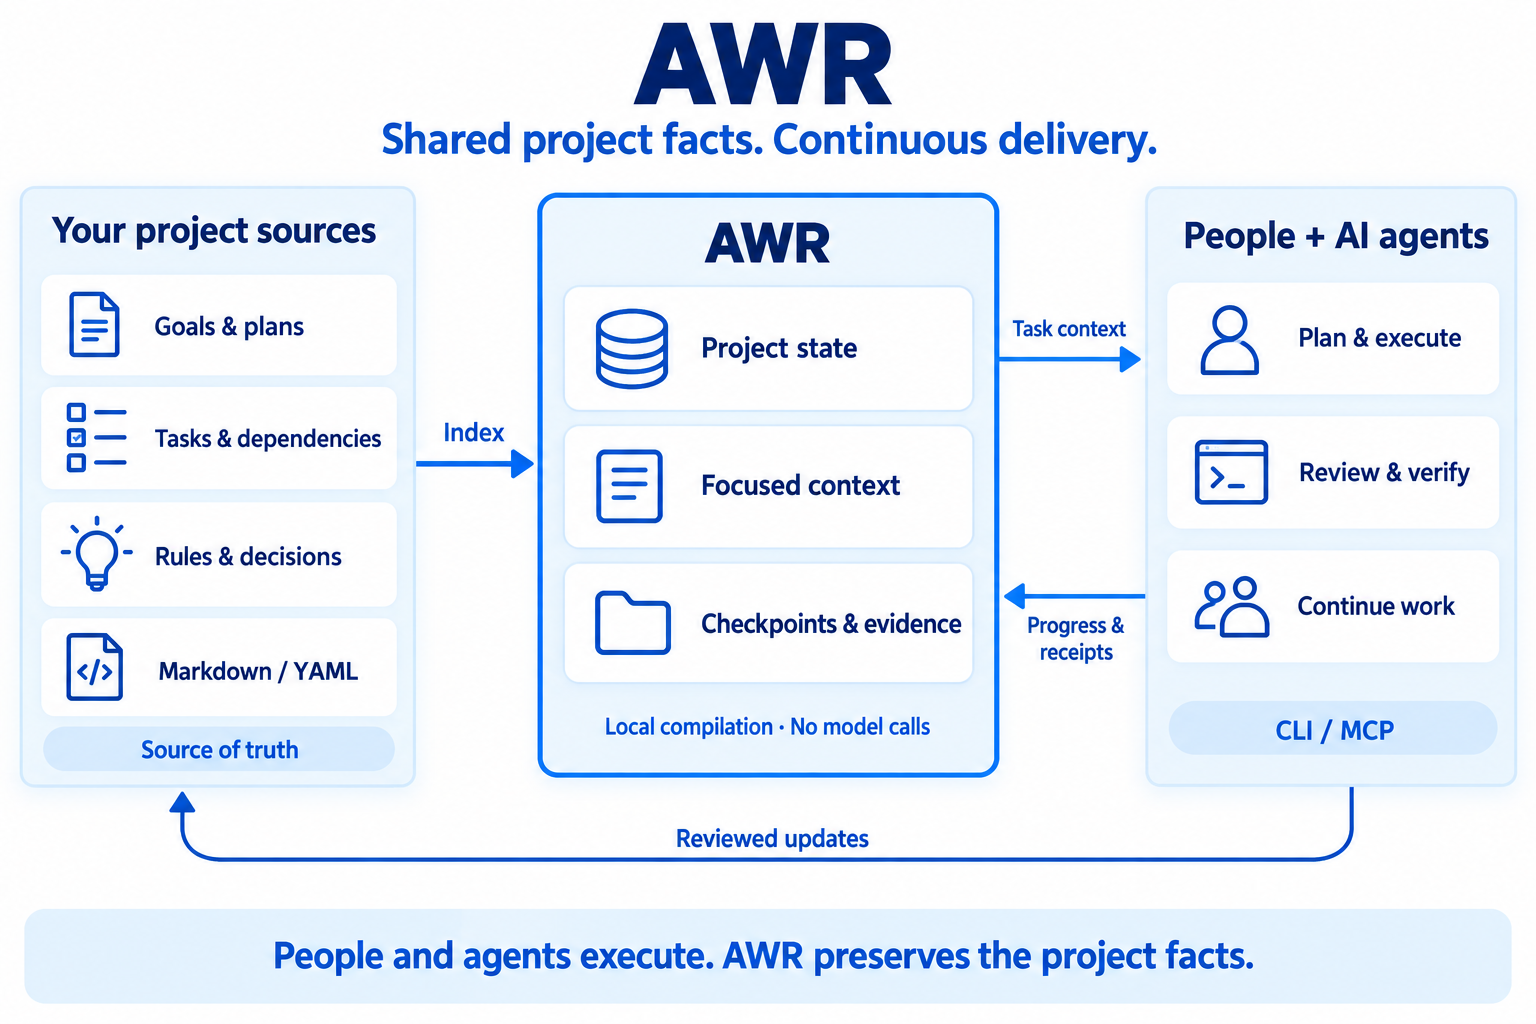
What 0.5.1 provides
This package installs the native Rust awr CLI and awr-mcp server for
personal, local SQLite projects. No model call is needed to compile context.
- Continue across sessions. Keep goals, rules, decisions, claims and checkpoints connected to the current work.
- Use the context that matters. Compile task-specific project context within a budget while retaining required facts and exposing missing dependencies.
- Keep progress honest. Distinguish source status, checkpoint observations and version-bound verification evidence; retain caller attribution.
- Check source freshness consistently. Build a shared file inventory that
ignores
.DS_Storeand other supported metadata, and records real file changes. - Organize personal workstreams. Explicit source ownership, session attribution and scoped context form the foundation for parallel work.
- Use your existing agent. CLI, stdio MCP and a shared HTTP MCP service connect supported clients and projects; optional lifecycle adapters deepen integration.
The optional Inspector runs from source and is not bundled in npm/PyPI. This release's source includes Chinese/English views, complete queue pagination and session/event panels.
Team/PG collaboration, advanced delivery adoption, DEC extensions, usage and ETA accounting are outside 0.5.1. The personal workstream foundation is not a claim of complete authenticated Team isolation. See the workstream guide for the supported boundaries.
Install with pip
Requires Python 3.9+. Use a virtual environment:
python -m venv .venv
# Activate .venv using your shell's standard command, then:
python -m pip install agent-work-runtime==0.5.1
awr --version
awr-mcp --version
For an isolated application installation, use
pipx install agent-work-runtime==0.5.1 or
uv tool install agent-work-runtime==0.5.1.
Wheels embed both native binaries; Rust is not needed for installation. Python provides launchers rather than a separate Python SDK. Source identity, binary hashes and third-party license notices travel with the native payload.
Connect a project
From your project directory, preview initialization and review the proposed sources before accepting the same goal:
awr init --goal "Deliver a customer portal with verified sign-in"
awr init --goal "Deliver a customer portal with verified sign-in" --accept
awr status
awr intake inspect
Existing Markdown/YAML sources remain authoritative. If intake reports
NeedsOrganization, fill in the required goal, work and acceptance information
before implementation. See the project intake guide.
Give your agent this working agreement:
Use AWR to carry this project from its goal to verified delivery. Read the current goals, rules, dependencies and checkpoint before starting. Keep clear acceptance criteria and ownership. Record actual progress and evidence, and save a checkpoint before stopping so the next session can continue.
Connect through MCP
After initialization, add this entry using your client's supported MCP configuration format and your project's absolute path:
{
  "mcpServers": {
    "awr": {
      "command": "awr-mcp",
      "args": ["--project", "/absolute/path/to/your/project"]
    }
  }
}
Reconnect the client and verify the project identity. For multiple clients and projects, see the shared HTTP MCP service guide. CLI/MCP is the common entry point for Codex, Cursor, Claude Code and other compatible agents. Host hooks are optional and require their own activation; a saved configuration does not prove a checkpoint was executed.
Supported systems and upgrades
Prebuilt packages support macOS 15+ (Apple Silicon and Intel), Linux x64/arm64 with glibc 2.39+, and Windows x64. SQLite is bundled; Git-bound operations also need Git. Other platforms require a separately verified source build. See the distribution guide.
Upgrading from 0.5.0: stop writers and retain matching program, runtime and source snapshots first. Explicit source refresh upgrades SQLite schema 4 through 5 and 6 to 7, preserving legacy identities and history. Old binaries refuse schema 7. A rollback requires the matching pre-upgrade snapshot, not just a package downgrade; keep any post-upgrade history separately.
Learn more
- Session and checkpoint workflow
- CLI/MCP response contract
- Source freshness inventory
- Content review
- Contributing · Report an issue
Licensed under Apache-2.0.
1 maintainer

Release files for agent-work-runtime 0.5.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| agent_work_runtime-0.5.1-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| agent_work_runtime-0.5.1-py3-none-manylinux_2_39_x86_64.whl | Python 3 | none | Linux glibc 2.39+ x86-64 | Details |
| agent_work_runtime-0.5.1-py3-none-manylinux_2_39_aarch64.whl | Python 3 | none | Linux glibc 2.39+ ARM64 | Details |
| agent_work_runtime-0.5.1-py3-none-macosx_15_0_x86_64.whl | Python 3 | none | macOS 15.0+ x86-64 | Details |
| agent_work_runtime-0.5.1-py3-none-macosx_15_0_arm64.whl | Python 3 | none | macOS 15.0+ ARM64 | Details |
Total release size: 106.8 MB
Release files / agent_work_runtime-0.5.1-py3-none-win_amd64.whl
| Download URL | agent_work_runtime-0.5.1-py3-none-win_amd64.whl |
|---|---|
| Size | 20.2 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
a3be0fe5f29b9925887f3efdd7dec15cc183bfd67575667de739f04b71f73618
|
|
BLAKE2b-256 checksum How to use checksums |
ba30fb32526e4a1aa56c5694bad934800ec4c00590d7084a85e3923b31abc291
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / agent_work_runtime-0.5.1-py3-none-manylinux_2_39_x86_64.whl
| Download URL | agent_work_runtime-0.5.1-py3-none-manylinux_2_39_x86_64.whl |
|---|---|
| Size | 22.5 MB |
| Tags | Linux glibc 2.39+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
38134e5dab53c5f531ec94f3522316c7a3d3090f0a4ec9c3f13bdb924948d54f
|
|
BLAKE2b-256 checksum How to use checksums |
f49c804b532e8894314b8af79304a54327dec0756fc9d58f82ec5dcd5bb2c7c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / agent_work_runtime-0.5.1-py3-none-manylinux_2_39_aarch64.whl
| Download URL | agent_work_runtime-0.5.1-py3-none-manylinux_2_39_aarch64.whl |
|---|---|
| Size | 21.8 MB |
| Tags | Linux glibc 2.39+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
6742b8e5d3acba075148bf5441b5fda5df63d866d70f6d39880158903ffa565b
|
|
BLAKE2b-256 checksum How to use checksums |
7bde8d8d8be06ef1c0ee52f9f9465cfb64e2d2f374616a9d37f7a8e5bb717c4b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / agent_work_runtime-0.5.1-py3-none-macosx_15_0_x86_64.whl
| Download URL | agent_work_runtime-0.5.1-py3-none-macosx_15_0_x86_64.whl |
|---|---|
| Size | 21.6 MB |
| Tags | Python 3 macOS 15.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
38099456c125682a47779b4cf3cc702ad9a9b968bac221b979d0c1d1c54bb36f
|
|
BLAKE2b-256 checksum How to use checksums |
7c093fa2feec1fad5c913587e98ab65982d3d28700f9ccf0ef94cff54177a42b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / agent_work_runtime-0.5.1-py3-none-macosx_15_0_arm64.whl
| Download URL | agent_work_runtime-0.5.1-py3-none-macosx_15_0_arm64.whl |
|---|---|
| Size | 20.6 MB |
| Tags | Python 3 macOS 15.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
8ad885332c936d11171ddcfbc4dce1bf713ca28541380a5244941ef47d01911b
|
|
BLAKE2b-256 checksum How to use checksums |
3cfc303051d5061552e9db5c4604055a70f765e8d4df8ac78b50a6b64a82615c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency log













