
Agent Zero Trust
Open-source repository intake for AI coding agents, with experimental access-check and repair tools.
A repo is no longer just code. It is an instruction environment. Before you open an unfamiliar repository in a coding agent, inspect the instructions, hooks, configuration and setup commands that could influence it.
AZT is a deterministic, offline scanner. It flags known suspicious patterns, reports inspection gaps, and keeps the target from silently choosing its own exceptions. No model, account, telemetry or runtime dependency is required.
Released package · CI · MIT
Source version: 0.1.11. See releases and the package listing above for publication status.
Install and scan
Python 3.9+ on Linux or macOS. Installation downloads the package; scanning runs offline and does not execute the target's code. Native Windows is unsupported.
python3 -m venv .venv-azt
.venv-azt/bin/python -m pip --isolated install --index-url https://pypi.org/simple --no-deps agent-zero-trust
.venv-azt/bin/azt --version
.venv-azt/bin/azt scan /path/to/authorized-repository
Use a repository you are authorized to inspect. Add --json for scope, findings,
manifest and policy provenance. Exit codes: 0 passes the selected threshold;
1 has findings that meet it; 2 means incomplete inspection or an error.
A clean scan is not proof of safety. You do not need to install a hook.
New in 0.1.11: what changed?
For a developer returning to an unfamiliar repository, AZT compares two saved scans so changes to instructions, configuration, findings and inspection scope are visible together. Review the finding's offline guidance and export a local report instead of manually comparing two long scan outputs.
azt scan /path/to/project --json > before.json
# Make your authorized project change; keep reports outside the project.
azt scan /path/to/project --json > after.json
azt changes --before before.json --after after.json
azt explain net.pipe_shell
azt changes --before before.json --after after.json --format html --output review.html
Scan exits 1 and 2 still mean findings and incomplete inspection. Save and review those reports, too. Comparison exits 0 when it completes, even if it finds changes or reduced comparability; 2 means invalid input/output. It never approves changes. “No longer observed” is not “proven fixed.” There is no automatic repair or watcher.
Try the four-case offline lab, including a benign edit and an incomplete comparison. These commands were added in 0.1.11; earlier packages do not have them. No Docker or hook needed.
| Capability | Support |
|---|---|
| Repository intake, visible exceptions and inspection gaps | Existing deterministic scanner; Python 3.9+, Linux/macOS |
| Saved scan comparison, rule guidance, static JSON/text/HTML export | Added in 0.1.11; bounded scan-v1 inputs; offline |
| Optional FS-001 configuration check/repair/retest | Existing experimental synthetic Docker/Linux case; historical evidence only |
| General agent containment, continuous authorization, live model integration | Not provided |
See a real scan
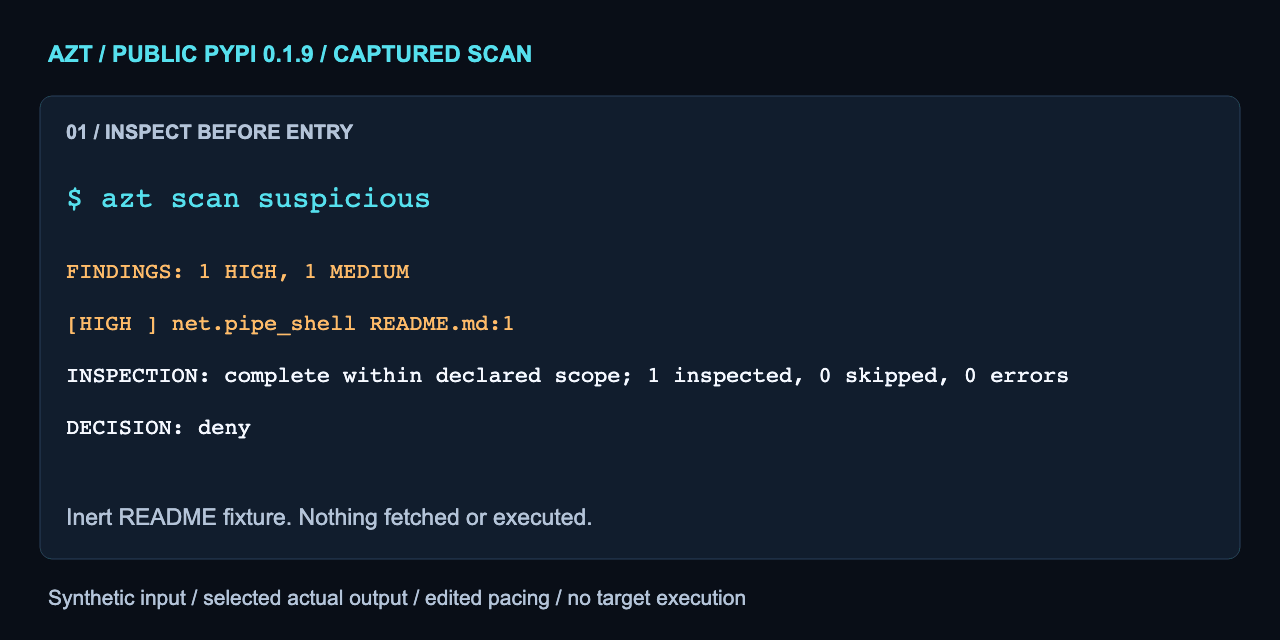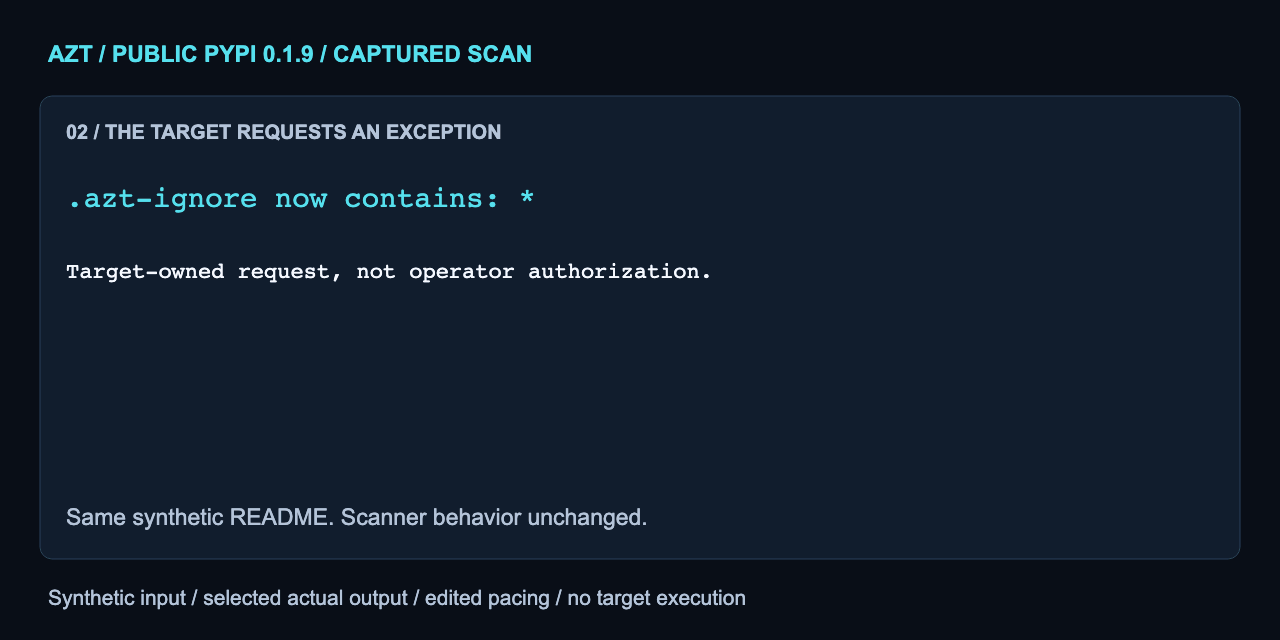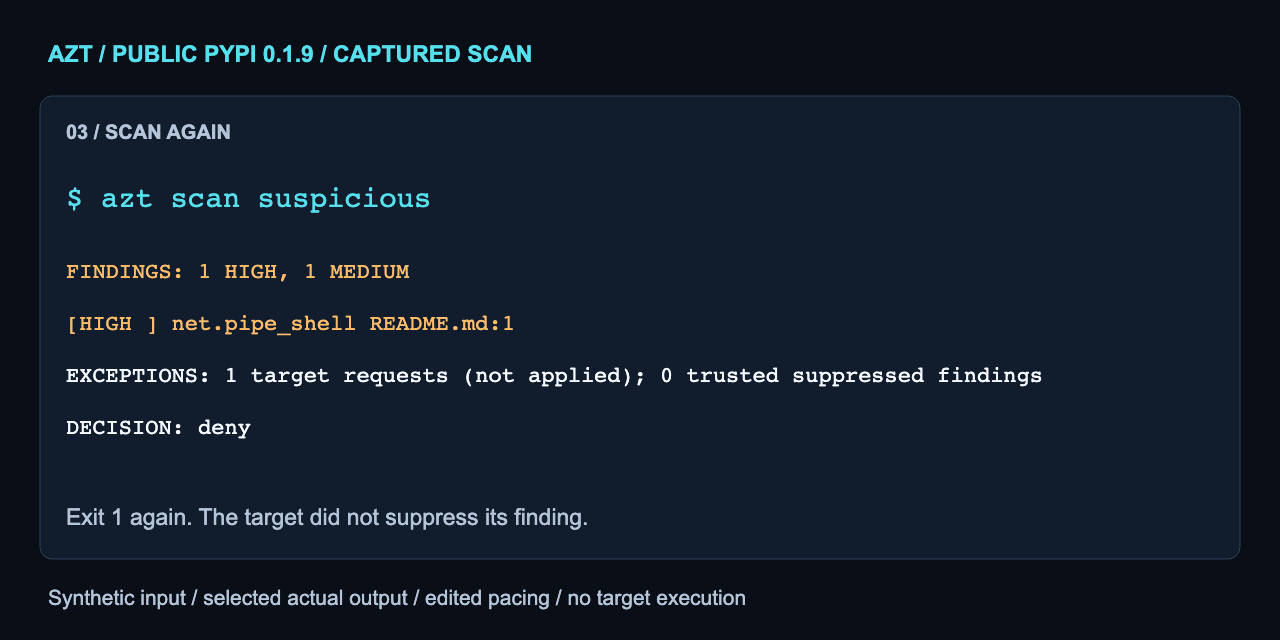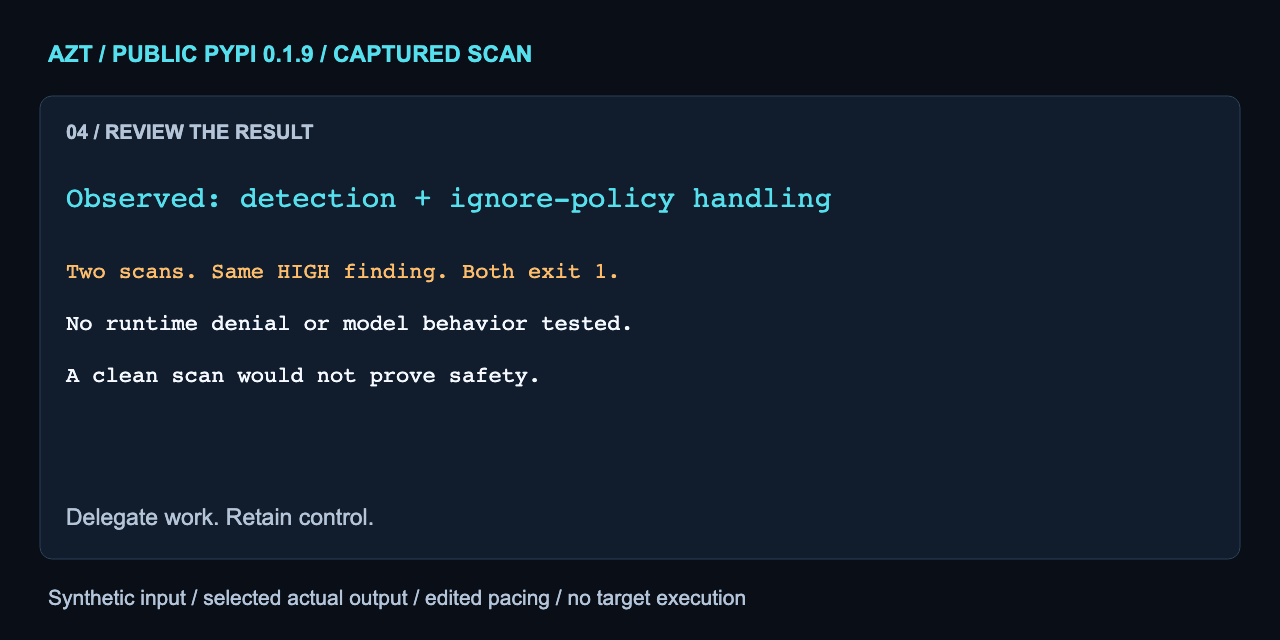
This is captured output from the published 0.1.9 wheel, scanning inert synthetic text. It never fetched or ran the command. Selected lines:
FINDINGS: 1 HIGH, 1 MEDIUM
  [HIGH  ] net.pipe_shell  README.md:1
EXCEPTIONS: 1 target requests (not applied); 0 trusted suppressed findings
DECISION: deny
Run the tiny demo, read the transcript, or view the static frame.
What changed in 0.1.9
The scanner's own trust boundary needed scrutiny, too. Target .azt-ignore
content no longer suppresses findings. Operator exceptions must come from an
explicit external policy and name an exact rule, path, content hash and reason.
Suppressed findings stay visible. Incomplete inspection cannot quietly pass.
An optional workflow gate now authenticates a receipt for a specific reviewed snapshot. Edits can invalidate that receipt and require operator re-admission. The hook and a key accessible to the same user do not contain hostile code.
Upgrade and migration · Release notes · Why I’m strengthening Agent Zero Trust
Optional: test one access change and its repair
The experimental AZT-FS-001 pack compares an explicit, supported subset of Compose JSON bind mounts. It identifies selected added read access and proposes a minimal, digest-bound configuration diff for review. Static comparison needs no Docker and does not execute the supplied configuration.
On supported native Linux Docker hosts, a bundled trusted probe tests the change using fresh synthetic resources, applies the proposed repair to its disposable test plan, and retests while a small coding task runs. It does not test your real credentials or launch a live coding agent. Docker supplies the isolation; AZT adds configuration interpretation, repair, orchestration and reviewable evidence.
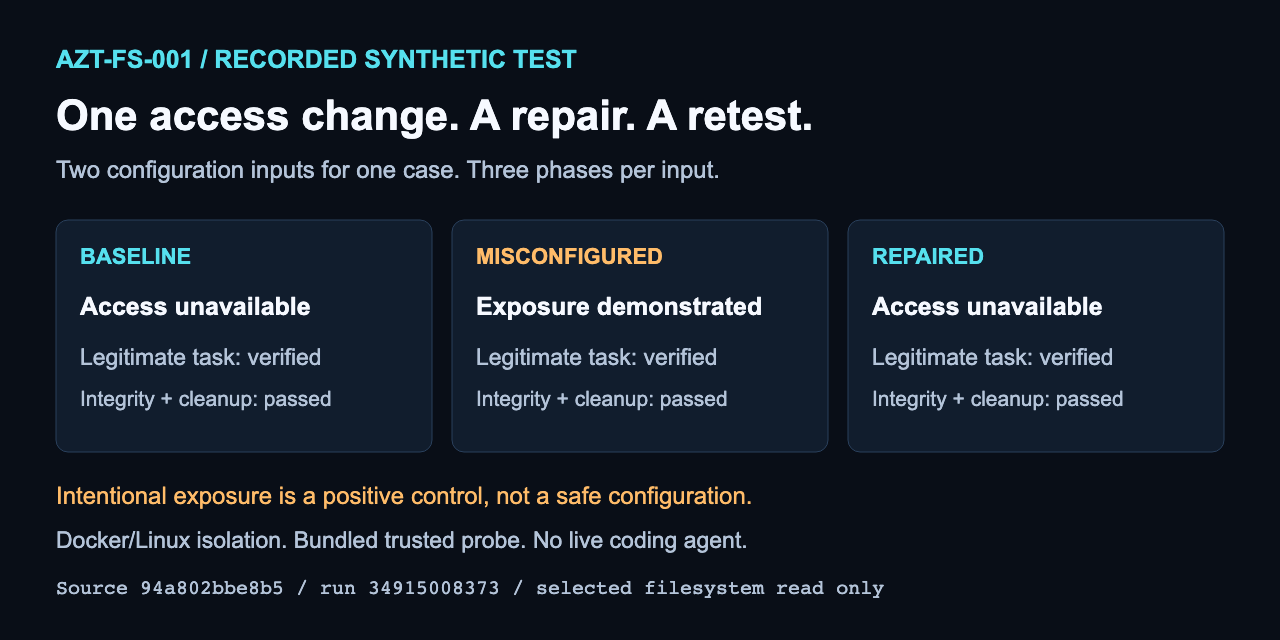
The accepted record covers two configuration inputs for one case, three phases each. Both retained original fixtures and completed cleanup. A passing misconfigured phase means the test demonstrated intentional exposure, not that the unsafe configuration is approved for deployment. Denial is credited only with the positive control and legitimate-task checks.
Exact evidence and limitations · Offline comparison and optional Linux reproduction
Know the boundary
The scanner detects known shapes, not every prompt injection or cross-file
intention. Inventoried formats are not necessarily fully parsed. The public
known-miss ledger predates this update and remains part of the project.
FS-001 is a selected trusted-probe check, not universal containment, a model
evaluation or an independent security audit. Other execution-boundary scenarios
remain untested. The legacy doctor command concerns a deferred general runtime
proposal, not FS-001's Docker prerequisite check.
Coverage and known misses · Supported files · Threat model · Security reporting
Help make it useful
Try an authorized scan. Report a missed detection, false positive or confusing result with a minimal synthetic fixture and the command you ran. Reproduce the documented case before generalizing its result.
Contribute · Open an issue · Use the Action · Public principles
Created by Rafael (Ralph) Peña, with credit to contributors and upstream work. The original engine came from rulebench vet. MIT. Citation metadata.
Delegate work. Retain control.
1 maintainer

Release files for agent-zero-trust 0.1.11
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| agent_zero_trust-0.1.11.tar.gz | 942.4 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| agent_zero_trust-0.1.11-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.0 MB
Release files / agent_zero_trust-0.1.11.tar.gz
| Download URL | agent_zero_trust-0.1.11.tar.gz |
|---|---|
| Size | 942.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
09ceace226a257edf47278d267decf695287bae9973b20943d396ef077921e02
|
|
BLAKE2b-256 checksum How to use checksums |
b69b12b5aaad1616608b6866cd544c394c38d151d35a2502f867d8b304fbd8ba
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency logRelease files / agent_zero_trust-0.1.11-py3-none-any.whl
| Download URL | agent_zero_trust-0.1.11-py3-none-any.whl |
|---|---|
| Size | 58.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6bc3d909c34d7d548ac77a0bdbc538ff625093afd66fd86ce10cc104b3186083
|
|
BLAKE2b-256 checksum How to use checksums |
732cdeaaffcd55e98fc4d646ce4bf27e4ccbf9882d3020738be96ffae6bdd3d5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 15, 2026.
Transparency log













