
agentwrapped
Spotify Wrapped for your AI coding agents. Your year with Claude Code, Codex and Gemini CLI: prompts sent, commands run, lines written, tokens burned, your longest session, how many times you told it "no", and your AI personality. Plus a share card.
uvx agentwrapped
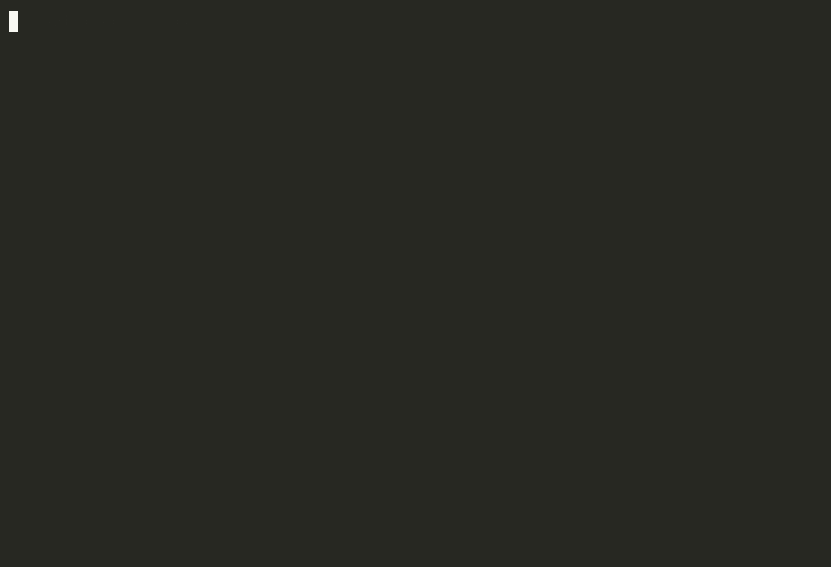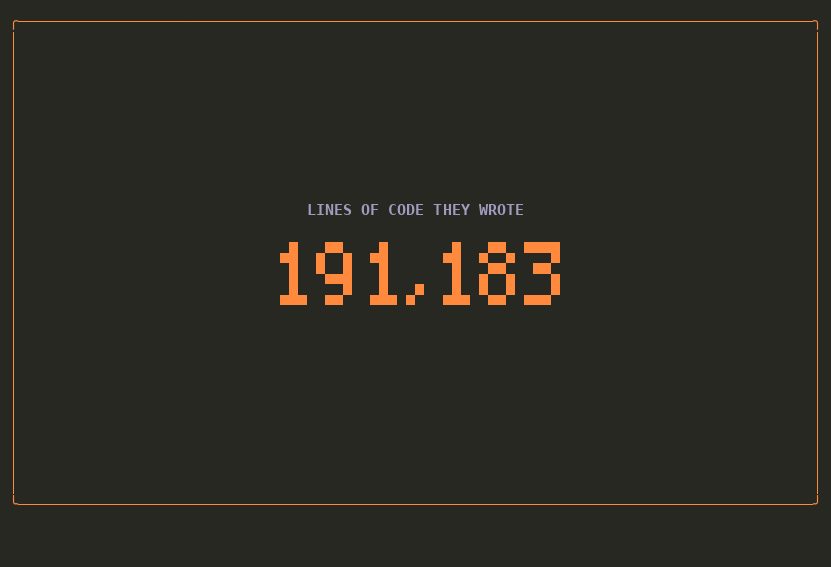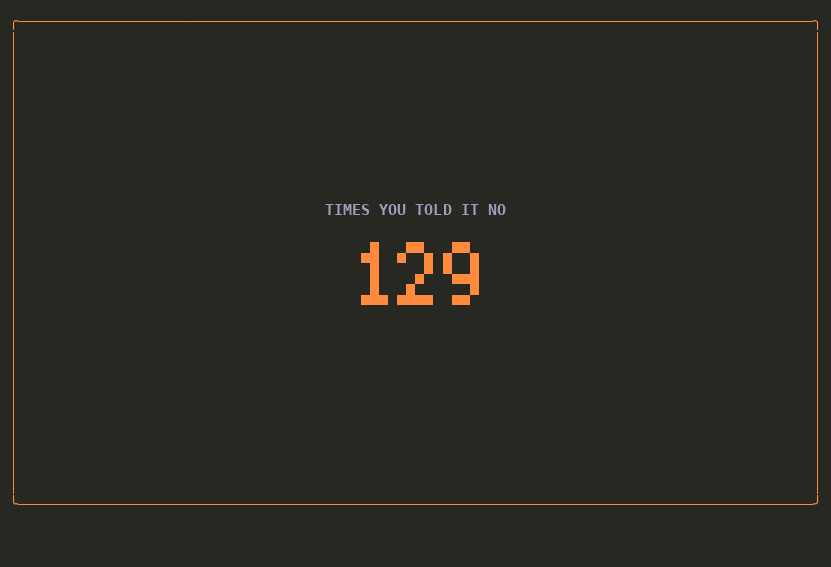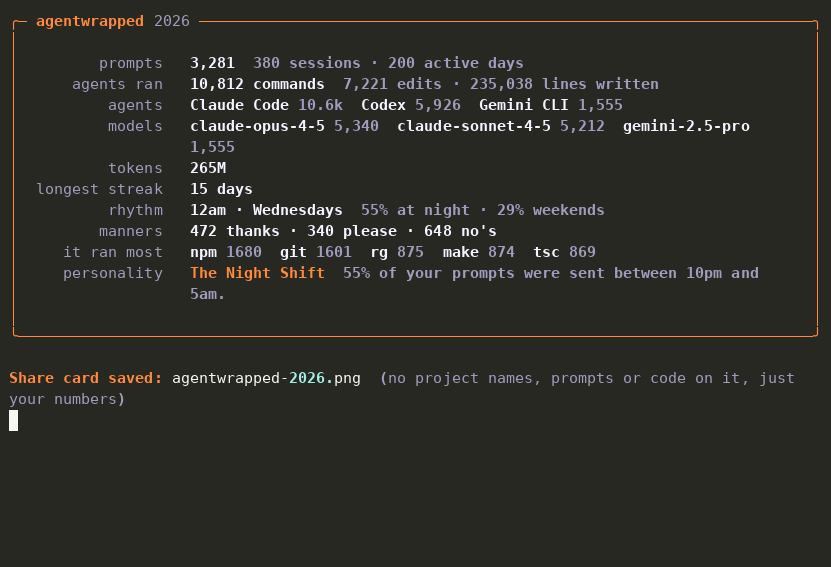
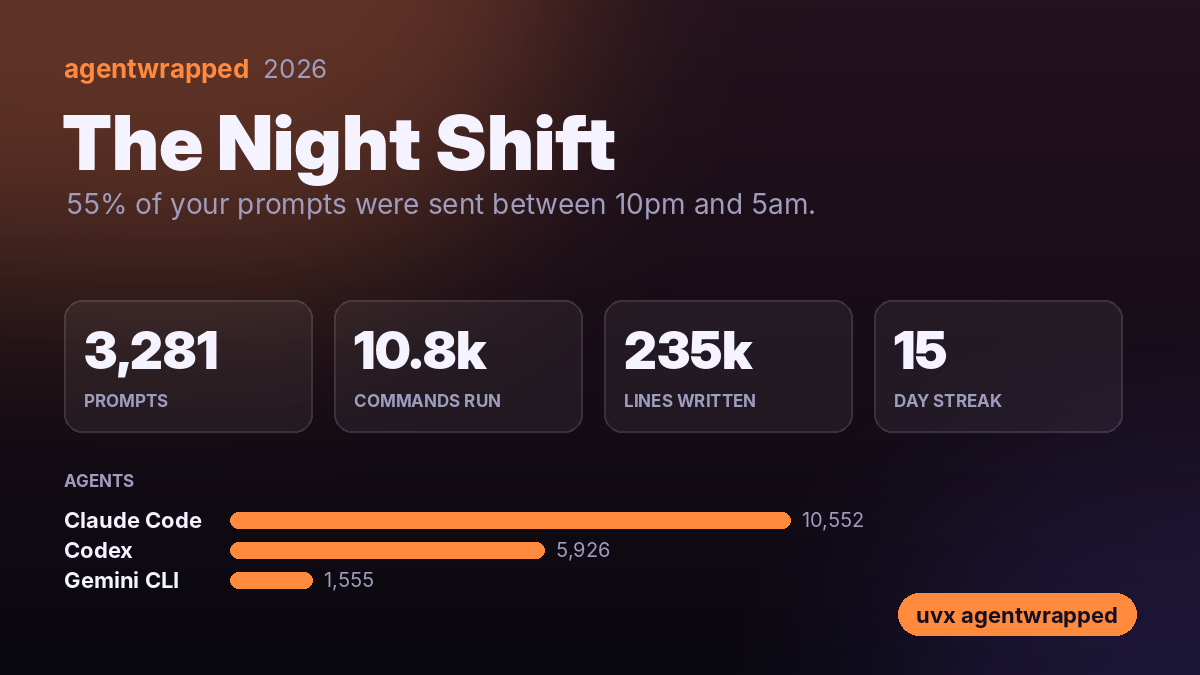
Demo on a made-up year of agent logs generated by docs/demo.py. Yours will be different.
What's in it
- Prompts, sessions and active days, and your longest daily streak
- Commands your agents ran and what they ran most (
npm,git,pytest…) - Lines of code they wrote, across how many files
- Which agents and models did the work, and tokens where the logs record them
- Your longest session, counting only time you were actually going back and forth
- When you prompt: peak hour and day, share at night and on weekends
- Manners: thanks, pleases, and every "no", "undo", "revert" and "that's not what I meant"
- Your AI personality: The Night Shift, The Polite One, The Micromanager, The Delegator, The Architect, The Weekend Hacker or The Pair Programmer
The share card (agentwrapped-<year>.png, 1200×675, the size X and LinkedIn previews use) shows only numbers and agent names: no project names, prompts or code.
Where it reads
| Agent | Logs |
|---|---|
| Claude Code | ~/.claude/projects/*/*.jsonl (or $CLAUDE_CONFIG_DIR) |
| Codex CLI | ~/.codex/sessions/**/rollout-*.jsonl (or $CODEX_HOME) |
| Gemini CLI | ~/.gemini/tmp/*/chats/session-* |
Agents only keep logs for so long (Claude Code deletes transcripts after 30 days by default; set cleanupPeriodDays in its settings to keep more), so run it before year-end.
Options
agentwrapped                 # this year, animated
agentwrapped --year 2025
agentwrapped --no-anim       # just the summary
agentwrapped --speed 2       # faster animation
agentwrapped --card me.png   # where to save the share card (or --no-card)
Privacy
Everything stays on your machine. agentwrapped only reads the log files above.
Install
uvx agentwrapped           # run without installing
pipx install agentwrapped  # or install it
Requires Python 3.9+. Depends on rich, pillow and pyfiglet. Card fonts: Inter (SIL Open Font License).
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for agentwrapped 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| agentwrapped-0.1.0.tar.gz | 738.6 kB | With provenance | Details for agentwrapped-0.1.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| agentwrapped-0.1.0-py3-none-any.whl | Python 3 | none | any | Details for agentwrapped-0.1.0-py3-none-any.whl |
Total release size: 1.5 MB
Release files / agentwrapped-0.1.0.tar.gz
| Download URL | agentwrapped-0.1.0.tar.gz |
|---|---|
| Size | 738.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d553a6e2637629ac0bede663168c68961da0168654eff7a69663e34bf6d23fd4
|
|
BLAKE2b-256 checksum How to use checksums |
a3e8606fea43d92116ec35f2c8431911f508d591518589af18d4dbcb260240f4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logRelease files / agentwrapped-0.1.0-py3-none-any.whl
| Download URL | agentwrapped-0.1.0-py3-none-any.whl |
|---|---|
| Size | 742.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5d4ee1a076d3552e508b1080e638b7e240b81c69b7a744c063f5dc84fb232544
|
|
BLAKE2b-256 checksum How to use checksums |
b47e43107a59c94c50dc142d15e542540cf2759ad947b5a00db4416e618fa4ba
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logSecurity for agentwrapped 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for agentwrapped-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 10, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













