

Open-source compliance-as-code for AI systems: one contract, executable OPA/Rego policies, and reproducible evidence across the EU AI Act, UK AI governance, NIST AI RMF, and more.




📦 Full documentation, forkable examples, contributing guides, translations, and 92 GOPAL/Rego policies live in the GitHub repository.
AICertify is the open execution and evidence layer for AI governance. Describe an AI system in a contract, supply organisation-known facts, attach or compute measured metrics, evaluate that evidence against versioned GOPAL policies through Open Policy Agent, and generate dated PDF, Markdown, JSON, or HTML reports.
The goal is simple: move from “we have an AI policy” to evidence another engineer, auditor, or risk team can inspect and reproduce.
Use AICertify to:
- evaluate an AI system against named governance and regulatory policy sets
- keep declared facts distinct from evaluator-produced measurements
- run inspectable OPA/Rego policy logic locally, in CI/CD, or air-gapped
- generate portable PDF, Markdown, JSON, or HTML evidence with per-policy results
- extend the stack with your own Rego policies and evaluator adapters
AICertify is part of the Open Policy Agent ecosystem, using the same policy engine widely used for Kubernetes admission, service authorisation, and infrastructure policy.
⭐ Building AI governance as code? Star the GitHub repo so other practitioners can find it.
Quick Start
# 1. Install AICertify (~3–5 min on first install; pulls langchain + transformers)
pip install aicertify

# 2. Install the OPA binary, one-time (~80 MB)
curl -L https://openpolicyagent.org/downloads/latest/opa_linux_amd64 -o /usr/local/bin/opa && sudo chmod +x /usr/local/bin/opa

# 3. Run the bundled demo (no contract file or API keys)
aicertify demo
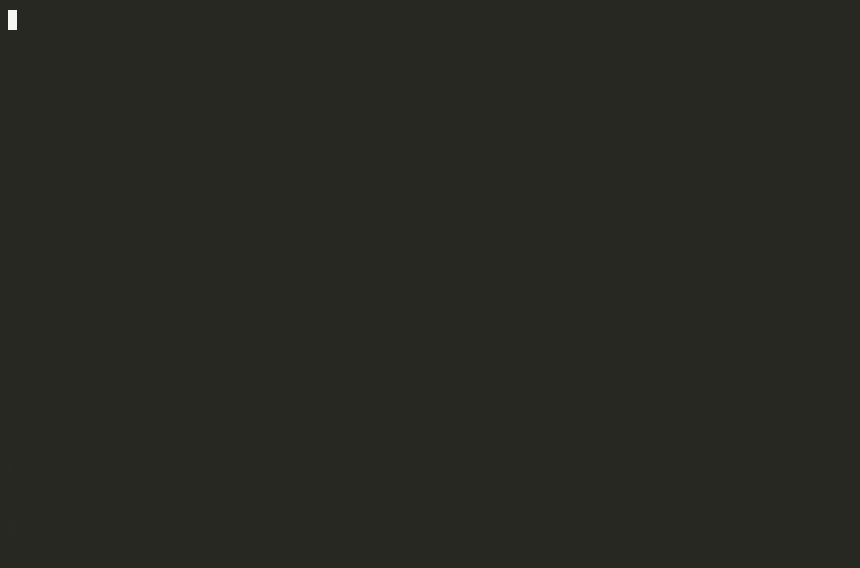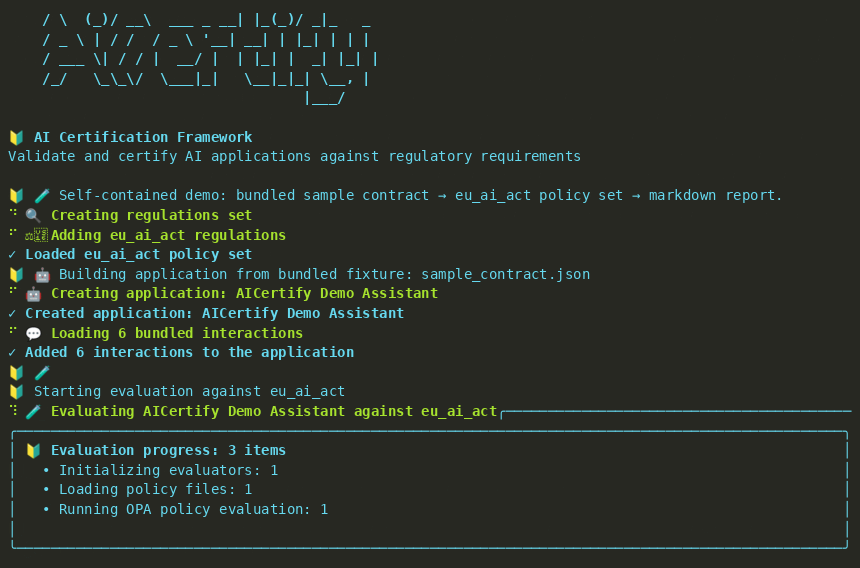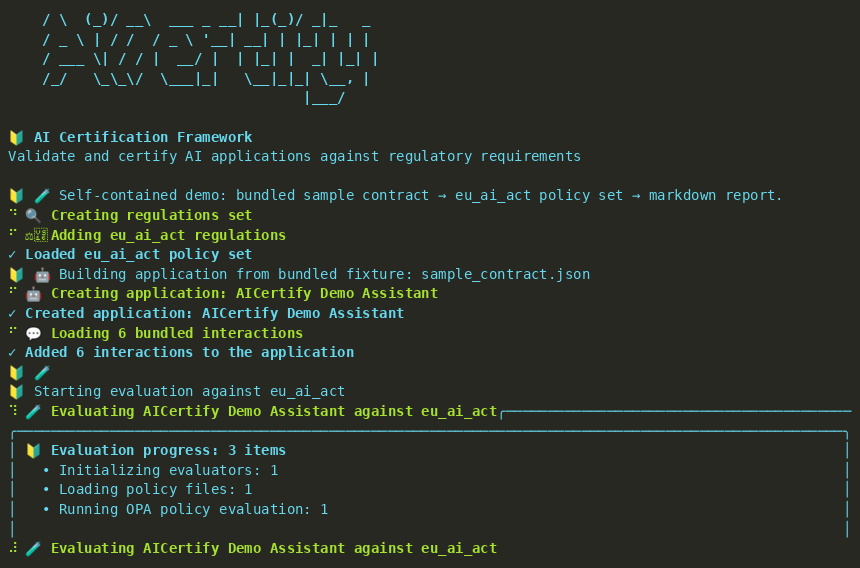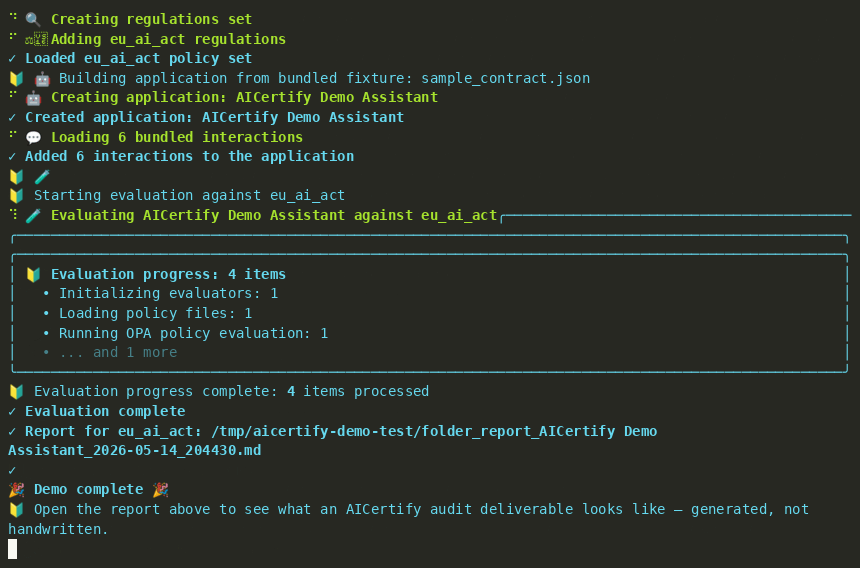
aicertify demo loads a bundled sample contract, evaluates it against the EU AI Act policy set via OPA, and writes aicertify_demo_report.md. The sample intentionally contains no compliance declarations, so evidence-dependent policies deny; this demonstrates fail-closed behavior rather than an artificially green demo.
For richer evaluations (LangFair fairness metrics, DeepEval content-safety scoring, PDF reports), see examples/quickstart.py and the forkable example bots, each of which ships an input_contract.json, a policy_config.yaml, and a run.py.
Minimal Python usage
from aicertify import regulations, application

# 1. Pick the regulations you want to certify against
regs = regulations.create("my_regulations")
regs.add("eu_ai_act")

# 2. Wrap your AI app
app = application.create(
    name="customer-support-bot",
    model_name="gpt-4o",
    model_version="2024-08-06",
)

# 3. Feed it real interactions
app.add_interaction(
    input_text="I want a refund for my order",
    output_text="I can help with that. Could you share your order number?",
)

# 4. Evaluate and get reports back
await app.evaluate(regulations=regs, report_format="pdf", output_dir="reports")
That's the whole loop. Contract → evidence → policy evaluation → report.
Why AICertify?
Evaluation libraries such as Fairlearn and AI Fairness 360 measure specific properties. Governance platforms address broader inventory and workflow needs. AICertify provides the open execution layer between them: combine declared system facts with measured evidence, run inspectable GOPAL/Rego policies through OPA, and emit portable, dated results.
The differentiator is reproducibility: inspect the rules, pin versions, run locally or air-gapped, review changes in Git, and retain the evidence outside a vendor account.
See the full positioning in docs/why-aicertify.md on GitHub.
Compared with alternatives
| AICertify | Fairlearn / AIF360 | MS RAI Toolbox | Governance SaaS | |
|---|---|---|---|---|
| Open source | ✅ Apache 2.0 | ✅ MIT | ✅ MIT | Varies |
| Local / air-gapped execution | ✅ | ✅ | ✅ | Varies |
| Named governance / regulatory policy sets | ✅ via GOPAL | ❌ (measurement library) | ❌ (toolkit) | Common |
| Inspectable policy-as-code | ✅ OPA / Rego | ❌ | ❌ | Varies |
| Industry-specific policy coverage | ✅ | ❌ | ❌ | Varies |
| Portable dated reports | ✅ PDF / MD / JSON / HTML | ❌ | Partial | Common |
| Custom policy logic | ✅ Rego | ❌ | N/A | Product-specific |
For OPA / Rego users
If you already use OPA, AICertify gives you the AI-application context layer OPA was missing. You bring your AI app; AICertify captures the interactions, feeds them through the OPA engine against AI-specific Rego policies sourced from gopal, and emits audit-ready evidence.
The whole stack is policy-as-code: the same workflow you already use for Kubernetes admission, microservice authorisation, and infrastructure governance.
Forkable examples
Copy any of these and substitute your own contract:
- customer-support-bot: limited-risk EU AI Act + global cross-cutting policies
- healthcare-triage-bot: EU AI Act high-risk Annex III(5)(a) + gopal healthcare patient-safety policies
- hiring-screening-bot: EU AI Act high-risk Annex III(4) + fair-lending proxy + FRIA metadata pattern
Each example ships an input_contract.json, policy_config.yaml, sample_interactions.json, an expected_report.md, and a run.py you can execute directly.
See the output
You don't have to install anything to see what AICertify produces. A sample pre-generated PDF is in the repo:
- demo-report-eu-ai-act.pdf: a customer-support agent evaluated against the EU AI Act
- expected reports: committed Markdown reports for the customer-support, healthcare-triage and hiring-screening examples, and a retained fair-lending PDF under
examples/outputs/loan_evaluation/
More on GitHub
- Full README with diagrams (English / 简体中文 / 日本語 / 한국어 / हिन्दी)
- CONTRIBUTING.md: how to add policies, examples, or framework coverage
- SECURITY.md: private vulnerability disclosure
- CHANGELOG.md: what changed in each release
- gopal: the upstream OPA/Rego policy library AICertify uses
License
Apache 2.0, see the LICENSE file.
1 maintainer

Metadata
1 maintainer
Release files for aicertify 0.8.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| aicertify-0.8.1.tar.gz | 602.4 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| aicertify-0.8.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.5 MB
Release files / aicertify-0.8.1.tar.gz
| Download URL | aicertify-0.8.1.tar.gz |
|---|---|
| Size | 602.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c92a8c8acb243f15964ac7185d9cb2862f68767d4606460981c0d1831590aee1
|
|
BLAKE2b-256 checksum How to use checksums |
bb1b305ff5b1a90ac7d8b256852eedc85c28080958d0957766ccb401ae872aec
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency logRelease files / aicertify-0.8.1-py3-none-any.whl
| Download URL | aicertify-0.8.1-py3-none-any.whl |
|---|---|
| Size | 852.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e9f506142c192dadb31744236082e38bfb6272a522f3331498feefc9075f6836
|
|
BLAKE2b-256 checksum How to use checksums |
3e13d481dc9d422a61940df5ed19ab73b5bdef66310e6f0943fcfab7f66350a4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency log













