
Altar
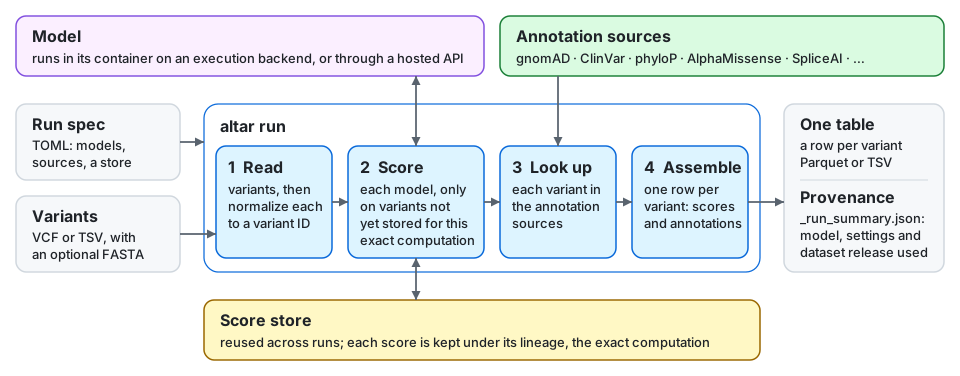
Altar scores genomic variants with sequence models and annotates them with published evidence, in one run that writes one table. A run spec names your variants, the models, the annotation sources and where to keep the scores. Altar runs each model in a container or calls its hosted API, looks up the evidence, and records which model, settings and dataset release produced every value.
Altar is in beta. Its interfaces are labelled Stable, Provisional or Preview; see Maturity labels.
Install
Altar needs Python 3.12 or newer. Install it with the bindings you need. To annotate variants with gnomAD and ClinVar:
pip install altar altar-popfreq altar-clinvar
Each model and annotation source is a separate binding, such as altar-legnet or altar-conservation. Cloud storage,
BigQuery and remote execution are extras, such as pip install "altar[gcs]". Model frameworks and weights run in
separate container images. Install Altar lists every binding
and extra.
Documentation
The documentation is at https://kundajelab.github.io/altar/.
- Quickstart: annotate a VCF, then score it with LegNet on the CPU
- Tutorials: five notebooks that build one analysis
- Models and data: every model and annotation source
- Concepts: how a run works, and what the scores, annotations and links mean
- Use Altar from Python
- Extend Altar: add a model, a dataset, a backend or a store
- Maturity labels: the public modules and the label each one carries
Cite and licence
Cite Altar as Cite Altar describes, and cite each model and dataset you use. Altar is copyright 2026 Riya Sinha and released under the MIT License. Models and datasets carry their own licences and terms.
1 maintainer

Metadata
1 maintainer
Release files for altar 0.6.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| altar-0.6.2.tar.gz | 3.6 MB | Without provenance | Details for altar-0.6.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| altar-0.6.2-py3-none-any.whl | Python 3 | none | any | Details for altar-0.6.2-py3-none-any.whl |
Total release size: 6.1 MB
Release files / altar-0.6.2.tar.gz
| Download URL | altar-0.6.2.tar.gz |
|---|---|
| Size | 3.6 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8ef3a2396e16df632c0d57519d44dd43df651a5064772120c72f16c8a5145c41
|
|
BLAKE2b-256 checksum How to use checksums |
02cc7dd9e32984baac499865edc189d37a8ff11641f6e23c0aa67bc0cc02f036
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.12.17 {"installer":{"name":"uv","version":"0.12.17","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"22.04","id":"jammy","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":null}
|
Release files / altar-0.6.2-py3-none-any.whl
| Download URL | altar-0.6.2-py3-none-any.whl |
|---|---|
| Size | 2.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5faa328490657973778233ed4af8afbcddb31cdb3703beefe8ade3e2591823ba
|
|
BLAKE2b-256 checksum How to use checksums |
8e25c336cf08462efa06aa7d8e23bb9ddb1dc0c6b4b0f3a504eb5a50e0f590c1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.12.17 {"installer":{"name":"uv","version":"0.12.17","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"22.04","id":"jammy","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":null}
|
Security for altar 0.6.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














