



A fast, C++-accelerated ANTLR runtime for Python, for target-agnostic grammars.
antlrope = ANTLR + Ordered Parse Events: your parse is delivered as one ordered stream of events instead of a per-node tree walk.
10–20× faster than the official pure-Python
antlr4-python3-runtimeon workloads that touch most nodes, and faster still when your listener subscribes to only part of the grammar.
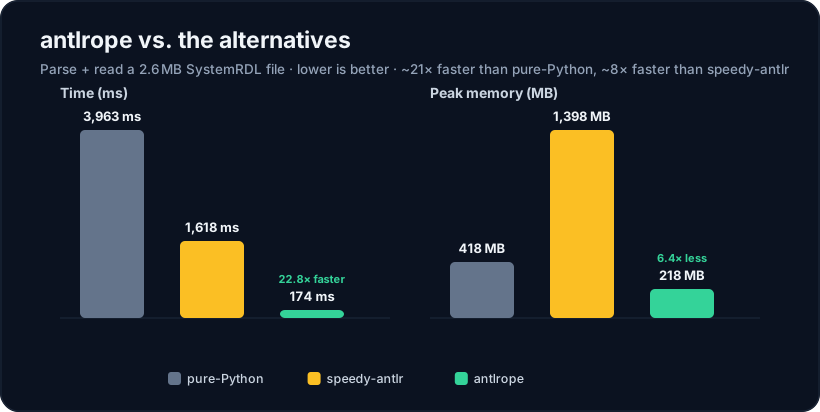
Parsing and reading a real 2.6 MB SystemRDL file, compared with the pure-Python runtime and the speedy-antlr accelerator. See the full benchmark.
Generate your parser with the ordinary ANTLR tool targeting Python, install this package, generate a small facade class, and write a pure-Python event listener. Parsing runs inside the official ANTLR4 C++ runtime, driven directly from the serialized ATN (Augmented Transition Network) that the stock Python target already emits. A conventional listener walks the parse tree node by node, crossing the foreign-function boundary once per node. Here, the C++ side instead collects a single, filtered stream of events and hands it to Python in one transfer. Rules and tokens your listener doesn't subscribe to are dropped in C++, before they reach Python.
It complements, rather than replaces, the official antlr4-python3-runtime: you
use the same generated parser and get a faster way to consume it.
Install
From PyPI:
pip install antlrope
Or from conda-forge (with conda, mamba, or pixi):
conda install -c conda-forge antlrope
Either way you get a pre-compiled binary, so there is nothing to build. The
official antlr4-python3-runtime is installed automatically as a dependency.
Quickstart
-
Generate your parser with the stock ANTLR tool (Python target):
antlr4 -Dlanguage=Python3 MyGrammar.g4 -o generated
-
Generate the facade from the generated parser module:
antlrope gen generated.MyGrammarParser MyGrammar -o my_listener.py
This emits a
MyGrammarEventListenerbase class withenter<Rule>,exit<Rule>,visitTerminal, andvisitErrorstubs and token-type constants. The facade also imports your lexer and parser and stores references to them, so you never pass them at parse time. The lexer module name is derived from the parser module name using ANTLR's<Grammar>Lexer/<Grammar>Parsernaming convention. Pass--lexerif your lexer module is named differently. -
Subclass it and override only the callbacks you care about:
from my_listener import MyGrammarEventListener

class Collector(MyGrammarEventListener):
    def enterPair(self) -> None:
        ...
    def visitTerminal(self, token_type: int, text: str) -> None:
        ...

Collector().walk(source_text)
The callbacks you override determine which events the C++ side emits; it skips every other rule and token. The fewer node kinds you subscribe to, the faster the walk.
How it works
- The C++ extension deserializes the ATN from your generated lexer and parser and
runs it with ANTLR's
LexerInterpreterandParserInterpreter. No C++ parser is generated. - After parsing, a native depth-first traversal of the parse tree appends
fixed-size
(kind, payload, start, stop)int32 records to a single buffer (parse_events). kind:0=ENTER_RULE, 1=EXIT_RULE, 2=TERMINAL, 3=ERROR;payloadis the rule index or token type;startandstopare character indices into the source (the token's span, or a rule's full extent;-1for an item with no span, such as an empty rule). Python recovers token text by slicingtext[start:stop + 1], so no strings are copied across the boundary.- Masks built from your overridden callbacks filter rules and tokens out of the stream in C++.
Limitations
Antlrope only works with target-language-agnostic grammars. It interprets the ATN, so it cannot run target-language semantic predicates or embedded grammar actions, and grammars that depend on them will not parse correctly. See Performance & limitations for details and for the performance characteristics of the event-stream approach.
Contributing
Development setup, pixi environments, and the vendored-runtime workflow live in CONTRIBUTING.md.
Documentation
Full documentation: zuzukin.github.io/antlrope.
In the repo, see docs/: getting started,
installation,
API reference,
chunking,
migrating from antlr4-python3-runtime,
performance & limitations,
how it works, and the
SystemRDL benchmark.
Using an AI coding assistant to write a listener or port a ParseTreeListener?
Give it the LLM-oriented summary of these docs at
zuzukin.github.io/antlrope/llms.txt,
your grammar, and, if you are porting, your existing listener.
License
Apache-2.0. Bundles the ANTLR4 C++ runtime (BSD-3-Clause) under
vendor/antlr4-cpp/; see vendor/antlr4-cpp/UPDATING.md for provenance.
1 maintainer

Metadata
1 maintainer
Release files for antlrope 1.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| antlrope-1.0.2.tar.gz | 447.5 kB | With provenance | Details for antlrope-1.0.2.tar.gz |
Built distributions (wheels)
| File | Actions Reset | |||
|---|---|---|---|---|
| antlrope-1.0.2-cp312-abi3-win_amd64.whl | CPython 3.12 | abi3 | Windows x86-64 | Details for antlrope-1.0.2-cp312-abi3-win_amd64.whl |
| antlrope-1.0.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | CPython 3.12 | abi3 | Linux glibc 2.17+ x86-64 | Details for antlrope-1.0.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
| antlrope-1.0.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | CPython 3.12 | abi3 | Linux glibc 2.17+ ARM64 | Details for antlrope-1.0.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
| antlrope-1.0.2-cp312-abi3-macosx_11_0_x86_64.whl | CPython 3.12 | abi3 | macOS 11.0+ x86-64 | Details for antlrope-1.0.2-cp312-abi3-macosx_11_0_x86_64.whl |
| antlrope-1.0.2-cp312-abi3-macosx_11_0_arm64.whl | CPython 3.12 | abi3 | macOS 11.0+ ARM64 | Details for antlrope-1.0.2-cp312-abi3-macosx_11_0_arm64.whl |
Total release size: 2.4 MB
Release files / antlrope-1.0.2.tar.gz
| Download URL | antlrope-1.0.2.tar.gz |
|---|---|
| Size | 447.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a4093fd872516fe3eef3522bc054712194bb7cbd81fd4d647e4d2071893bd648
|
|
BLAKE2b-256 checksum How to use checksums |
8ebdf92ae6b99ab31400766703273ba37bd97a6b5486a2f8923b9e1a61a1e77b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / antlrope-1.0.2-cp312-abi3-win_amd64.whl
| Download URL | antlrope-1.0.2-cp312-abi3-win_amd64.whl |
|---|---|
| Size | 313.4 kB |
| Tags | CPython 3.12 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
149fe8f79bf417920a378537397912620287144711792a65496bb5de14649600
|
|
BLAKE2b-256 checksum How to use checksums |
6768f5f276cc416b469d185ce042a999e599fa3b326e2f453305110ae22c409d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / antlrope-1.0.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | antlrope-1.0.2-cp312-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 442.7 kB |
| Tags | CPython 3.12 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
f045b6191d66d1c2691bd1e2f5f847044ce543fa806ae4d7f184f8e3f204968e
|
|
BLAKE2b-256 checksum How to use checksums |
25fc1e8a661dcf9a95079a1f8b407bae0364b9c65da8306f3ed9c057a1b13f28
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / antlrope-1.0.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | antlrope-1.0.2-cp312-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 426.9 kB |
| Tags | CPython 3.12 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
2db0ce9ed397bde65648e68927f190bc49c599f40c78fa7dd030fe82c1c1ad96
|
|
BLAKE2b-256 checksum How to use checksums |
f1131fa8c028dc49964894c2a7ca6a35044f81a91d3da62c01ce97670e3a5286
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / antlrope-1.0.2-cp312-abi3-macosx_11_0_x86_64.whl
| Download URL | antlrope-1.0.2-cp312-abi3-macosx_11_0_x86_64.whl |
|---|---|
| Size | 374.4 kB |
| Tags | CPython 3.12 abi3 macOS 11.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
f37e772d227560887517e70ed5dbc287a5eebe54a61ba3804fbd9552271d3f56
|
|
BLAKE2b-256 checksum How to use checksums |
b3f8dd1713bfb0135daa06175d01d233b1102cab1c0405c11c4b7903e6499dc5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logRelease files / antlrope-1.0.2-cp312-abi3-macosx_11_0_arm64.whl
| Download URL | antlrope-1.0.2-cp312-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 364.9 kB |
| Tags | CPython 3.12 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
3405c4109841cdd6d4566d193ca93bbd0575f8815a13afdb6366519f3ebfbfda
|
|
BLAKE2b-256 checksum How to use checksums |
7ecd8d81730abfd6a32bad8ec485a319c663f3b03634f786dd93000ac6c7a1fb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logSecurity for antlrope 1.0.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 6 files in this release have been uploaded with provenance metadata.
Attestation for antlrope-1.0.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 26, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














