
apeGmsh

Structural-FEM wrapper around Gmsh with a composition-based API and a
snapshot FEM broker. Designed to make it cheap to describe a model
once (geometry + physical groups + loads + constraints) and feed it
to any solver. OpenSees has first-class support; other solvers can be
plugged in through the same FEMData contract.
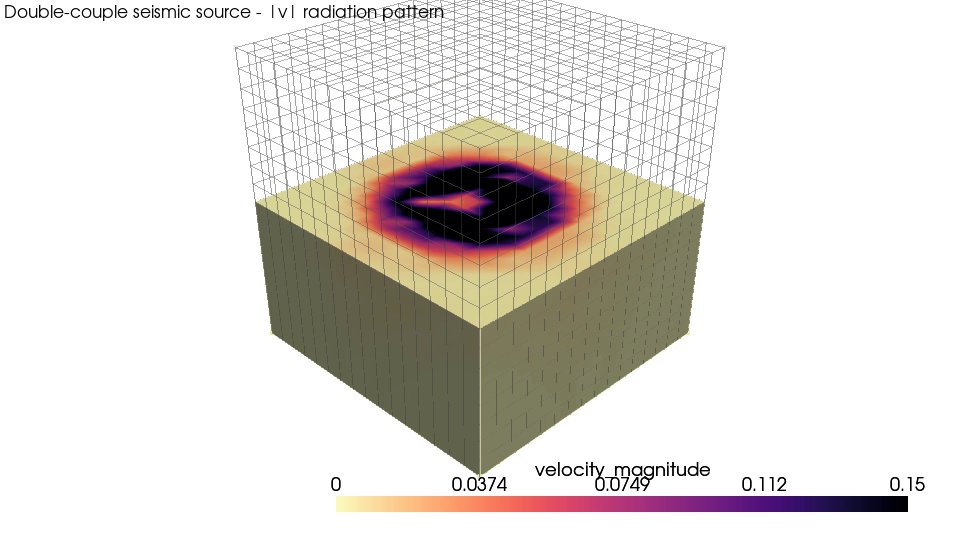
New to the library? Start with the learning path — every tutorial and worked example in reading order, each checked against a known answer — or jump straight into your first model in 10 minutes.
Documentation: https://nmorabowen.github.io/apeGmsh/
Installation
Not on PyPI yet — install directly from the repo:
# Latest from main
pip install "git+https://github.com/nmorabowen/apeGmsh.git@main"

# With all optional dependencies
pip install "apeGmsh[all] @ git+https://github.com/nmorabowen/apeGmsh.git@main"
Or clone for editable development:
git clone https://github.com/nmorabowen/apeGmsh.git
cd apeGmsh
pip install -e ".[all]"
Requires Gmsh (with Python bindings), NumPy, and Pandas. Optional
extras: matplotlib (plotting), openseespy (analysis),
pyvista + PySide6 (Qt and web viewers).
Quick start
from apeGmsh import apeGmsh

with apeGmsh(model_name="plate") as g:
    # 1. Geometry — sub-composites under g.model
    p1 = g.model.geometry.add_point(0,   0,  0, lc=10)
    p2 = g.model.geometry.add_point(100, 0,  0, lc=10)
    p3 = g.model.geometry.add_point(100, 50, 0, lc=10)
    p4 = g.model.geometry.add_point(0,   50, 0, lc=10)
    l1 = g.model.geometry.add_line(p1, p2)
    l2 = g.model.geometry.add_line(p2, p3)
    l3 = g.model.geometry.add_line(p3, p4)
    l4 = g.model.geometry.add_line(p4, p1)
    loop = g.model.geometry.add_curve_loop([l1, l2, l3, l4])
    surf = g.model.geometry.add_plane_surface(loop)

    # 2. Mesh — sub-composites under g.mesh
    g.mesh.sizing.set_global_size(10)
    g.mesh.generation.generate(dim=2)
    g.mesh.partitioning.renumber(dim=2, method="simple", base=1)

    # 3. Snapshot for the solver
    fem = g.mesh.queries.get_fem_data(dim=2)
    print(fem.info)
On import, apeGmsh prints an ASCII banner with the version to
stderr. Set APEGMSH_QUIET=1 to suppress it (useful for tests
and CI).
How it fits together
You describe a model inside an apeGmsh session — one Gmsh kernel
fronted by focused composites (g.model for geometry, g.mesh for
meshing, plus physical groups, parts, constraints, loads, and masses).
Definitions reference labels, not raw mesh tags, so you can declare
a load on "TopFace" before a single node exists. Once the mesh is
generated, get_fem_data() resolves every definition against it and
returns a frozen FEMData snapshot — nodes, elements, and all loads,
masses, and constraints as plain nodal records. That snapshot is the
single contract between Gmsh and any downstream solver.
For OpenSees, the snapshot feeds apeSees(fem), a typed bridge built
after the session closes: typed constructors for materials, sections,
and elements; MP constraints emitted automatically; loads pulled in
per pattern with p.from_model(case). The bridge emits a runnable
Tcl or Python deck — or runs openseespy in-process — and solver output
comes back as a Results object with interactive and web viewers.
The mental model
page walks through these ideas properly; the
design notes cover the
internals; the site's API reference owns the full method inventory.
Credits
Developed by: Nicolás Mora Bowen · Patricio Palacios · José Abell · Guppi
Part of José Abell's El Ladruño Research Group.
License
apeGmsh is licensed under the GNU General Public License v3.0 or later (see LICENSE).
GPL rather than a permissive license because apeGmsh builds on Gmsh, which is GPLv2+ — its linking exception covers only Netgen, METIS, OpenCASCADE and ParaView, not downstream API consumers. pygmsh is GPLv3+ for the same reason.
Note that the GPL constrains distribution, not use: running apeGmsh internally — including on commercial engineering projects — carries no source-disclosure obligation.
Citing
If you use apeGmsh in published work, please cite it via its DOI:
Mora Bowen, N., Palacios, P., Abell, J., & Guppi. apeGmsh: a structural-FEM wrapper around Gmsh with a snapshot FEM broker. Zenodo. https://doi.org/10.5281/zenodo.21815489
@software{apeGmsh,
  author    = {Mora Bowen, Nicolás and Palacios, Patricio and Abell, José and Guppi},
  title     = {apeGmsh: a structural-FEM wrapper around Gmsh with a snapshot FEM broker},
  year      = {2026},
  publisher = {Zenodo},
  doi       = {10.5281/zenodo.21815489},
  url       = {https://doi.org/10.5281/zenodo.21815489}
}
That is the concept DOI — it always resolves to the most recent release, so prefer it unless you need to pin the exact version you ran. For that, use the version DOI shown on the Zenodo record (v2.0.0 is 10.5281/zenodo.21815490).
Machine-readable metadata lives in CITATION.cff — GitHub's "Cite this repository" button reads it directly.
1 maintainer

Metadata
1 maintainer
Release files for apeGmsh 2.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| apegmsh-2.0.0.tar.gz | 3.2 MB | With provenance | Details for apegmsh-2.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| apegmsh-2.0.0-py3-none-any.whl | Python 3 | none | any | Details for apegmsh-2.0.0-py3-none-any.whl |
Total release size: 6.1 MB
Release files / apegmsh-2.0.0.tar.gz
| Download URL | apegmsh-2.0.0.tar.gz |
|---|---|
| Size | 3.2 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f3cb2e11d684fc3cef346d7fa1f7145595a2f21f31d5f58704f5b5eb4b2ace26
|
|
BLAKE2b-256 checksum How to use checksums |
0732d1d15ccb306ba281c93d1e6728cf1e15fc110b03bb2d604624184037f153
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 6, 2026.
Transparency logRelease files / apegmsh-2.0.0-py3-none-any.whl
| Download URL | apegmsh-2.0.0-py3-none-any.whl |
|---|---|
| Size | 2.9 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
3edee2a68c0461764fe5b8cb6fecd32a819fd64e5f5976069f19df5d08a96207
|
|
BLAKE2b-256 checksum How to use checksums |
4ff91084ca466421d741f503929ad7f2d84a1c8dbb0eb529a549269d9e3f7633
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 6, 2026.
Transparency logSecurity for apeGmsh 2.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for apegmsh-2.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 6, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













