
Apirelio Django SDK

See the customer behind every API request
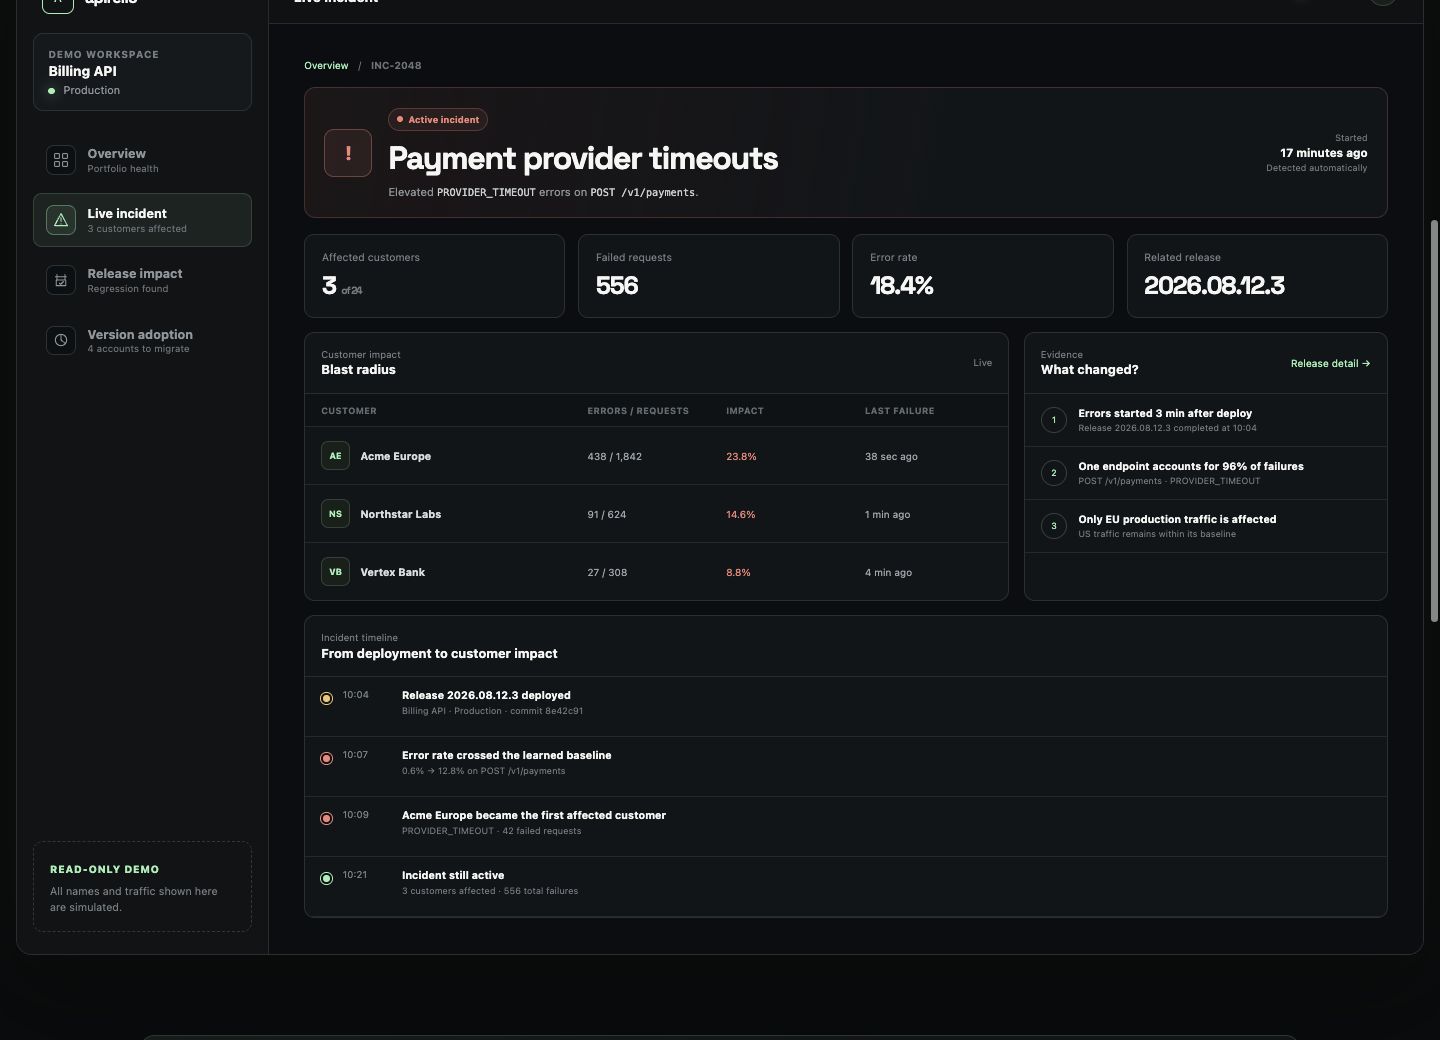
Follow a release regression from the failing endpoint to the exact customer accounts it affects in the public, read-only workspace.
Try it in 30 seconds
pip install apirelio-django
export APIRELIO_API_KEY=apr_live_your_project_key
Copy the minimal setup below or run the quickstart example. Delivery is fail-safe and no request or response payloads are captured.
Documentation · PyPI · Apirelio
Connect Django and DRF API errors, latency and releases to the affected customers without capturing request or response payloads.
Native Django middleware for privacy-safe, customer-aware API analytics. The same package supports regular Django views and Django REST Framework endpoints.
pip install apirelio-django
Add the middleware after Django's authentication middleware so identity resolvers can use
request.user:
# settings.py
import os

MIDDLEWARE = [
    # ...
    "django.contrib.auth.middleware.AuthenticationMiddleware",
    "apirelio_django.ApirelioMiddleware",
]

APIRELIO = {
    "API_KEY": os.environ.get("APIRELIO_API_KEY", ""),
    "ENDPOINT": os.environ.get("APIRELIO_ENDPOINT", "https://apirelio.com"),
    "SERVICE": "billing-api",
    "ENVIRONMENT": "production",
    "INCLUDE_ROUTES": ("/api/**",),
    "EXCLUDE_ROUTES": ("/api/health/", "/api/internal/**"),
    "RESOLVE_CUSTOMER": "billing.apirelio.resolve_customer",
}
Resolvers receive the completed HttpRequest and may return an Apirelio customer, application or
metadata dictionary:
def resolve_customer(request):
    account = getattr(request.user, "account", None)
    if account is None:
        return None
    return {"id": str(account.id), "name": account.name, "plan": account.plan}
The middleware records the final status, duration, resolved URL pattern and DRF error code. Both synchronous and asynchronous Django handlers are supported. Events enter the bounded Python Core background queue and are flushed when the process exits. Bodies, query strings, cookies, authorization values, email addresses and client IP addresses are never captured.
1 maintainer

Metadata
1 maintainer
Release files for apirelio-django 0.2.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| apirelio_django-0.2.1.tar.gz | 10.0 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| apirelio_django-0.2.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 17.3 kB
Release files / apirelio_django-0.2.1.tar.gz
| Download URL | apirelio_django-0.2.1.tar.gz |
|---|---|
| Size | 10.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
0100a14ff9be3c0b93665cf7181ed96d21f91f0ec2f15dc805729825fb2e1b9a
|
|
BLAKE2b-256 checksum How to use checksums |
8f5cba8ef0d7b6ed523500b73d223ec8711dcee30623b136eec46509a5a98379
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 20, 2026.
Transparency logRelease files / apirelio_django-0.2.1-py3-none-any.whl
| Download URL | apirelio_django-0.2.1-py3-none-any.whl |
|---|---|
| Size | 7.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
fc733f8579df9fe2945b3141e39377bcb1cdfb2e8ad4f2c42153254fbef2ce23
|
|
BLAKE2b-256 checksum How to use checksums |
71099d82d5e1a4877337f0104287554f8c40cc915212f4238f1f3292ab6fdeba
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 20, 2026.
Transparency log













