
Documentation: http://www.aquilify.vvfin.in/
AQUILIFY
Aquilify is an ASGI (Asynchronous Server Gateway Interface) framework designed to facilitate the development of web applications with Python. It enables efficient handling of HTTP requests, WebSocket connections, middleware processing, and exception handling in an asynchronous environment.
Installation
$ pip install aquilify
Or you can install the aquilify[full]
$ pip install aquilify[full]
Basic Setup
Create a new aquilify app using the command show below :
$ aquilify create-app myapp
Now, move inside the myapp and run :
$ aquilify runserver
To make changes in ASGI server configuration open myapp/config.cfg :
Default Configuration :
[ASGI_SERVER]
server = NETIX
host = 127.0.0.1
port = 8000
debug = True
reload = False
instance = asgi:application
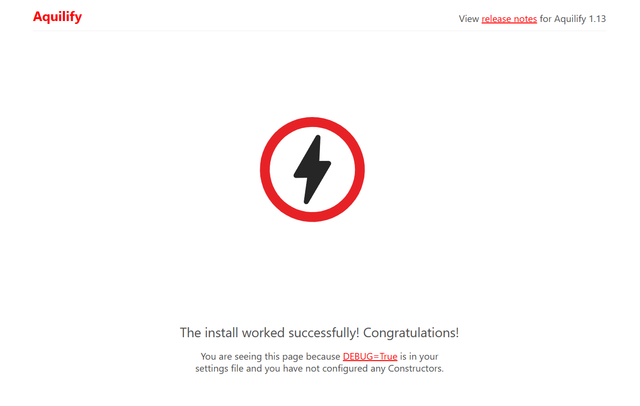
visit: http://localhost:8000
output:
Creating views
myapp/views.py
async def myview() -> dict:
  return {"message": "Welcome to aquilify"}, 200
myapp/routing.py
from aquilify.core.routing import rule

import views

ROUTER = [
  rule('/', view.myview)
]
run server
$ aquilify runserver
Starting Netix v1.12 (cpython 3.12.1, win32)
------------------------------------------------------------------------
Options:
  run(host=127.0.0.1, port=8000, reuse_port=True, worker_num=1, ssl={}, debug=True, app=asgi:application, log_level=DEBUG)
------------------------------------------------------------------------
[2024-01-08 15:48:19] Netix detected Aquilify starting.. : Aquilify
[2024-01-08 15:48:19,421] INFO: lifespan: startup
[2024-01-08 15:48:19,423] INFO: lifespan.startup.complete
[2024-01-08 15:48:20] Netix (ASGI) (pid 17892) is started at 127.0.0.1 port 8000
output : http://localhost:8000/ :
{
    "message": "Welcome to aquilify"
}
Credits
- Thanks to
starlette. - This project uses code adapted from the Starlette framework.
Dependencies
Aquilify only requires anyio, and the following are optional:
- [
aiofiles][aiofile] - Required if you want to use theStaticMIddlewareorFile based Opertation. - [
jinja2][jinja2] - Required if you want to useTemplateResponse. - [
python-multipart][python-multipart] - Required if you want to support form parsing, withrequest.form(). - [
itsdangerous][itsdangerous] - Required forSessionMiddlewareandCSRFsupport. - [
markupsafe][markupsafe] - Required forJinja2andCSRFsupport.
1 maintainer

Metadata
1 maintainer
Release files for aquilify 1.17
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| aquilify-1.17.tar.gz | 275.1 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| aquilify-1.17-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 668.4 kB
Release files / aquilify-1.17.tar.gz
| Download URL | aquilify-1.17.tar.gz |
|---|---|
| Size | 275.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
8e9802453fd5d324ed6104692780a76bab09ed12c08061b9efd72f60f7687c18
|
|
BLAKE2b-256 checksum How to use checksums |
cc182ecaec90c8d03cbf5ba45c632ebcfab58f0b46be25448c5dbff63219953e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.12.2
|
Release files / aquilify-1.17-py3-none-any.whl
| Download URL | aquilify-1.17-py3-none-any.whl |
|---|---|
| Size | 393.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
be165caf78b4e7933a64d39828fef64073a1a9abc11b814ad08ccacca3c31556
|
|
BLAKE2b-256 checksum How to use checksums |
4c82a1e688e901521d1c1363f629e72639956d2574fed17fd509814ed04dae9c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.12.2
|
Security for aquilify 1.17
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














