
Build provenance: This package is built and distributed by Astral as part of
astral-dev-toolchain. It packagescargo-auditfrom tagcargo-audit/v0.22.2at commit281452c35cf0870969042374110f099a411bc185.
RustSec: cargo audit



Audit your dependencies for crates with security vulnerabilities reported to the RustSec Advisory Database.
Related Experimental Tool
If you want additional function-level reachability context, see
reachsec, an experimental standalone
companion to cargo audit.
Requirements
cargo audit requires Rust 1.74 or later.
Installation

cargo audit is a Cargo subcommand and can be installed with cargo install:
$ cargo install cargo-audit
Once installed, run cargo audit at the toplevel of any Cargo project.
Alpine Linux
# apk add cargo-audit
Arch Linux
# pacman -S cargo-audit
MacOS
$ brew install cargo-audit
OpenBSD
# pkg_add cargo-audit
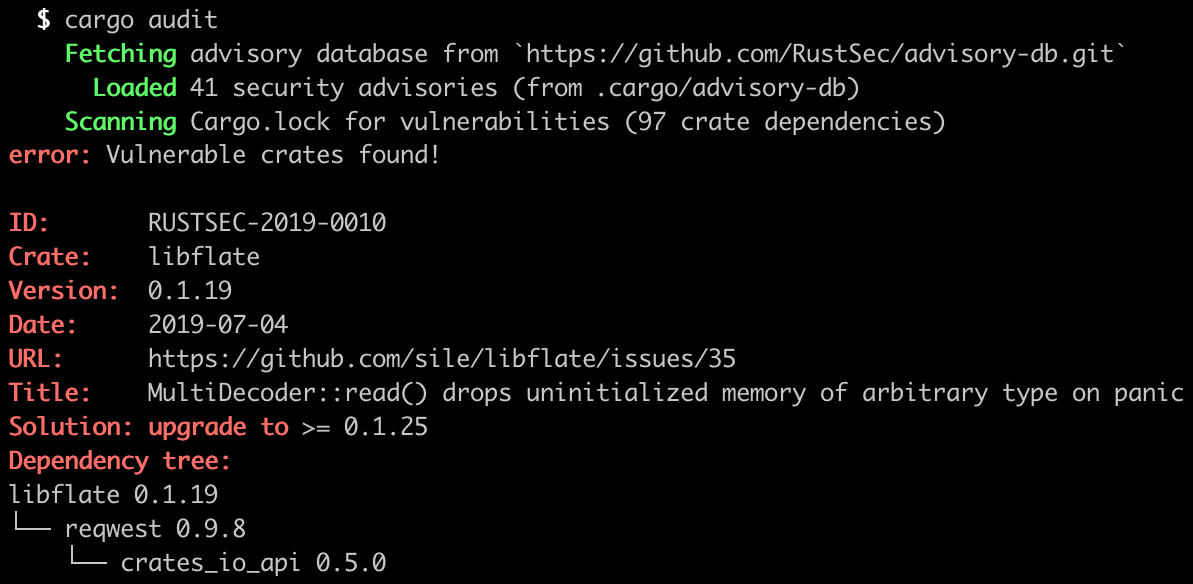
Screenshot
cargo audit fix subcommand
This tool supports an experimental feature to automatically update Cargo.toml
to fix vulnerable dependency requirements.
To enable it, install cargo audit with the fix feature enabled:
$ cargo install cargo-audit --features=fix
Once installed, run cargo audit fix to automatically fix vulnerable
dependency requirements in your Cargo.toml:
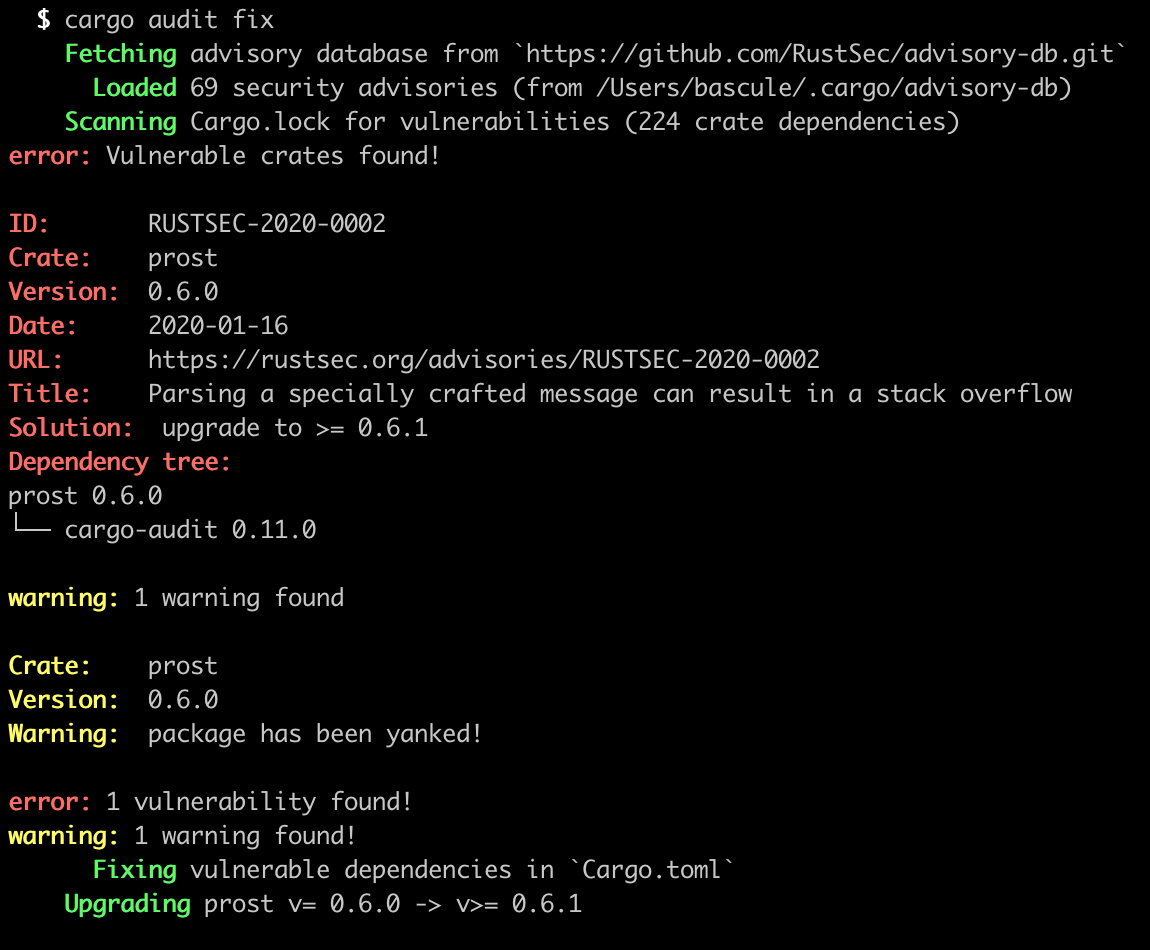
This will modify Cargo.toml in place. To perform a dry run instead, which
shows a preview of what dependencies would be upgraded, run
cargo audit fix --dry-run.
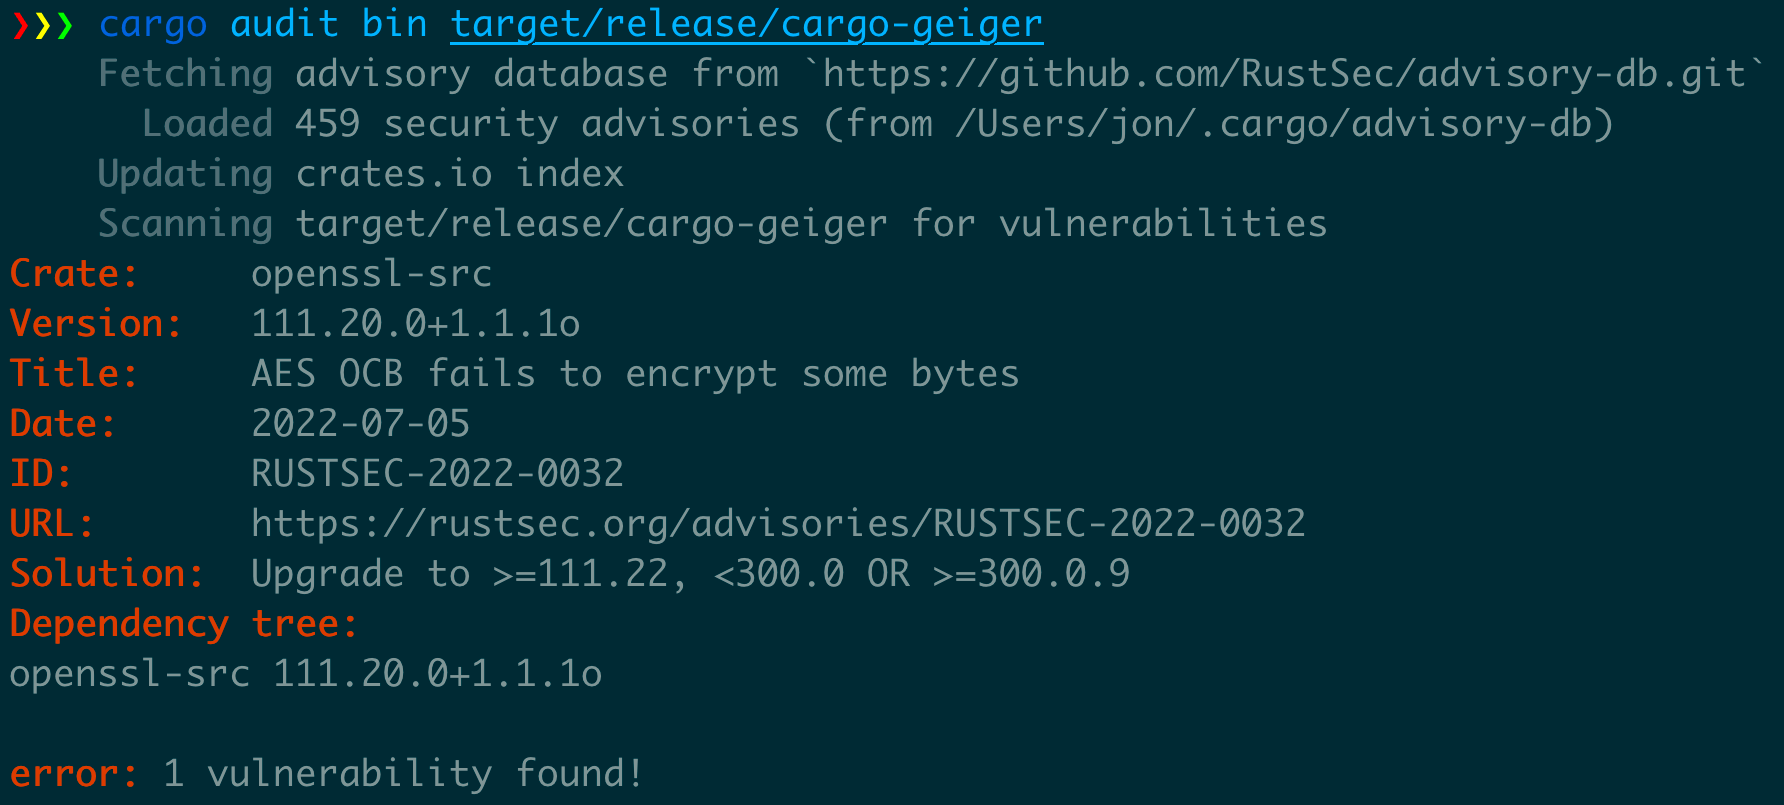
cargo audit bin subcommand
Run cargo audit bin followed by the paths to your binaries to audit them:
You can scan a directory recursively using fd:
fd --type=executable --exec-batch cargo audit bin
If your programs have been compiled with cargo auditable,
the audit is fully accurate because all the necessary information is embedded in the compiled binary.
For binaries that were not compiled with cargo auditable
it will recover a part of the dependency list by parsing panic messages.
This will miss any embedded C code (e.g. OpenSSL) as well as roughly half of the Rust dependencies
because the Rust compiler is very good at removing unnecessary panics,
but that's better than having no vulnerability information whatsoever.
Ignoring advisories
The first and best way to fix a vulnerability is to upgrade the vulnerable crate.
But there may be situations where an upgrade isn't available and the advisory doesn't affect your application. For example the advisory might involve a cargo feature or API that is unused.
In these cases, you can ignore advisories using the --ignore option.
$ cargo audit --ignore RUSTSEC-2017-0001
This option can also be configured via the audit.toml file.
Using cargo audit on Travis CI
To automatically run cargo audit on every build in Travis CI, you can add the following to your .travis.yml:
language: rust
cache: cargo # cache cargo-audit once installed
before_script:
  - cargo install --force cargo-audit
  - cargo generate-lockfile
script:
  - cargo audit
Using cargo audit on GitHub Action
Please use audit-check action directly.
Reporting Vulnerabilities
Report vulnerabilities by opening pull requests against the RustSec Advisory Database GitHub repo:
License
Licensed under either of:
- Apache License, Version 2.0 (LICENSE-APACHE or https://www.apache.org/licenses/LICENSE-2.0)
- MIT license (LICENSE-MIT or https://opensource.org/licenses/MIT)
at your option.
Contribution
Unless you explicitly state otherwise, any contribution intentionally submitted for inclusion in the work by you shall be dual licensed as above, without any additional terms or conditions.
Release files for astral-dev-toolchain-cargo-audit 0.22.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| astral_dev_toolchain_cargo_audit-0.22.2-py3-none-win_arm64.whl | Python 3 | none | Windows ARM64 | Details |
| astral_dev_toolchain_cargo_audit-0.22.2-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| astral_dev_toolchain_cargo_audit-0.22.2-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64 | Details |
| astral_dev_toolchain_cargo_audit-0.22.2-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64 | Details |
| astral_dev_toolchain_cargo_audit-0.22.2-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details |
| astral_dev_toolchain_cargo_audit-0.22.2-py3-none-macosx_10_12_x86_64.whl | Python 3 | none | macOS 10.12+ x86-64 | Details |
Total release size: 38.9 MB
Release files / astral_dev_toolchain_cargo_audit-0.22.2-py3-none-win_arm64.whl
| Download URL | astral_dev_toolchain_cargo_audit-0.22.2-py3-none-win_arm64.whl |
|---|---|
| Size | 6.4 MB |
| Tags | Python 3 Windows ARM64 |
|
SHA-256 checksum How to use checksums |
1295c810c2fd3716f711edb89f17102e2c5843e1e168b33363cad000758c0e40
|
|
BLAKE2b-256 checksum How to use checksums |
ea2f5b89f6fc21b7cf71f7beab7c3971637e8de332aa44a389410dcd33c406f1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.6 {"installer":{"name":"uv","version":"0.12.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logRelease files / astral_dev_toolchain_cargo_audit-0.22.2-py3-none-win_amd64.whl
| Download URL | astral_dev_toolchain_cargo_audit-0.22.2-py3-none-win_amd64.whl |
|---|---|
| Size | 6.7 MB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
ca4cc785faa108091a955d2f8d322e97438a0a9f1dc329b0f28f4cc3f84f2af5
|
|
BLAKE2b-256 checksum How to use checksums |
966f41b634c4ec2301c2aa06395ad9edbc668ffd1fa6c0671d3cafafe793e52f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.6 {"installer":{"name":"uv","version":"0.12.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logRelease files / astral_dev_toolchain_cargo_audit-0.22.2-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | astral_dev_toolchain_cargo_audit-0.22.2-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 6.8 MB |
| Tags | Linux glibc 2.17+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
08c93fa1f2548f39fd56614496b3629388ccb7df1962f3c6cf9913940e60c40e
|
|
BLAKE2b-256 checksum How to use checksums |
2a19daf2941c20e19f423da48b6eb03969c76be2c7031d4ad33ce862d92e64c1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.6 {"installer":{"name":"uv","version":"0.12.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logRelease files / astral_dev_toolchain_cargo_audit-0.22.2-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | astral_dev_toolchain_cargo_audit-0.22.2-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 6.4 MB |
| Tags | Linux glibc 2.17+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
9a1079816e0a8dc7bb944e6330e17f3ced31b6f42148dd4771571e65bfd8b127
|
|
BLAKE2b-256 checksum How to use checksums |
1acfcf09555b25879fc0dfee061fd50d0e293087be55c65dfa9a55a7a7ed36c3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.6 {"installer":{"name":"uv","version":"0.12.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logRelease files / astral_dev_toolchain_cargo_audit-0.22.2-py3-none-macosx_11_0_arm64.whl
| Download URL | astral_dev_toolchain_cargo_audit-0.22.2-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 6.2 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
c03a59d970ed80b985d06be7aeac8d762f887b6a309f093bcb9943f5fe0108bd
|
|
BLAKE2b-256 checksum How to use checksums |
bb1063aac1ed165b6aadf1a02e4691546f58927f2490627e1c051655cb7ab930
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.6 {"installer":{"name":"uv","version":"0.12.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency logRelease files / astral_dev_toolchain_cargo_audit-0.22.2-py3-none-macosx_10_12_x86_64.whl
| Download URL | astral_dev_toolchain_cargo_audit-0.22.2-py3-none-macosx_10_12_x86_64.whl |
|---|---|
| Size | 6.5 MB |
| Tags | Python 3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
f010ac148da38fb562934e3a91e56cf14771c59e569ad2e12268791b02edf81b
|
|
BLAKE2b-256 checksum How to use checksums |
a67c9716acf566440a6eb0b173f50a0b0e9b96f4d1f5ddfe649e4b902d95557a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.6 {"installer":{"name":"uv","version":"0.12.6","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 25, 2026.
Transparency log












