
Build provenance: This package is built and distributed by Astral as part of
astral-dev-toolchain. It packagescritcmpfrom tag0.1.8at commiteccc77b50f847be82b4790260fda6721fdf1b181.
critcmp
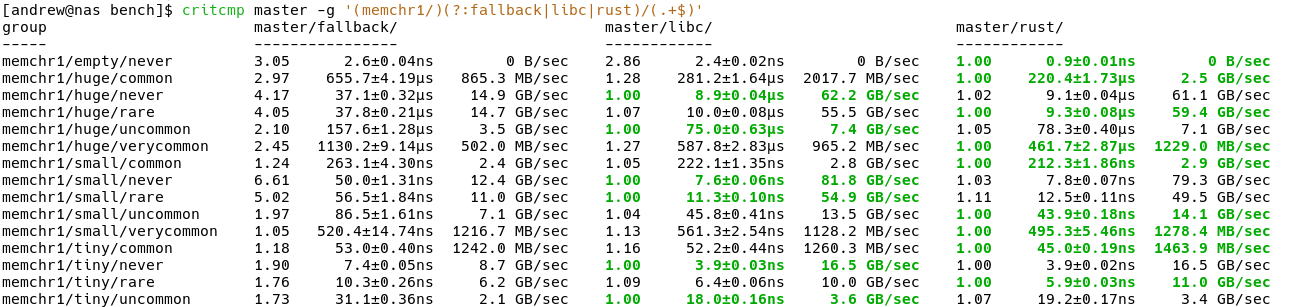
A command line tool to for comparing benchmarks run by Criterion. This supports comparing benchmarks both across and inside baselines, where a "baseline" is a collection of benchmark data produced by Criterion for a single run.


Dual-licensed under MIT or the UNLICENSE.
Installation
Since this tool is primarily for use with the Criterion benchmark harness for Rust, you should install it with Cargo:
$ cargo install critcmp
critcmp's minimum supported Rust version is the current stable release.
WARNING: This tool explicitly reads undocumented internal data emitted by Criterion, which means this tool can break at any point if Criterion's internal data format changes.
critcmp is known to work with Criterion 0.3.3. This project will track the latest release of Criterion if breaking changes to Criterion's internal format occur, but will also attempt to keep working on older versions within reason.
Example
Usage
critcmp works by slurping up all benchmark data from Criterion's target directory, in addition to extra data supplied as positional parameters. The primary unit that critcmp works with is Criterion's baselines. That is, the simplest way to use critcmp is to save two baselines with Criterion's benchmark harness and then compare them. For example:
$ cargo bench -- --save-baseline before
$ cargo bench -- --save-baseline change
$ critcmp before change
Filtering can be done with the -f/--filter flag to limit comparisons based on a regex:
$ critcmp before change -f 'foo.*bar'
Comparisons with very small differences can also be filtered out. For example, this hides comparisons with differences of 5% or less
$ critcmp before change -t 5
Comparisons are not limited to only two baselines. Many can be used:
$ critcmp before change1 change2
The list of available baselines known to critcmp can be printed:
$ critcmp --baselines
A baseline can exported to one JSON file for more permanent storage outside of Criterion's target directory:
$ critcmp --export before > before.json
$ critcmp --export change > change.json
Baselines saved this way can be used by simply using their file path instead of just the name:
$ critcmp before.json change.json
Benchmarks within the same baseline can be compared as well. Normally, benchmarks are compared based on their name. That is, given two baselines, the correspondence between benchmarks is established by their name. Sometimes, however, you'll want to compare benchmarks that don't have the same name. This can be done by expressing the matching criteria via a regex. For example, given benchmarks 'optimized/input1' and 'naive/input1' in the baseline 'benches', the following will show a comparison between the two benchmarks despite the fact that they have different names:
$ critcmp benches -g '\w+/(input1)'
That is, the matching criteria is determined by the values matched by all of the capturing groups in the regex. All benchmarks with equivalent capturing groups will be included in one comparison. There is no limit on the number of benchmarks that can appear in a single comparison.
Finally, if comparisons grow too large to see in the default column oriented display, then the results can be flattened into lists:
$ critcmp before change1 change2 change3 change4 change5 --list
Motivation
This tool is similar to cargo-benchcmp, but it works on data gathered by Criterion.
In particular, Criterion emits loads of useful data, but its facilities for interactively comparing benchmarks and analyzing benchmarks in the aggregate are exceedingly limited. Criterion does provide the ability to save benchmark results as a "baseline," and this is primarily the data with which critcmp works with. In particular, while Criterion will show changes between a saved baseline and the current benchmark, there is no way to do further comparative analysis by looking at benchmark results in different views.
Release files for astral-dev-toolchain-critcmp 0.1.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| astral_dev_toolchain_critcmp-0.1.8-py3-none-win_arm64.whl | Python 3 | none | Windows ARM64 | Details |
| astral_dev_toolchain_critcmp-0.1.8-py3-none-win_amd64.whl | Python 3 | none | Windows x86-64 | Details |
| astral_dev_toolchain_critcmp-0.1.8-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64 | Details |
| astral_dev_toolchain_critcmp-0.1.8-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | Python 3 | none | Linux glibc 2.17+ ARM64 | Details |
| astral_dev_toolchain_critcmp-0.1.8-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details |
| astral_dev_toolchain_critcmp-0.1.8-py3-none-macosx_10_12_x86_64.whl | Python 3 | none | macOS 10.12+ x86-64 | Details |
Total release size: 25.6 MB
Release files / astral_dev_toolchain_critcmp-0.1.8-py3-none-win_arm64.whl
| Download URL | astral_dev_toolchain_critcmp-0.1.8-py3-none-win_arm64.whl |
|---|---|
| Size | 912.4 kB |
| Tags | Python 3 Windows ARM64 |
|
SHA-256 checksum How to use checksums |
e8d83fe0253655fc311aa2f73bef320dd0369c81fbb0e7fc47950fca035d8cfb
|
|
BLAKE2b-256 checksum How to use checksums |
a25a7decb1d6e9701854cd3c6312cef5b12f72d1031d75e1815e99b62a0a4830
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.9 {"installer":{"name":"uv","version":"0.12.9","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 3, 2026.
Transparency logRelease files / astral_dev_toolchain_critcmp-0.1.8-py3-none-win_amd64.whl
| Download URL | astral_dev_toolchain_critcmp-0.1.8-py3-none-win_amd64.whl |
|---|---|
| Size | 993.3 kB |
| Tags | Python 3 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
dcc35133cc5a58413bceaed128d09185608599393d1fd9329abdb169bee99aac
|
|
BLAKE2b-256 checksum How to use checksums |
523f2cc609dc6819ad14e8e10685f0c0af561e8ec088f7eb494d69167dec842f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.9 {"installer":{"name":"uv","version":"0.12.9","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 3, 2026.
Transparency logRelease files / astral_dev_toolchain_critcmp-0.1.8-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | astral_dev_toolchain_critcmp-0.1.8-py3-none-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 11.0 MB |
| Tags | Linux glibc 2.17+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
72f85046daab4edfab29dbe82cff3b442cb70598949a5e235d35fc3b3f251e5b
|
|
BLAKE2b-256 checksum How to use checksums |
b87dc1b7255fb8f10b6c04bade1e1c19fa25fe00df0808ba08c2ba5a7b597728
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.9 {"installer":{"name":"uv","version":"0.12.9","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 3, 2026.
Transparency logRelease files / astral_dev_toolchain_critcmp-0.1.8-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | astral_dev_toolchain_critcmp-0.1.8-py3-none-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 10.4 MB |
| Tags | Linux glibc 2.17+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
96984c1549e00900bd35def5deb1e827edf37320a5e78ce83fabbc8b88dab1ce
|
|
BLAKE2b-256 checksum How to use checksums |
0c9522d5e77905d3bddf70829a4aa5ac7df9e14242f61352bc85322fceeca3ee
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.9 {"installer":{"name":"uv","version":"0.12.9","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 3, 2026.
Transparency logRelease files / astral_dev_toolchain_critcmp-0.1.8-py3-none-macosx_11_0_arm64.whl
| Download URL | astral_dev_toolchain_critcmp-0.1.8-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 1.1 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
91888ab61fd6cee3eb216e7cf53edb356071441567c3d16bb7ceac992cea7de1
|
|
BLAKE2b-256 checksum How to use checksums |
d6223d4c760ddf983b923946eaf2ffd19e325f8f5ccef15d8033a4a400342a95
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.9 {"installer":{"name":"uv","version":"0.12.9","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 3, 2026.
Transparency logRelease files / astral_dev_toolchain_critcmp-0.1.8-py3-none-macosx_10_12_x86_64.whl
| Download URL | astral_dev_toolchain_critcmp-0.1.8-py3-none-macosx_10_12_x86_64.whl |
|---|---|
| Size | 1.2 MB |
| Tags | Python 3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
c5d3d12917b4e7172c6827a46302a01da01a178076f4b03e1c49471b054d94e1
|
|
BLAKE2b-256 checksum How to use checksums |
cfdf081c4e1e435b96c2d489ab003b18307a0e0611e836aa39579c404aa08590
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
uv/0.12.9 {"installer":{"name":"uv","version":"0.12.9","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":{"name":"Ubuntu","version":"24.04","id":"noble","libc":null},"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":true}
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 3, 2026.
Transparency log












