
Agent Trace Analysis Platform (atap)
The attribution & recovery layer on top of your existing agent observability stack (e.g. Langfuse) — find, explain, and fix LLM-agent failures, then write the answers back as scores


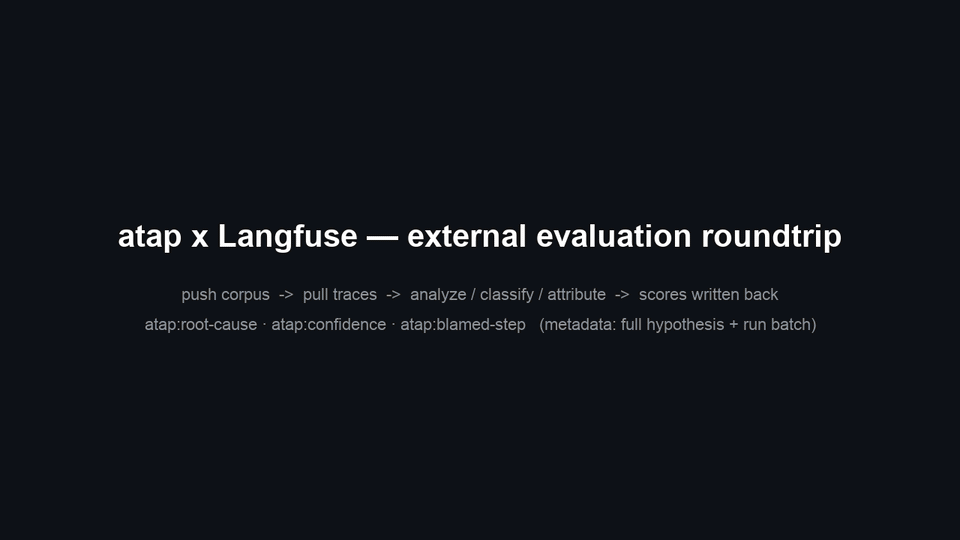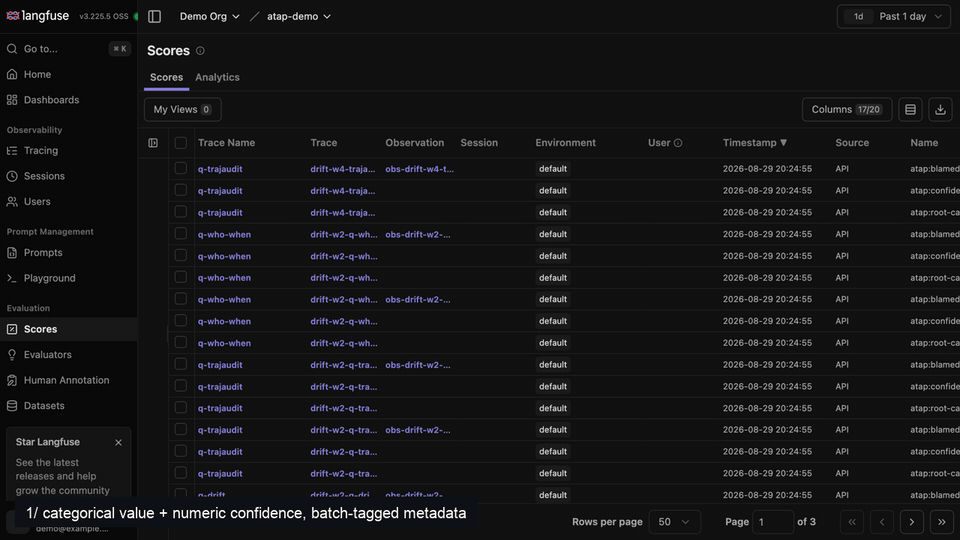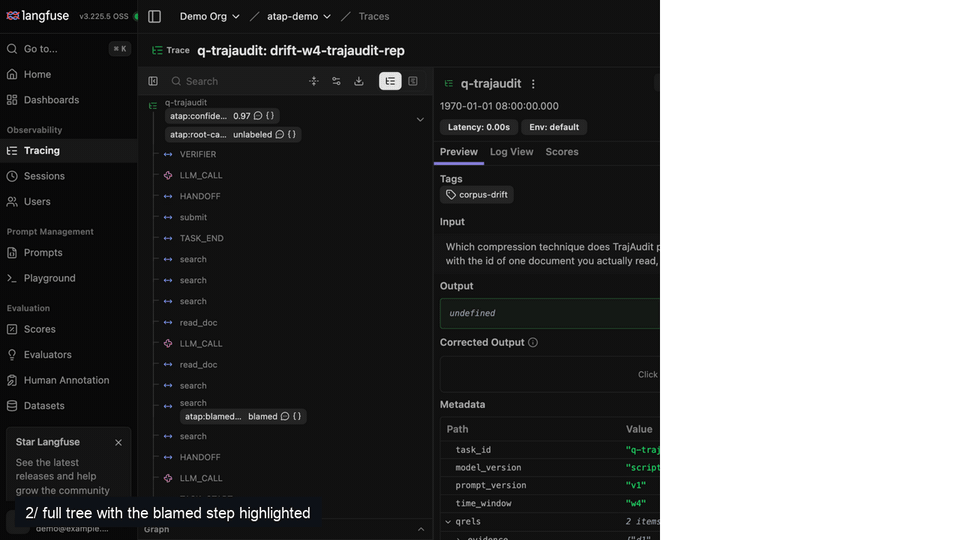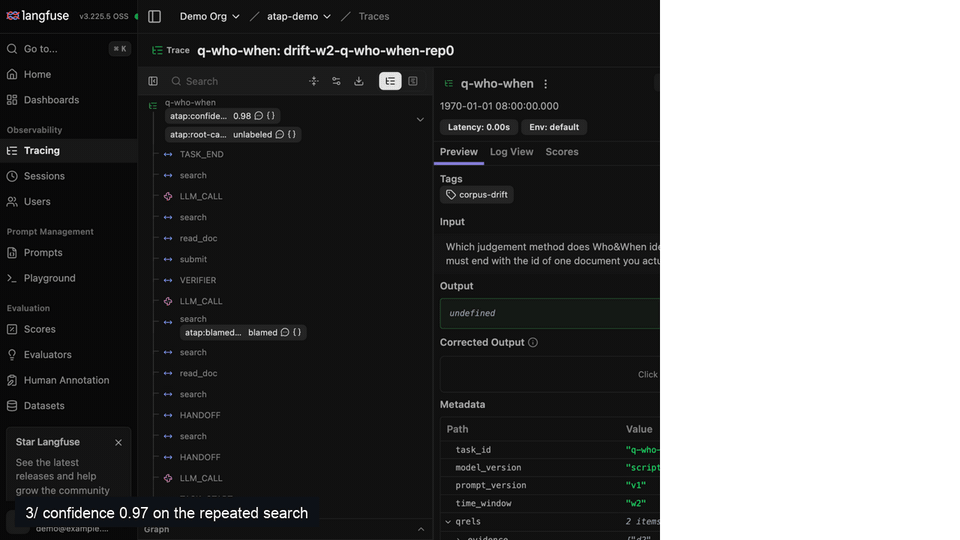
atap × Langfuse: pull live traces → analyze / classify / attribute → root-cause + confidence + blamed-step written back as Scores
atap pulls traces from Langfuse (or JSONL / OTel / Phoenix exports), locates the responsible agent and the decisive step of every failure, and writes the verdicts back as Langfuse scores.
- 24 pluggable algorithms, 5 stages — one module each, YAML-composed, artifact-coupled
- Deterministic offline mode — FakeLLM judge + fault-injected sandbox, zero network
- Real LLMs — any OpenAI-compatible API, per-call audit log
- Langfuse integration —
atap langfuse-evalwrites root-cause scores + blamed-step markers back onto your traces - Closed loop — one shared
Hypothesiscontract; recovered reruns re-enter analysis for verification
Results on real data
First external benchmark: Who&When (ICML 2025) — 184 real multi-agent failure trajectories, gold hidden from the judge, scored with the stock evaluator:
| Stack (deepseek-v4-flash) | step hit | agent hit | cost |
|---|---|---|---|
| all_at_once | 33.2% | 56.0%† | $1.43 · 2.9h |
| all_at_once, thinking off | 33.2% | 54.3% | $0.16 · 9min |
| binary_search | 11.4% | 34.2% | $0.26 · 32min |
vs the paper's GPT-4o baseline (Without-GT): step-level 2.9× on algorithm-generated (13.5% → 38.9%) and 5.9× on hand-crafted (3.5% → 20.7%) — on a cheaper model.
Quick start
pip install atap
atap demo    # offline end-to-end pipeline: FakeLLM judge, deterministic, zero network
Real-LLM runs, live-Langfuse round trips, the full head-to-head table, caveats and reproduction commands:
https://github.com/aaronlyt/agent-trace-analysis-platform
† hand-crafted agent figures corrected for a Magentic-One routing-label scoring artifact; the judge model differs from the paper's GPT-4o, so gains reflect prompt engineering + model — details and a controlled-ablation recipe in the repo's benchmark report.
1 maintainer

Metadata
1 maintainer
Release files for atap 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| atap-0.1.0.tar.gz | 279.4 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| atap-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 505.3 kB
Release files / atap-0.1.0.tar.gz
| Download URL | atap-0.1.0.tar.gz |
|---|---|
| Size | 279.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
dad716ed786cbcec211d121844c2b0ea714553bf67c16daf50d4a85e68e78e9f
|
|
BLAKE2b-256 checksum How to use checksums |
608505cc4266c0229372a639f4631b05dc718233e52f2e7cd1da568d0fba1c87
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency logRelease files / atap-0.1.0-py3-none-any.whl
| Download URL | atap-0.1.0-py3-none-any.whl |
|---|---|
| Size | 225.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
b351b01161941f3f3e307c83725820a7e9b9cf89ada659ffb3eea4d1f572323f
|
|
BLAKE2b-256 checksum How to use checksums |
2a271d7588940598467f620b147b44d6f6a0989d47b0b50d35660cfbb4ae521c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency log












