
AttackMap
Local-first, AI-assisted defensive security analysis for codebases. AttackMap reads a repository (or a whole fleet of them), reconstructs the attack surface — routes, data stores, external calls, auth signals, trust boundaries — traces request-to-sink data flow, and produces an evidence-grounded, prioritized security review. It finds the cross-cutting weaknesses single-file scanners miss, and never sends your code anywhere.


Status: beta (v0.6.4). Core engine + 15 analyzer plugins, published on PyPI and validated on real codebases. AttackMap is heuristic by design — findings are confidence-tiered evidence, not proof. Roadmap to 1.0: issue #209.
Full documentation: docs.mlaify.io · architecture & internals: wiki.
The macOS app
Prefer a GUI? A native macOS front-end drives this CLI and renders every result view. Install it with Homebrew (this also installs the CLI), or build it from source at mlaify/AttackMap-mac:
brew install --cask mlaify/tap/attackmap-app
| Overview | Exploitability |
|---|---|
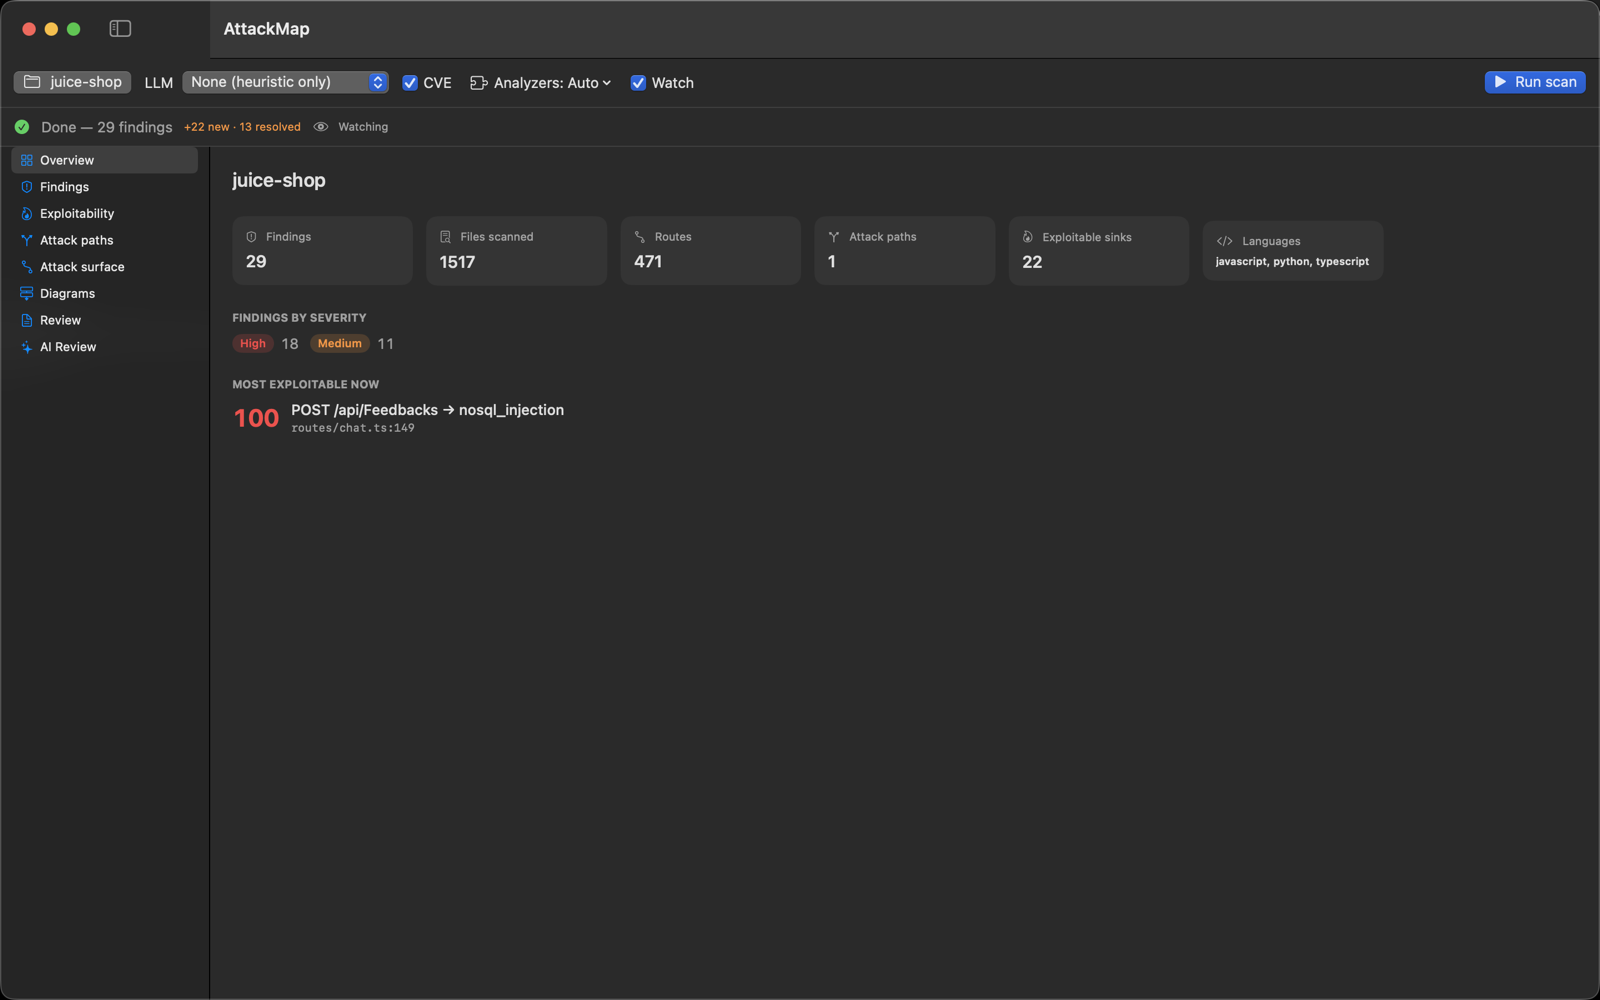 |
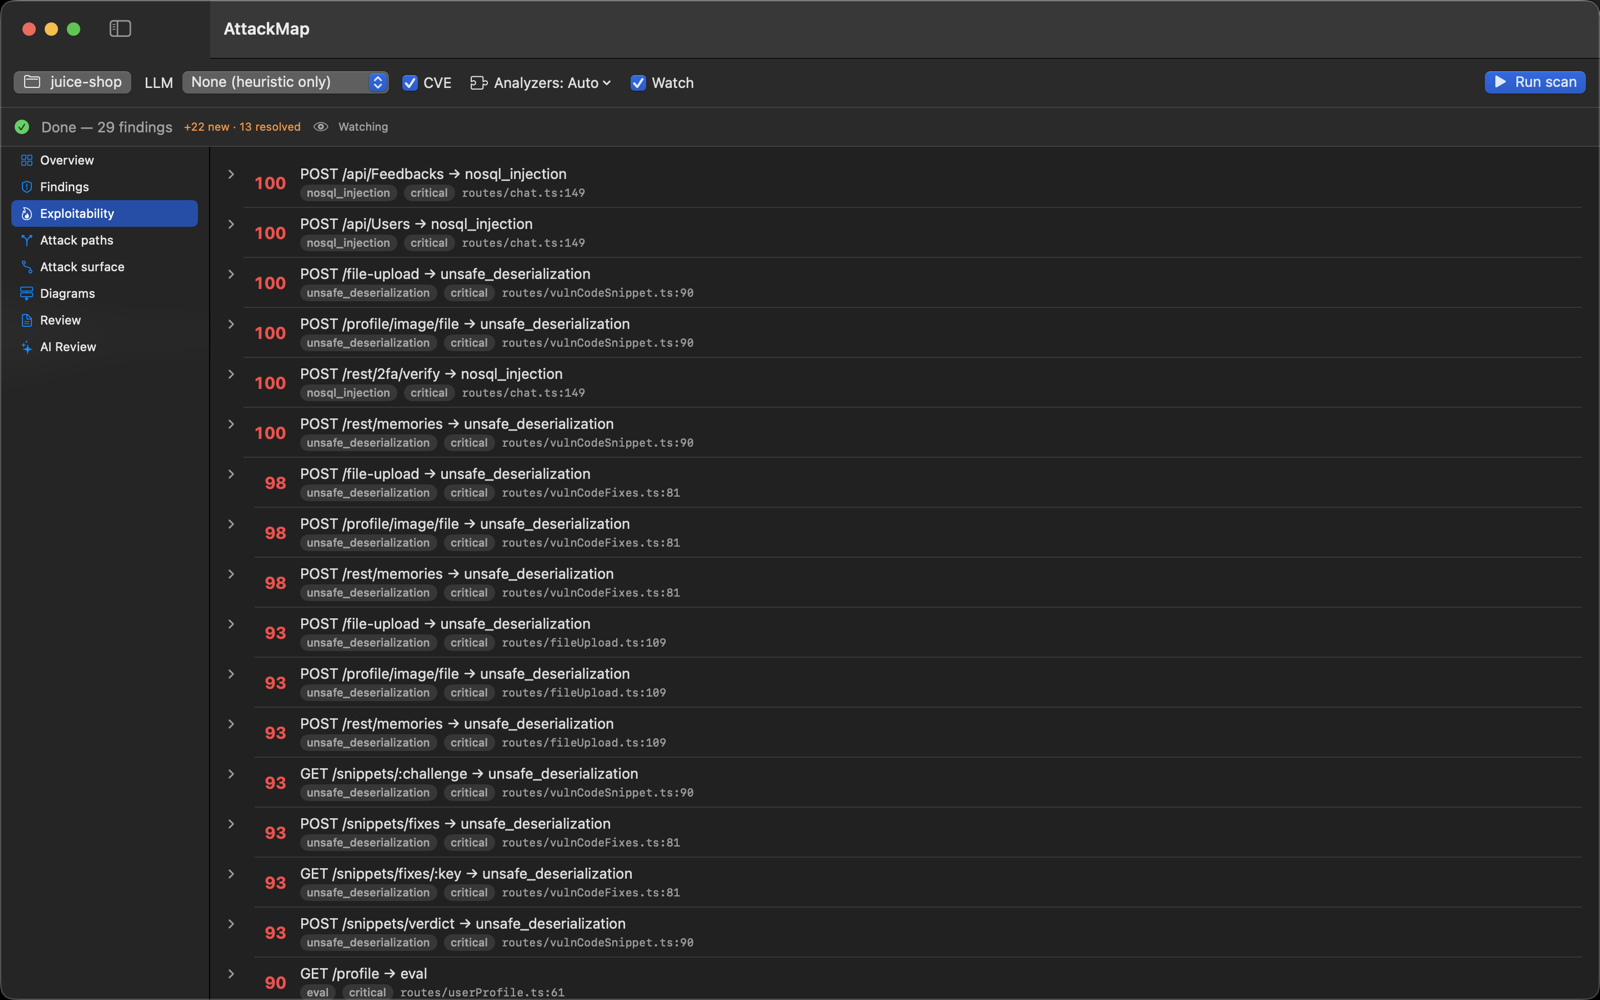 |
Scanning OWASP Juice Shop. Walkthrough in the macOS app docs; source at mlaify/AttackMap-mac.
Quickstart
brew install mlaify/tap/attackmap         # Homebrew: CLI + all 15 analyzer plugins
# or, from PyPI: uv tool install "attackmap[all]"   (or pipx install "attackmap[all]")
attackmap analyze /path/to/repo           # heuristic review → reports/
attackmap analyze /path/to/repo --llm     # + AI-narrated review (Claude or OpenAI)
attackmap analyze ./svc-a ./svc-b ./gw    # cross-repo / fleet scan
Read reports/defensive-review.md for the heuristic review, and (with --llm)
reports/defensive-review-llm.md for the AI narration. --llm resolves auth
automatically (ANTHROPIC_API_KEY, or your Claude/codex CLI subscription); add
--llm-provider openai for OpenAI/Codex.
Other install paths: pip install git+https://github.com/mlaify/AttackMap.git (core
only), or the [llm] extra for AI narration. Not sure
which analyzer plugins a repo needs? attackmap suggest ./repo. Full install and
CI setup: install guide.
What it finds
- Attack-surface recon — routes, data stores, external calls, auth signals,
secrets, frameworks, entrypoints; every signal carries a
file:linecitation, evidence snippet, and confidence. - Data-flow / injection taint (Python, JS/TS, Go, PHP, Java, C#, Ruby) —
SQL, shell, eval/code and expression (SpEL/OGNL) injection, JNDI, SSRF, SSTI,
NoSQL, LDAP, XPath, path traversal and zip-slip, deserialization, open
redirect, header and regex injection — traced source → variable → sink
inside each handler, with flow-bound sanitizers, SARIF
codeFlows, a plugin-extensible sink registry (taint_sinks.yaml), and a deterministic 0–100 exploitability score. - Novel vuln classes — prototype pollution, mass assignment, JWT, XXE, ReDoS, insecure upload, GraphQL exposure; BOLA/IDOR authorization; insecure-crypto & web-hardening; anomaly/outlier + signature-free invariant mining.
- Dependency CVEs (
--cve) — SBOM + lockfile resolution against OSV.dev, folded into the exploitability score. - Unknown-bug discovery —
--hunt --verify(a multi-pass, majority-vote LLM jury), verifier-gated--recall, and cross-repo / fleet analysis: confused-deputy flows, trust-assumption gaps, and the sibling service that omits a control its peers enforce. - Workflow —
--triage,--remediate, finding suppression, baseline diff gating, SARIF + Mermaid/Graphviz output, and a GitHub Action + PR bot.
Each run writes Markdown, JSON (attackmap-report.json), SARIF 2.1.0, and
diagram artifacts; fleet runs add fleet-summary.{md,json} + fleet-graph.md.
See the outputs reference for the full list.
Supported ecosystems
Fourteen analyzer plugins (each installable on its own; [all] installs every one):
Python, JavaScript/TypeScript (Node services), Go, Java/Kotlin
(Spring), C# (ASP.NET Core), Rust, PHP (web / Laminas / Omeka-S),
C, C++, Terraform, IaC (Docker / compose / GitHub Actions),
AT Protocol. Specialty and experimental analyzers are opt-in: when one
matches a repo, analyze says so, and -m <name> runs it (attackmap modules
shows which). Details: analyzers reference.
Write your own against the documented analyzer SDK.
CLI cheat-sheet
attackmap analyze <path>                  # review a repo (--output dir, --format all|json|markdown)
attackmap analyze repoA repoB …           # multi-repo fleet scan
attackmap analyze <path> --cve            # dependency CVEs (OSV.dev)
attackmap analyze <path> --recall         # widen taint discovery (extra reach = SPECULATIVE)
attackmap analyze <path> --llm            # AI narrative (--llm-provider claude|openai)
attackmap analyze <path> --hunt --verify  # LLM exploit-hypothesis hunt, adjudicated vs. source
attackmap analyze <path> --triage         # cluster/dedupe/rank existing findings
attackmap analyze <path> --remediate      # review-first fix suggestions
attackmap analyze <path> --baseline prev.json --fail-on-new-high   # PR gate
attackmap suggest ./repo                  # recommend analyzer plugins    · attackmap modules  # list installed
Verify-jury knobs (--verify-votes / --hunt-lenses / --hunt-rounds /
--hunt-budget) and suppression (--no-suppress / --suppress-file) are
documented in the CLI reference.
What AttackMap is not
- Not a runtime detector. It's static; its detection hints are leads for your SIEM team, not deployable rules.
- Not a replacement for dedicated SCA.
--cvefolds CVE signal into an architecture-aware narrative; Trivy/Grype/Dependabot go deeper on resolution. - Not a sound taint engine. Taint follows local assignments within one
function (intra-procedural def-use) and a call-graph-refined import walk
across files; it does not follow a value into a helper it is passed to, and
branches are not distinguished. Precision over recall; findings are evidence,
not proof. See the limits in
src/attackmap/taint_flow.py. - Not exhaustive. Heuristic by design, with explicit confidence tiers and guardrails for stale signals.
Documentation & links
- docs.mlaify.io — user guide, install, CLI, analyzers, SDK
- Wiki — architecture, roadmap, contributor references
- Roadmap / Bug Triage / Kanban — project boards · Road to 1.0
CHANGELOG.md·CONTRIBUTING.md·SECURITY.md·VISION.md
Special thanks
AttackMap is built by its contributors.
Contributing
Issues and PRs welcome — see CONTRIBUTING.md. By contributing you agree your contributions will be MIT-licensed.
License
MIT. Copyright (c) 2026 Matthew Davis and AttackMap Contributors.
1 maintainer

Metadata
1 maintainer
Release files for attackmap 0.6.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| attackmap-0.6.4.tar.gz | 812.3 kB | With provenance | Details for attackmap-0.6.4.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| attackmap-0.6.4-py3-none-any.whl | Python 3 | none | any | Details for attackmap-0.6.4-py3-none-any.whl |
Total release size: 1.4 MB
Release files / attackmap-0.6.4.tar.gz
| Download URL | attackmap-0.6.4.tar.gz |
|---|---|
| Size | 812.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b2773950d5face3e3533bdf2f3cb9e3d3b8d7f646e8f45d181c77623c69264ba
|
|
BLAKE2b-256 checksum How to use checksums |
091f52c5f889c361d87e78895264b0b3dad4dc54931d598bd79a002e047d6fe6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logRelease files / attackmap-0.6.4-py3-none-any.whl
| Download URL | attackmap-0.6.4-py3-none-any.whl |
|---|---|
| Size | 555.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7c10b1a88601503513ac880345ef9c2b491a60917e71e44005ddc97cfc48db69
|
|
BLAKE2b-256 checksum How to use checksums |
fc36a197385beef1dcd683ed3fe336e43d7f9f5e01e8a029352503e4c635514a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logSecurity for attackmap 0.6.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for attackmap-0.6.4.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














