
autocrop-rs


Finds the actual content inside a screenshot and crops away letterbox bars, app chrome and meme text, while leaving photos, art and manga pages untouched. Python bindings for the Rust autocrop crate: the package installs as autocrop-rs, imports as autocrop_rs and ships the command line as uvx autocrop-rs.
Example
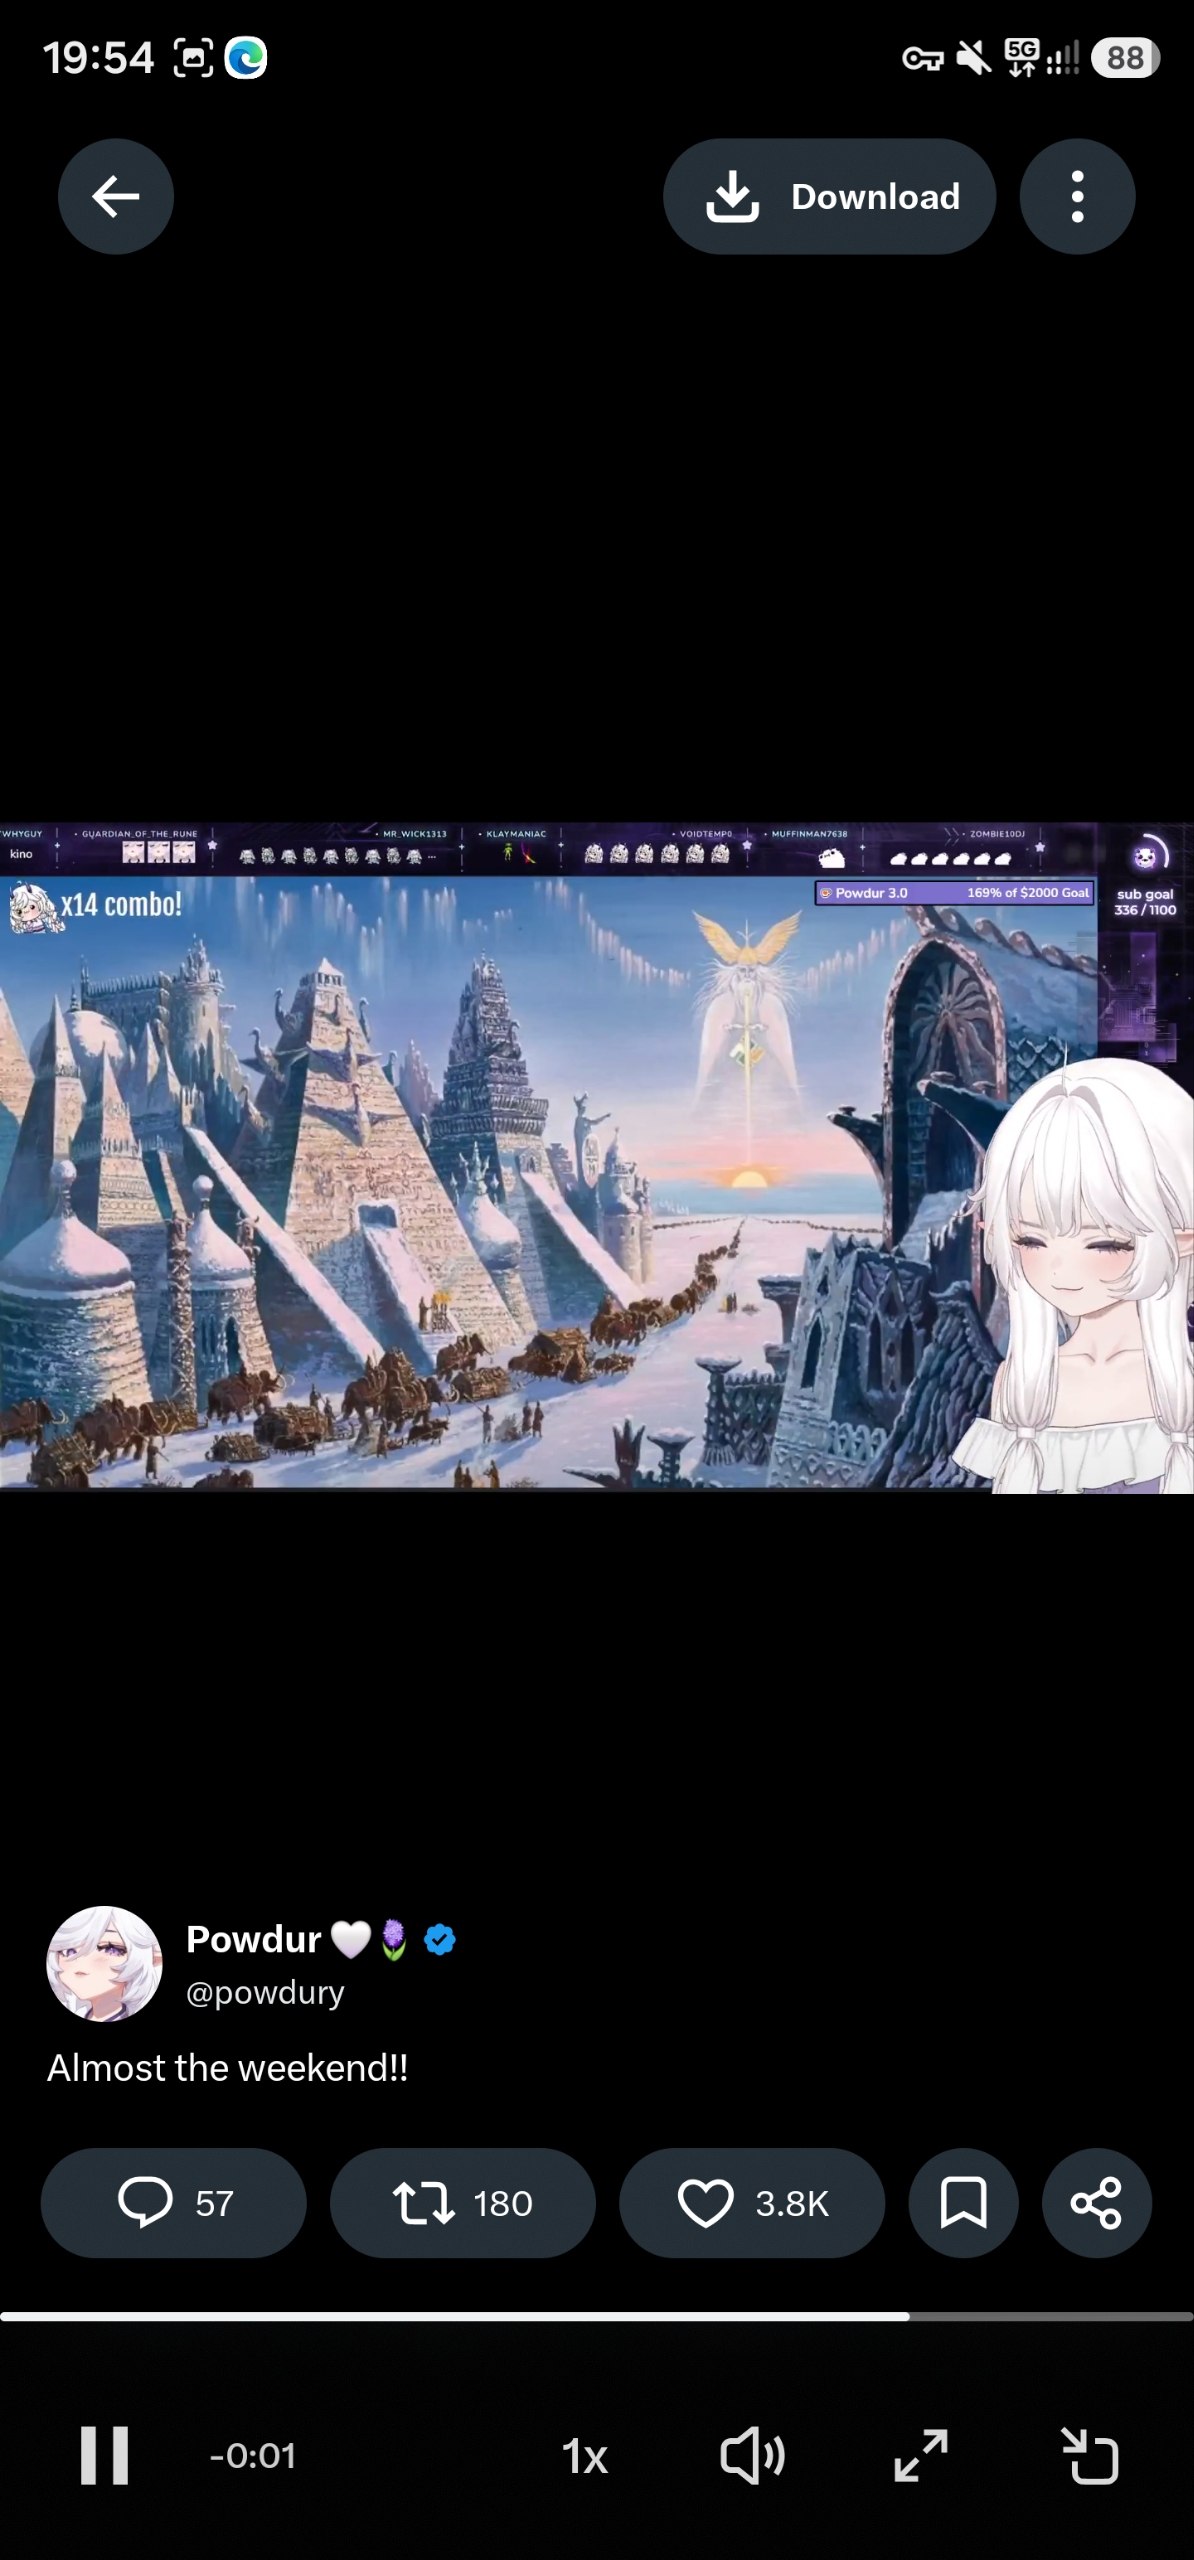
A phone screenshot of a tweet with an embedded stream clip (1194 x 2560), the
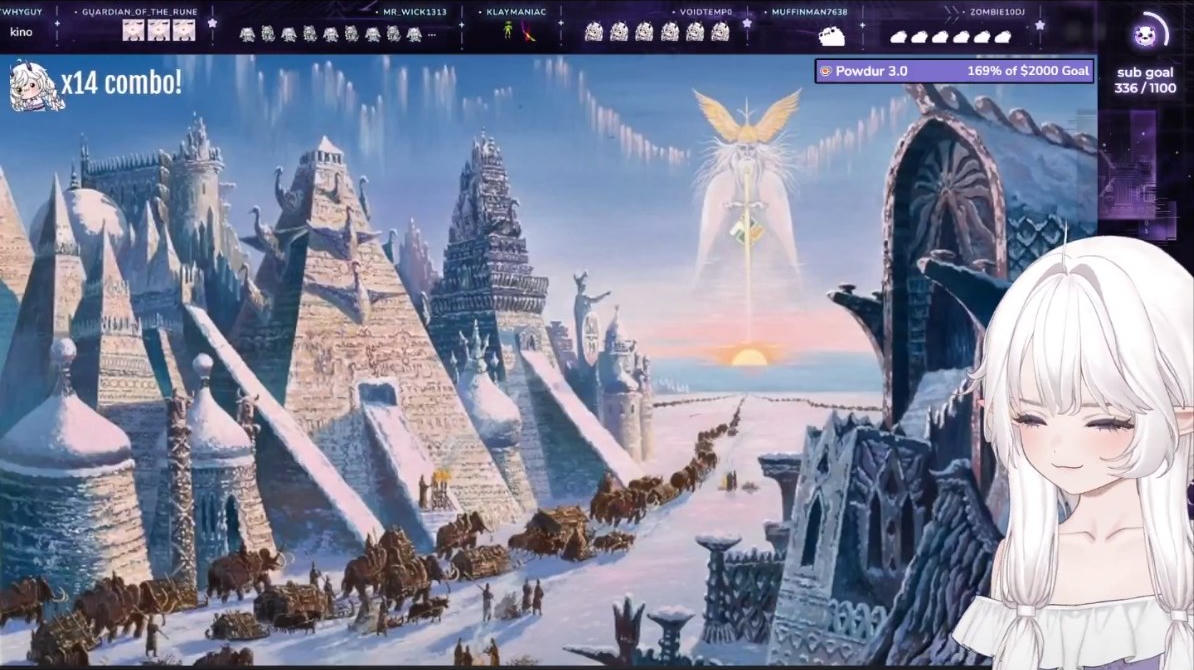
crop autocrop writes (1194 x 670), and a debug overlay showing the row and
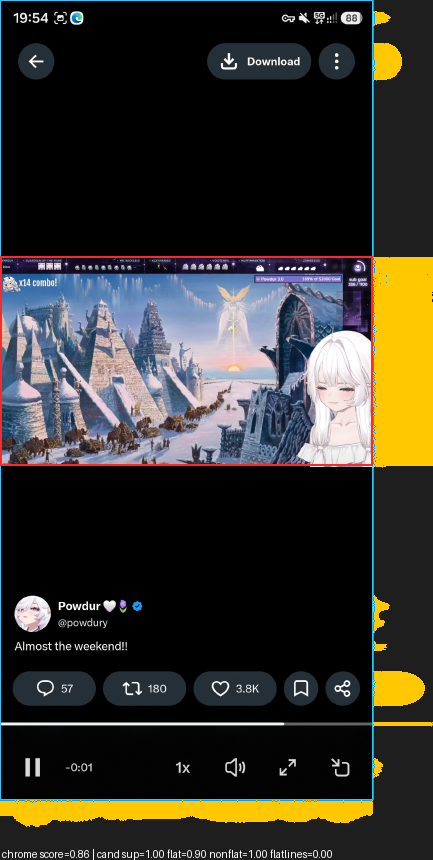
column profiles the detector works from together with the chosen box.
| input | crop | debug overlay |
|---|---|---|
 |
 |
 |
$ uvx autocrop-rs example.jpg --out out --time
example.jpg: chrome score=0.86 box=Some((0, 822, 1194, 1492))
  decode 16.6 ms, detect 11.0 ms (1194x2560)
Build and test
Rust toolchain required (the extension is compiled on install):
cd python
uv sync            # builds the extension into the venv via maturin
uv run pytest
uv sync --reinstall-package autocrop-rs   # after changing Rust code (uv caches the build)
Released wheels are on PyPI: pip install autocrop-rs (or uv add autocrop-rs). To build one locally: uv run maturin build --release. The
wheel is abi3 for CPython 3.11 and newer.
Usage
import autocrop_rs

result = autocrop_rs.detect_file("screenshot.jpg")
if result:  # truthy when a crop was found
    x0, y0, x1, y1 = result.box  # original pixel coordinates
print(result.reason, result.score)

# Encoded bytes (e.g. straight from an HTTP response or a database blob)
result = autocrop_rs.detect_bytes(data)

# An already decoded HxWx3 uint8 RGB array (numpy, or anything with the buffer protocol)
import numpy as np
from PIL import Image

result = autocrop_rs.detect_array(np.asarray(Image.open("screenshot.jpg").convert("RGB")))

# Detect and write the crop in one call (format by extension); writes nothing when box is None
autocrop_rs.crop_file("screenshot.jpg", "out/screenshot.png")

# Bytes in, bytes out: no decoding or re-encoding on the Python side
result, png = autocrop_rs.crop_bytes(data)  # PNG by default
result, jpg = autocrop_rs.crop_bytes(data, format="jpeg", quality=85)
result = autocrop_rs.crop_bytes_to_file(data, "out/screenshot.webp")  # format by extension

# Thresholds
params = autocrop_rs.Params(accept_score=0.5)
result = autocrop_rs.detect_file("screenshot.jpg", params)
params.to_dict()  # every field and its value
All four functions release the GIL while decoding and detecting, so they can run in a thread pool.
1 maintainer

Metadata
1 maintainer
Release files for autocrop-rs 0.1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| autocrop_rs-0.1.1.tar.gz | 893.1 kB | With provenance | Details |
Built distributions (wheels)
| File | Reset | |||
|---|---|---|---|---|
| autocrop_rs-0.1.1-cp311-abi3-win_amd64.whl | CPython 3.11 | abi3 | Windows x86-64 | Details |
| autocrop_rs-0.1.1-cp311-abi3-musllinux_1_2_x86_64.whl | CPython 3.11 | abi3 | Linux musl 1.2+ x86-64 | Details |
| autocrop_rs-0.1.1-cp311-abi3-musllinux_1_2_aarch64.whl | CPython 3.11 | abi3 | Linux musl 1.2+ ARM64 | Details |
| autocrop_rs-0.1.1-cp311-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl | CPython 3.11 | abi3 | Linux glibc 2.17+ x86-64 | Details |
| autocrop_rs-0.1.1-cp311-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl | CPython 3.11 | abi3 | Linux glibc 2.17+ ARM64 | Details |
| autocrop_rs-0.1.1-cp311-abi3-macosx_11_0_arm64.whl | CPython 3.11 | abi3 | macOS 11.0+ ARM64 | Details |
| autocrop_rs-0.1.1-cp311-abi3-macosx_10_12_x86_64.whl | CPython 3.11 | abi3 | macOS 10.12+ x86-64 | Details |
Total release size: 7.5 MB
Release files / autocrop_rs-0.1.1.tar.gz
| Download URL | autocrop_rs-0.1.1.tar.gz |
|---|---|
| Size | 893.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a9c55628531c0b8cf3366f9c25fa8c0187f252e7ff2086f354e4728d3bf9de01
|
|
BLAKE2b-256 checksum How to use checksums |
371628c0657eb9d5fb2bf1a0555e2434f874e881295708a6f7f8216a281375fa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-win_amd64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-win_amd64.whl |
|---|---|
| Size | 812.7 kB |
| Tags | CPython 3.11 Windows x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
e926a096fd8f93787d5f07e086db6d57f3ba6208a72e283f02e03f455305f705
|
|
BLAKE2b-256 checksum How to use checksums |
0398427a98f3984130ac6b023ce3186353dcfd497c16f8eed1cefcaae84cca3d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-musllinux_1_2_x86_64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-musllinux_1_2_x86_64.whl |
|---|---|
| Size | 1.1 MB |
| Tags | CPython 3.11 Linux musl 1.2+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
81b7e841b37d2778d59f13e1ff2e819bff71f2e7f8ba69333c83f30670c0b139
|
|
BLAKE2b-256 checksum How to use checksums |
a12788fbbf9b24b02d40d4872ef95374c10e34543e41d08375372808677717a5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-musllinux_1_2_aarch64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-musllinux_1_2_aarch64.whl |
|---|---|
| Size | 1.1 MB |
| Tags | CPython 3.11 Linux musl 1.2+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
af74db490a215f0bc34fe2fed24b573207b390ea57873ec98fccee1eb6654d5b
|
|
BLAKE2b-256 checksum How to use checksums |
5f51a2b309c67a4d99fbd3adda69843a13ec677ce10b2a94c6404082cf88c793
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-manylinux_2_17_x86_64.manylinux2014_x86_64.whl |
|---|---|
| Size | 921.1 kB |
| Tags | CPython 3.11 Linux glibc 2.17+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
0be09164fb651bb3bd410a752d6f0cce05b7b4e16dbfe40edeb146b01bbc7355
|
|
BLAKE2b-256 checksum How to use checksums |
08fa1220ee5646f1f5f6d361b6dafc12ebd51c5d1e2780572459686cc04b7113
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-manylinux_2_17_aarch64.manylinux2014_aarch64.whl |
|---|---|
| Size | 888.2 kB |
| Tags | CPython 3.11 Linux glibc 2.17+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
cfb762439787e9b8d87ea9d8dd5d43c460c8b4b6afbd49d9221f116e1708d383
|
|
BLAKE2b-256 checksum How to use checksums |
4692a07304671f6e57a9f798de1ef22d513e67257504aa1ac8ebb22abdb09359
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-macosx_11_0_arm64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 842.6 kB |
| Tags | CPython 3.11 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
0c323c343878c5e115c324eb55217f73f0fa254ca98363b078f23247677e6109
|
|
BLAKE2b-256 checksum How to use checksums |
7154b503245846a7954b80da005ee1e034ed1aff70d0700cde22198328fd38b1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logRelease files / autocrop_rs-0.1.1-cp311-abi3-macosx_10_12_x86_64.whl
| Download URL | autocrop_rs-0.1.1-cp311-abi3-macosx_10_12_x86_64.whl |
|---|---|
| Size | 889.6 kB |
| Tags | CPython 3.11 abi3 macOS 10.12+ x86-64 |
|
SHA-256 checksum How to use checksums |
fcd9f4c4a16f34be82946a3c37f3b5d696c7a898b15f94e77141617b7e40de31
|
|
BLAKE2b-256 checksum How to use checksums |
0fdc942a0ad6880d573f94117e2ffb81bdfc914add6ba148a82bf516e6495bae
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logSecurity for autocrop-rs 0.1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 8 files in this release have been uploaded with provenance metadata.
Attestation for autocrop_rs-0.1.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














