
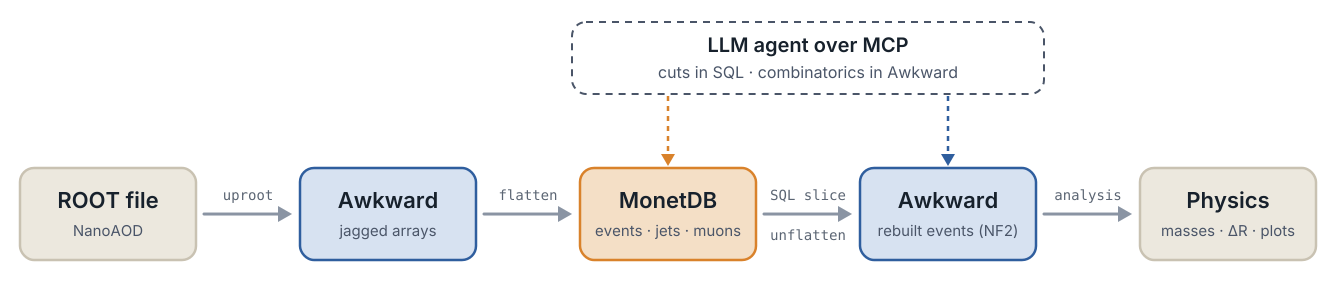
Hybrid analysis of nested (ragged) HEP data: flatten ROOT events into MonetDB tables, push selections down to SQL, then rebuild the nesting in Awkward Array for the physics. An LLM agent can drive the same pipeline through MCP.
Install
python -m pip install awkward-monetizer             # core
python -m pip install "awkward-monetizer[agent]"    # + LLM agent and MCP server
Python 3.10+. The MonetDB server is installed separately (brew install monetdb
on macOS). For development (pip or pixi), see
docs/usage.md.
Quickstart
awkward-monetizer make-nano          # synthetic NanoAOD file
awkward-monetizer adl                # IRIS-HEP ADL Q1–Q8 on it, no database needed
With a MonetDB server running, load real CMS Open Data:
monetdb create hep && monetdb release hep
awkward-monetizer ingest <NanoAOD file>.root --dataset nanoaod --database hep \
    --create-schema --step-size 50000 --entry-stop 100000
Agentic analysis
An LLM agent gets six tools: schema discovery, read-only SQL, Awkward code on events selected in SQL, submit, plot, and (over MCP) a check against the ADL reference. To use it from Claude Code:
claude mcp add -s user awkward-monetizer -- awkward-monetizer agent mcp --database hep
It speaks MCP over stdio (started by the client, as above) or HTTP
(awkward-monetizer agent mcp --database hep --transport http, local-only by
default). One tool runs agent-written Python behind a guard that is not a
sandbox; see SECURITY.md
and --no-code-tool.
On 100,000 CMS Open Data events (DoubleMuon Run2016H, record 30555), Claude answered all eight ADL questions correctly on the first attempt, doing cuts in SQL and combinatorics in Awkward. On the full record, 48.9 million events streamed from EOS in 22 minutes, all eight reproduce the reference exactly on a laptop, the SQL ones in under 3 s each. See docs/agent.md.
Documentation
- docs/usage.md: development setup, datasets, ingestion, sharding, benchmarks, notebooks, tests
- docs/agent.md: the agent, its tools, evaluation and demo
- CONTRIBUTING.md: how to contribute and how releases are made
Status
A finished prototype in maintenance mode: bug fixes and releases continue, no new features are planned. Arrow transport, electrons and b-tag are open for anyone who wants to take them on.
1 maintainer

Metadata
1 maintainer
Release files for awkward-monetizer 0.3.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| awkward_monetizer-0.3.2.tar.gz | 125.1 kB | With provenance | Details for awkward_monetizer-0.3.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| awkward_monetizer-0.3.2-py3-none-any.whl | Python 3 | none | any | Details for awkward_monetizer-0.3.2-py3-none-any.whl |
Total release size: 222.0 kB
Release files / awkward_monetizer-0.3.2.tar.gz
| Download URL | awkward_monetizer-0.3.2.tar.gz |
|---|---|
| Size | 125.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
330e3b7ddae5a02d710f4512e75162dab45dd7d5ba5912c94c228b5402017b13
|
|
BLAKE2b-256 checksum How to use checksums |
4a0cd90c5e05fdf206aa5061d43b767f7521523e0a68ea0c1954cd61e1f157f1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / awkward_monetizer-0.3.2-py3-none-any.whl
| Download URL | awkward_monetizer-0.3.2-py3-none-any.whl |
|---|---|
| Size | 97.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f864baab88e5b0956c00d731ebdfbe7a0317a79200305b9d9496b581c5cc1d71
|
|
BLAKE2b-256 checksum How to use checksums |
40f40d0bdcb216eb930081862de18277f38aa7d85bf4fb55f6541b1bbd2e15d9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logSecurity for awkward-monetizer 0.3.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for awkward_monetizer-0.3.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














