
badbyte
Deal with bad characters easily during exploit writing with badchars.
Table of Contents
↑Instalation
using pip:
pip3 install badbyte
or from repo:
git clone git@github.com:C3l1n/badbyte.git
cd badbyte
pip3 install .
↑Usage
You can always use:
badbyte --help
↑Cyclic pattern generate
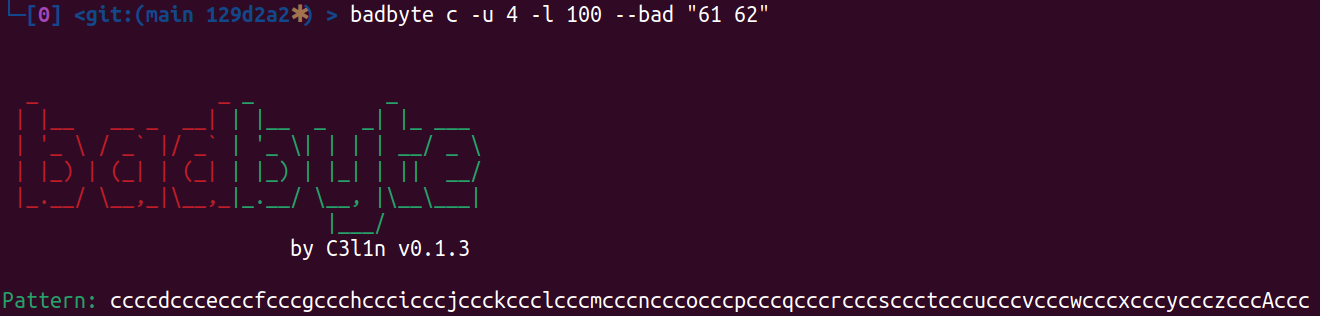
It is useful to search for offset at which you should put your sniper shot constants. For example return address: you generate pattern with this function, trigger vulnerability with generated payload. EIP value (remember about little ending in x86) has uniq part of pattern and offset of that part could be calculated with badbyte parse (see next chapter).
badbyte c -u 4 -l 100 --bad "61 62"
↑Search for offset in cyclic pattern
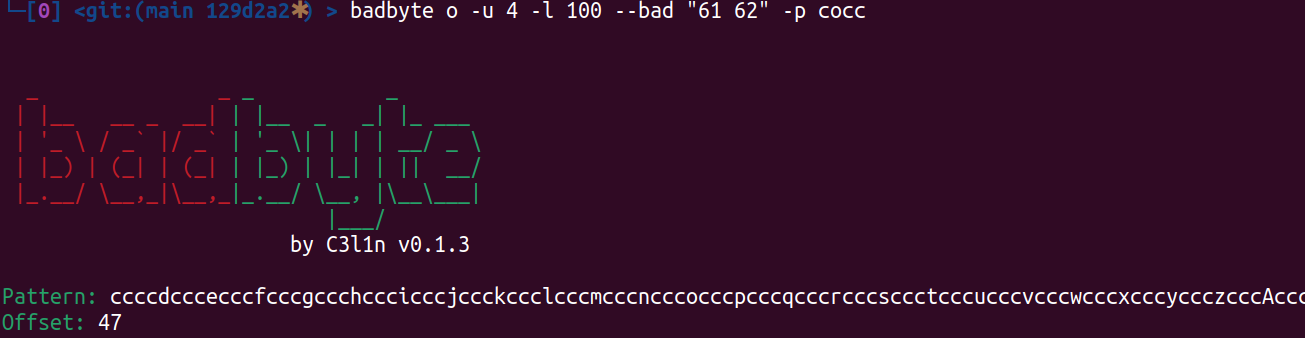
Search for offset of provided part in --pattern argument.
badbyte o -u 4 -l 100 --bad "61 62" -p cocc
↑Generate payload to check all characters
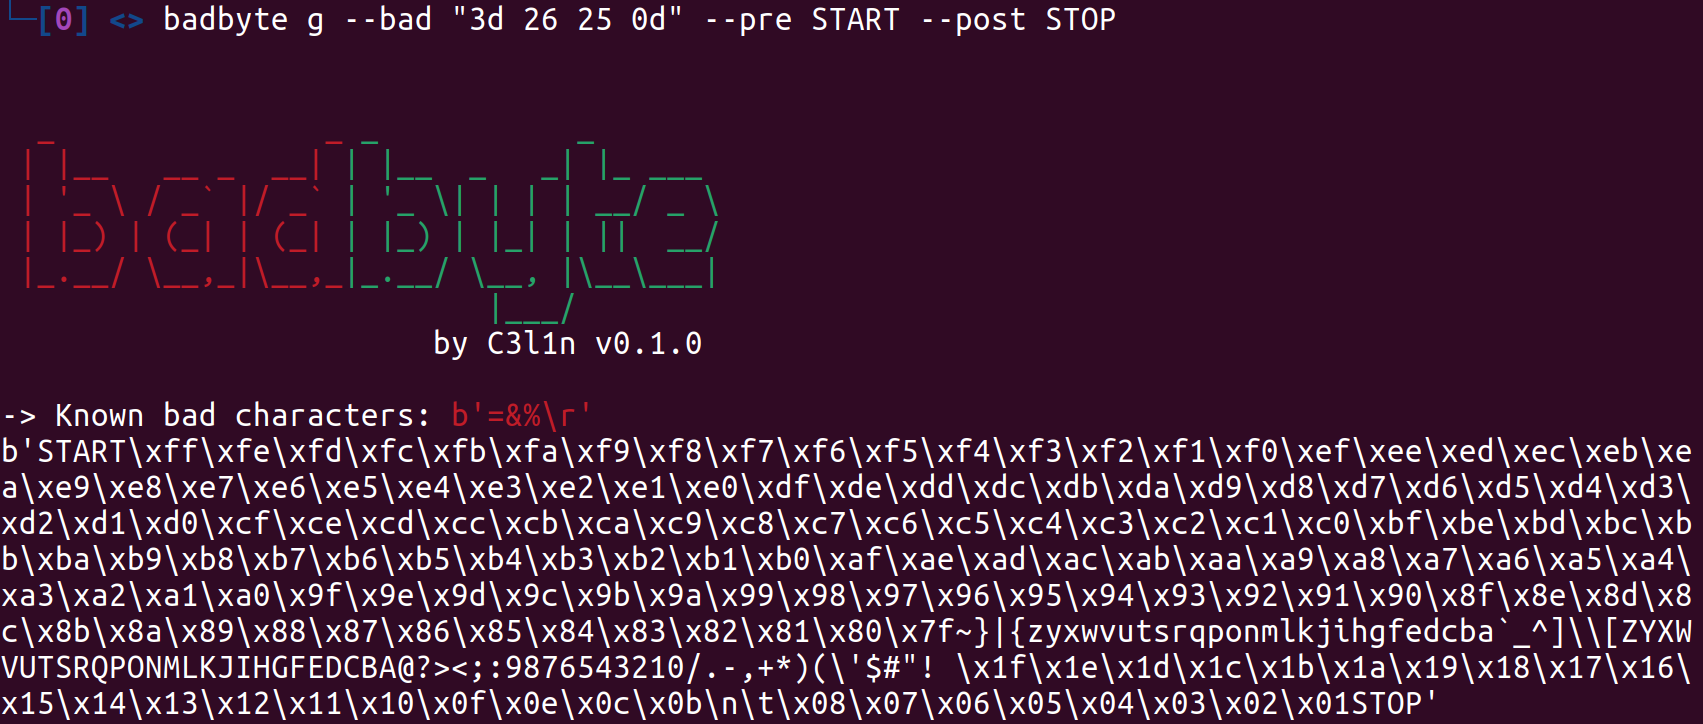
badbyte g --bad "3d 26 25 0d" --pre START --post STOP
use:
- --bad to supply hexascii values of bad characters
- --pre to set string for marking start point (or leave default)
- --post to set string for marking stop point (or leave default)
Then use payload in your exploit and fire it.
↑Analyze memory dumped after trigger
Copy hexascii from memory dump of your favourite debugger i.e. windbg:
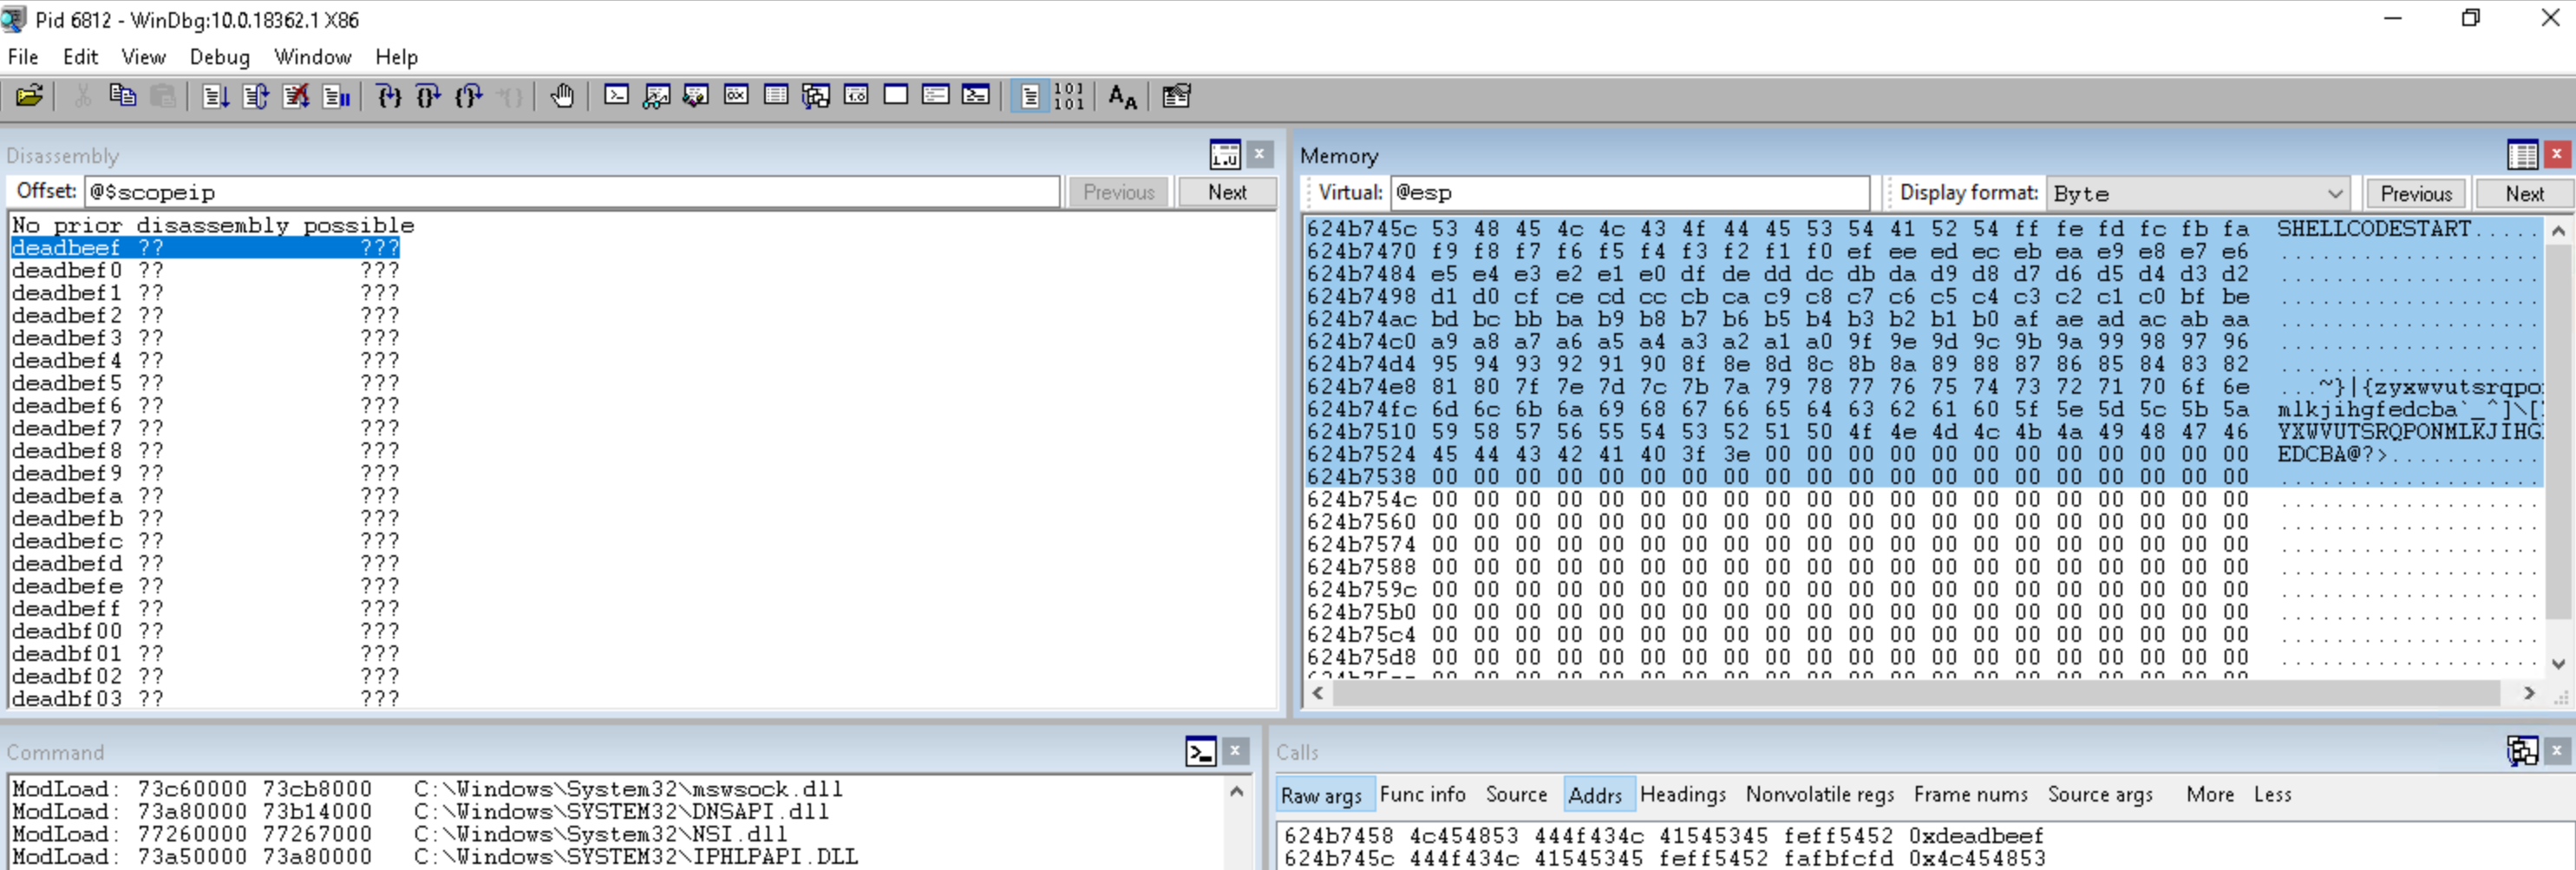
remember to skip addresses and ascii representation. I use vim and column select or visual studio code and alt+shift select.
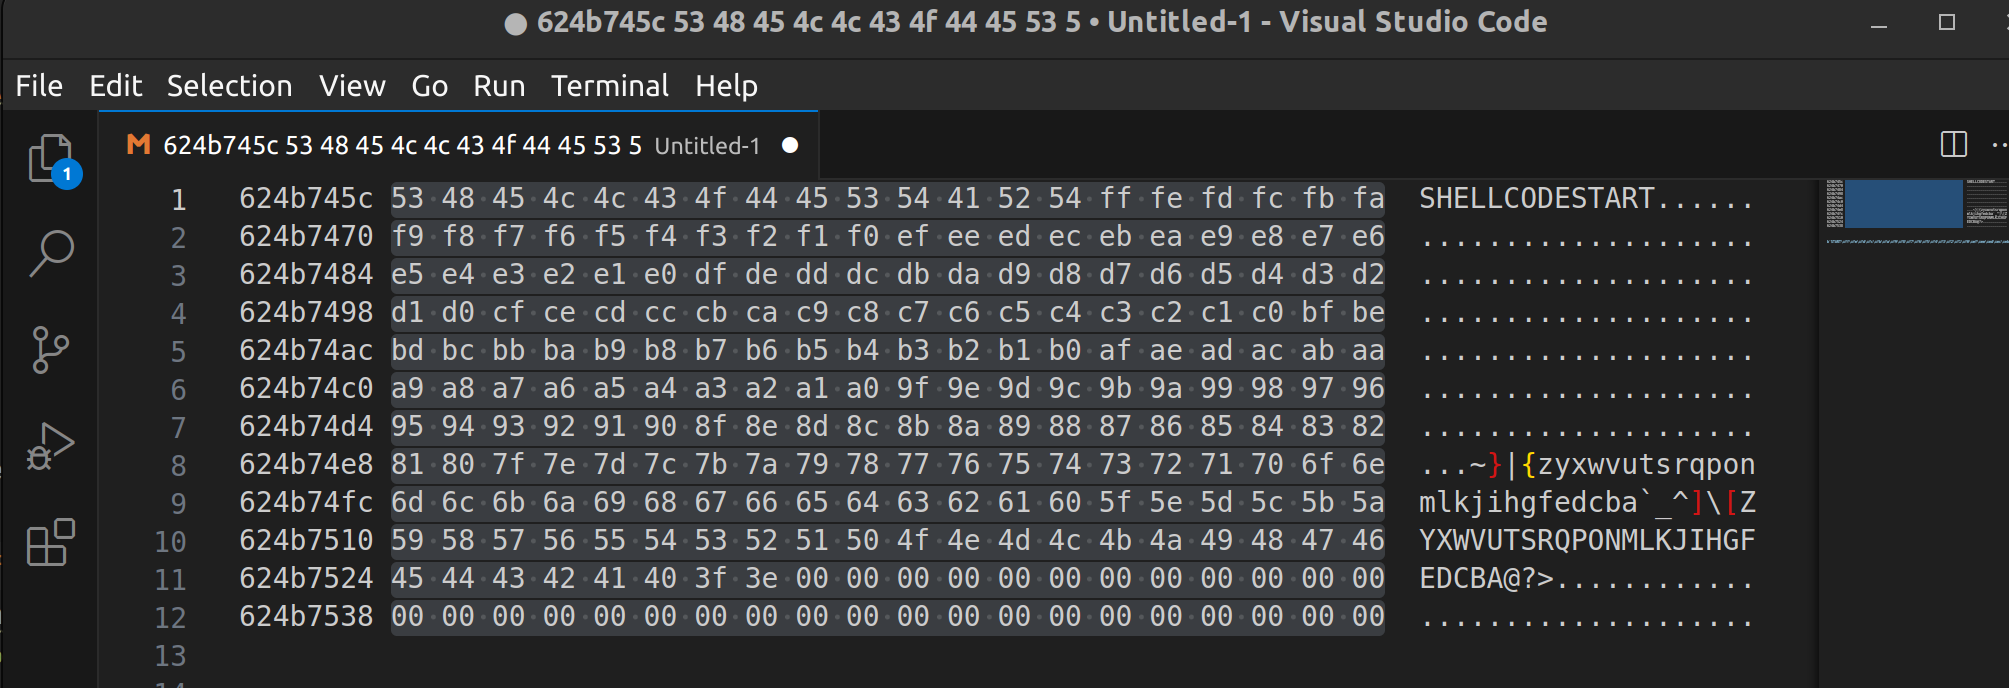
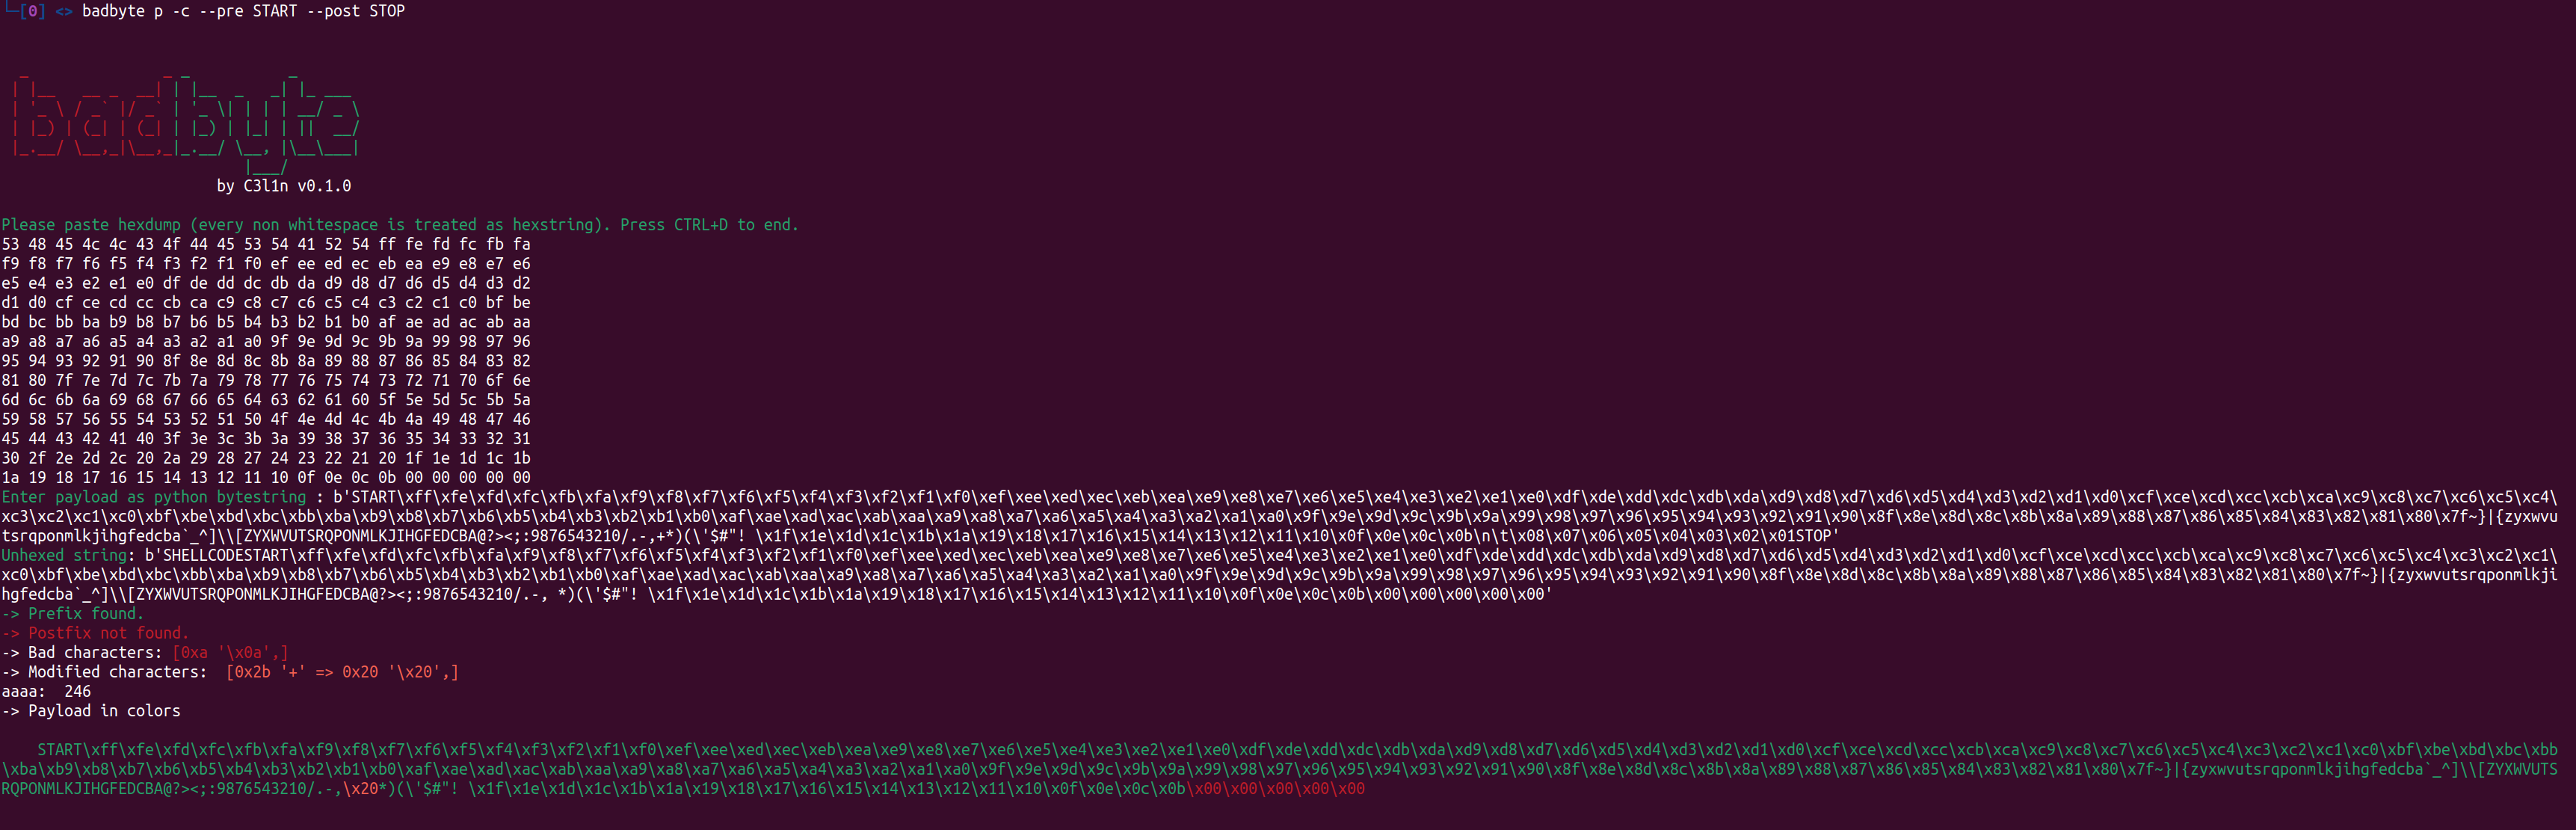
Fire badbyte to analyze output:
badbyte p -c --pre START --post STOP
↑Programatically use
Documentation not made (feel free to read code) but you can find in example/programatically_generate_payload.py example of payload generation in exploit.
1 maintainer

Release files for badbyte 0.1.11
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| badbyte-0.1.11.tar.gz | 6.3 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| badbyte-0.1.11-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 13.5 kB
Release files / badbyte-0.1.11.tar.gz
| Download URL | badbyte-0.1.11.tar.gz |
|---|---|
| Size | 6.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
2f5ead494cd0b77bdeff92a48bb489031c1c0daf40c877727e06b1daef9d7203
|
|
BLAKE2b-256 checksum How to use checksums |
e8000bf07ac5ddea3116755bd8341d0ad54e88d157fa60293aa83a469ffd43c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/5.1.1 CPython/3.12.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2024.
Transparency logRelease files / badbyte-0.1.11-py3-none-any.whl
| Download URL | badbyte-0.1.11-py3-none-any.whl |
|---|---|
| Size | 7.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c64de5cfb22e3c73585ea0c982504ecc5f21e126a67f4130cde5939fcb835d8e
|
|
BLAKE2b-256 checksum How to use checksums |
abc67a4e80d42d45c4b048f8b6bd643296248723d2b6d64f9d078376de9e30ff
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/5.1.1 CPython/3.12.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 15, 2024.
Transparency log













