
BaselithCore
Agents that survive production. Durable execution, enforced budgets and compliance evidence — self-hosted, with no companion SaaS.

Quick start · Plugins · Operating it · Architecture · Docs · Marketplace · Changelog
BaselithCore is a Python orchestration engine for agentic AI. Execution is checkpointed as a run proceeds, so an interrupted process resumes from its last completed step instead of replaying side effects. Every request carries a budget for iterations, tool calls, tokens and USD, and every step emits OpenTelemetry spans and Prometheus metrics with real cost attached.
- Durable. Checkpoint/resume, replayable tool steps, state history and fork/rewind. A
SIGKILLmid-run recovers without repeating a side effect. - Controlled. Autonomy gating, durable human approvals, per-request budgets, prompt-injection guardrails and sandboxed code execution, fail-closed by default.
- Complete and self-hosted. Evaluation, LLM-as-judge, red-teaming, tracing, metrics, Helm and Terraform are built in. Opt-in EU AI Act, GDPR, NIS2 and DORA primitives write their evidence while the system runs.
Stable since 1.0. The public
baselithAPI follows Semantic Versioning: a breaking change waits for a major release and a deprecation cycle. Coming from 0.x? See Migrating to 1.0.
Quick start
uvx --from baselith-core baselith --version     # try it without installing
uv pip install baselith-core                    # or: pip install baselith-core
import asyncio
from baselith import Agent, Crew, Task

researcher = Agent(system_prompt="You are a meticulous researcher.")
writer = Agent(system_prompt="You write crisp executive summaries.")

crew = Crew(agents=[researcher, writer], tasks=[
    Task("Research {topic} and list the key facts.", agent=researcher),
    Task("Write a summary from the research.", agent=writer),
])


async def main() -> None:
    result = await crew.run(inputs={"topic": "vector databases"})
    print(result.final)


asyncio.run(main())
baselith is the public API and the only surface with a compatibility promise
(see API stability tiers).
The quickstart adds
tools, structured output and a checkpoint store.
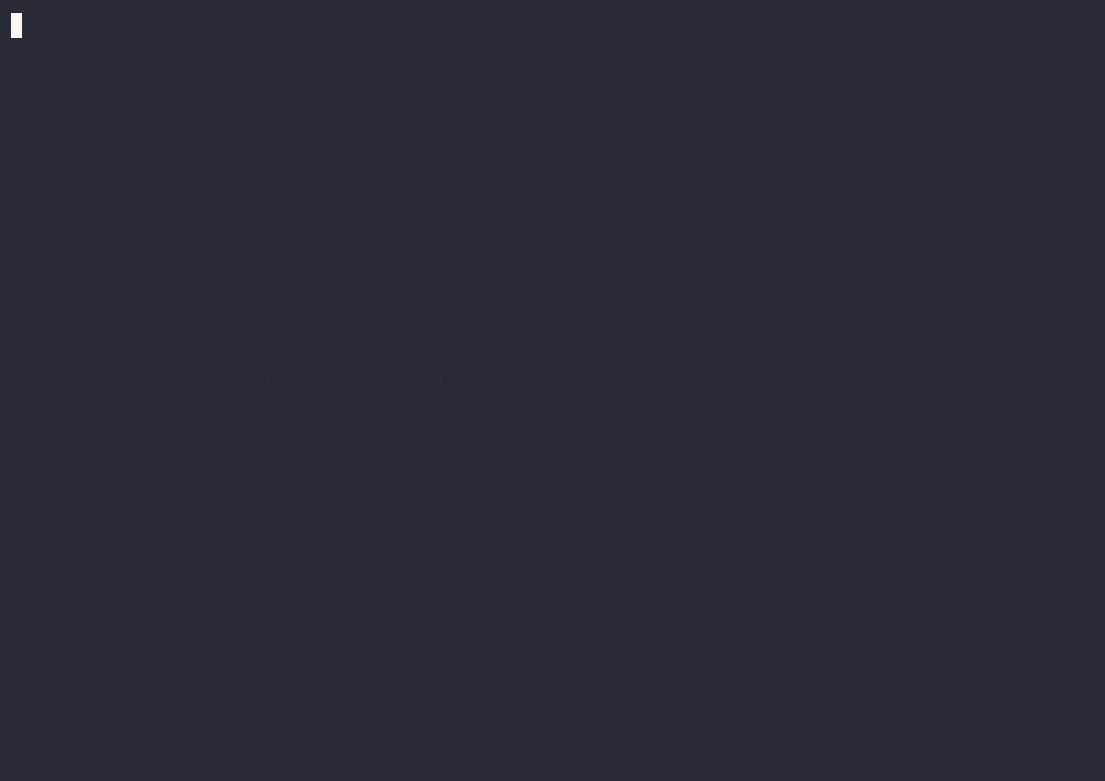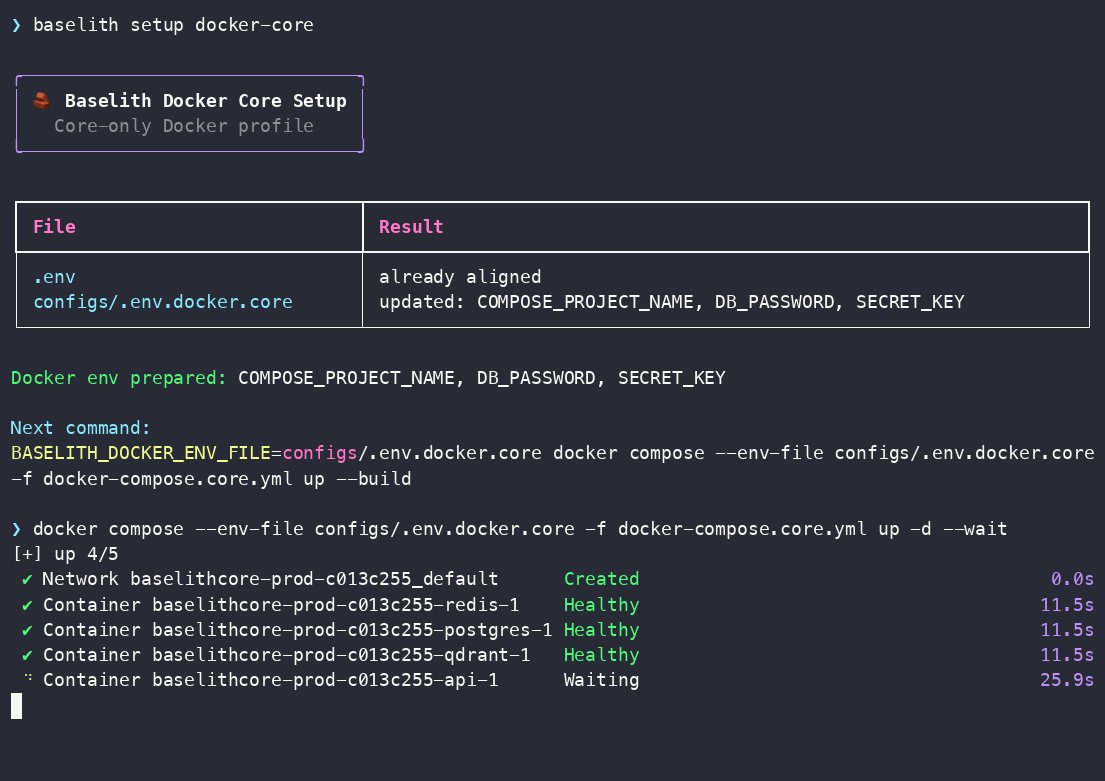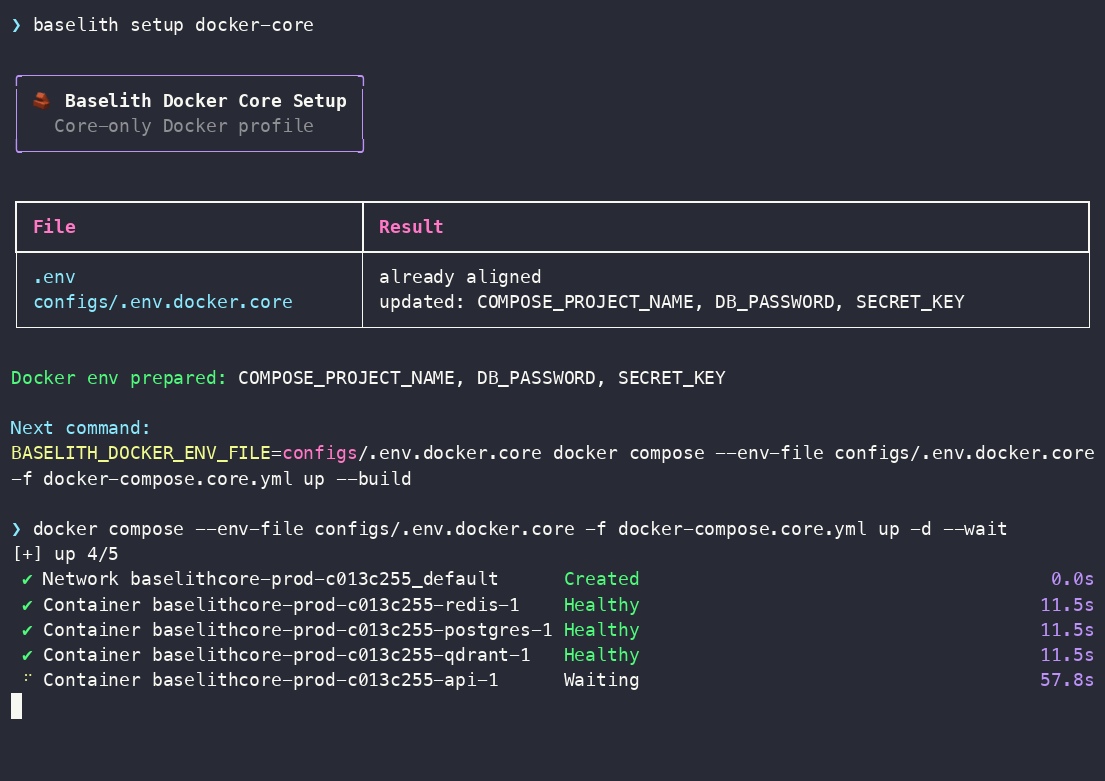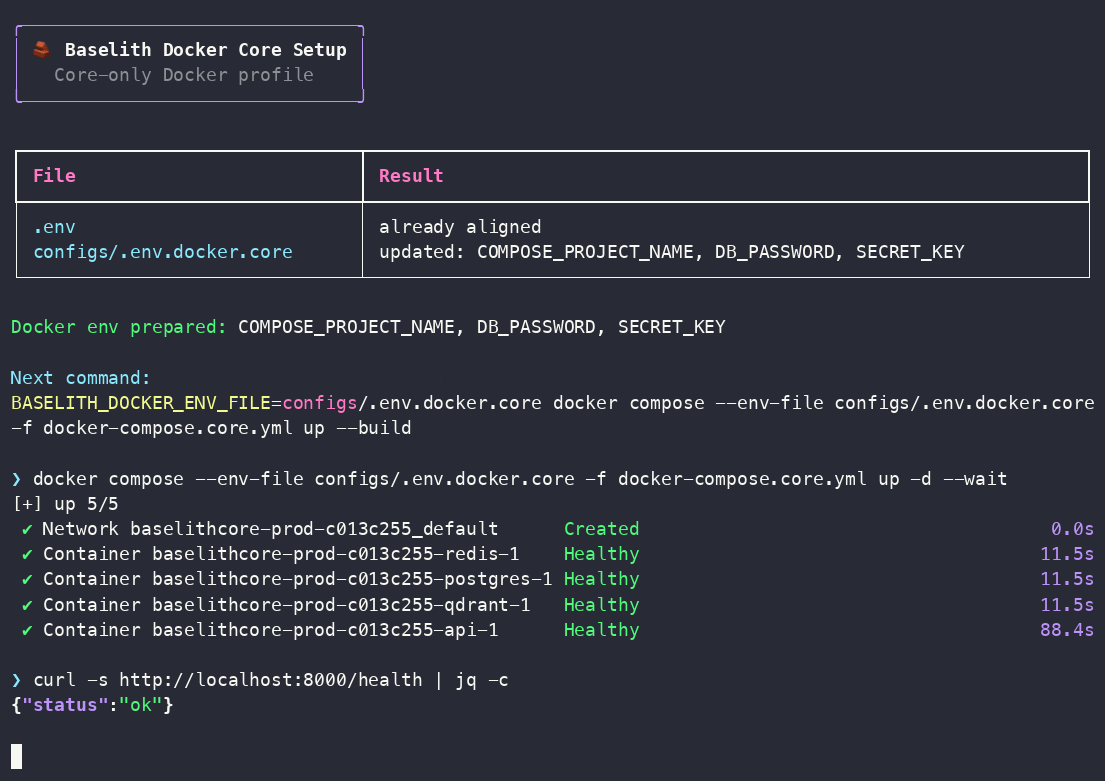
The whole runtime — API, PostgreSQL, FalkorDB, Qdrant and embedding/rerank servers, migrations applied at startup — from a checkout, with Docker running:
uv pip install -e .
baselith setup docker-core
docker compose --env-file configs/.env.docker.core -f docker-compose.core.yml up -d --wait
baselith doctor && curl --fail http://localhost:8000/health
In a project created by baselith init, baselith up does the same in one
command. Optional capabilities (RAG, browser automation, OCR, extra providers
and vector backends) install as extras: see the
installation guide
and the Docker Core guide.
Plugins
Everything domain-specific is a plugin, and the CLI does the plumbing:
baselith plugin create my_plugin --type agent    # agent | router | graph
baselith plugin validate my_plugin               # syntax, manifest, schema, deps, env vars
baselith plugin add my_plugin --name my_plugin --docker
baselith plugin marketplace search browser
baselith plugin add https://github.com/your-org/plugin-example --docker
baselith plugin sign writes the integrity hash a hardened deployment checks
before importing anything. Official plugins ship under baselith.plugins, each
signed and strictly typed: api_routers, browser_agent, coding_agent,
document_sources, goals, payments, reasoning_agent and web_scraper.
Start with the first-plugin tutorial.
You keep your source. The plugin exception lets any plugin that uses the framework as a library ship under any licence, including a closed one. Same terms for everyone.
Operating it
Updates are a checked, reversible operation rather than a git pull:
baselith update status            # core and plugins: installed vs available
baselith update check             # refresh now; exits non-zero if the check fails
baselith update preflight         # can an update be installed right now?
baselith update apply             # install the latest signed core release
baselith update rollback          # return to the commit the last update replaced
baselith update policy set ...    # auto-apply patch releases inside a maintenance window
Releases are verified against provenance or an ed25519 signature before
anything is touched, a failed health check rolls the install back, and every
run is audited. A security update shows in baselith doctor as a warning,
never a failure. See Plugin updates.
Architecture
graph TD
    subgraph SC["Core — domain-agnostic"]
        A["Orchestrator<br/>(routing · adaptive loop · checkpoint/resume)"]
        COG["Cognitive layer<br/>(reasoning · world model · swarm · planning)"]
        LP["Engineered loops<br/>(verifier · stall guard · escalation)"]
        M["Memory<br/>(STM → MTM → LTM)"]
        S["Storage<br/>(Postgres · Qdrant/pgvector · Redis)"]
        R["Plugin registry"]
        GOV["Governance<br/>(autonomy · approvals · budgets · evidence)"]
        RES["Resilience · Observability · Guardrails"]
    end
    A --> COG & LP & M
    M --> S
    R -.->|handlers, routers| A
    R --> P["Plugins"]
    A --> H["LLM layer<br/>(Anthropic · OpenAI · Gemini · Ollama · HF)"]
    A --> I["Interop<br/>(MCP · A2A · AP2 · realtime)"]
    A -.->|gated by| GOV
    A -.->|wrapped by| RES
Two rules hold the shape: baselith/core/ stays domain-agnostic, and
everything domain-specific is a plugin. See the
architecture docs.
What's inside
| Agents and crews | Typed Agent; sequential, parallel or manager-led Crew; group chat → Agent API |
| Durable execution | Postgres, SQLite or in-memory checkpoints, replay, fork/rewind, async runs with webhooks → Orchestration |
| Loops and reasoning | Verifier-owned loops, MCTS, Tree-of-Thoughts, swarm auctions → Loops · Reasoning |
| Memory and RAG | STM→MTM→LTM, hybrid search, full RAG pipeline, Qdrant or pgvector → Memory |
| Multimodal | Vision, PDF and audio blocks, speech in and out, duplex voice with barge-in |
| Interoperability | MCP server and client, A2A peers, AP2 signed mandates → MCP |
| Evaluation and observability | Trajectory eval in CI, LLM-as-judge, red-team, OTel and Prometheus with USD cost → Evaluation |
| Self-improvement, governed | Skill evolution and prompt search, every change eval-gated and auditable → Skill evolution |
| Compliance | EU AI Act, GDPR, NIS2, DORA primitives with evidence trails → Regulatory |
| Deployment | Docker, Helm, Terraform, SLO rules, typed SDKs → Deployment |
Contributing
Start from a good first issue, pick up a help wanted or ask in Discussions. CONTRIBUTING.md covers setup and the quality gates every PR passes: 13,000+ tests behind an 85% branch-coverage floor, strict typing, and architecture and docs-consistency checks. See also GOVERNANCE, SUPPORT, SECURITY and the Code of Conduct.
Licence
AGPL-3.0-only (LICENSE), with a section 7 permission
(LICENSE.exception): a plugin that uses the framework as a
library, rather than patching baselith/core/, may carry any licence, closed
ones included. NOTICE adds an attribution term: keep the file, and
credit "Based on BaselithCore by The BaselithCore Authors" wherever a product
shows legal notices.
Copyright © 2026 The BaselithCore Authors.
1 maintainer

Metadata
1 maintainer
Release files for baselith-core 1.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| baselith_core-1.4.0.tar.gz | 2.7 MB | With provenance | Details for baselith_core-1.4.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| baselith_core-1.4.0-py3-none-any.whl | Python 3 | none | any | Details for baselith_core-1.4.0-py3-none-any.whl |
Total release size: 6.1 MB
Release files / baselith_core-1.4.0.tar.gz
| Download URL | baselith_core-1.4.0.tar.gz |
|---|---|
| Size | 2.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
de3e29874b3cb0168ebd7518c45c4846d17acf544230e0bd80386161fda0c76f
|
|
BLAKE2b-256 checksum How to use checksums |
99eb94f5144e3661ed7b34773d9cce78863bcfcc9c5229f209c740a5f5a058f6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logRelease files / baselith_core-1.4.0-py3-none-any.whl
| Download URL | baselith_core-1.4.0-py3-none-any.whl |
|---|---|
| Size | 3.4 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
2d3aa6ff75dabe2bde0afd88112255a814e8deba1406ebf76d60aaae1790822b
|
|
BLAKE2b-256 checksum How to use checksums |
9dbccb4c683e23e9453e2e8b82909f54bd017d4537a5c16187d63e8b5cb9d217
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logSecurity for baselith-core 1.4.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for baselith_core-1.4.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














