


Documentation · Quick start · What can I do with BEAM? · How BEAM works
Every possible sequence, accounted for.
BEAM is a probability model of biological sequences, amino acid or nucleotide. It learns from the sequences alone, with their abundances if you have them, and then answers: how likely is this sequence? How many distinct sequences will a sample of a given depth hold, and how many will two samples share? How many people in a cohort will carry a sequence? How do two repertoires, cell types or conditions differ, and why? Each answer is summed over every combinatorially possible sequence, without listing or simulating a single one, so the same input always gives the same answer.
BEAM comes with a ready-made reference model of T cell receptor β (TCRβ) CDR3s, built from 38,538 human repertoires, and builds models from your own data in one line.
Paper: T. Konstantinovsky and G. Yaari. A computable probability landscape for T cell receptor repertoire sampling and comparison. (Submitted.)
What can I do with it?
| Question | What BEAM gives you |
|---|---|
| How likely is this sequence? | Its probability, normalised over all possible sequences, including ones never seen, and which residues make it likely or unlikely |
| What do typical sequences look like? | Realistic sequences drawn from the model |
| How deeply should I sequence? | The expected number of distinct sequences at any depth, and how many two samples share |
| How many people share this sequence? | The expected number of repertoires in a cohort that contain it, and its full distribution |
| How different are two repertoires, and why? | A distance that separates differences in sequence length from differences in local sequence patterns, and names the patterns |
Install
pip install beam-model
Ready-to-use packages exist for Linux (x86-64 and ARM), macOS (Apple Silicon, macOS 14 or newer) and Windows (x86-64), for Python 3.11 to 3.15.
Quick start
import BEAM

# downloads once (~90 MB), then cached
model = BEAM.load_pretrained("human_tcrb_cdr3_aa_foundation")

model.pseq("CASSLGQGYEQYF")        # probability of one sequence
# 3.3e-05
The reference model uses about 1 GB of memory once loaded.
Examples
How likely is a sequence?
pseq returns the probability of a sequence under the model: for the reference
model, the chance that one T cell drawn at random carries exactly this CDR3. It
takes one sequence or a list.
model.pseq(["CASSLGQGYEQYF", "CASSPGTGELFF", "CWWWWWWWWF"])
# array([3.3e-05, 2.9e-05, 6.9e-23])
Sequences the model has never seen still get a sensible probability: a
plausible new CDR3 gets a moderate one, an implausible one (like the last) a
vanishingly small one. Use log_pseq_batch for millions of sequences at once.
BEAM reads every residue twice, once from the start of the sequence and once
from the end, and explain shows how each residue contributes to the score:
e = model.explain("CASSLGQGYEQYF")
e["forward"]     # each residue's log probability, read from the start
e["backward"]    # ... and read from the end
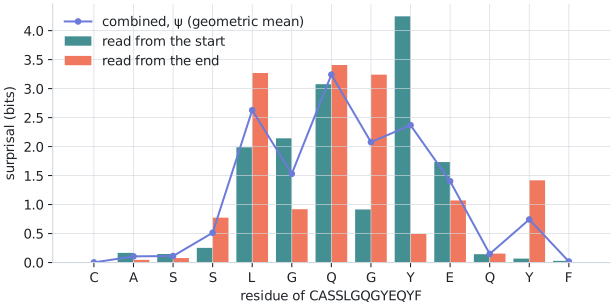
How unexpected each residue of CASSLGQGYEQYF is, in bits, read from the start (teal) and from the end (orange), and the two combined. The conserved start and end are expected; the information sits in the junction between them.
What do typical sequences look like?
model.sample(5, seed=1)
# ['CASSPGTSSDTYEQYF', 'CASSLGTYSYNEQFF', 'CASRPGNSPLHF', ...]
Sequences are drawn in proportion to their probability. The model can also be
drawn as sequence logos computed over every sequence of a length, without
sampling (model.insights.logo):
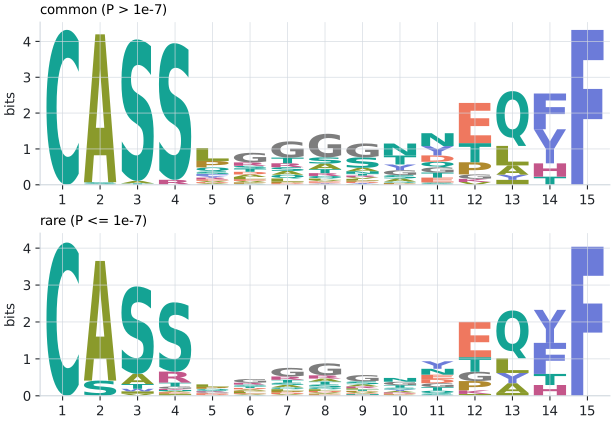
Length-15 CDR3s under the reference model: the common sequences (probability above 10⁻⁷, a quarter of all the probability at this length) and the rare ones. Both keep the conserved CASS…F frame; the common ones are more constrained, with 37 bits of information against 29.
How deeply should I sequence?
If you sample n cells from a population, how many different sequences will you see? And if two labs each sample n, how many sequences will they have in common? BEAM computes both directly, without simulation.
from BEAM.analytics.exact_occupancy import ExactOccupancy

occupancy = ExactOccupancy(model)

# distinct sequences in 100,000 cells, and in a million
occupancy.richness(100_000).value
# 96771.4...
occupancy.richness(1_000_000).value
# 879776.1...

# sequences shared by two samples of 100,000 cells
occupancy.sharing(100_000, 100_000).value
# 3678.4...
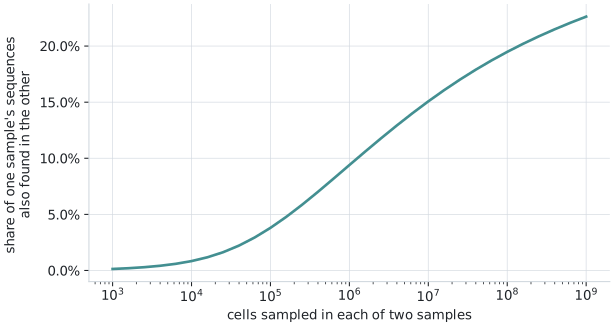
The share of one sample's distinct sequences that a second sample of the same size also contains, from a thousand to a billion cells per sample, under the reference model.
Each result also reports a guaranteed bound on its relative error (.bound),
here below one part in ten billion. The first query takes a minute or two while BEAM
prepares the integrals it needs; every later query, at any depth, is instant.
How many people will share a sequence?
A sequence is public when many people carry it. Describe a cohort by how deeply each person's repertoire was sampled, and BEAM tells you how many of them are expected to carry a sequence.
from BEAM import PublicnessModel

# 100 people, 50,000 cells sampled from each
cohort = PublicnessModel([50_000] * 100)

mean, variance = cohort.moments(model.pseq("CASSLGQGYEQYF"))
mean                     # expected number of people who carry it
# 80.8
cohort.pmf(p) gives the full distribution: the probability that exactly 0,
1, 2, ... people carry the sequence.
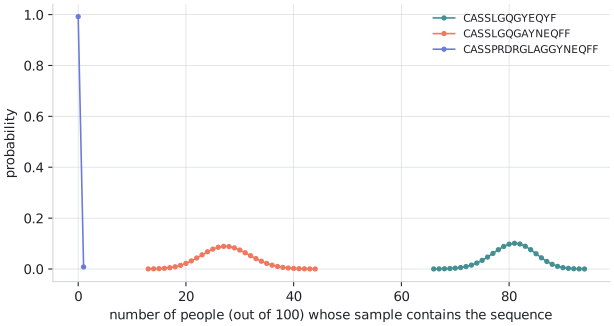
How many of the 100 people carry each of three CDR3s: a public one, found in about 80 of them, one found in about 27, and a rare one that almost nobody carries.
How different are two repertoires, and why?
Build a model from each person's repertoire and compare them. The distance splits into two parts that add up to it, one due to different sequence lengths and one due to different local sequence patterns, and it names the patterns that differ most.
import pandas as pd
from BEAM import BeamModel
from BEAM.analytics.distance import compare

def repertoire_model(path):
    table = pd.read_csv(path, sep="\t")             # an AIRR-format table
    return BeamModel.from_dataframe(table, sequence_column="junction_aa",
                                    abundance_column="duplicate_count")

a = repertoire_model("donor_A.tsv")
b = repertoire_model("donor_B.tsv")

result = compare(a, b)
result.distance          # 0 = identical
result.patterns[:5]      # the patterns that differ most

# the share of the distance due to lengths
result.length_squared_distance / result.squared_distance
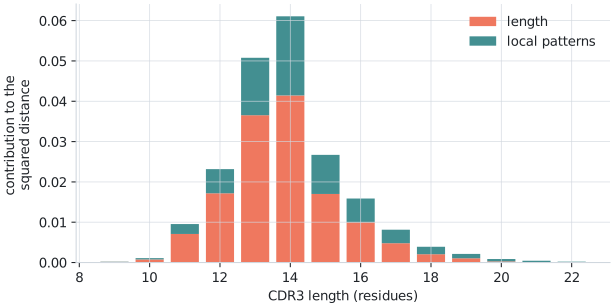
Where the distance between two repertoires comes from, length by length: a typical repertoire against one with more long CDR3s and more …NEQFF endings. Most of it is the difference in lengths (orange); the rest is local patterns (teal), led by NEQFF.
Comparing two repertoires takes under a minute.
Using your own data
from BEAM import BeamModel

# from Python lists
model = BeamModel(sequences, abundances=counts)

# from a file with one "SEQUENCE<TAB>COUNT" per line
model = BeamModel.from_sequence_file("cdr3.tsv")

model.save("my_repertoire")          # writes my_repertoire.beam
model = BeamModel.from_file("my_repertoire.beam")
Abundances are optional; without them every sequence counts once. Nucleotide
sequences work too, with alphabet="nt".
To score sequences against the reference model, or to compare your models with
it, write CDR3s as it does: including the conserved cysteine at the start and
the phenylalanine or tryptophan at the end, for example CASSLGQGYEQYF. In
AIRR-format files this is the junction_aa column; AIRR's cdr3_aa column
leaves those two residues out.
Why no simulation?
Most questions about a repertoire are sums over every possible sequence, and there are far too many sequences to list. The usual workaround is simulation: draw many sequences and count. BEAM is built so that these sums can be computed directly, by dynamic programming over the whole sequence space. Its probabilities are normalised over all sequences, and quantities such as expected richness, overlap and publicness are evaluated numerically, with stated error bounds where a sum is approximated. The same input always gives the same answer, and small differences between groups are not lost in simulation noise.
Documentation
The documentation website, mutejester.github.io/BEAM, has guides for each question above, explanations of how BEAM works with interactive figures, and the API reference.
Questions and ideas are welcome in Discussions; bugs in Issues.
Citing BEAM
If BEAM is useful in your work, please cite the paper above. GitHub's "Cite
this repository" button (from CITATION.cff) gives the
reference in BibTeX and APA.
License
BEAM is free software under the GNU General Public License v3.0 or
later. Contributions are welcome: see
CONTRIBUTING.md.
1 maintainer

Metadata
1 maintainer
Release files for beam-model 0.9.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| beam_model-0.9.0.tar.gz | 612.6 kB | With provenance | Details |
Built distributions (wheels)
Total release size: 22.2 MB
Release files / beam_model-0.9.0.tar.gz
| Download URL | beam_model-0.9.0.tar.gz |
|---|---|
| Size | 612.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
51e3cf0f29c8aa301e2d2f0eced0d921984787c3be6ff5fb5d00e28a0dcad67f
|
|
BLAKE2b-256 checksum How to use checksums |
2cb5590ac9402f99c1b6cfe5f79e3c121e31e2db18c1113d15745d80a1d92603
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp315-cp315-win_amd64.whl
| Download URL | beam_model-0.9.0-cp315-cp315-win_amd64.whl |
|---|---|
| Size | 877.5 kB |
| Tags | CPython 3.15 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
af7779e2651894985d7439754b97808823016aa772e2c198e569aab317ada48e
|
|
BLAKE2b-256 checksum How to use checksums |
a69d393aa503f554a2f493aa6d14b1cd075cc369c74c88920c4b03c5e35093ab
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp315-cp315-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl
| Download URL | beam_model-0.9.0-cp315-cp315-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.15 Linux glibc 2.24+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
18aa852a7d799ddd81e0816ec1ec1b85253cbacaa63a1ca1b1c43a9ea78ca4fd
|
|
BLAKE2b-256 checksum How to use checksums |
2baea01437e965139b26c1efe7343dfb3074d742e22837b840316b088337d821
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp315-cp315-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl
| Download URL | beam_model-0.9.0-cp315-cp315-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.15 Linux glibc 2.24+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
75a6fc2da4a9d5d444fe5dfb5414ec57fca6635b6c370742466f8e3350da965e
|
|
BLAKE2b-256 checksum How to use checksums |
9253852234dc9aab4d22de2e0c2471b2e432d1c72c22efcfb87623aefd570cad
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp315-cp315-macosx_14_0_arm64.whl
| Download URL | beam_model-0.9.0-cp315-cp315-macosx_14_0_arm64.whl |
|---|---|
| Size | 734.5 kB |
| Tags | CPython 3.15 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
284b52043c021bc5d72ff0172155e173517d83b206a7080b17a9eaeff4cf0cd5
|
|
BLAKE2b-256 checksum How to use checksums |
6ca7f7b06a4299e1846aa8d3471b40aa13832d08a17febcee77b18805af0baf4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp314-cp314-win_amd64.whl
| Download URL | beam_model-0.9.0-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 877.5 kB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
0b2175bc7c966c758505912cbeeeb3c4bc549939ab62bfa94b85bae6246358ec
|
|
BLAKE2b-256 checksum How to use checksums |
b44c2ac9f98bae246f7063dd79b724d423cacd4f686d9a9c8b3366ebe7d1c8c2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp314-cp314-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl
| Download URL | beam_model-0.9.0-cp314-cp314-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.14 Linux glibc 2.24+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
132a86e9a52244ce1e82885b970de343878cd1c48c6a2b4f5f70ec94349735bc
|
|
BLAKE2b-256 checksum How to use checksums |
5c731d5084178ae061cba82f9c60478282a2e93cf9a414cadd65bfd2419f2305
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp314-cp314-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl
| Download URL | beam_model-0.9.0-cp314-cp314-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.14 Linux glibc 2.24+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
b8a073a3cafcd8533d3071317653f2b7e016250092c6ba32f4a07cda447e1387
|
|
BLAKE2b-256 checksum How to use checksums |
aac6a7ede6f9d0ea4bfdf6e1887e1ae49a2a0992ec9a060ec04c0e5679b02e48
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp314-cp314-macosx_14_0_arm64.whl
| Download URL | beam_model-0.9.0-cp314-cp314-macosx_14_0_arm64.whl |
|---|---|
| Size | 734.3 kB |
| Tags | CPython 3.14 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
5fa7b34463a408fd9e71f80c4a73269de806267ebe7c5888cc1759efe29c3500
|
|
BLAKE2b-256 checksum How to use checksums |
20ec552b58a471df690fdc2277b75c8df5127d8f90e74bf64e1627005c85d0dc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp313-cp313-win_amd64.whl
| Download URL | beam_model-0.9.0-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 860.0 kB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
b6f630bdf3f3da8b15cf35a7cc552eb3d8bf247a1c6cb04c38a035e843febbd6
|
|
BLAKE2b-256 checksum How to use checksums |
941b04d72889df19c45fc279f80d34039dbfcd779e8cbffd65badcca979d15ce
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp313-cp313-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl
| Download URL | beam_model-0.9.0-cp313-cp313-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.13 Linux glibc 2.24+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
a63bbb9b4f55e20d6a0a715464df48e51fde38b940ca50ac039781d1232f35bf
|
|
BLAKE2b-256 checksum How to use checksums |
07ba789ca63f1735bea135bdd1710be04859685a0bba1279f118ee278cf20412
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp313-cp313-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl
| Download URL | beam_model-0.9.0-cp313-cp313-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.13 Linux glibc 2.24+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
b68a178bf30830d276deccfdeb275363f1f6252c9a3fd5a5205159181322c3b0
|
|
BLAKE2b-256 checksum How to use checksums |
02dbe8e8b62b1ad23bd4b137ee0eed0717b8ff4d2289a3e7bb223dae57df409c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp313-cp313-macosx_14_0_arm64.whl
| Download URL | beam_model-0.9.0-cp313-cp313-macosx_14_0_arm64.whl |
|---|---|
| Size | 734.3 kB |
| Tags | CPython 3.13 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
061b3b174403470e57afae070aa098690a36f729ea43842dc1edf8e7b35fe8c6
|
|
BLAKE2b-256 checksum How to use checksums |
236c52707c29ce9b704e84e3e9c2cb198f1a2e77dc0d7981524d1f5427da4ecc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp312-cp312-win_amd64.whl
| Download URL | beam_model-0.9.0-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 860.0 kB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
7a09223e0d6d50718f602563317b2433c6f0451353090d71dcd1dc78928874e7
|
|
BLAKE2b-256 checksum How to use checksums |
f6ab5473925d9d8a21995f5a447ceb2fe4658e5f5c86dfbf5b59cb102452b133
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp312-cp312-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl
| Download URL | beam_model-0.9.0-cp312-cp312-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.12 Linux glibc 2.24+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
c79b10d91bb30ca12779c6c50fb37df4ff22944e849c33a25572315f3bda71c8
|
|
BLAKE2b-256 checksum How to use checksums |
24d43ca3abff80aded71326ef86e9eff6a30650e593791bc8b451346af511962
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp312-cp312-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl
| Download URL | beam_model-0.9.0-cp312-cp312-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.12 Linux glibc 2.24+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
969c15b5163ba85b12add07115fb428cf606e3b6a92693ca34304555106b4957
|
|
BLAKE2b-256 checksum How to use checksums |
1042d95781aedae76ef67c971b16cbd5075981622a4a4044df953ee6d4fbd5ed
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp312-cp312-macosx_14_0_arm64.whl
| Download URL | beam_model-0.9.0-cp312-cp312-macosx_14_0_arm64.whl |
|---|---|
| Size | 734.3 kB |
| Tags | CPython 3.12 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
4ba53e65e2c99a9e89d63dbba777b741ff0570785370b47105bca51bbd9a17e9
|
|
BLAKE2b-256 checksum How to use checksums |
4b27c3920787d344d6c199ea1e5bbefff223d345c5f4a4d99df9b5b6d237f481
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp311-cp311-win_amd64.whl
| Download URL | beam_model-0.9.0-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 859.9 kB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
9298c490b66914ff8a9161c1edd607922b13138143c62aa74daf8d314c05c9b9
|
|
BLAKE2b-256 checksum How to use checksums |
4307cdfcdf9945846510e7fc8f47a20569823360bc3f15ad437043651b465aad
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp311-cp311-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl
| Download URL | beam_model-0.9.0-cp311-cp311-manylinux_2_24_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 1.4 MB |
| Tags | CPython 3.11 Linux glibc 2.24+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
8ebe560e9b980c13a7c03b5636d685920ff3903edd5371fbb0c7909dfe2994fd
|
|
BLAKE2b-256 checksum How to use checksums |
8b53bf05e1088dbcd8e065f3c408b268e9604cc6f06006150c3f9e3a147f83e6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp311-cp311-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl
| Download URL | beam_model-0.9.0-cp311-cp311-manylinux_2_24_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 1.3 MB |
| Tags | CPython 3.11 Linux glibc 2.24+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
2b89bc2440187b0b5833dee310d4236ed1680c088472c1aa196547e9b7315654
|
|
BLAKE2b-256 checksum How to use checksums |
3e00e1d482061dd340a535ea09fefb300189a501c2234f353e550467748c40db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logRelease files / beam_model-0.9.0-cp311-cp311-macosx_14_0_arm64.whl
| Download URL | beam_model-0.9.0-cp311-cp311-macosx_14_0_arm64.whl |
|---|---|
| Size | 734.1 kB |
| Tags | CPython 3.11 macOS 14.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
cb36f59d85e8ce2e3d0a8e7717698a424c1f048b58a6c0237c494f8f6fe18c27
|
|
BLAKE2b-256 checksum How to use checksums |
35dd5515e7907cb63de3a83b14e2dc45fb810d6d70c5c1027880e38bac69f6db
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logSecurity for beam-model 0.9.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 21 files in this release have been uploaded with provenance metadata.
Attestation for beam_model-0.9.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 19, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.













