
BeforePush


A lightweight CLI that checks whether your Git branch is ready before pushing or opening a pull request.
Features
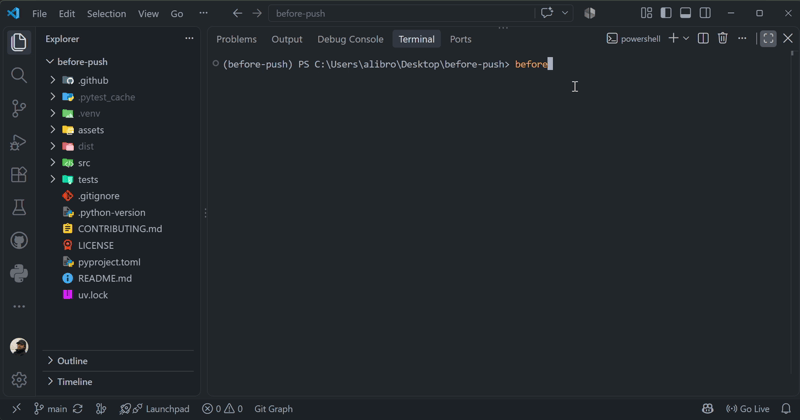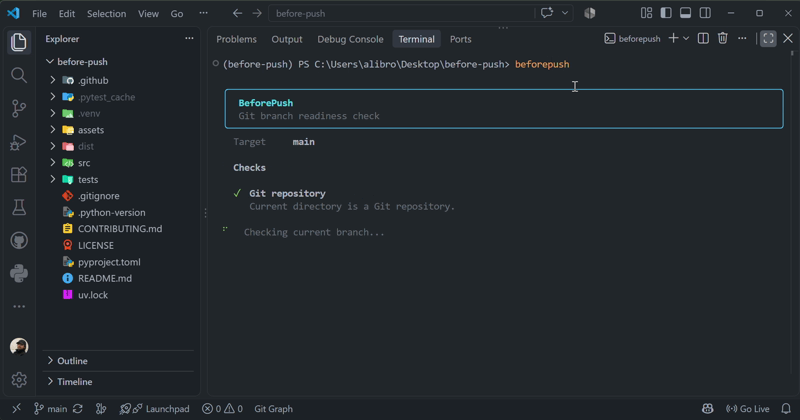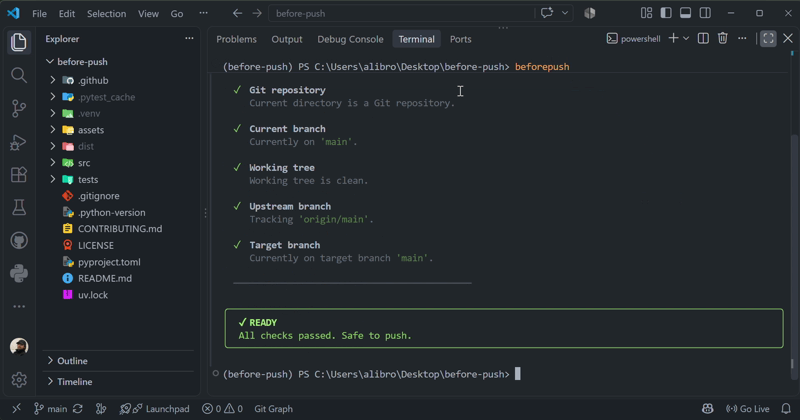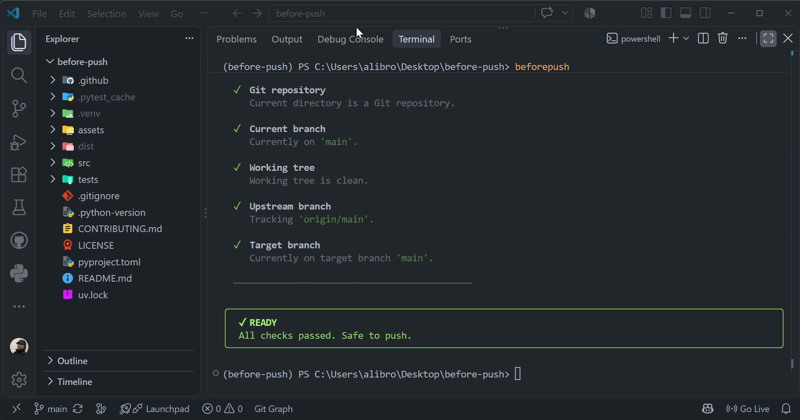
- Check if the current directory is a Git repository
- Show the current branch
- Detect uncommitted or untracked changes
- Check upstream branch configuration
- Check if the current branch is behind a target branch
- Show repository and Git-state diagnostics with
--verboseor-v - Run checks automatically before git push with a pre-push hook
- Support custom target branches
- Warn about newly staged files larger than 5 MB (configurable)
- Clean terminal output with Rich
Installation
Install BeforePush from PyPI:
pip install before-push
Usage
Run BeforePush inside a Git repository:
beforepush
To specify a different target branch:
beforepush --target develop
For detailed usage, including the --max-file-size option and Git pre-push hook instructions, see the documentation.
Demo
Contributing
Contributions are welcome! See CONTRIBUTING.md for development setup, testing, and contribution guidelines.
Contributors
Thanks to everyone who contributes to BeforePush! ❤️
Scope
BeforePush focuses on local Git branch readiness.
It does not create or merge pull requests, authenticate with GitHub, perform code reviews, manage remote repositories, or modify Git history.
License
This project is licensed under the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for before-push 0.1.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| before_push-0.1.5.tar.gz | 12.7 kB | Without provenance | Details for before_push-0.1.5.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| before_push-0.1.5-py3-none-any.whl | Python 3 | none | any | Details for before_push-0.1.5-py3-none-any.whl |
Total release size: 22.7 kB
Release files / before_push-0.1.5.tar.gz
| Download URL | before_push-0.1.5.tar.gz |
|---|---|
| Size | 12.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
67fd84c63d934fcc9c9c482241fb2aaa87e11c338fcf8c733ed04ccfb96cf903
|
|
BLAKE2b-256 checksum How to use checksums |
6b0e44fe0362e00f5a6dc8b1c3db3387a65744df957d502e54159cbf8f21b6b3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.11.32 {"installer":{"name":"uv","version":"0.11.32","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":null,"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":null}
|
Release files / before_push-0.1.5-py3-none-any.whl
| Download URL | before_push-0.1.5-py3-none-any.whl |
|---|---|
| Size | 10.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
b7a5ea1482f75b9e2e8378d8d7ecf8710f91aaa62ac35775dca0692618c2f213
|
|
BLAKE2b-256 checksum How to use checksums |
7c9bd467eb5fe4c2d8b4a0e939267035064465e634301fc065ee27d559e1dc7f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
uv/0.11.32 {"installer":{"name":"uv","version":"0.11.32","subcommand":["publish"]},"python":null,"implementation":{"name":null,"version":null},"distro":null,"system":{"name":null,"release":null},"cpu":null,"openssl_version":null,"setuptools_version":null,"rustc_version":null,"ci":null}
|
Security for before-push 0.1.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














