


An extremely fast, highly opinionated test scheduler for pytest.
The name comes from the Russian быстро (bystro), meaning “fast” or “quickly.”
Bistra is built for real test suites with uneven runtimes. It uses timing history to balance work across workers and reduce the wait for the last worker.
Run your tests with bistra. Keep your pytest fixtures, plugins, and options.
Benchmarks
Benchmarked on nine open-source projects, including pytest, Polars, SQLAlchemy, and Textual. Charts show one project.
- Machine: Apple M4 Max, macOS.
- Workers: 12 for Bistra and xdist; 1 for pytest.
- Timing history: none for cold runs, reused for warm runs.
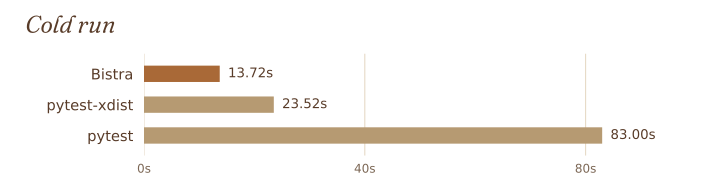
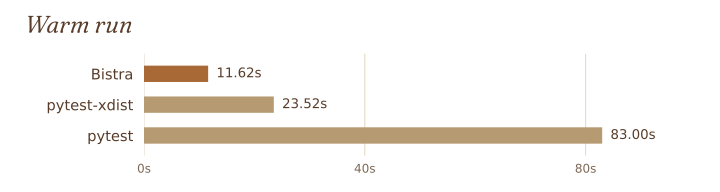
Installation
uv add --dev bistra
uv run bistra
Use your usual pytest options with bistra.
Workers default to the available CPU count. Override with -j or --workers:
uv run bistra -j 8
Try a few worker counts; the fastest setting depends on your machine and test suite.
For coding agents
Paste this into your agent:
Install Bistra and switch our local and CI test commands to `uv run bistra`.
Keep our existing plugins and test settings, remove xdist scheduling options,
and check that the tests still pass.
Plugins
Works with pytest-cov and pytest-testmon using their usual options:
uv run bistra --cov=my_package --cov-report=xml
uv run bistra --testmon
Bistra replaces xdist scheduling. Remove xdist options (-n, --dist,
--looponfail) from your commands and pytest config; xdist can stay installed.
Optimizations
- Timing history. Balances work using past test runtimes.
- Fixture locality. Keeps tests with shared fixtures together unless splitting them is predicted to be faster.
- Dynamic rebalancing. Redistributes queued work as workers become available.
- Less collection work. Reuses worker collection results in the controller.
Contributing
Bistra is early-stage software: expect bugs and breaking changes. Issues and PRs are welcome. See CONTRIBUTING.md to get started.
1 maintainer

Metadata
1 maintainer
Release files for bistra 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| bistra-0.1.0.tar.gz | 38.2 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| bistra-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 67.0 kB
Release files / bistra-0.1.0.tar.gz
| Download URL | bistra-0.1.0.tar.gz |
|---|---|
| Size | 38.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
d9fb239953b9f6e4081ff920fe85d2196810e3013d907de88819d4deea73a6b9
|
|
BLAKE2b-256 checksum How to use checksums |
c9490fa81e641006b81150aa8756cb7aef0f54f168a1317db7af247a36e48a9b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logRelease files / bistra-0.1.0-py3-none-any.whl
| Download URL | bistra-0.1.0-py3-none-any.whl |
|---|---|
| Size | 28.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
c642755d526e2987c6823721e64a7af68eb78b0b5623137c362a5fe9304896d5
|
|
BLAKE2b-256 checksum How to use checksums |
7c58858b7647e2b5d17ab78586ba6c111bafc791f81927631445874e2abc8fa8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logSecurity for bistra 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for bistra-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 22, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














