
📖 Book Cipher Kit
The cipher that needs no key — only a shared book.


"Anyone who has the book can read it. Anyone who doesn't, never will."
What is it?
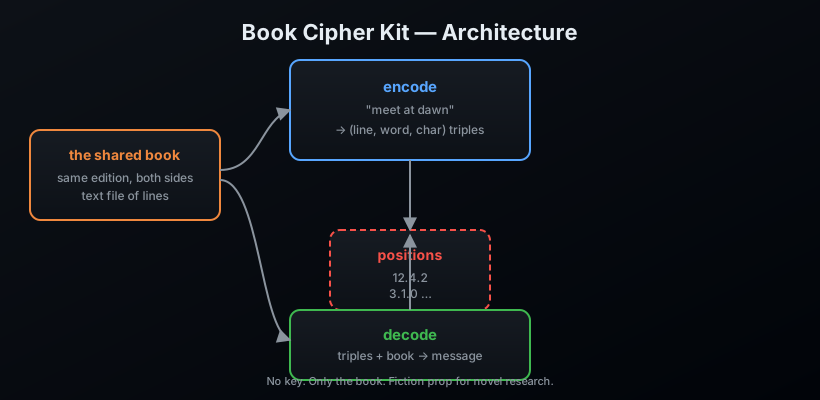
A book cipher encodes each character of a message as a position inside the words of a book: (line, word, character). Without the same edition of the same book, the positions are meaningless — and there is no key to steal, no algorithm to break, no trace to find. It is the cipher of lovers, prisoners, and people who trust each other with a bookstore.
Features
Core
- 🔡 Encode messages into
line.word.charposition triples - 📚 Decode them back with the same book
- 🎲 Optional seed for reproducible (or plausibly deniable) output
- 📊
stats— tells you what your book can and cannot encode - 🧾 Positions live in a plain text file — one triple per line, easy to hide
Formats & protection
- 📦 Convert positions between text / JSON / CSV / hex / base64 (
convert) - 🔒 Passphrase encryption of positions (PBKDF2 + counter-mode SHA-256 + HMAC)
- 🗝️ Book-derived one-time pad with a burn-after-use ledger (
otp-*) - 🧩 Shamir secret sharing of passphrases — k-of-n recovery (
share-*)
Steganography & disguise
- 📝 Hide positions inside generated prose (sentence-length codec,
stego-*) - 🛒 Disguise positions as a shopping list, server log, invoice, or schedule (
disguise-*) - 🔤 Acrostic and null-cipher message hiding
Analysis & operations
- 🩺
doctor— diagnoses a book, a position file, or a pair - 🕵️
attack— cryptanalysis yardsticks (chi-squared, IoC, entropy, leakage) - 🧮
grid-*— book-derived straddling checkerboard for compact digit streams - 🗣️
voice-*— render positions as phonetically distinct words to read aloud - 🧠
mnemonic— render a book fingerprint as a memorable word phrase - 🤝
verify-*— challenge/response ceremony proving you share the same edition - 📜
audit-*— hash-chained, tamper-evident operations log - 📬
send/receive— the whole pipeline (encode → encrypt/disguise → audit) in one envelope - 📦 Zero dependencies
Install
pip install book-cipher-kit
From source:
git clone https://github.com/AnonymoDGH/book-cipher-kit
cd book-cipher-kit
pip install -e .
Quickstart
# What can your book encode?
bookcipher stats --book novel.txt
# [*] Alphabet coverage: 98%
# [+] Found:   abcdefghijklmnopqrstuvwxyz
# [-] Missing: q

# Encode
bookcipher encode --book novel.txt --message "meet at dawn" --out coords.txt

# The courier carries only this:
cat coords.txt
# 12.4.2
# 3.1.0
# 87.12.5
# ...

# Decode on the other side
bookcipher decode --book novel.txt --input coords.txt
# meet at dawn
CLI reference
| Command | What it does |
|---|---|
bookcipher encode --book <f> --message <m> [--out <f>] [--seed <n>] |
Message → positions |
bookcipher decode --book <f> --input <f> |
Positions → message |
bookcipher decode --book <f> --positions "1.0.2 2.3.0" |
Inline positions |
bookcipher stats --book <f> |
Alphabet coverage report |
bookcipher convert --input <f> --to hex |
Convert between formats |
bookcipher encrypt --input <f> --passphrase <p> |
Encrypt positions |
bookcipher decrypt --input <f> --passphrase <p> |
Decrypt positions |
bookcipher otp-encrypt --book <f> --message <m> --page-start N --page-end M |
Book one-time pad |
bookcipher share-split --secret <s> --k 2 --n 3 --out-dir <d> |
Shamir split |
bookcipher share-combine --share <f> --share <f> |
Shamir recover |
bookcipher stego-hide --input <f> |
Hide positions in prose |
bookcipher disguise-hide --input <f> --scheme invoice |
Disguise as a document |
bookcipher doctor --book <f> |
Diagnose a book |
bookcipher attack --input <f> --book <f> |
Cryptanalysis yardsticks |
bookcipher grid-encode --book <f> --message <m> |
Compact digit stream |
bookcipher voice-hide --input <f> |
Positions → spoken words |
bookcipher mnemonic --book <f> |
Fingerprint → word phrase |
bookcipher verify-challenge --book <f> --salt <s> |
Edition-verification probes |
bookcipher audit-log --log <f> --op encode |
Append to audit trail |
bookcipher audit-verify --log <f> |
Verify audit chain |
bookcipher send --book <f> --message <m> [--passphrase <p> | --scheme <s>] |
Full send pipeline |
bookcipher receive --book <f> --input <env> |
Full receive pipeline |
How it works
Tests
pip install pytest
pytest
The suite covers every module — core encode/decode, formats, crypto, the one-time pad, Shamir sharing, steganography, disguise schemes, the checkerboard, voice/word maps, the edition-verification ceremony, the audit chain, and the end-to-end protocol — with deterministic seeds throughout.
License
MIT — a fiction research prop. Share the book, keep the story.
1 maintainer

Metadata
1 maintainer
Release files for book-cipher-kit 0.2.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| book_cipher_kit-0.2.0.tar.gz | 105.6 kB | Without provenance | Details for book_cipher_kit-0.2.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| book_cipher_kit-0.2.0-py3-none-any.whl | Python 3 | none | any | Details for book_cipher_kit-0.2.0-py3-none-any.whl |
Total release size: 189.9 kB
Release files / book_cipher_kit-0.2.0.tar.gz
| Download URL | book_cipher_kit-0.2.0.tar.gz |
|---|---|
| Size | 105.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
16a9a596260ba418b6d9dfa800ef44e4df7fcce981069e738d85365aa9b2a21a
|
|
BLAKE2b-256 checksum How to use checksums |
a8975f8efbb63ab3f5122ac8727964b37fe955ff93245dff6bc010c268447a1d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.14.3
|
Release files / book_cipher_kit-0.2.0-py3-none-any.whl
| Download URL | book_cipher_kit-0.2.0-py3-none-any.whl |
|---|---|
| Size | 84.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5353d0993dd0d5b7945ce23dd1a2d8d2008ec63699519608d75867d03b9f2712
|
|
BLAKE2b-256 checksum How to use checksums |
d9aff005cd9f6e5676c0801110466e66aa0f2ce52575b7d3c955cf3c647325a7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.14.3
|
Security for book-cipher-kit 0.2.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














