
CANopen Lens
Give it a candump log and it tells you, in plain words, what happened on your CANopen network and what to check — as a desktop app and as a Python library.
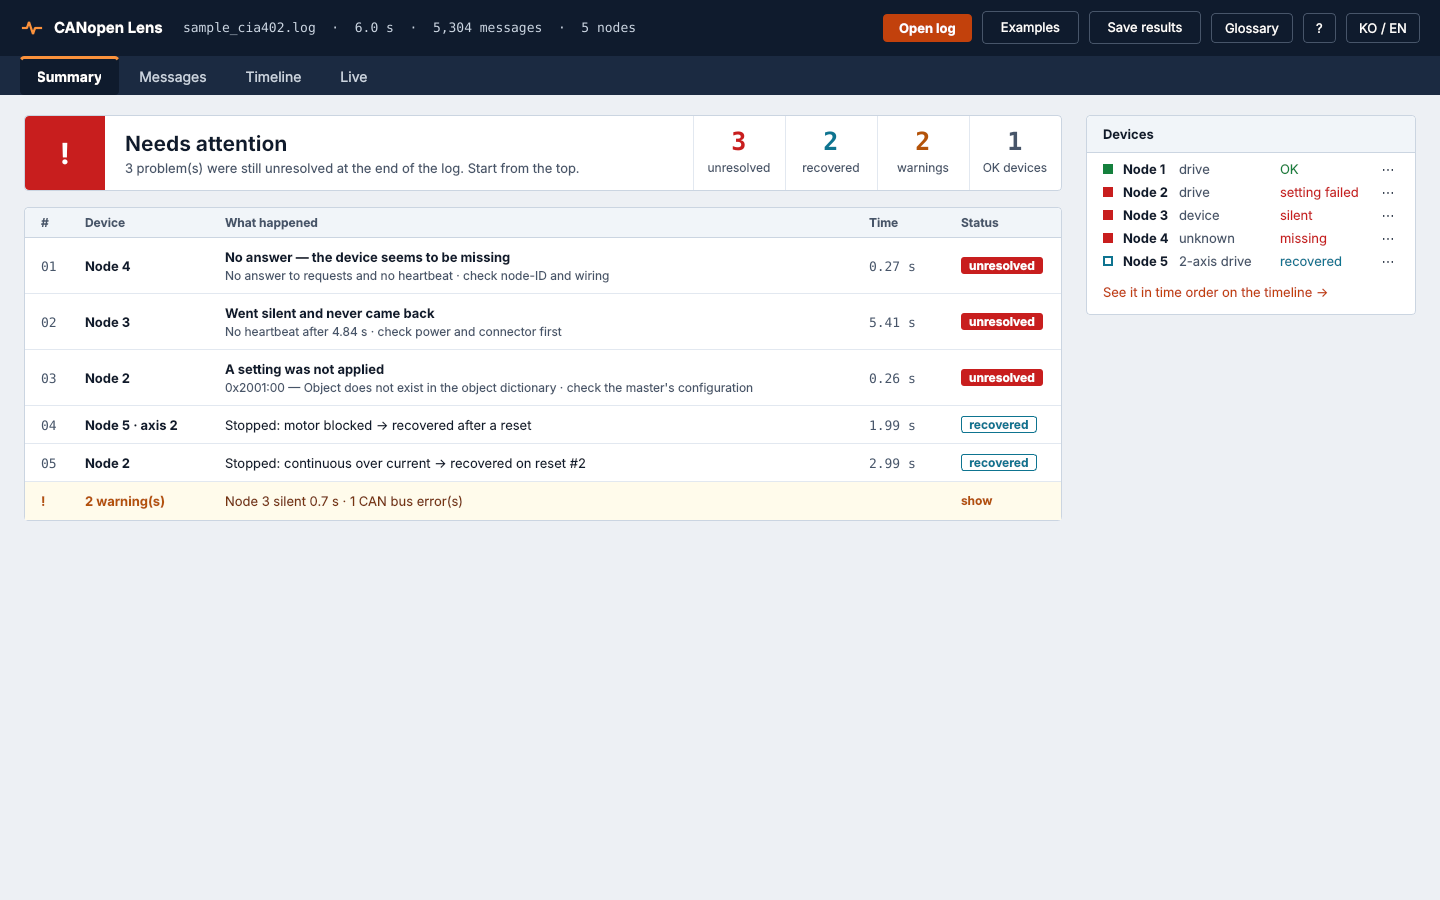
Made so that someone new to CANopen can find a root cause from a single log, without knowing CAN IDs or bytes:
- A verdict – "Problems found – 3 kinds of error, 1 kind of warning"
- The status of every device – "Node 5 (CiA 402 drive): had problems but recovered · Axis 2: faulted 1 time but recovered to Enabled"
- What to check first – every problem explained as What happened? / Why does it matter? / How to check
The UI and all explanations are available in English and Korean.
Install
1. Download the app (no Python needed)
Get the file for your computer from Releases, unpack it and run it.
| System | File | Run |
|---|---|---|
| Windows 10/11 | CANopenLens-…-windows-x64.zip |
double-click CANopenLens\CANopenLens.exe |
| Linux (Ubuntu 22.04+ and similar) | CANopenLens-…-linux-x86_64.tar.gz |
CANopenLens/CANopenLens |
| Raspberry Pi 4/5 (64-bit OS) | CANopenLens-…-linux-aarch64.tar.gz |
CANopenLens/CANopenLens |
2. pip (Python 3.9+)
pip install "canopen-lens[gui]"     # app + library
pip install canopen-lens            # library and command line only (servers, headless Pi)
Prebuilt wheels are published for Windows x64, Linux x86_64 and Linux aarch64, so no C++ compiler is needed.
Run canopen-lens to open the window.
Five-minute guide
- Record a log on the Linux PC or Raspberry Pi attached to the machine:
candump -l can0, reproduce the problem, stop withCtrl+C. (Saved console output such ascandump -t a can0 > log.txtworks too.) - Open it – drop the file on the window. No log yet? Pick an example under Try the sample log: a mixed network with many problems, or a two-wheel AMR (ros2_canopen master + STM32 two-axis drive) from boot-time PDO configuration to an E-stop and recovery.
- Read the overview – the colour at the top is the verdict; below it are the status of each device and the problems to check first, most important first. Repeats of the same problem are shown once with a count.
- Dig deeper – Show the messages jumps to the moment of a problem, with every message explained in one line.
- Live monitor – the Live monitor tab connects to a USB-CAN adapter or SocketCAN and shows messages and problems as they happen (
socketcan,pcan,kvaser,ixxat,vector,slcan,gs_usb). No hardware? Pick Demo to replay the sample log in real time. Everything received is recorded and can be saved as a candump file or opened in log analysis with one click. - State timeline – how each device and motor axis changed state over time. Red is a fault, a gap means the device went silent. Click a bar to jump there.
Unknown words are explained under Glossary. Save results writes a readable report (.txt), JSON or an Excel-friendly CSV.
What it finds
| Finding | In plain words |
|---|---|
| SDO failed | The device refused a setting; the abort code is explained together with where to look |
| No SDO answer | The device did not reply; check node-ID, power and wiring in that order |
| Emergency (EMCY) | The device reported an error; the code is turned into readable text |
| Heartbeat gap / stopped | The device went quiet for longer than its normal period, or never came back |
| Unexpected restart | The device rebooted without a reset command (power dip, watchdog, …) |
| Drive fault | A motor drive stopped with a fault; the EMCY at the same moment is linked as the likely cause |
| Enable did not work | Enable operation was sent but the drive never turned on (wrong order, motor power, STO) |
| Fault reset did not work | A reset was sent but the fault stayed (its cause is still there) |
| Quick stop | The drive entered quick stop |
| CAN bus errors | Corrupted traffic on the wires (termination, bit rate, cabling) |
Verdicts: ✔ OK – nothing went wrong · ▲ recovered – something went wrong but was fine again at the end of the log · ✖ needs attention – still wrong at the end (fault, silent device) or a setting was not applied.
How a log is analysed
(1760500002.000250) can0 185#3702180220030000
 └ time               └ port └ ID └ data bytes
- Who sent what. CANopen IDs are "message type + node-ID":
0x185=0x180(TPDO1, real-time data from a device) + node 5. - Where the values are. Which values sit where inside a PDO (the PDO mapping) is taken from, in this order: SDO configuration found earlier in the log → the EDS you attach → the CiA 402 default (assumed, axis 1 only).
- Values into words. Here: axis 1 statusword + axis 2 statusword + axis 1 actual velocity →
TPDO1: Axis 1 state: Enabled (SW 0x0237), Axis 2 state: Fault (SW 0x0218), Axis 1 Velocity actual value=800. - Following the story. SDO questions are paired with answers; each node's heartbeat period is learned and late heartbeats are flagged; every CiA 402 axis gets its own state machine, commands are checked against the state that follows, and EMCY messages around a fault are linked to it.
- Grouping. Identical findings are collapsed and sorted by importance.
Clicking a message shows a byte-by-byte breakdown. For 582#4300100092010200: 43 = command byte (binary 010 0 00 1 1: read reply, value inside the frame, 4 bytes), 00 10 = index 0x1000 read back to front (CANopen sends the least significant byte first), 00 = sub-index, 92 01 02 00 = 0x00020192: profile 0x0192 = 402 (drive), additional info 0x0002 = servo drive.
Not CANopen? candump records every frame regardless of protocol. If a log has no heartbeat/NMT/SDO/EMCY/SYNC at all, or mostly 29-bit IDs (J1939, vendor protocols), the overview says so instead of pretending, and shows a protocol-independent traffic by ID table (count, period, largest gap, DLC).
Decoding runs in C++; a two-million-frame log opens in one to two seconds on an ordinary PC, and only the rows on screen are turned into text, so large logs stay responsive.
Using it from Python
from canopen_lens import open_log, Kind

log = open_log("robot.log", eds={1: "drive.eds"})   # EDS optional

print(log.report("en"))                  # the whole readable report

h = log.health("en")                     # verdict, per-node status, grouped findings
for group in log.grouped_issues():
    ex = log.explain(group.first, "en")
    print(ex.title, group.count, ex.steps)

df = log.to_dataframe("en")              # pandas (pip install pandas)
log.to_csv("frames.csv")                 # UTF-8 with BOM, opens cleanly in Excel
log.to_json("result.json")

for row in log.trace.filter(kinds=[Kind.EMCY], node=2):
    print(log.summary(int(row), "en"))
for p in log.trace.axis_timeline(5, axis=1):  # node 5, axis 2
    print(p.t, p.state)
Live bus (python-can)
import can
from canopen_lens import LiveDecoder

dec = LiveDecoder(eds={1: "drive.eds"})
with can.Bus(interface="socketcan", channel="can0") as bus:
    dec.run(bus, lang="en")              # prints findings the moment they happen
Or push frames yourself with dec.feed(t, can_id, data). Only the newest frame is kept, so memory stays flat however long it runs.
Command line / CI
canopen-lens report robot.log                          # readable report
canopen-lens report robot.log --brief --fail-on-error  # exit code 1 on errors
canopen-lens report robot.log --format json -o result.json
canopen-lens report robot.log --format csv -o frames.csv
canopen-lens live --channel can0 -v                    # pip install "canopen-lens[live]"
Type hints are included for IDE completion.
Limitations
- Log files must be in
candumpformat; PCAN.trcis next (the live monitor can use PCAN adapters directly). - PDOs are assumed to use the default COB-IDs (
0x180 + node, …); COB-IDs changed through0x1400/0x1800are not followed yet. - Axes 2–8 of multi-axis drives are decoded when the EDS or the log provides their PDO mapping.
- Findings are guidance based on what the log shows; the device manual has the final word.
- The Python API may still change before 1.0.
Development
git clone https://github.com/lch-98/canopen-lens
cd canopen-lens
pip install -e ".[gui,test,pandas,live]"
pytest
python tests/make_sample.py      # regenerate the mixed-network example
python tests/make_amr_sample.py  # regenerate the two-wheel AMR example
Releases: see RELEASING.md.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for canopen-lens 0.4.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| canopen_lens-0.4.1.tar.gz | 1.8 MB | With provenance | Details for canopen_lens-0.4.1.tar.gz |
Built distributions (wheels)
Total release size: 11.0 MB
Release files / canopen_lens-0.4.1.tar.gz
| Download URL | canopen_lens-0.4.1.tar.gz |
|---|---|
| Size | 1.8 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
930da79e8d4cc759d169c9c54a1a8b610225e8d30fd257aa4d30af6520d9ecf7
|
|
BLAKE2b-256 checksum How to use checksums |
1cc6350bf01f83a3293b487046a8bc6df87ae19769c1b6e7609e2b9e8e6be030
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp314-cp314-win_amd64.whl
| Download URL | canopen_lens-0.4.1-cp314-cp314-win_amd64.whl |
|---|---|
| Size | 610.5 kB |
| Tags | CPython 3.14 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
40ab212703488cdfac69f26fae2c3122ac3313877ae70c740a5fbc5079757eb7
|
|
BLAKE2b-256 checksum How to use checksums |
e5b903470361172773c43ef992db34768826f222c635a5e6b187c2a20a76bf7c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp314-cp314-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | canopen_lens-0.4.1-cp314-cp314-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 482.3 kB |
| Tags | CPython 3.14 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
fd2cf535265cc6d4291688360841d73a0a14f387b8f4d3205496aa1f0168b8eb
|
|
BLAKE2b-256 checksum How to use checksums |
d59eee9d5f5808b61400648b5527fb5f79795a8b163b18e66feac8f5d72316c4
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp314-cp314-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | canopen_lens-0.4.1-cp314-cp314-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 454.2 kB |
| Tags | CPython 3.14 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
cf0f2db412d82b3570fb7bd18ca2a4161fba11dbe1d103e8802c38649b321c62
|
|
BLAKE2b-256 checksum How to use checksums |
33a590acbd09ca8497e8c19a316385c1c323e18ac830e4e7164994afa20ebdb7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp313-cp313-win_amd64.whl
| Download URL | canopen_lens-0.4.1-cp313-cp313-win_amd64.whl |
|---|---|
| Size | 594.0 kB |
| Tags | CPython 3.13 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
9ab8144493a2e4a820f7908ee353f44228eceda6157b6e4f61dc09ab05db948f
|
|
BLAKE2b-256 checksum How to use checksums |
2ce342ecc547554789e8d0c3d5dffa0e06c27211f5e65babc0cdd89200219f35
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | canopen_lens-0.4.1-cp313-cp313-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 482.6 kB |
| Tags | CPython 3.13 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
3b279651a1edfc57cceea798f593dafc2a26a0047a03532fb21ec19c515cdbde
|
|
BLAKE2b-256 checksum How to use checksums |
29ad327d253aebddc88a276c771f6e6d25badc4900417c34c40699d190eaeccc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp313-cp313-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | canopen_lens-0.4.1-cp313-cp313-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 453.6 kB |
| Tags | CPython 3.13 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
d54ba663b57fde346b3cb4c885451a78f326288676e9733534f04f0b5d281d28
|
|
BLAKE2b-256 checksum How to use checksums |
130c9cb7f94d20e468bae022c1176c921a2946140a2d64827c3844dc78cccef5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp312-cp312-win_amd64.whl
| Download URL | canopen_lens-0.4.1-cp312-cp312-win_amd64.whl |
|---|---|
| Size | 593.9 kB |
| Tags | CPython 3.12 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
e634449a925f05f48583e9d330a6c113e50be4c63b5e5f101f1778b8f014120c
|
|
BLAKE2b-256 checksum How to use checksums |
6427b5fa8bc0a139623825007b9480d0cbf7936075b90afe6acd04630da9faab
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | canopen_lens-0.4.1-cp312-cp312-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 482.5 kB |
| Tags | CPython 3.12 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
d5ae77c1895756aa8292f2a7001722b7ae53d25fab798ac746c0c9c2f60a17b9
|
|
BLAKE2b-256 checksum How to use checksums |
fc9a758fac66e541c6d2ab51862a2048b7e316c4fd1de97351f233f9e6299c5f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp312-cp312-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | canopen_lens-0.4.1-cp312-cp312-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 453.6 kB |
| Tags | CPython 3.12 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
cc216a9dfeb9b581eced51fab2338298c006973f3a078e7222189c9e27694ee2
|
|
BLAKE2b-256 checksum How to use checksums |
bf87dad52914a7d15e5f55daeb8bbbaba834b0b2f6254c96e47adaba2d71b77f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp311-cp311-win_amd64.whl
| Download URL | canopen_lens-0.4.1-cp311-cp311-win_amd64.whl |
|---|---|
| Size | 591.9 kB |
| Tags | CPython 3.11 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
0b738381d14f2834da6de523d9b26569c87ddbd314e746858447a3797c53a572
|
|
BLAKE2b-256 checksum How to use checksums |
7e4f6d4d6b7c74fa3da9d448ec34c1790f1c1b91a16a8705b645126ee9fc2134
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | canopen_lens-0.4.1-cp311-cp311-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 481.0 kB |
| Tags | CPython 3.11 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
9d0b4b858e5dd226390edd79e15d790c0a207ead0c1e989d0864ad5cd6145da7
|
|
BLAKE2b-256 checksum How to use checksums |
7db7f4f9f536a1037031d09c69559f1dd6913bb6863b65676580d3a981b370c8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp311-cp311-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | canopen_lens-0.4.1-cp311-cp311-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 452.1 kB |
| Tags | CPython 3.11 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
6d1651a07bbf54965173fe6def13f72e4b3b59b432e4f95414bd31e81d841081
|
|
BLAKE2b-256 checksum How to use checksums |
62d86d075eb68ddc29b745fae7169a894810249dbd293684e9c62bc31691ce3d
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp310-cp310-win_amd64.whl
| Download URL | canopen_lens-0.4.1-cp310-cp310-win_amd64.whl |
|---|---|
| Size | 590.4 kB |
| Tags | CPython 3.10 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
e02bbc02a626f96da72558c2a63d11c4708a90255a7ff42668d980121c0d41fc
|
|
BLAKE2b-256 checksum How to use checksums |
abee93a818ecdd29f67ba6b6f8f30c4f79c3707a6a84e3fd0ce15a7add2aac40
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp310-cp310-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | canopen_lens-0.4.1-cp310-cp310-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 479.5 kB |
| Tags | CPython 3.10 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
ebca840e7882eae593a0016bec24094ee3fd40c53031cd0d7c6bfb98540b3afb
|
|
BLAKE2b-256 checksum How to use checksums |
59d269c87972a689a6c0dfb12119229ed0ff7c472907885066be6e823ad4eca3
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp310-cp310-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | canopen_lens-0.4.1-cp310-cp310-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 450.8 kB |
| Tags | CPython 3.10 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
0fec94678f11f59d9aea5bfd5e475e5312f800a0771f5c6721804fd5d0ebeef0
|
|
BLAKE2b-256 checksum How to use checksums |
ae99fc5656b2df863a7f95c483e11c0a44217bcf2d39dc369e297fbd67bab94a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp39-cp39-win_amd64.whl
| Download URL | canopen_lens-0.4.1-cp39-cp39-win_amd64.whl |
|---|---|
| Size | 591.2 kB |
| Tags | CPython 3.9 Windows x86-64 |
|
SHA-256 checksum How to use checksums |
1175f297ab859cff46cb438f8a6d55e63d911573d181a4db639e3ebc5e49d89e
|
|
BLAKE2b-256 checksum How to use checksums |
8177352a9891f718abc4e1d98b4762d7381dcadc86478833a66b8479171d3cb5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp39-cp39-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl
| Download URL | canopen_lens-0.4.1-cp39-cp39-manylinux_2_27_x86_64.manylinux_2_28_x86_64.whl |
|---|---|
| Size | 479.9 kB |
| Tags | CPython 3.9 Linux glibc 2.27+ x86-64 Linux glibc 2.28+ x86-64 |
|
SHA-256 checksum How to use checksums |
d3858191c7e6c8374d64da0804f77bee0a46016df407f8aa91c738c0973762d2
|
|
BLAKE2b-256 checksum How to use checksums |
ae1ea3300f23cf9d52ecbd127e4f6f0487bd010e4fcda6d2734c76f95da3dd51
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / canopen_lens-0.4.1-cp39-cp39-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl
| Download URL | canopen_lens-0.4.1-cp39-cp39-manylinux_2_26_aarch64.manylinux_2_28_aarch64.whl |
|---|---|
| Size | 451.0 kB |
| Tags | CPython 3.9 Linux glibc 2.26+ ARM64 Linux glibc 2.28+ ARM64 |
|
SHA-256 checksum How to use checksums |
c704f0a5d1e34dfe47f296a06eac92dc65ea59ef8d9077fa4ff1a0e55182657a
|
|
BLAKE2b-256 checksum How to use checksums |
24c961a5e5f2ae841ee6aab93c9405168c4f7dc55438971f57f03e9b07199b09
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logSecurity for canopen-lens 0.4.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 19 files in this release have been uploaded with provenance metadata.
Attestation for canopen_lens-0.4.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














