
Your best training data is rotting in ~/.claude. cc-steer mines every correction, interrupt, and rejected plan from your transcripts into judge-refined, TRL-ready SFT/DPO/KTO pairs on HuggingFace.



Get started
uvx cc-steer scan
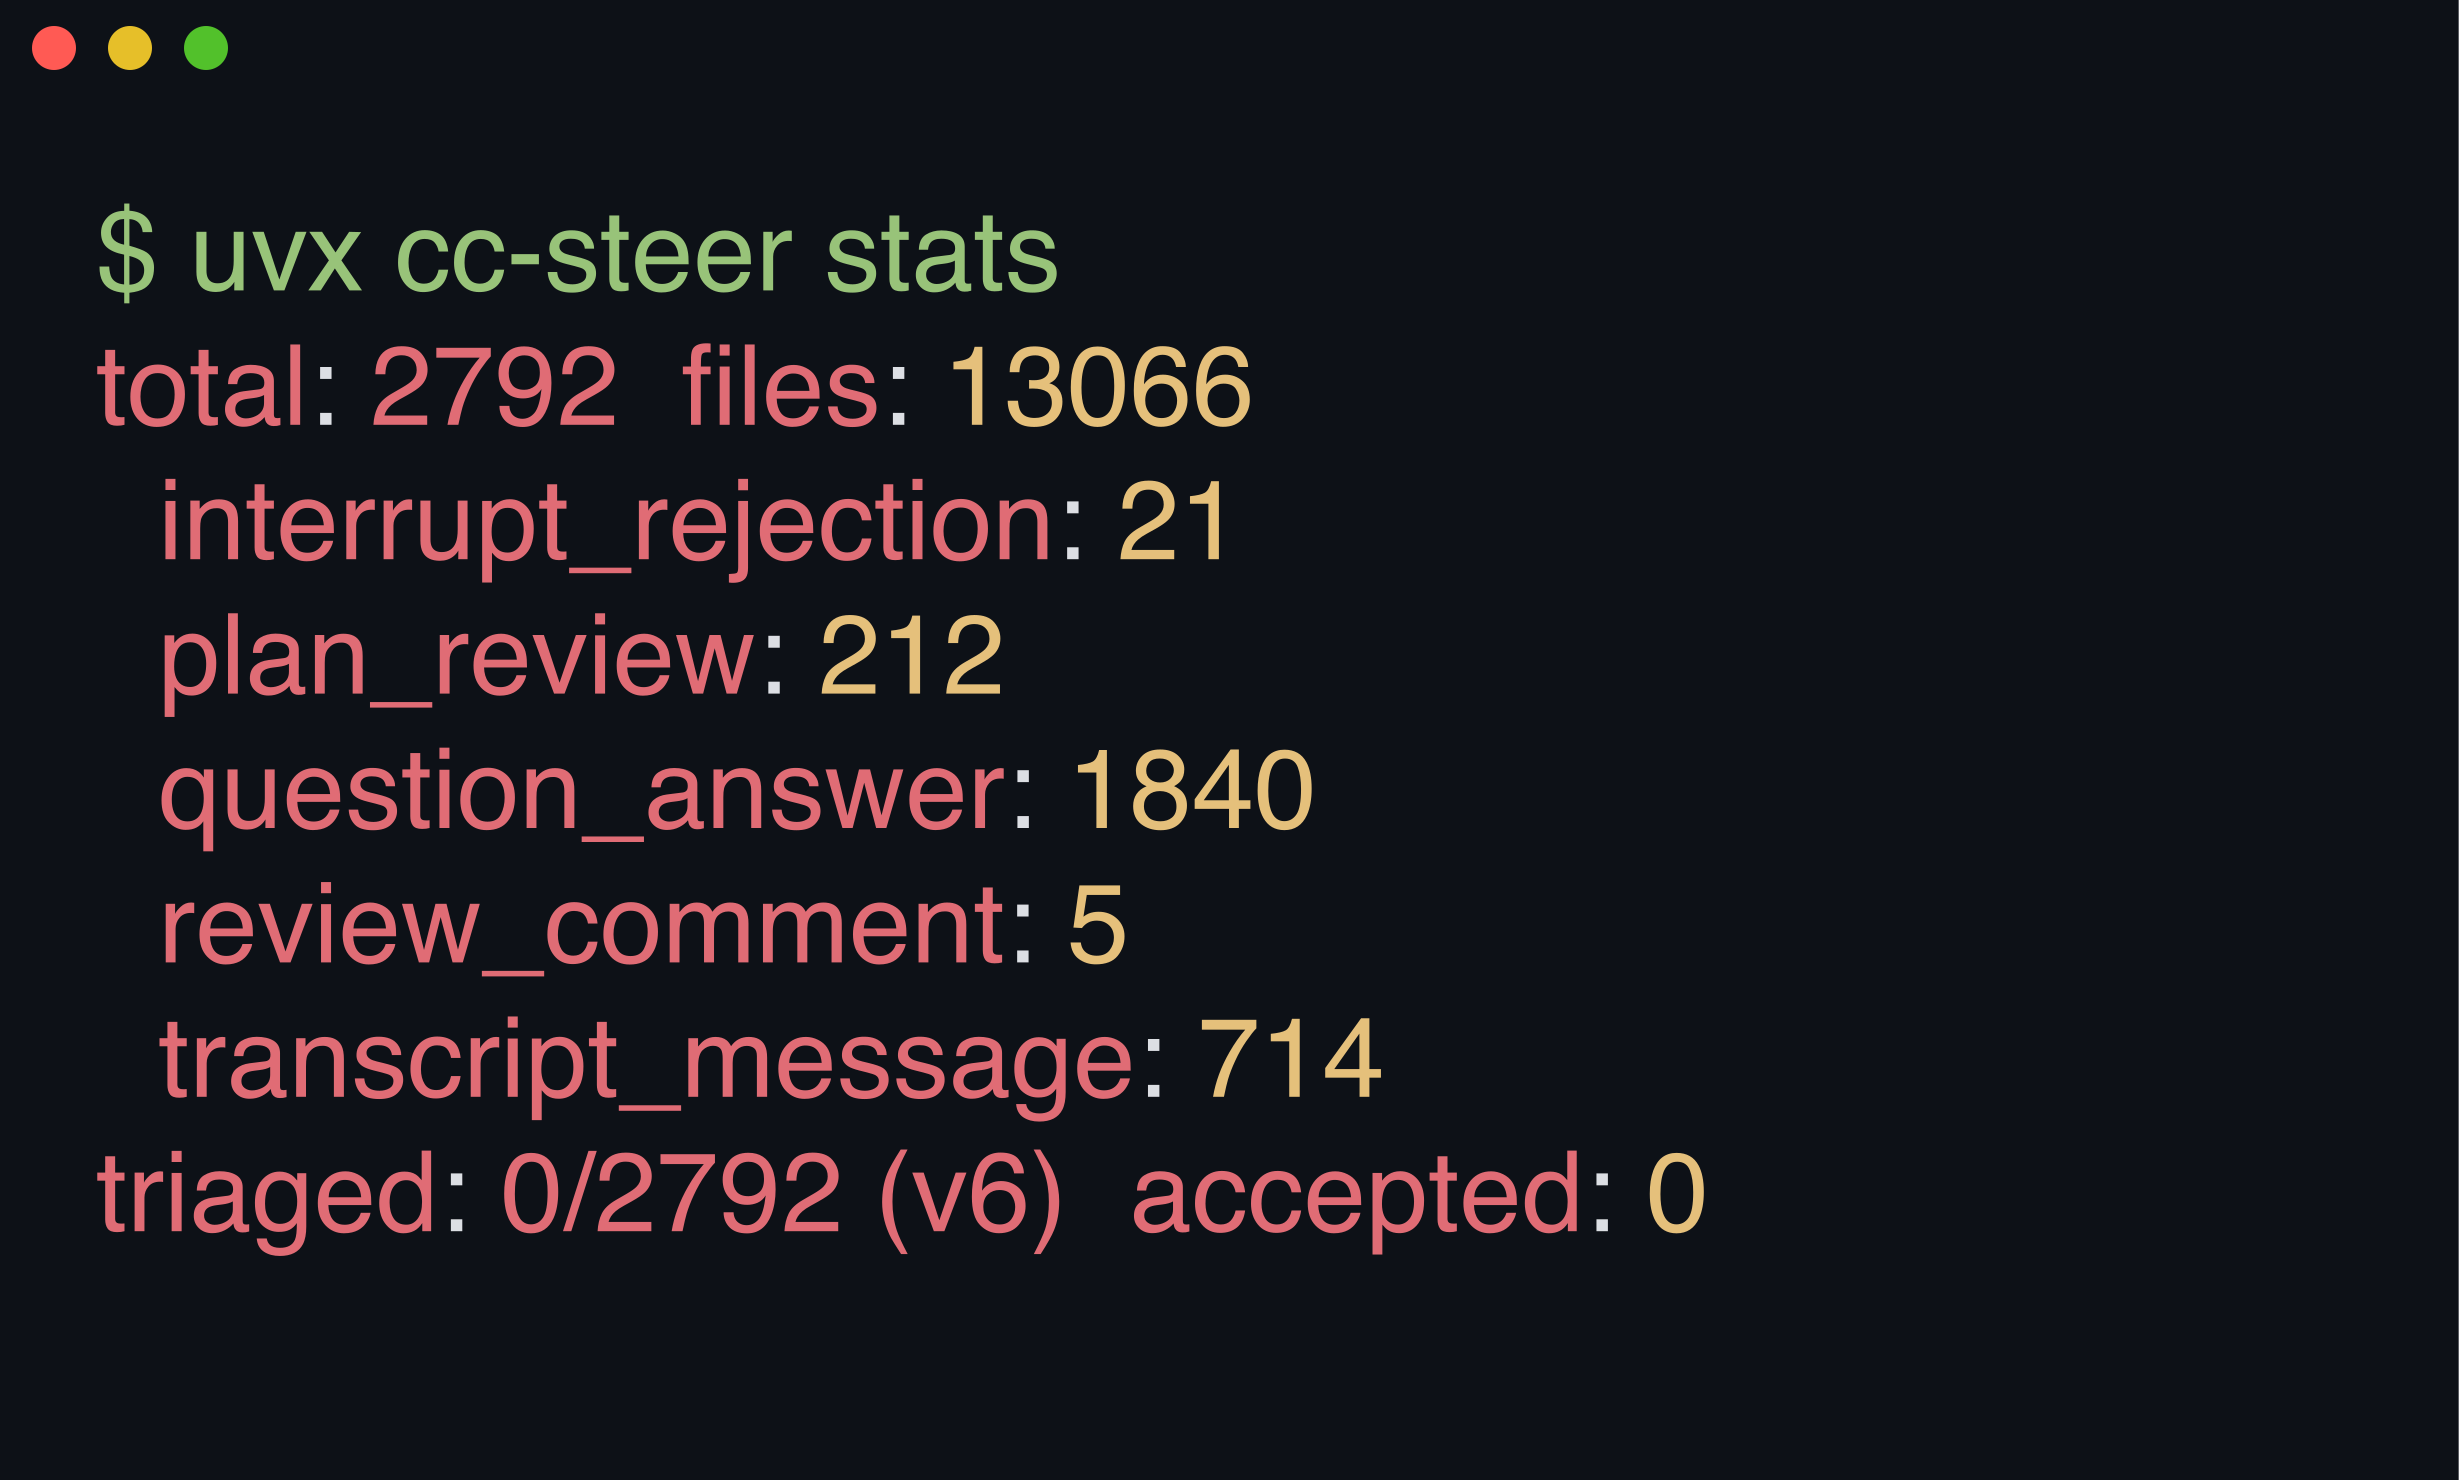
One pass over ~/.claude/projects fills ~/.cc-steer/feedback.db with every correction you typed, every plan you rejected, every question you answered, and every inline review comment, conversational context included. stats shows what landed:
Driving with an agent? Paste this:
Run `uvx cc-steer scan` to mine my Claude Code transcripts into ~/.cc-steer/feedback.db.
Then run `uvx cc-steer stats` and report how much steering was collected per source kind.
Docs: https://yasyf.github.io/cc-steer/
Use cases
Build a training set from feedback you already gave
You've spent months telling Claude "no, not like that", and that signal evaporates as transcripts rotate out. Judge the corpus, then distill the accepted events into atomic pairs, the corrective ones grounded in the code they fault:
uvx cc-steer triage
uvx cc-steer refine
uvx cc-steer enrich
uvx cc-steer pairs prints the deliverable. Each training pair is distilled from your own steering and carries the conversational window and code evidence behind it.
See how you actually steer, across every project
Your taste is mostly tacit, and you notice a rule only when it's violated. The corpus makes it legible:
uvx cc-steer list --source plan_review
On my machine the split is 1,840 answered questions, 714 mid-session corrections, 212 rejected plans, 21 interrupts, and 5 review comments. Another machine's history folds in too. Mirror it with rsync and point scan --transcripts at it; scans are repeatable, so several mirrors fold into one corpus.
Push a private SFT/DPO/KTO dataset to your HuggingFace namespace
A judged corpus in SQLite trains nothing. Export projects it into TRL-ready configs:
uvx cc-steer export --push
traces: train 1156  test 115
sft: train 499  test 67
dpo: train 363  test 44
kto: train 1156  test 115
Four configs land as per-split parquet in a private <hf-user>/cc-steer-traces, next to a generated dataset card. Splits group on the session hash, so a session never straddles train and test.
Retrain the watcher that steers you back
The exported views close the loop: cc-steer's live watcher — a local 4-bit LoRA that drafts steers as you work — retrains from them on Tinker, gated so a worse model never ships:
uvx --from 'cc-steer[retrain]' cc-steer retrain --component watcher
With a Tinker key in ~/.cc-steer/tinker.env, one run curates the training pool, trains under a hard spend cap ($15 default), scores the candidate server-side against a frozen eval, and promotes only on a strict beat of the incumbent: higher sentinel AUC, fire budget held, coverage wins. On a promote, the watch daemon restarts on the new adapter; on a reject, production never notices. --component gate retrains the stage-1 lexical gate the same way, minus the GPU bill, and cc-steer pipeline install-launchd schedules both for Sunday 4am.
More in the docs
- Incremental scanning explains how content digests and one-transaction commits keep re-scans cheap and interrupt-safe.
- Triage, audit, and eval cover prompt-versioned judging, a seeded audit sample, and mechanical metrics that need no LLM calls.
- view-samples serves a local dashboard for browsing refined pairs and their full lineage.
- The Python API drives the scanner and the feedback store from your own code.
- Retraining covers the weekly gate and watcher lanes, the promotion gate's math, and the frozen-eval store.
cc-steer is alpha. The pipeline runs end to end, and the judge prompt still iterates (v6 today).
Read the docs for the full guide. Licensed under PolyForm Noncommercial 1.0.0.
1 maintainer

Metadata
1 maintainer
Release files for cc-steer 0.20.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| cc_steer-0.20.0.tar.gz | 268.2 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cc_steer-0.20.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 582.9 kB
Release files / cc_steer-0.20.0.tar.gz
| Download URL | cc_steer-0.20.0.tar.gz |
|---|---|
| Size | 268.2 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
5871e507004075245ba439d5a7826718882de95ea274b7cf90e05407a356fea3
|
|
BLAKE2b-256 checksum How to use checksums |
6121ff07cb1e4cdcf119e988d08c4f001ded709cc164d8cdb841adcb0ab84d91
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 23, 2026.
Transparency logRelease files / cc_steer-0.20.0-py3-none-any.whl
| Download URL | cc_steer-0.20.0-py3-none-any.whl |
|---|---|
| Size | 314.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
1ebfad41483634e5a1442538a7df1ae65da786ee4265cae094db1ebcaf5e8a82
|
|
BLAKE2b-256 checksum How to use checksums |
25c5bd392900e5a39f3d6288023674acd659bb5f1061dfe7cb8ee6e8ee50b464
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 23, 2026.
Transparency logSecurity for cc-steer 0.20.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for cc_steer-0.20.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 23, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














