
cc-tap


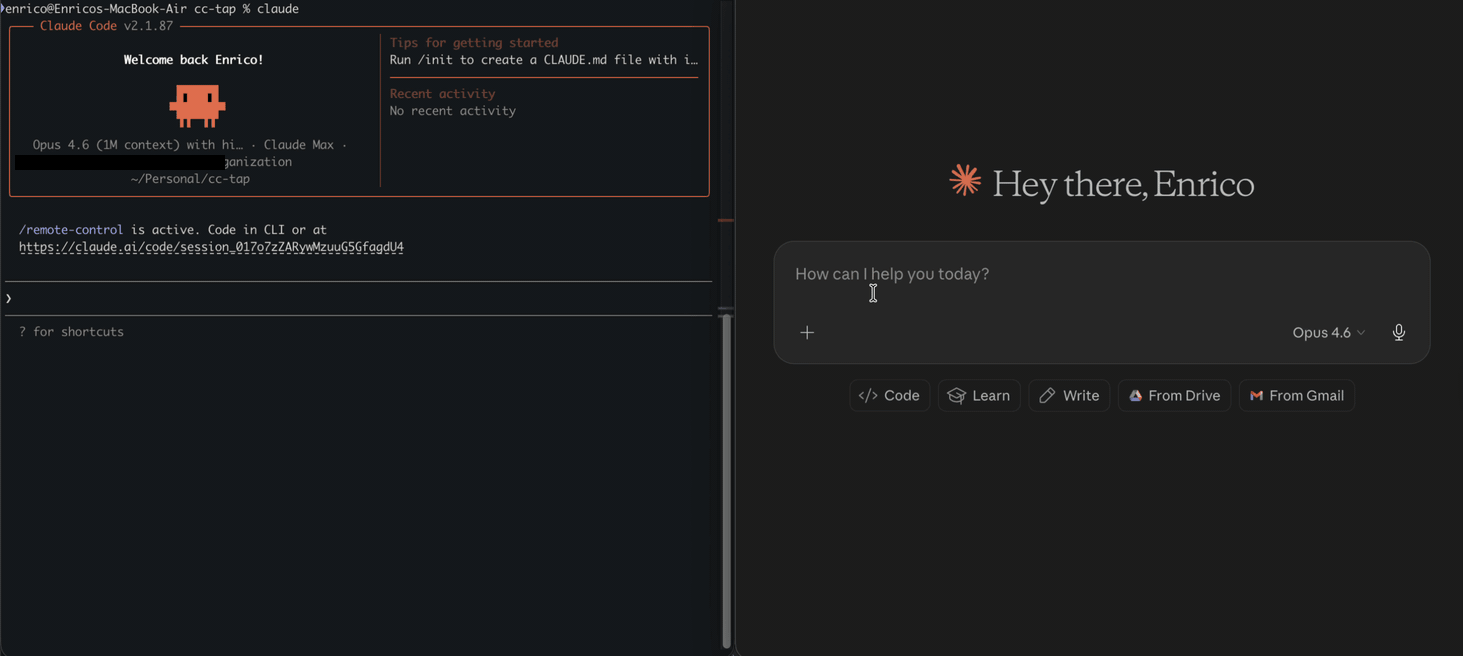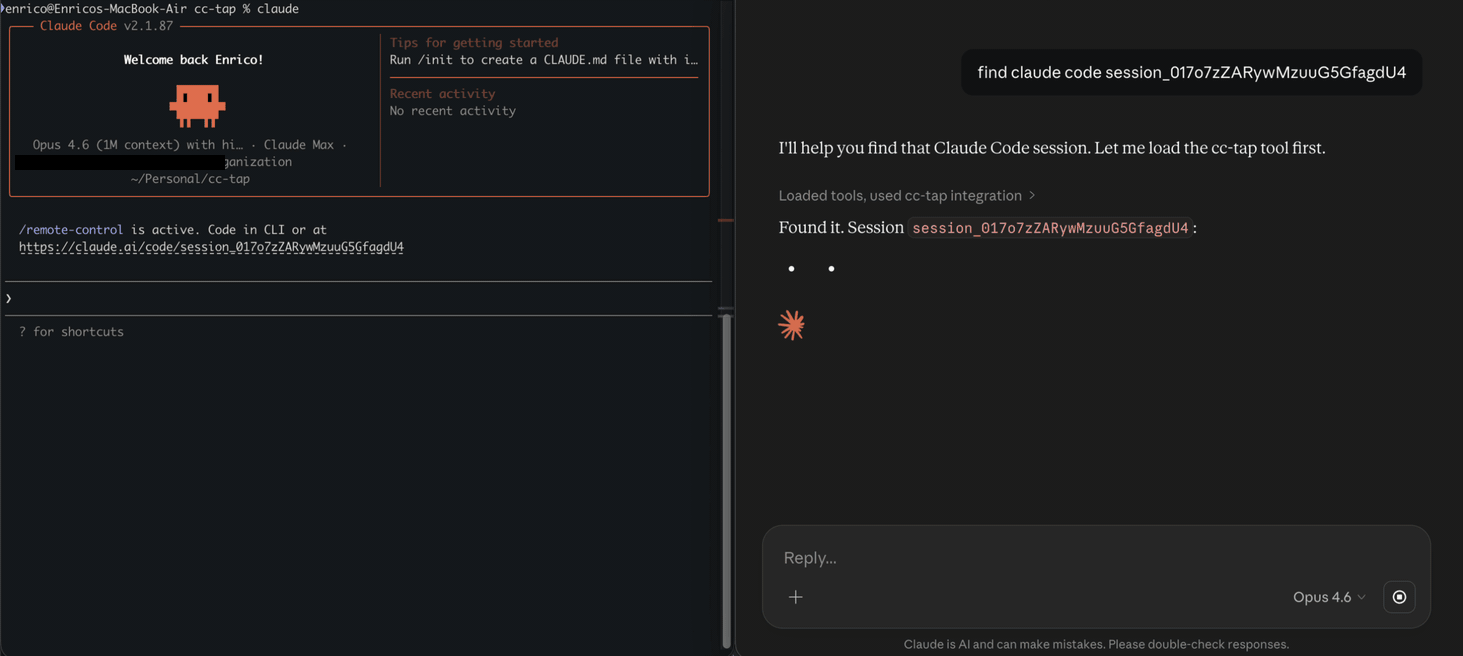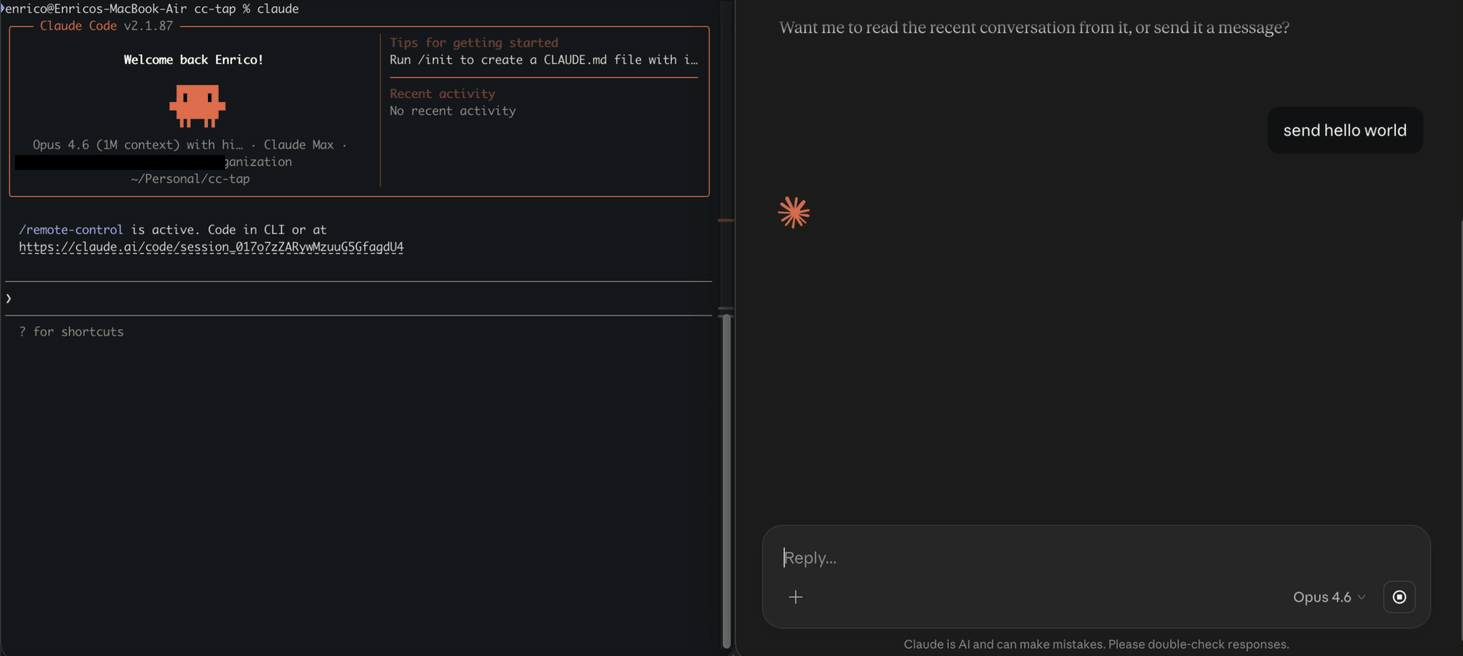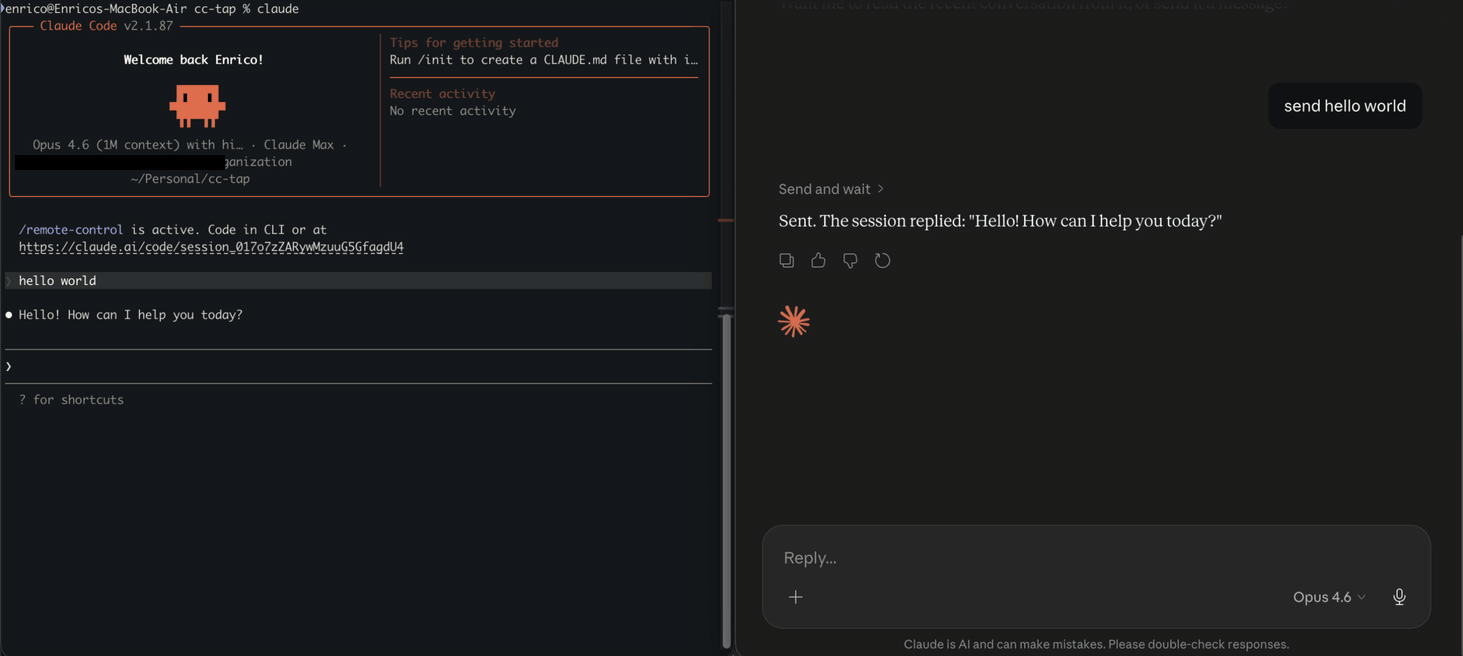
Experimental MCP server that lets Claude Desktop see into and interact with Claude Code Remote Control sessions.
Example: Ask Claude Desktop "what's my Code session working on?" and get a real answer.
Why this exists
Claude Desktop and Claude Code are separate worlds. Both build up rich context on your project, but neither can see what the other is doing. A design idea on Desktop that should drive an implementation in Code, or an implementation detail in Code that the Desktop conversation needs; both require you to copy-paste between windows and re-explain context that already exists.
Claude Code's Remote Control lets you drive a session from another device, but that's still you driving the same session. cc-tap is for the other axis: letting a different agent (Claude Desktop, or another Claude Code instance) read and interact with a running CC session through MCP.
Who is this for
- Developers who use both Claude Desktop and Claude Code
- Anyone who wants to monitor or interact with CC sessions programmatically
- Multi-agent workflows where one Claude instance needs to coordinate with another
Quickstart
pip install cc-tap
Requires an active Claude Code login (claude /login) and Remote Control enabled.
Claude Code
claude mcp add cc-tap -- cc_tap
Claude Desktop
Add to claude_desktop_config.json:
{
  "mcpServers": {
    "cc-tap": {
      "command": "cc_tap",
      "args": []
    }
  }
}
Tools
| Tool | Description |
|---|---|
list_sessions |
List all CC sessions (optionally filter by status) |
get_session_info |
Get details about a specific session |
read_session |
Read recent conversation from a session |
get_session_events |
Get raw events, optionally filtered by type |
send_message |
Send a message to a CC session (fire and forget) |
send_and_wait |
Send a message and wait for the full response |
How it works
cc-tap reads your Claude Code OAuth credentials (from macOS Keychain or ~/.claude/.credentials.json) and talks to the same API that Claude Code's Remote Control web UI uses. No additional authentication needed.
Sessions are accessed via HTTP polling (~1.5s latency). Messages you send appear in the target CC session as if typed by the user.
Limitations
- Tool approval — the session runtime only picks up approvals via WebSocket (behind Cloudflare bot protection). You can see pending tool requests via
send_and_wait, but must approve them in the CC terminal or claude.ai/code web UI. - Not real-time — uses HTTP polling, not WebSocket streaming. ~1.5s latency.
- Undocumented API — uses internal Anthropic endpoints that may change without notice.
- Local only — reads credentials from the local machine. Can't be deployed as a remote service.
Protocol
See PROTOCOL.md for the reverse-engineered Claude Code Remote session API documentation.
Development
git clone https://github.com/es617/cc-tap.git
cd cc-tap
pip install -e ".[dev,test]"
pre-commit install
pytest
Disclaimer
This project is an experimental research tool for personal and educational use. It interacts with undocumented, internal Anthropic APIs that are not part of any public or supported API surface. These endpoints may change, break, or be removed at any time without notice.
This project is not affiliated with, endorsed by, or supported by Anthropic. Use it at your own risk. The authors assume no responsibility for any consequences of using this tool, including but not limited to account restrictions, data loss, or service disruption.
By using this tool you acknowledge that you are responsible for compliance with Anthropic's Terms of Service and Acceptable Use Policy.
License
1 maintainer

Metadata
1 maintainer
Release files for cc-tap 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| cc_tap-0.1.0.tar.gz | 1.3 MB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cc_tap-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.3 MB
Release files / cc_tap-0.1.0.tar.gz
| Download URL | cc_tap-0.1.0.tar.gz |
|---|---|
| Size | 1.3 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
1b9d929b15d3fd8f0ad00465a9787649ddb09c7aa9a9f8cc588214776b2825e4
|
|
BLAKE2b-256 checksum How to use checksums |
bd0a7a5029b6a4322e230d8eef1a9bd1c258f935574cae484ce9fc59bfd4d80a
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Apr 16, 2026.
Transparency logRelease files / cc_tap-0.1.0-py3-none-any.whl
| Download URL | cc_tap-0.1.0-py3-none-any.whl |
|---|---|
| Size | 10.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
99207f0196dbf5d626ad6301550824fa90006992c24a4ea90a49d1b9d4b502d1
|
|
BLAKE2b-256 checksum How to use checksums |
158306cb45f0d5bf0c7a7b6589de6d9dca19b717a2fe73d7392be3f145038399
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.12
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Apr 16, 2026.
Transparency logSecurity for cc-tap 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for cc_tap-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Apr 16, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.













