
Grep every Claude Code session you've ever run. The lossless Rust parser reads Claude Code's on-disk JSONL at 169 MB/s; the compiled CLI greps it and renders one line per event, 25 ms cold.



Get started
uvx cc-transcript list
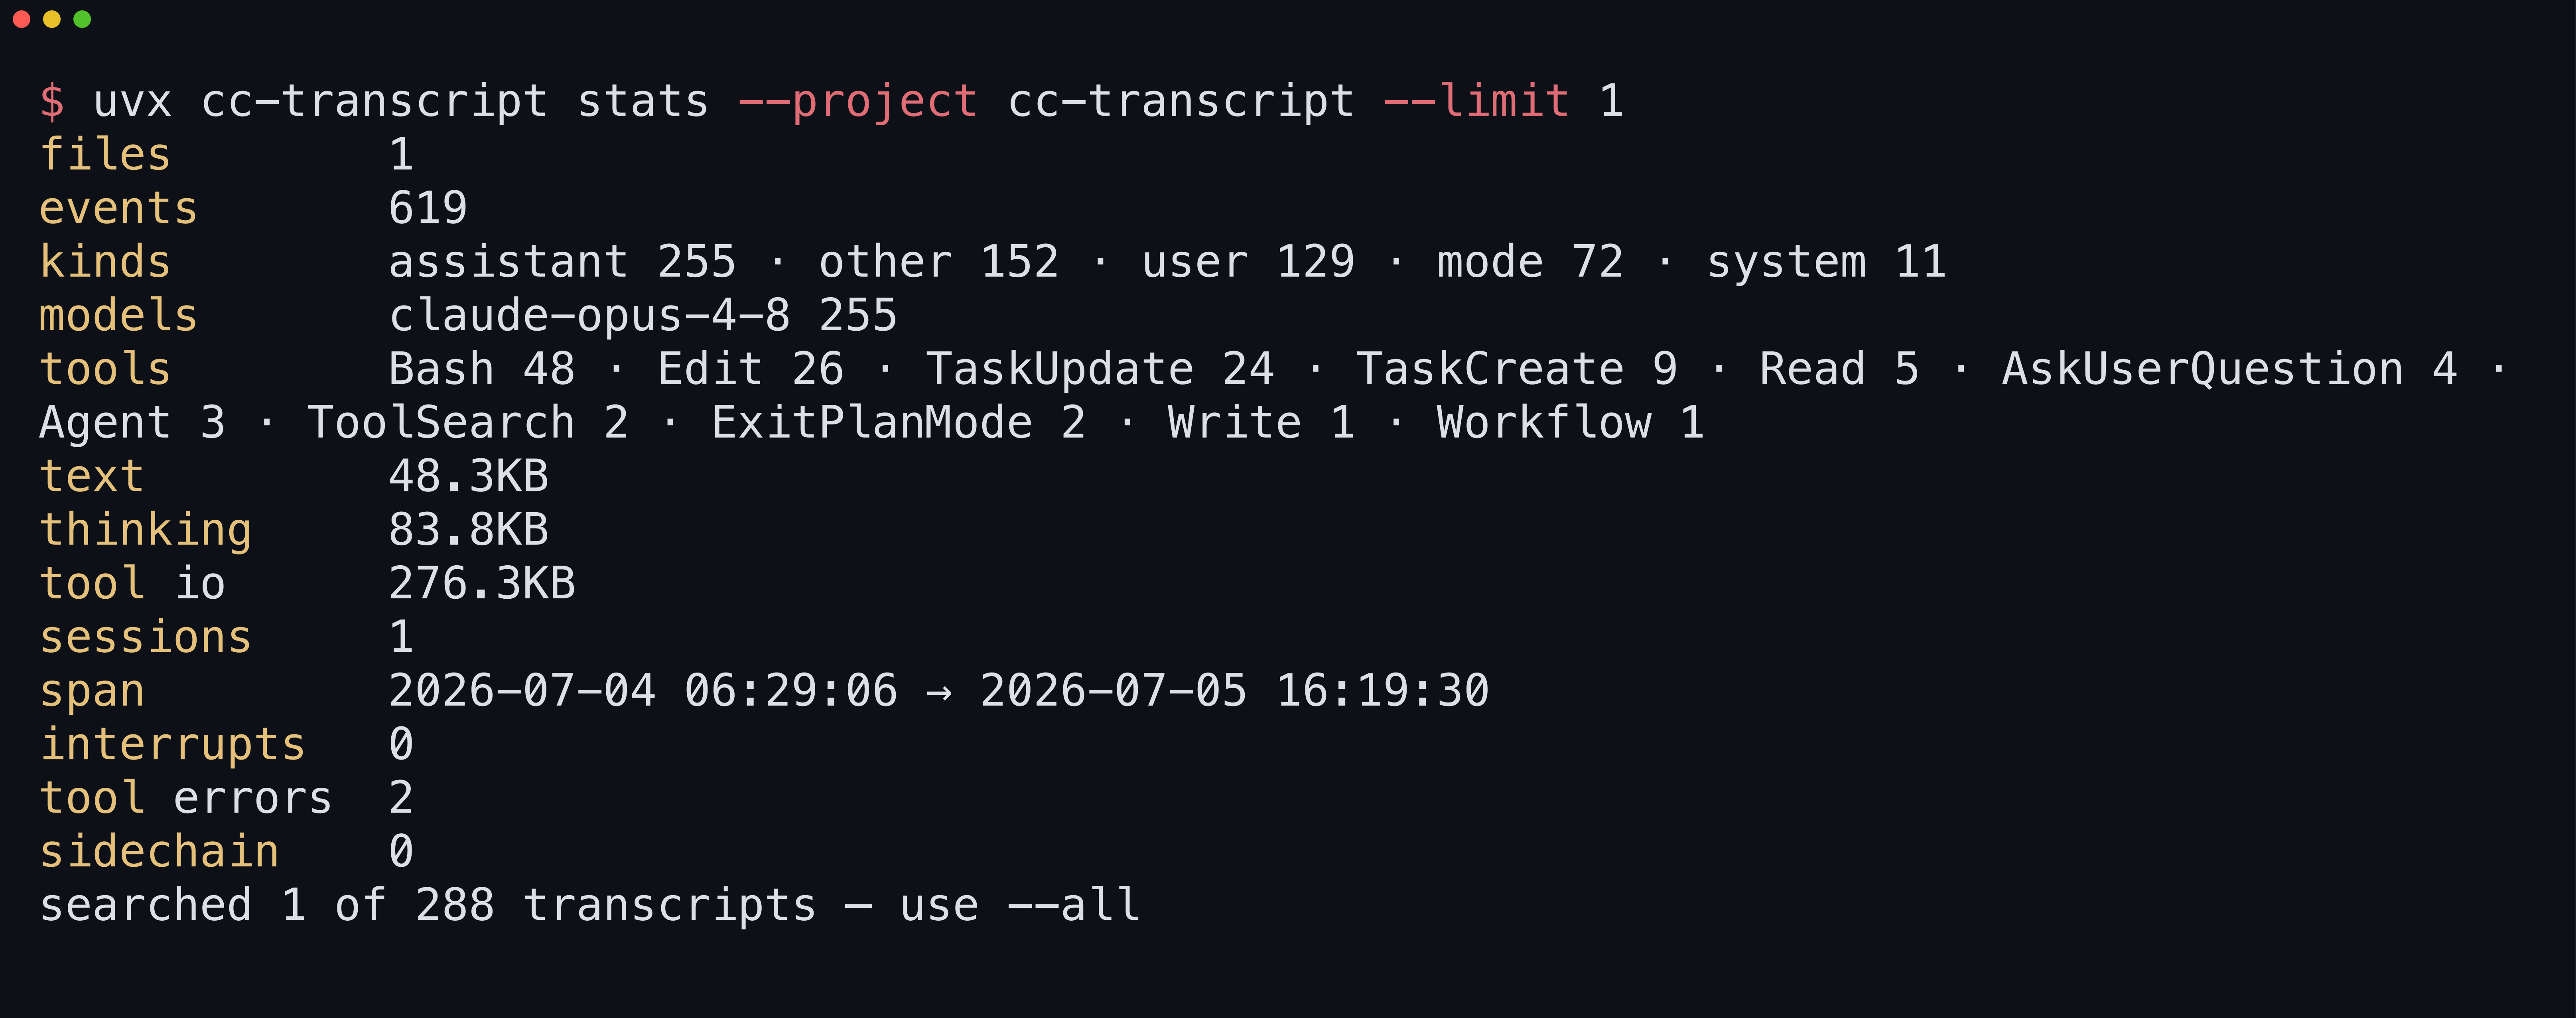
Every session is already on disk under ~/.claude/projects. list finds them newest first, and stats collapses one into a screenful:
Driving with an agent? Paste this:
/plugin marketplace add yasyf/cc-transcript
/plugin install cc-transcript@cc-transcript
The plugin's skill teaches Claude to answer "what did I ask you yesterday" from its own history, funneling through the CLI instead of reading raw JSONL.
No Claude Code? Point any agent at the CLI
Use `uvx cc-transcript` to investigate my Claude Code sessions: `list` finds
transcripts on disk, `stats` summarizes one, `grep` searches content, and `show`
renders one compact line per event. Start by listing my newest sessions and
summarizing the most recent one. Docs: https://yasyf.github.io/cc-transcript/
Use cases
Ask Claude what you asked Claude yesterday
Yesterday's session is a megabyte of JSONL, and pasting it into a chat blows the context window. Render the spine instead:
uvx cc-transcript show --signal --tail 20 ~/.claude/projects/<project>/<session>.jsonl
--signal keeps only the substantive user and assistant turns. One line per event, a few hundred tokens for the whole exchange. With the plugin installed, skip the command and ask Claude directly; its skill runs this funnel for you.
Find the session where you fixed that bug
The fix happened weeks ago, in one of a few hundred transcripts. Search them all:
uvx cc-transcript grep "TranscriptExpiredError" --project cc-transcript
Hits print under their transcript's path, each line carrying its raw event index; feed an index back into show --range to re-read the conversation around the fix. grep searches your newest 50 transcripts by default; --all takes it to every session on disk, and a no-match run exits 1 so it scripts cleanly.
Debug a token blowup from transcript evidence
A session burned through the context window and you want the culprit, not a guess. Rank the evidence:
uvx cc-transcript stats --per-file --project myapp
Each block reports text, thinking, and tool-io bytes plus per-tool call counts; the blowup stands out as an outsized tool io line. Then grep --tool <name> --with-result pins it to the exact calls.
Script it from Python
The CLI's funnel is four commands; your own tooling wants the events themselves. parse turns a path into a Transcript of typed lazy views, with the noise already dropped inside the engine:
from cc_transcript import NOISE_SPEC, discover, parse

transcript = parse(discover()[0], drop=NOISE_SPEC)
print(len(transcript.events), "events after the noise drop")
discover() lists every transcript on disk newest first, stream fans a whole corpus across the parse pool, and resolve finds one session by UUID. parse also reads OpenAI Codex CLI rollouts — hand it a path from ~/.codex/sessions and the same typed events come back. The getting-started guide builds this out to a composed filter and a sentiment score.
JSON output schema
show --json and grep --json emit JSONL, with one object per event. Each event
uses the envelope {i, kind, meta, model, text, blocks, stop_reason, usage};
fields that do not apply to its kind are omitted. Every object in blocks has
a type discriminator such as text, thinking, tool_use, tool_result,
or fallback.
More in the docs
- The Python library turns a transcript into typed lazy views, a composed filter, and a score in a dozen lines.
- Filtering events covers composable clauses, specs, and the ready-made
NOISE_SPEC. - Sentiment scoring buckets conversations and scores them around any inference engine.
- Feedback mining runs detectors, confidence calibration, and LLM verdict passes over your corpus.
- The Rust engine is the implementation — parsing, filtering, scoring, and mining — its correctness pinned by hand-owned literals and golden fixtures.
- Codex rollouts make the parser two-provider: OpenAI Codex CLI sessions lower into the same typed events, with rollout discovery, subagent joins, and per-session lifecycle and token totals.
list --provider codexfinds them from the shell. - API reference documents the complete typed surface, from
TranscriptEventtoSessionActivity.
Read the docs for the full guide. Licensed under PolyForm Noncommercial 1.0.0.
1 maintainer

Metadata
1 maintainer
Release files for cc-transcript 14.45.17
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| cc_transcript-14.45.17.tar.gz | 12.7 MB | With provenance | Details for cc_transcript-14.45.17.tar.gz |
Built distributions (wheels)
| File | Actions Reset | |||
|---|---|---|---|---|
| cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_x86_64.whl | CPython 3.13 | abi3 | Linux glibc 2.28+ x86-64 | Details for cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_x86_64.whl |
| cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_aarch64.whl | CPython 3.13 | abi3 | Linux glibc 2.28+ ARM64 | Details for cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_aarch64.whl |
| cc_transcript-14.45.17-cp313-abi3-macosx_11_0_x86_64.whl | CPython 3.13 | abi3 | macOS 11.0+ x86-64 | Details for cc_transcript-14.45.17-cp313-abi3-macosx_11_0_x86_64.whl |
| cc_transcript-14.45.17-cp313-abi3-macosx_11_0_arm64.whl | CPython 3.13 | abi3 | macOS 11.0+ ARM64 | Details for cc_transcript-14.45.17-cp313-abi3-macosx_11_0_arm64.whl |
Total release size: 136.5 MB
Release files / cc_transcript-14.45.17.tar.gz
| Download URL | cc_transcript-14.45.17.tar.gz |
|---|---|
| Size | 12.7 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
69453cf646bd2854c18a92b34f1815186e433462db1e379d2b21a08337b682c1
|
|
BLAKE2b-256 checksum How to use checksums |
d8113ff12ca5da9c4d72828af7137029655881150baa6b74c27faf6161d367b7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_x86_64.whl
| Download URL | cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_x86_64.whl |
|---|---|
| Size | 31.4 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ x86-64 abi3 |
|
SHA-256 checksum How to use checksums |
8b800982ac10c17f2877330adecef93c6c93329c66456935a2fc8da64049ace8
|
|
BLAKE2b-256 checksum How to use checksums |
7a0015759350b28df4a69a5f6cdfbfe612e818cd4c6d9d7be590143a84c2e0e8
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_aarch64.whl
| Download URL | cc_transcript-14.45.17-cp313-abi3-manylinux_2_28_aarch64.whl |
|---|---|
| Size | 30.7 MB |
| Tags | CPython 3.13 Linux glibc 2.28+ ARM64 abi3 |
|
SHA-256 checksum How to use checksums |
3353e4662dae7516737d895ace426f4352515f7b2298e06a56fb27955ac8454c
|
|
BLAKE2b-256 checksum How to use checksums |
58273da89a442a916958a6b0b9209505513fe9481c63d5a0974475fe20cff273
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / cc_transcript-14.45.17-cp313-abi3-macosx_11_0_x86_64.whl
| Download URL | cc_transcript-14.45.17-cp313-abi3-macosx_11_0_x86_64.whl |
|---|---|
| Size | 31.1 MB |
| Tags | CPython 3.13 abi3 macOS 11.0+ x86-64 |
|
SHA-256 checksum How to use checksums |
c9e67c0738cef9e545556feddfd9319e14bc1ca6eb2cfdc17ebdca671c814465
|
|
BLAKE2b-256 checksum How to use checksums |
12f5bc6ef7627335ccc3297203426ed8753d6f7cceac76dfa6e1cb3101198437
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logRelease files / cc_transcript-14.45.17-cp313-abi3-macosx_11_0_arm64.whl
| Download URL | cc_transcript-14.45.17-cp313-abi3-macosx_11_0_arm64.whl |
|---|---|
| Size | 30.5 MB |
| Tags | CPython 3.13 abi3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
f39f197f148d9e323f77aad98070846ef38b27b53b1edf6acc68a92ad47339e6
|
|
BLAKE2b-256 checksum How to use checksums |
cf1d389707220a2118730efc3c6cdec98960b22d6ee5e2a28af1a2eb2772a29b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logSecurity for cc-transcript 14.45.17
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 5 files in this release have been uploaded with provenance metadata.
Attestation for cc_transcript-14.45.17.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 30, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














