
This project has been archived by its maintainers, and is no longer receiving any updates.
CDP-Patches v1.1




Install it from PyPI
pip install cdp-patches
Or for Full Linting
(Includes: playwright, botright, selenium, selenium_driverless)
pip install cdp-patches[automation_linting]
Leak Patches
Input Package
Concept: Input Domain Leaks
Bypass CDP Leaks in Input domains
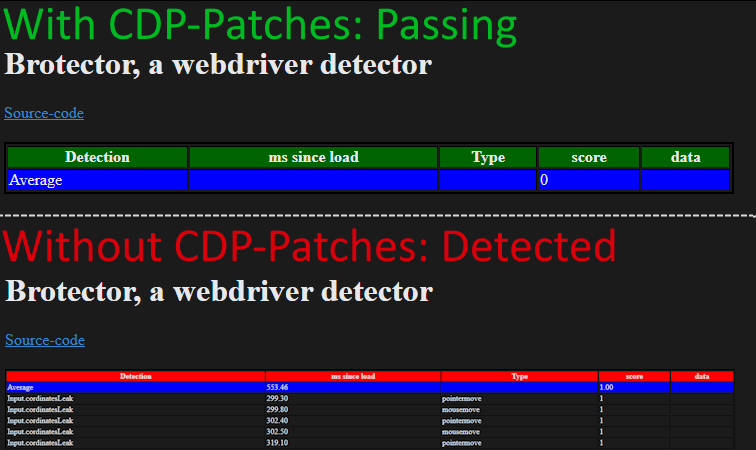
For an interaction event e, the page coordinates won't ever equal the screen coordinates, unless Chrome is in fullscreen.
However, all CDP input commands just set it the same by default (see crbug#1477537).
var is_bot = (e.pageY == e.screenY && e.pageX == e.screenX)
if (is_bot && 1 >= outerHeight - innerHeight){ // fullscreen
    is_bot = false
}
Furthermore, CDP can't dispatch CoalescedEvent's (demo).
As we don't want to patch Chromium itsself, let's just dispatch this event at OS-level!
Usage
from cdp_patches.input import SyncInput

sync_input = SyncInput(pid=pid)
# Or
sync_input = SyncInput(browser=browser)

# Dispatch Inputs
sync_input.click("left", 100, 100)  # Left click at (100, 100)
sync_input.double_click("left", 100, 100)  # Left double-click at (100, 100)
sync_input.down("left", 100, 100)  # Left mouse button down at (100, 100)
sync_input.up("left", 100, 100)  # Left mouse button up at (100, 100)
sync_input.move(100, 100)  # Move mouse to (100, 100)
sync_input.scroll("down", 10)  # Scroll down by 10 lines
sync_input.type("Hello World!")  # Type "Hello World!"
Async Usage
import asyncio

from cdp_patches.input import AsyncInput

async def main():
    async_input = await AsyncInput(pid=pid)
    # Or
    async_input = await AsyncInput(browser=browser)

    # Dispatch Inputs
    await async_input.click("left", 100, 100)  # Left click at (100, 100)
    await async_input.double_click("left", 100, 100)  # Left double-click at (100, 100)
    await async_input.down("left", 100, 100)  # Left mouse button down at (100, 100)
    await async_input.up("left", 100, 100)  # Left mouse button up at (100, 100)
    await async_input.move(100, 100)  # Move mouse to (100, 100)
    await async_input.scroll("down", 10)  # Scroll down by 10 lines
    await async_input.type("Hello World!")  # Type "Hello World!"

if __name__ == '__main__':
    asyncio.run(main())
TODO
- Improve mouse movement timings.
- Implement extensive testing.
Owner: Vinyzu
Co-Maintainer: Kaliiiiiiiiii
Read the Documentation
Development
Read the CONTRIBUTING.md file.
Copyright and License
© Vinyzu
(Commercial Usage is allowed, but source, license and copyright has to made available. Botright does not provide and Liability or Warranty)
Authors
2 maintainers


Metadata
2 maintainers
Release files for cdp-patches 1.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| cdp_patches-1.1.tar.gz | 28.5 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cdp_patches-1.1-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 51.1 kB
Release files / cdp_patches-1.1.tar.gz
| Download URL | cdp_patches-1.1.tar.gz |
|---|---|
| Size | 28.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
bc7025e7f92e4301231b6bbc231459f91260aa252ef35dedb57725e2fa9f95d0
|
|
BLAKE2b-256 checksum How to use checksums |
ade1efec51a335f988b3b0bb1d3363b03b31b572a05d1cc55d4b021b2af309a2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.11.13
|
Release files / cdp_patches-1.1-py3-none-any.whl
| Download URL | cdp_patches-1.1-py3-none-any.whl |
|---|---|
| Size | 22.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
9c7df908b2cce9ca3cc4d66d592c632538f12712f6ef4834d830046da7065e94
|
|
BLAKE2b-256 checksum How to use checksums |
eeb05e8d56be8ceaa7f31a013932c5610e73f8689e6da8398d21528029d846c7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/6.2.0 CPython/3.11.13
|
Security for cdp-patches 1.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














