
Celery Logger
celery-logger is a python library for logging celery events such as tasks received, tasks failed/succeeded and tasks retried, along with task args.
Features
- Simple and flexible task logs
- Multiple deployment options (docker, virtual machines)
- Integration possibilities: ELK stack and AWS cloudwatch for example
How does it work?
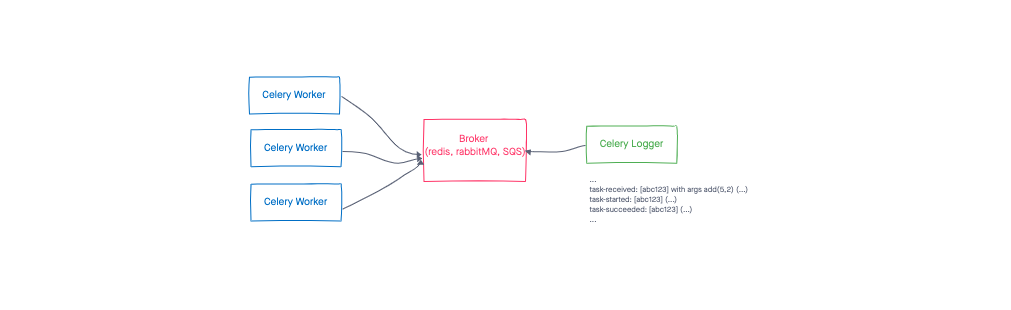
Celery-logger connects with your message broker (such as redis, rabbitMQ or SQS) and logs the tasks on a file or stdout.
This way you can easily have multiple celery workers and see your logs in a single place.
Sample project
We provided a sample project for playing around and seeing how it works.
Getting started:
# navigate to the sample-project folder
$ cd sample-project
# Build and start the containers:
$ docker-compose up
Querying logs
Make sure you are in the sample-project folder
Calling a few tasks
$ docker-compose exec celeryd python call_tasks.py

Tasks have been called!
Run `docker-compose logs -f celery-logger` to see the logger in action.
Taking a look in all events
$ docker-compose logs celery-logger
Searching for failed tasks:
$ docker-compose logs celery-logger | grep task-failed
Searching for a specific task:
$ docker-compose logs celery-logger | grep "app.add"
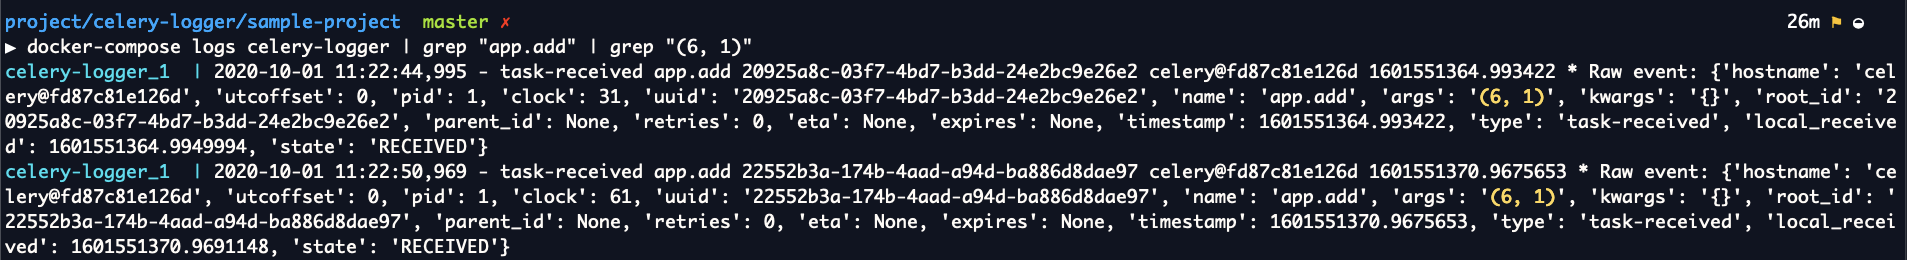
Searching for a specific task and args:
$ docker-compose logs celery-logger | grep "app.add" | grep "(6, 1)"
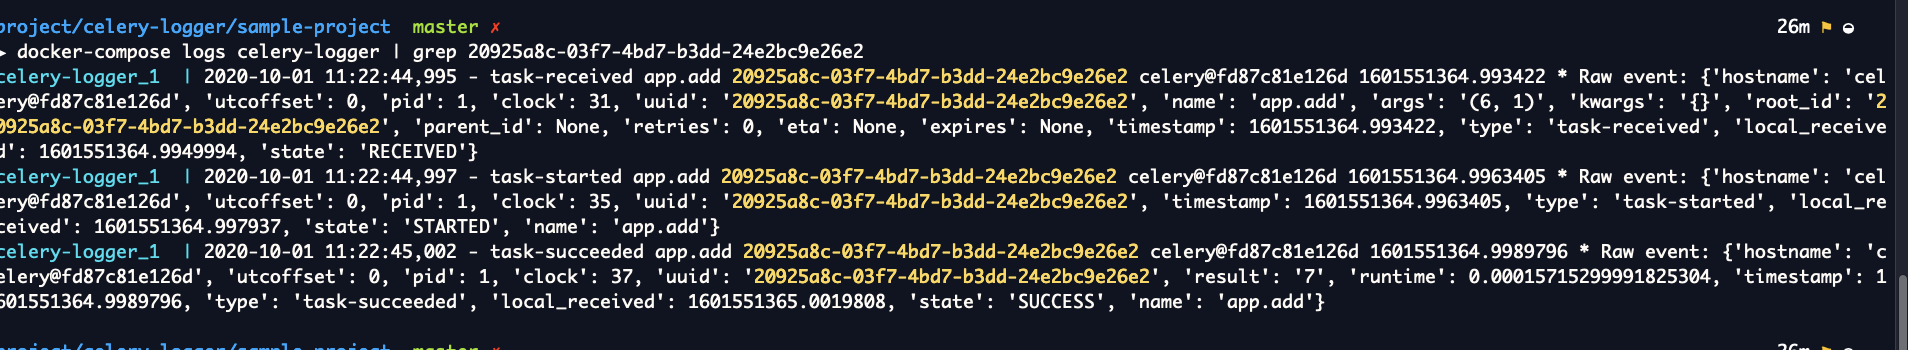
Searching for a task id
$ docker-compose logs celery-logger | grep 20925a8c-03f7-4bd7-b3dd-24e2bc9e26e2
Installation
Use the package manager pip to install celery-logger.
pip install celerylogger
Usage
The executable will be available in the path as celery-logger:
# Display the help text
$ celery-logger -h
# Start logging from a redis broker
$ celery-logger --celery-broker redis://redis:6379/0
Authors
- Sergio Oliveira - Initial work - Seocam
- Thiago Ferreira - Improvements, documentation and current maintainer - thiagoferreiraw
- André Girol - Packaging and distribution - Girol
1 maintainer

Metadata
1 maintainer
Release files for celery-logger 0.0.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| celery-logger-0.0.3.tar.gz | 4.7 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| celery_logger-0.0.3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 9.7 kB
Release files / celery-logger-0.0.3.tar.gz
| Download URL | celery-logger-0.0.3.tar.gz |
|---|---|
| Size | 4.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
dd6468438cb668552ba381d1e5742919b387b2417591a9223bf41b00a3a39fee
|
|
BLAKE2b-256 checksum How to use checksums |
00b22e98fcac338623d9973306f692c34825affbe1a0151a3f3acdfa04bb61e7
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.2.0 pkginfo/1.5.0.1 requests/2.24.0 setuptools/57.1.0 requests-toolbelt/0.9.1 tqdm/4.50.0 CPython/3.9.1
|
Release files / celery_logger-0.0.3-py3-none-any.whl
| Download URL | celery_logger-0.0.3-py3-none-any.whl |
|---|---|
| Size | 5.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
92ef506e6ffd274d3393be3b8a1c9090842a6487b04a77f5f4987844ab44ba1d
|
|
BLAKE2b-256 checksum How to use checksums |
8357d5fd3250d2750c3bc87b17e96fe461697b16007851032d04ac2534c76e59
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.2.0 pkginfo/1.5.0.1 requests/2.24.0 setuptools/57.1.0 requests-toolbelt/0.9.1 tqdm/4.50.0 CPython/3.9.1
|
Security for celery-logger 0.0.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














