
cf-tool


Codeforces from your terminal: get a contest, test your code on the samples, submit, and watch the verdict. No setup first.
Install
uv tool install cf-tool-cli # or: pipx install cf-tool-cli
You need Python 3.10+, a compiler or interpreter for your language, and Google Chrome to log in (it works in the background).
A contest, start to finish
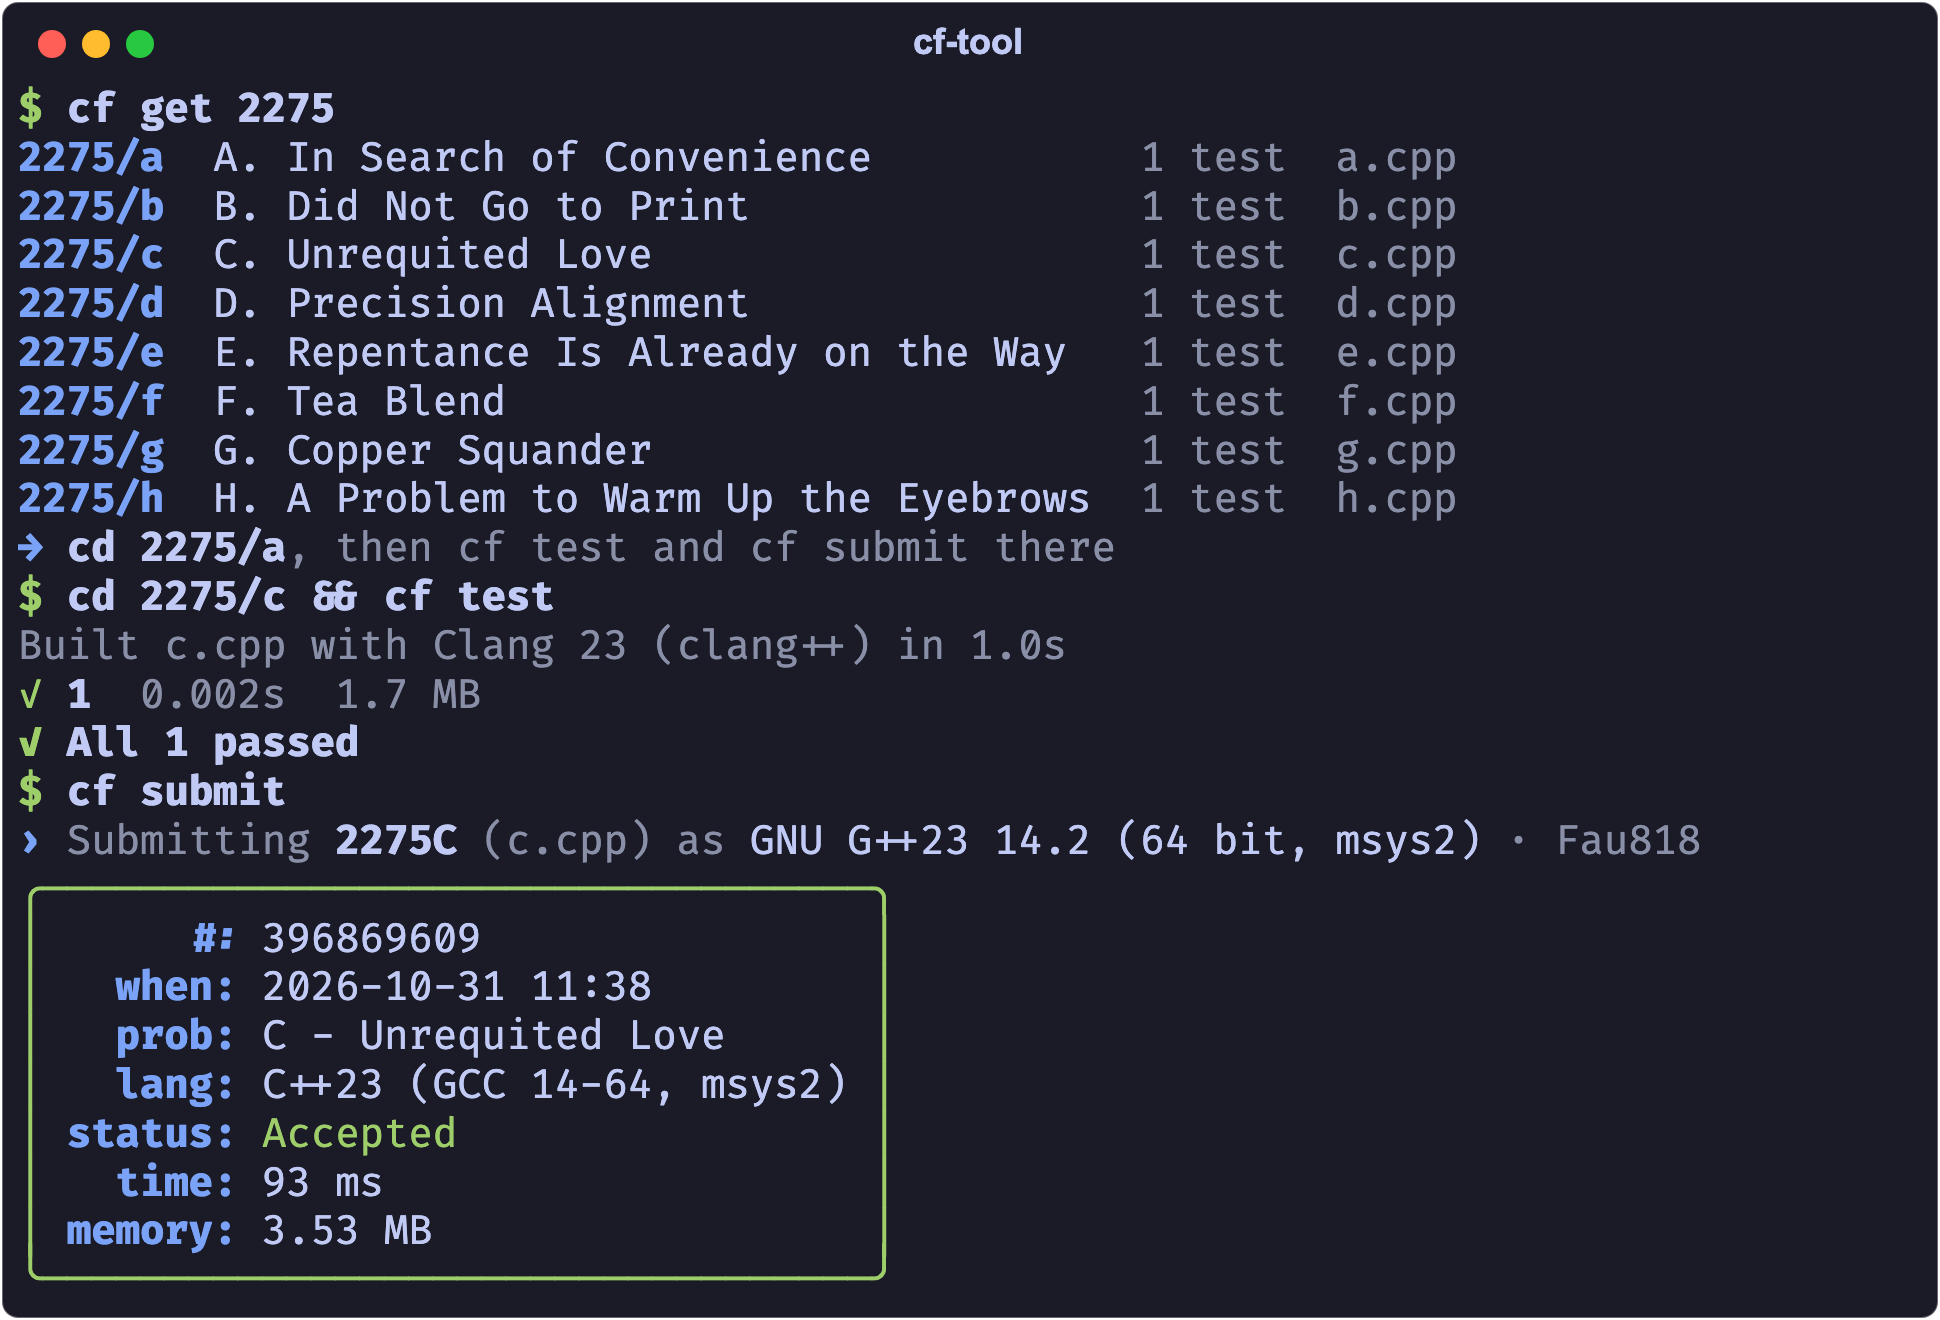
cf get 2050 makes a folder per problem: the statement, the samples and your starter
code. The first time, cf asks which language you write in.
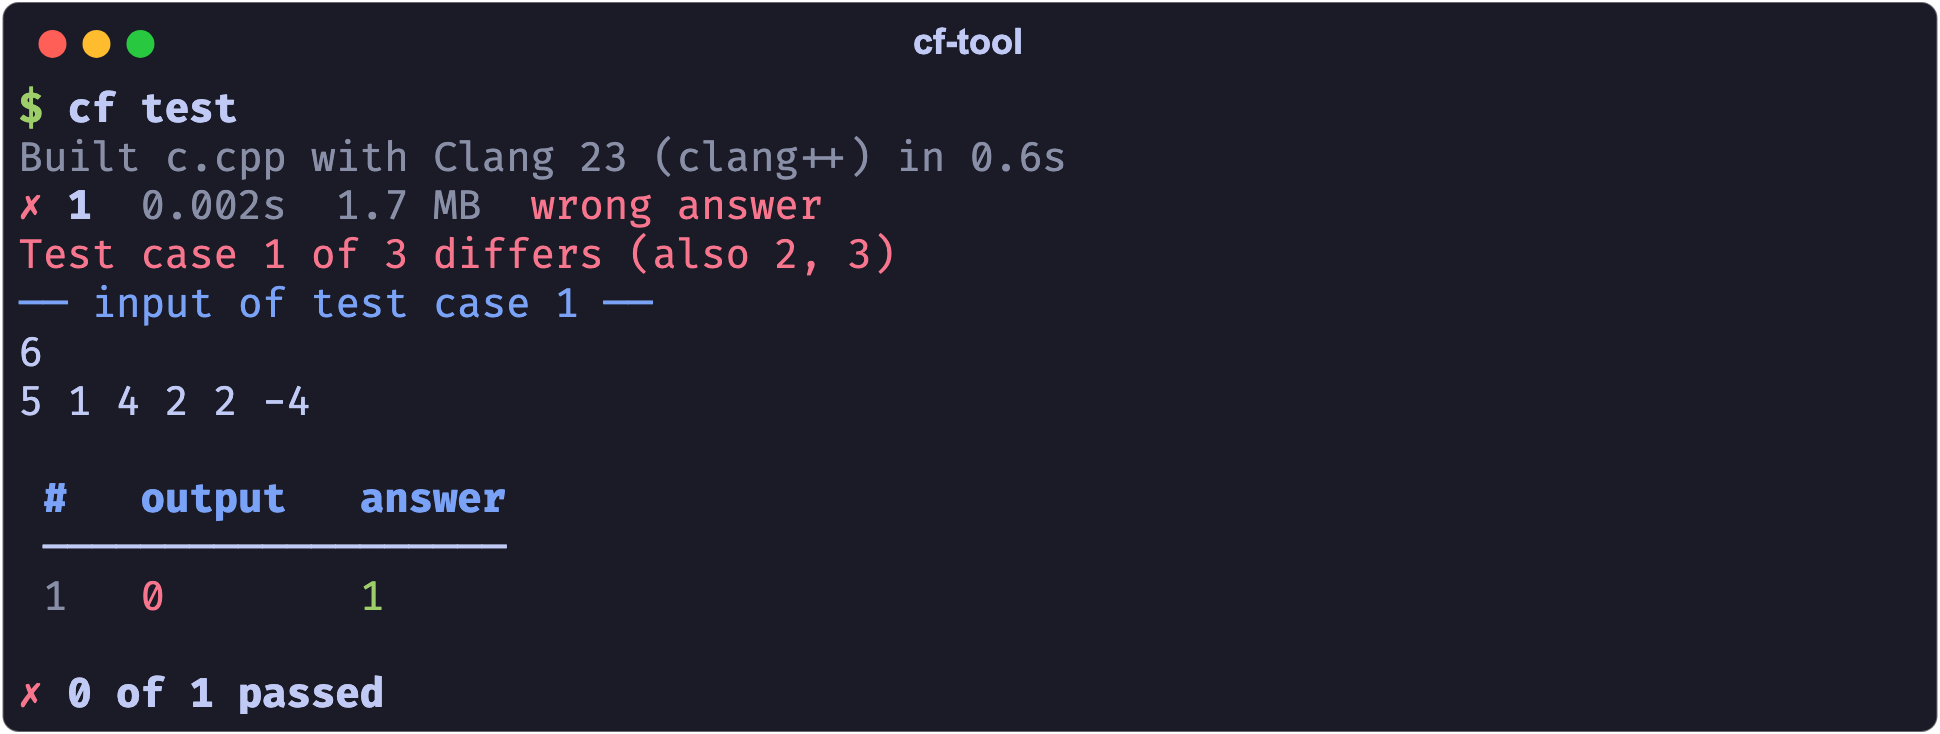
cf test builds your code and runs it on the samples. A wrong answer shows the input
and where your output parts from the answer, down to the test case:
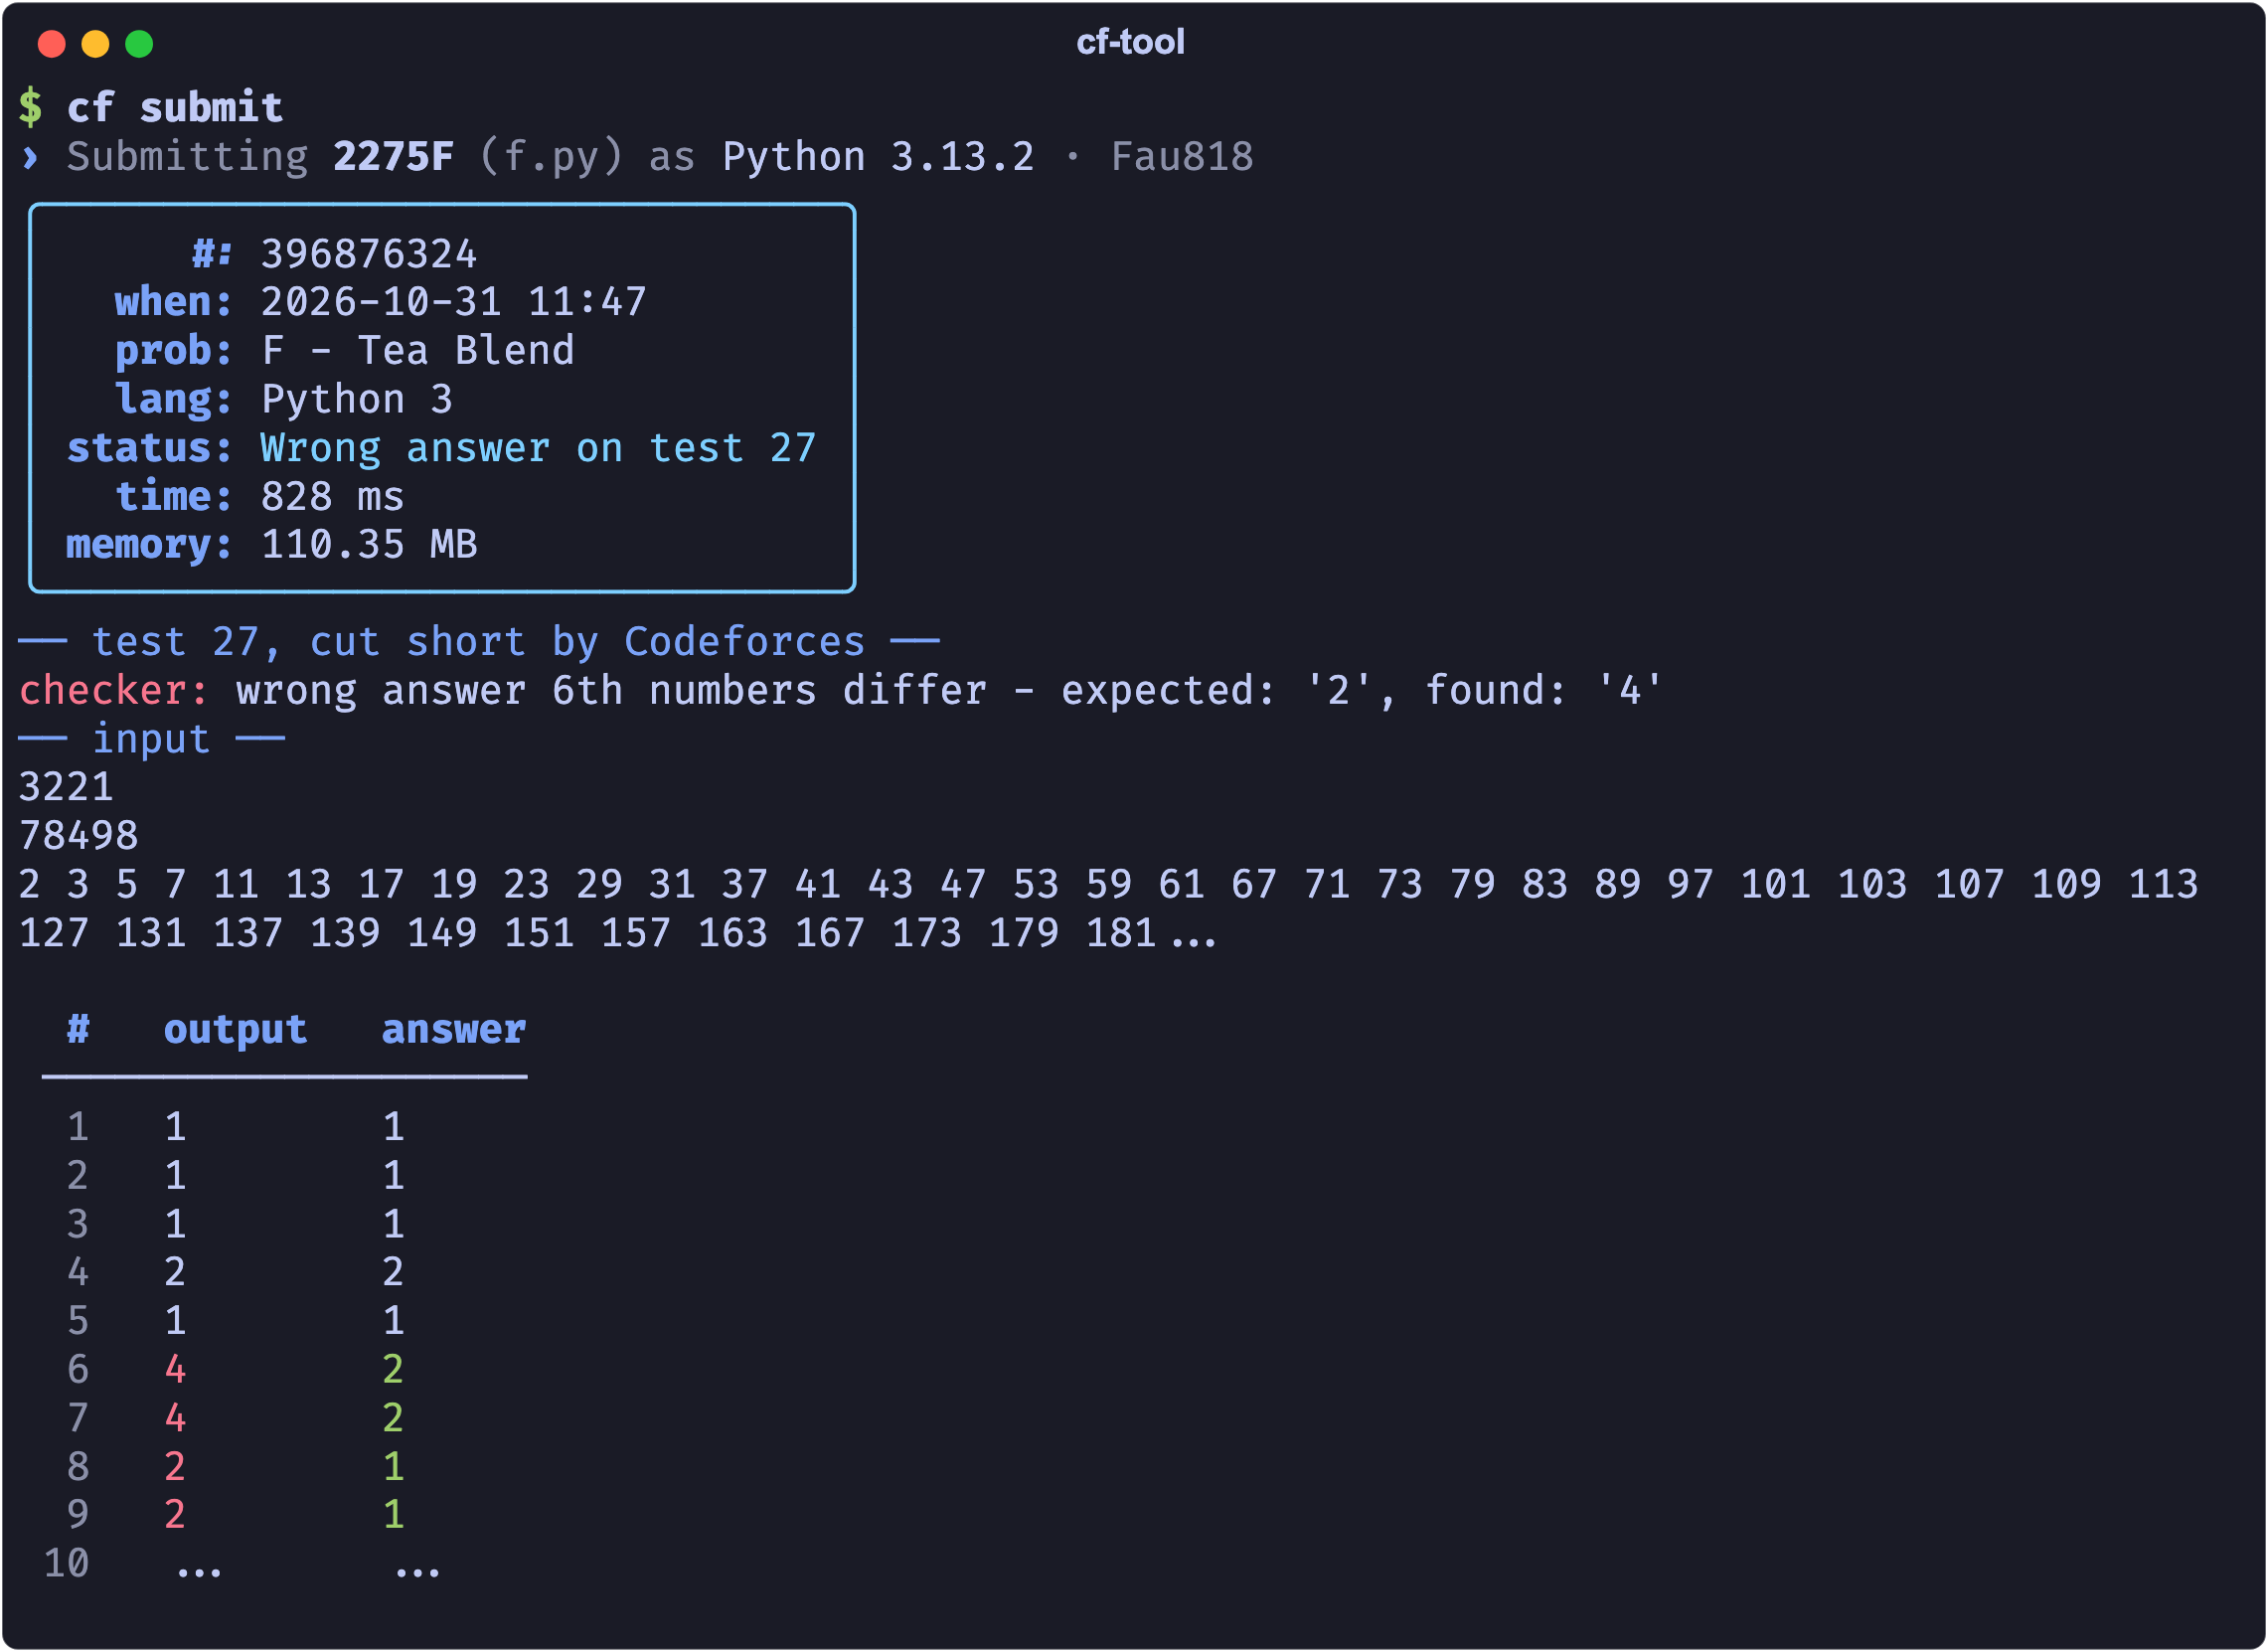
cf submit sends it and shows the verdict as it comes. Once the contest is over, a
failed test comes with it, as Codeforces keeps it, and is saved for cf test:
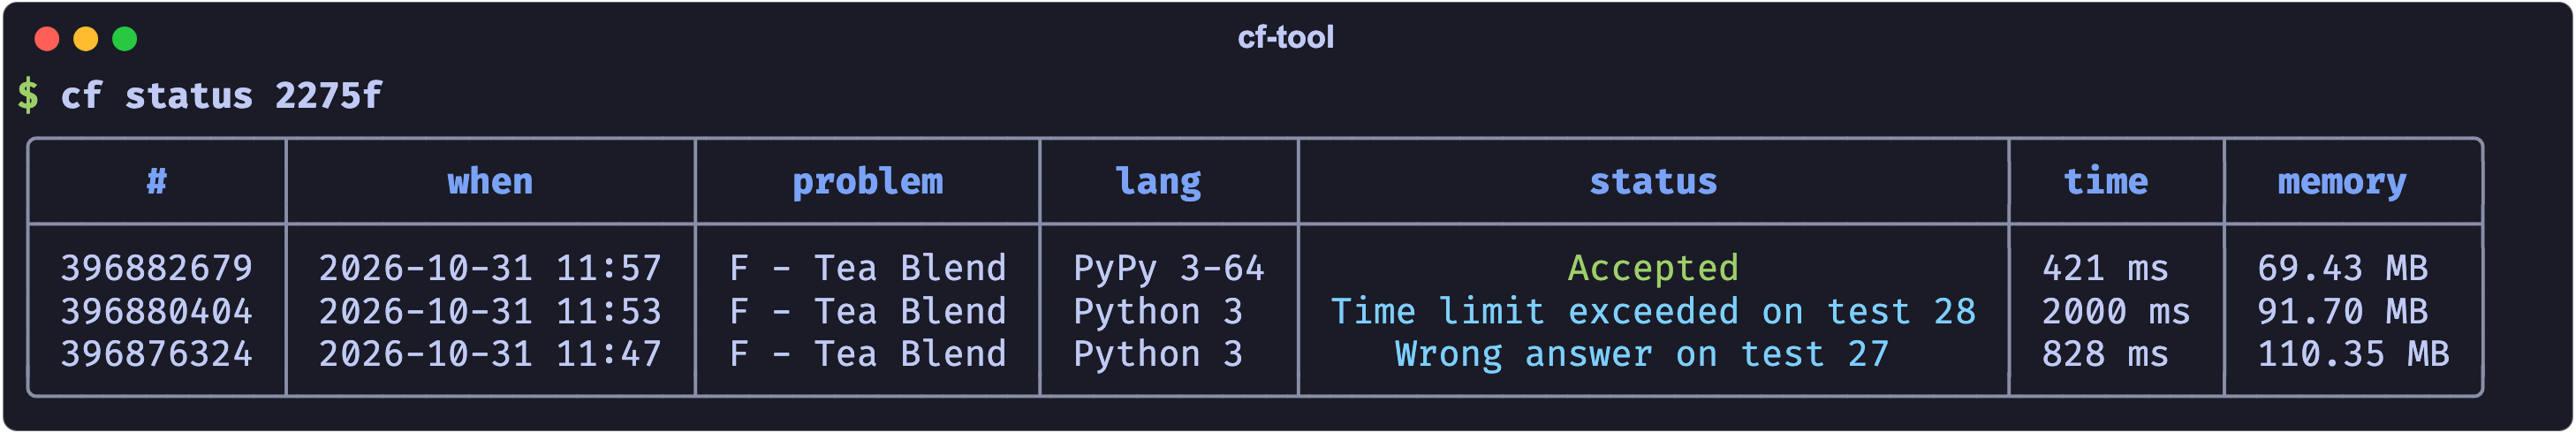
cf status lists your submissions, refreshed until they're judged:
Commands
| Command | What it does |
|---|---|
cf get 2050 / cf get 2050b |
folders, samples and starter code for a contest or a problem |
cf test [problem] [test...] |
build your code and run it on the problem's tests (-w: on every save) |
cf submit [problem] [file] |
submit, then watch the verdict |
cf status [submission] |
your submissions, or one with the test it failed |
cf stress |
random tests until your code and a brute force disagree |
cf race 2050 |
count down to the start, then get the problems |
cf open / cf problems / cf contests |
the problem in the browser, a contest's problems, upcoming contests |
cf pick -r 1600 -t dp |
a random problem you haven't solved |
cf new / cf listen |
a code file from your starter code; problems from Competitive Companion |
cf pull / cf clone |
download the code of your (or anyone's) submissions |
cf login / cf config / cf doctor |
log in; settings from menus; check the setup |
More in the guide: your own tests, checkers, interactive problems, settings, CP Editor, Tab completion, coming from cf-tool 0.3.
License
MIT. cf-tool began as a port of xalanq/cf-tool.
1 maintainer

Metadata
1 maintainer
Release files for cf-tool-cli 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| cf_tool_cli-1.0.0.tar.gz | 162.6 kB | With provenance | Details for cf_tool_cli-1.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| cf_tool_cli-1.0.0-py3-none-any.whl | Python 3 | none | any | Details for cf_tool_cli-1.0.0-py3-none-any.whl |
Total release size: 286.2 kB
Release files / cf_tool_cli-1.0.0.tar.gz
| Download URL | cf_tool_cli-1.0.0.tar.gz |
|---|---|
| Size | 162.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
f05a0dfb60e5927e11c5e5b07e445c33952b252aed0207429d5506a0d39e682f
|
|
BLAKE2b-256 checksum How to use checksums |
907e39f6f9a4a7fb6259d97e4c23d1129c4dd31d2acd3007de86d82484a72f7b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 31, 2026.
Transparency logRelease files / cf_tool_cli-1.0.0-py3-none-any.whl
| Download URL | cf_tool_cli-1.0.0-py3-none-any.whl |
|---|---|
| Size | 123.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
fd86a7622cabd780746d86947a17bae74b0d62468bb2aaf17bcbab4f91cd4414
|
|
BLAKE2b-256 checksum How to use checksums |
73cf5ef889bf3344333c1d20856217347487e4414cb8c531fcfd086004d93801
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 31, 2026.
Transparency logSecurity for cf-tool-cli 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for cf_tool_cli-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 31, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













