
Cheqlist. A simple Qt checklist.
- Info:
This is the README file for Cheqlist.
- Author:
Chris Warrick <chris@chriswarrick.com>
- Copyright:
© 2015-2019, Chris Warrick.
- Date:
2019-12-01
- Version:
0.3.2
PURPOSE
This is a simple checklist application, written in Qt and Python. Both PySide2 and PyQt5 are supported, but PySide2 is preferred.
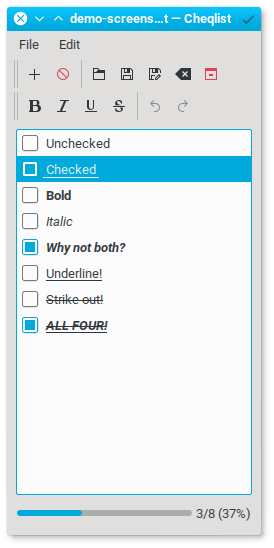
SCREENSHOT
INSTALLATION
pip install cheqlist pyside2
An AUR package also available.
If you are on Linux, run:
sudo update-mime-database /usr/share/mime
FILE FORMAT
GitHub Flavored Markdown is the usual file format:
- [ ] unchecked
- [x] checked
However, the parser is quite liberal when it comes to reading files. It also supports Markdown-style formatting for **bold**, *italic*, <u>underline</u>, ~~strikeout~~.
READ MORE
See the Cheqlist User’s Guide for more details.
COPYRIGHT
Copyright © 2015-2019, Chris Warrick. All rights reserved.
Redistribution and use in source and binary forms, with or without modification, are permitted provided that the following conditions are met:
Redistributions of source code must retain the above copyright notice, this list of conditions, and the following disclaimer.
Redistributions in binary form must reproduce the above copyright notice, this list of conditions, and the following disclaimer in the documentation and/or other materials provided with the distribution.
Neither the name of the author of this software nor the names of contributors to this software may be used to endorse or promote products derived from this software without specific prior written consent.
THIS SOFTWARE IS PROVIDED BY THE COPYRIGHT HOLDERS AND CONTRIBUTORS “AS IS” AND ANY EXPRESS OR IMPLIED WARRANTIES, INCLUDING, BUT NOT LIMITED TO, THE IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS FOR A PARTICULAR PURPOSE ARE DISCLAIMED. IN NO EVENT SHALL THE COPYRIGHT OWNER OR CONTRIBUTORS BE LIABLE FOR ANY DIRECT, INDIRECT, INCIDENTAL, SPECIAL, EXEMPLARY, OR CONSEQUENTIAL DAMAGES (INCLUDING, BUT NOT LIMITED TO, PROCUREMENT OF SUBSTITUTE GOODS OR SERVICES; LOSS OF USE, DATA, OR PROFITS; OR BUSINESS INTERRUPTION) HOWEVER CAUSED AND ON ANY THEORY OF LIABILITY, WHETHER IN CONTRACT, STRICT LIABILITY, OR TORT (INCLUDING NEGLIGENCE OR OTHERWISE) ARISING IN ANY WAY OUT OF THE USE OF THIS SOFTWARE, EVEN IF ADVISED OF THE POSSIBILITY OF SUCH DAMAGE.
1 maintainer

Metadata
1 maintainer
Release files for cheqlist 0.3.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| cheqlist-0.3.2.tar.gz | 29.4 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cheqlist-0.3.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 52.7 kB
Release files / cheqlist-0.3.2.tar.gz
| Download URL | cheqlist-0.3.2.tar.gz |
|---|---|
| Size | 29.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a6ff10e3a6e9eda5c32599298948315c1f80402d9fa166b406afbf0ea9c33d9e
|
|
BLAKE2b-256 checksum How to use checksums |
4340d8b41cb78447fee23ab3873cb3582dce77abb2df2cc078d840f9f6e0e925
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.11.0 pkginfo/1.4.2 requests/2.22.0 setuptools/40.8.0 requests-toolbelt/0.8.0 tqdm/4.23.4 CPython/3.7.5
|
Release files / cheqlist-0.3.2-py3-none-any.whl
| Download URL | cheqlist-0.3.2-py3-none-any.whl |
|---|---|
| Size | 23.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
e7a81ad1eb09eced0ca15530c4805a579f0d6e73e77dc02faf697fe715963258
|
|
BLAKE2b-256 checksum How to use checksums |
b1193abe52412eb44c932b922c08818b523311a8085f517e56c2a242c9544b81
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/1.11.0 pkginfo/1.4.2 requests/2.22.0 setuptools/40.8.0 requests-toolbelt/0.8.0 tqdm/4.23.4 CPython/3.7.5
|
Security for cheqlist 0.3.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














