
Structured logs for the HTTP client


English | Русский
The with_structlogger option for the HTTP client
logs all requests and responses through structlog.
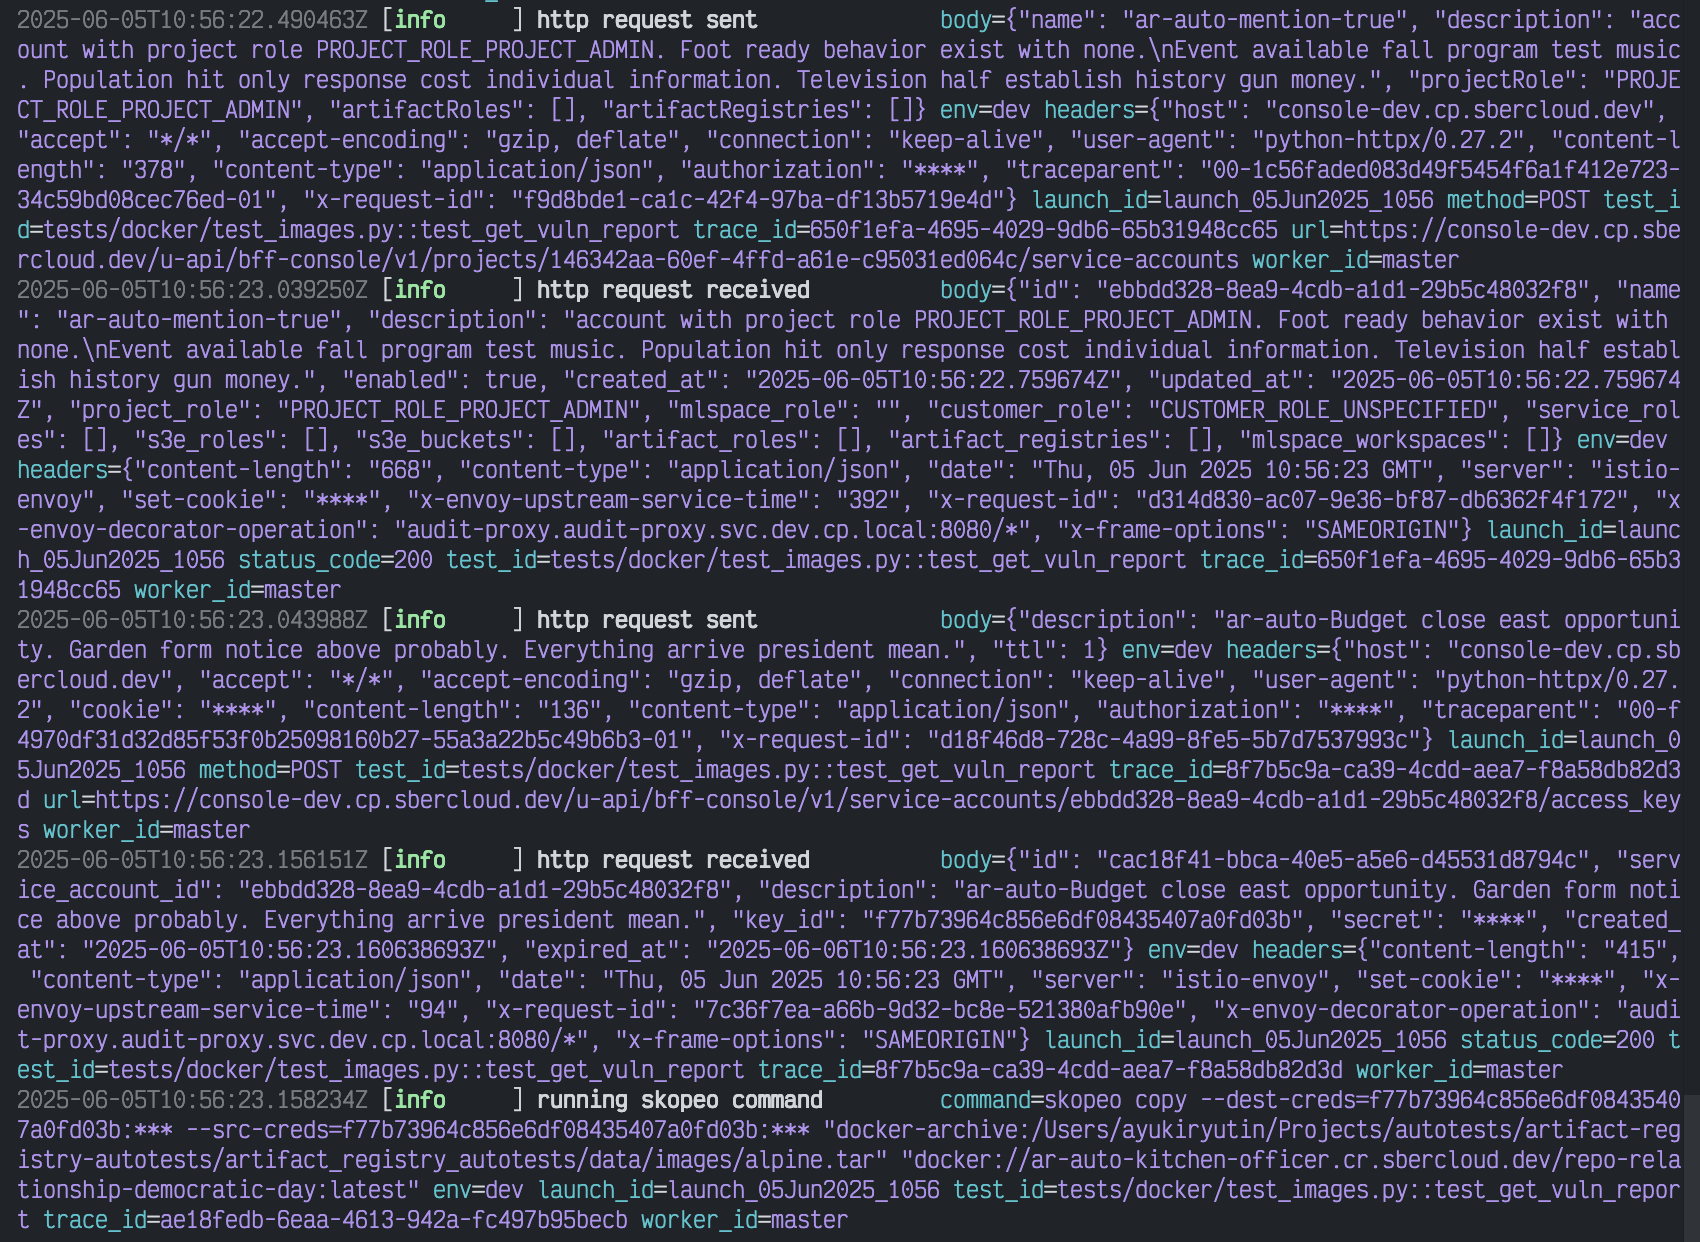
The standard http-client logger puts the request in one text string. This option logs the method, URL, headers, body, and other data as separate fields, visible in the console during debugging and available for searching and filtering in collected logs.
Installation
Requires Python 3.13 or later.
pip install cloudru-qa-http-client-structlog
Import the library as http_client_structlog. A compatible version of
cloudru-qa-http-client
is installed with it.
Skills for AI agents
The package includes the http-client-structlog-usage skill
with examples and usage rules for AI agents. Install the library
in your project environment, then run this from its root (requires uv):
uvx library-skills install --skill http-client-structlog-usage --yes
For Claude Code, add --claude. The instructions are shipped with the library version.
Usage
Pass the option to the client constructor; logging is then automatic:
import structlog

from http_client import HttpClient
from http_client_structlog import with_structlogger


class OrdersClient(HttpClient):
    def get_order(self, order_id: str):
        request = self.client.build_request("GET", f"/orders/{order_id}")
        return self.send(request)


with OrdersClient("https://api.example.com", with_structlogger(structlog.get_logger("orders"))) as client:
    client.get_order("42")
The request is logged as an http request sent event, the response as http response received.
A shared trace_id field links them.
Structured logs for automated tests can look like this:
Asynchronous client
Use the same option without extra configuration:
from http_client import AsyncHttpClient


class AsyncOrdersClient(AsyncHttpClient):
    async def get_order(self, order_id: str):
        request = self.client.build_request("GET", f"/orders/{order_id}")
        return await self.send(request)


async with AsyncOrdersClient("https://api.example.com", with_structlogger(logger)) as client:
    await client.get_order("42")
Masking secrets
Fields with common secret names — authorization, cookie, token, password, api_key, and others
from http_client.event_hooks.DEFAULT_SANITIZE_KEYS — are masked by default at every depth,
including nested objects and array items.
Add your own fields with sanitize_keys. These are exact paths in
glom format, applied to headers, query parameters,
and the JSON body. They extend the default list rather than replacing it:
with_structlogger(
    logger,
    sanitize_keys=["user.password", "items.*.token"],
)
Write header names in lowercase: "authorization", not "Authorization".
Disable the default list explicitly with use_default_sanitize_keys=False.
Parameters
| Parameter | Type | Purpose |
|---|---|---|
logger |
structlog.stdlib.BoundLogger |
where to write |
sanitize_keys |
Sequence[str] | None |
glom paths to fields replaced with **** |
json_indent |
int | None |
indentation width for JSON properties |
log_level |
int | None |
record level; INFO by default |
use_default_sanitize_keys |
bool |
mask common secrets at every depth; True by default |
Set the level and indentation for the whole project with http_client.configure_logging(...)
or HTTP_CLIENT_* environment variables. Values passed to with_structlogger override shared settings.
Development
The library is developed in the qa-libraries monorepo
alongside the other cloudru-qa-* libraries. You need uv, GNU Make,
and checkmake.
Run commands from the repository root:
make sync                              # install dependencies for all libraries from uv.lock
make test-http-client-structlog        # tests for this library
make typecheck-http-client-structlog   # mypy for this library
make check                             # formatting, ruff, mypy, and tests for the entire workspace
Tests run on Python 3.13 and 3.14. Create a separate environment for another version:
make sync test-http-client-structlog PYTHON_VERSION=3.14.
Publish a release with the git tag http-client-structlog/v<version>. The tag version must match
the version in packages/http-client-structlog/pyproject.toml.
1 maintainer

Metadata
1 maintainer
Release files for cloudru-qa-http-client-structlog 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| cloudru_qa_http_client_structlog-1.0.0.tar.gz | 22.3 kB | With provenance | Details for cloudru_qa_http_client_structlog-1.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| cloudru_qa_http_client_structlog-1.0.0-py3-none-any.whl | Python 3 | none | any | Details for cloudru_qa_http_client_structlog-1.0.0-py3-none-any.whl |
Total release size: 44.0 kB
Release files / cloudru_qa_http_client_structlog-1.0.0.tar.gz
| Download URL | cloudru_qa_http_client_structlog-1.0.0.tar.gz |
|---|---|
| Size | 22.3 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
ae54c99742eba8a80806e4099e43ff9c2f9ab821316f0fc2bb9f692b75c88e4b
|
|
BLAKE2b-256 checksum How to use checksums |
256c64958a7bbb66d312dcd89e29805f4edcb5803f2c17d3326db52507e46bea
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logRelease files / cloudru_qa_http_client_structlog-1.0.0-py3-none-any.whl
| Download URL | cloudru_qa_http_client_structlog-1.0.0-py3-none-any.whl |
|---|---|
| Size | 21.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
899d06c7c3d854af814d9b92e94084dd09ae82f7685088d088728a61af5ae5f8
|
|
BLAKE2b-256 checksum How to use checksums |
45a72ae331b0a10c2baa9de46846c4f70b9d7bc025f2809296b452adf346eead
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logSecurity for cloudru-qa-http-client-structlog 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for cloudru_qa_http_client_structlog-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 14, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













