
cm-rgb
Control your Wraith Prism RGB on Linux, Mac OS and Windows
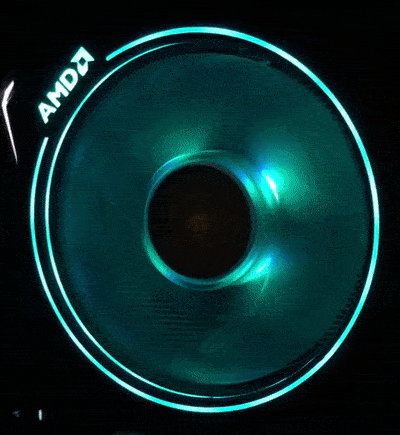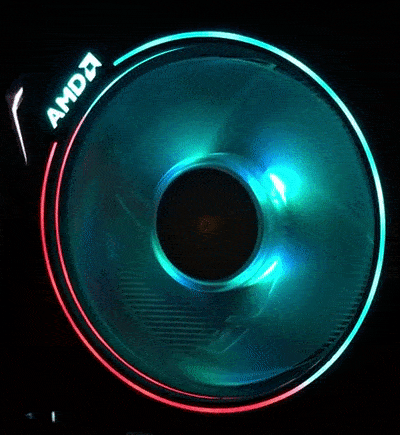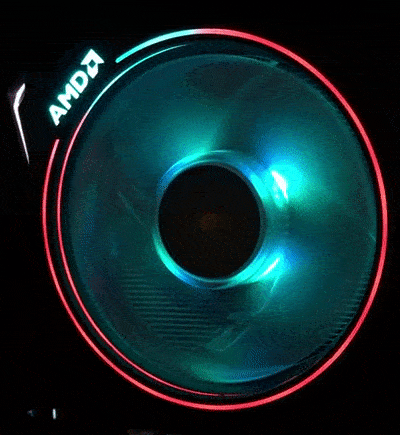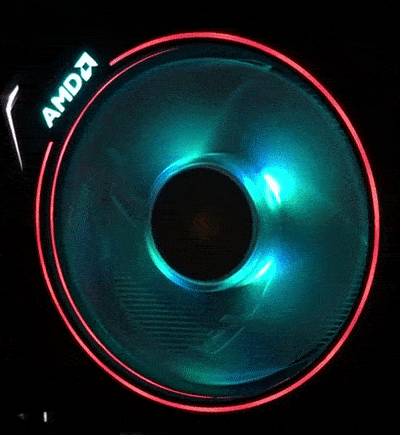
cm-rgb-monitor showing realtime cpu utilization.
Getting started
Installation & Configuration
Follow this simple guide on our wiki.
Usage
Package comes with two scripts cm-rgb-cli and cm-rgb-monitor.
cm-rgb-cli allows for fine grained control of each individual zone including turning off the LED's completely.
Check out the examples in our wiki.
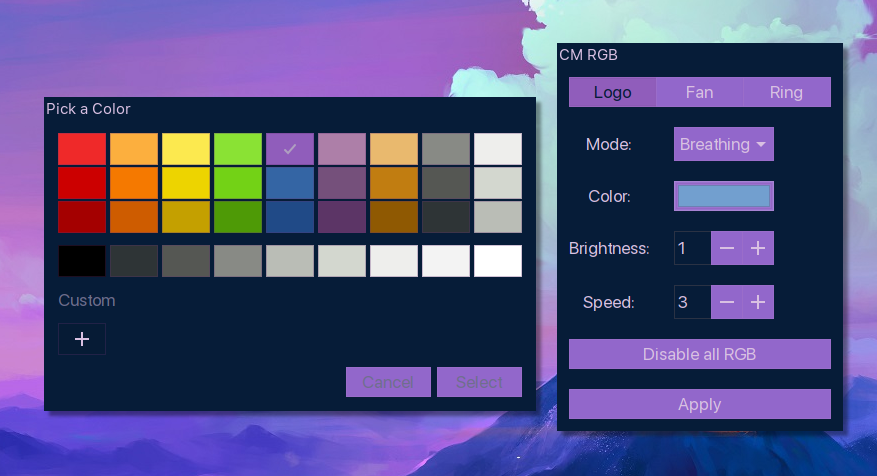
cm-rgb-gui GUI interface that serves the purpose of simplifying the usage of [cm-rgb-cli] (thanks to groovykiwi)
cm-rgb-monitor allows for displaying cpu utilization with ring LED's, along with temperature (thanks to mpsdskd).
Combining the cli + monitor can create neat transition from powering your system right to booting your OS.
Check out the examples in our wiki.
Licence
MIT
See LICENCE file for details
1 maintainer

Metadata
1 maintainer
Release files for cm-rgb 0.3.6
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| cm_rgb-0.3.6.tar.gz | 1.3 MB | Without provenance | Details |
Release files / cm_rgb-0.3.6.tar.gz
| Download URL | cm_rgb-0.3.6.tar.gz |
|---|---|
| Size | 1.3 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
c49833bb50b4e00bfa6bda60725b0e61557dd50ee175f1b65cef818e6e1dc2b8
|
|
BLAKE2b-256 checksum How to use checksums |
d725ad8a93712a5d1c55841677a61e0861983f4e089f27d2bb09f9541e9bac25
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/3.3.0 pkginfo/1.7.0 requests/2.25.1 setuptools/57.0.0 requests-toolbelt/0.9.1 tqdm/4.46.0 CPython/3.9.5
|
Security for cm-rgb 0.3.6
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














