




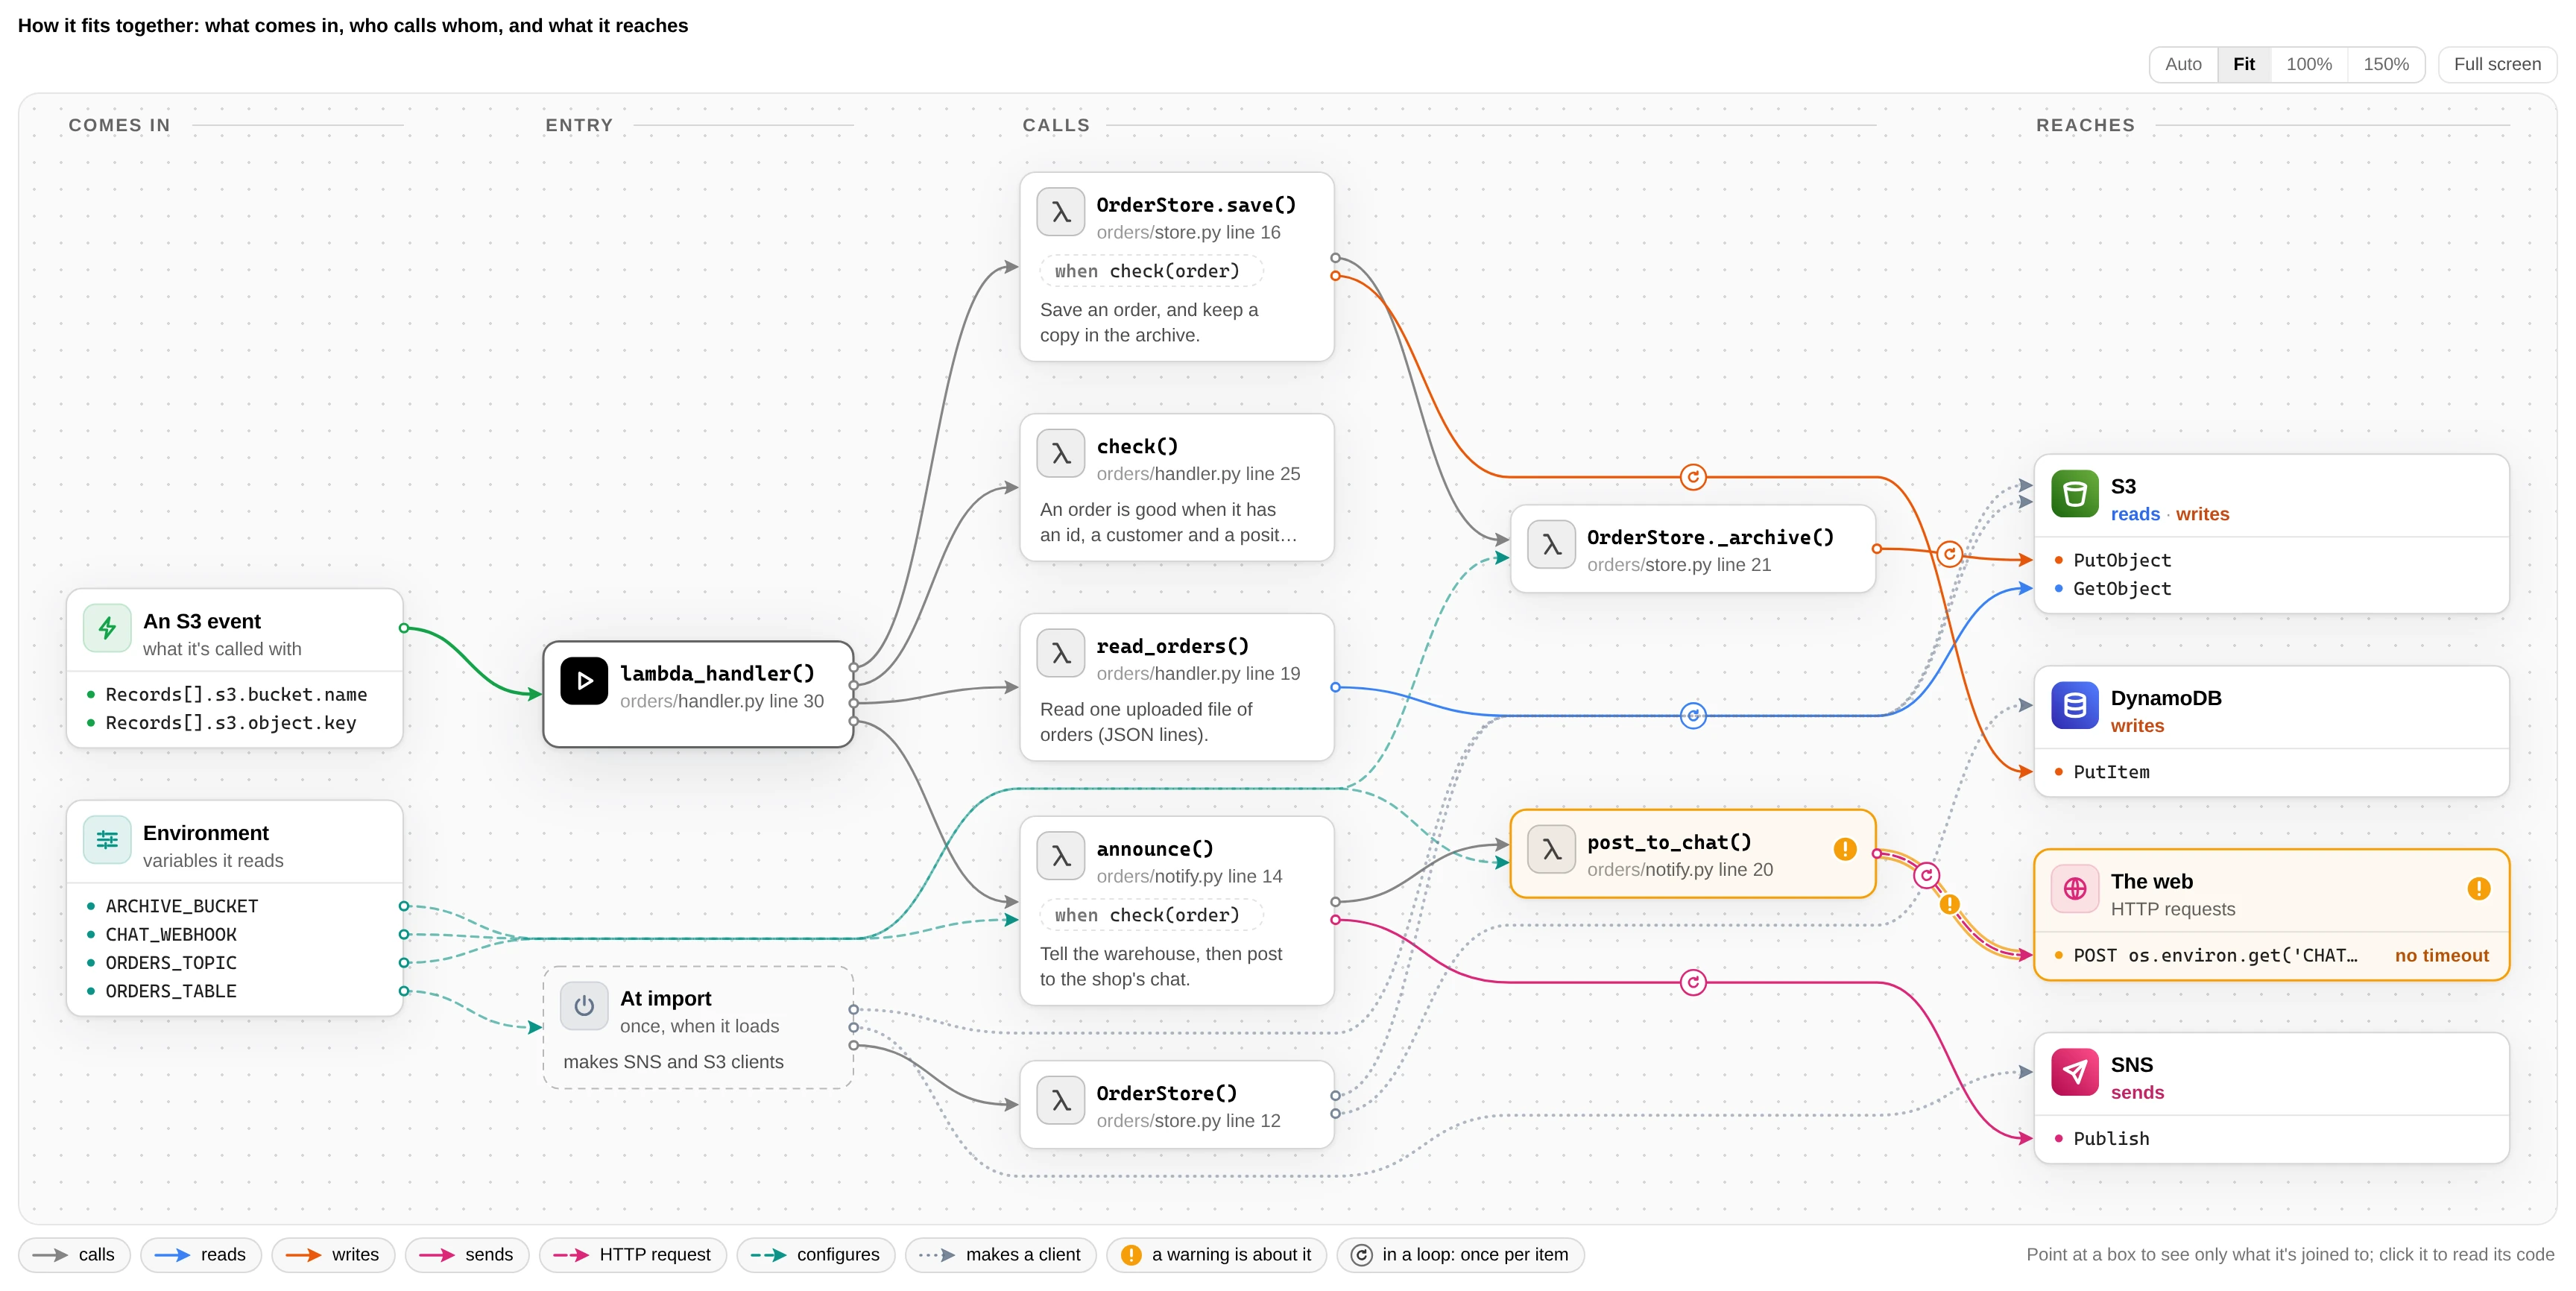
Point it at a repo. Get a page showing where the code starts, who calls whom, and what each path touches: AWS, HTTP, environment variables.
Install
pip install code-node-graph        # or: uv tool install code-node-graph
cd your/repo && code-node
What you get
| 🗺️ Graph | What comes in, who calls whom, what each path reaches. AWS calls coloured by kind (read, write, send, run); ↻ marks loops |
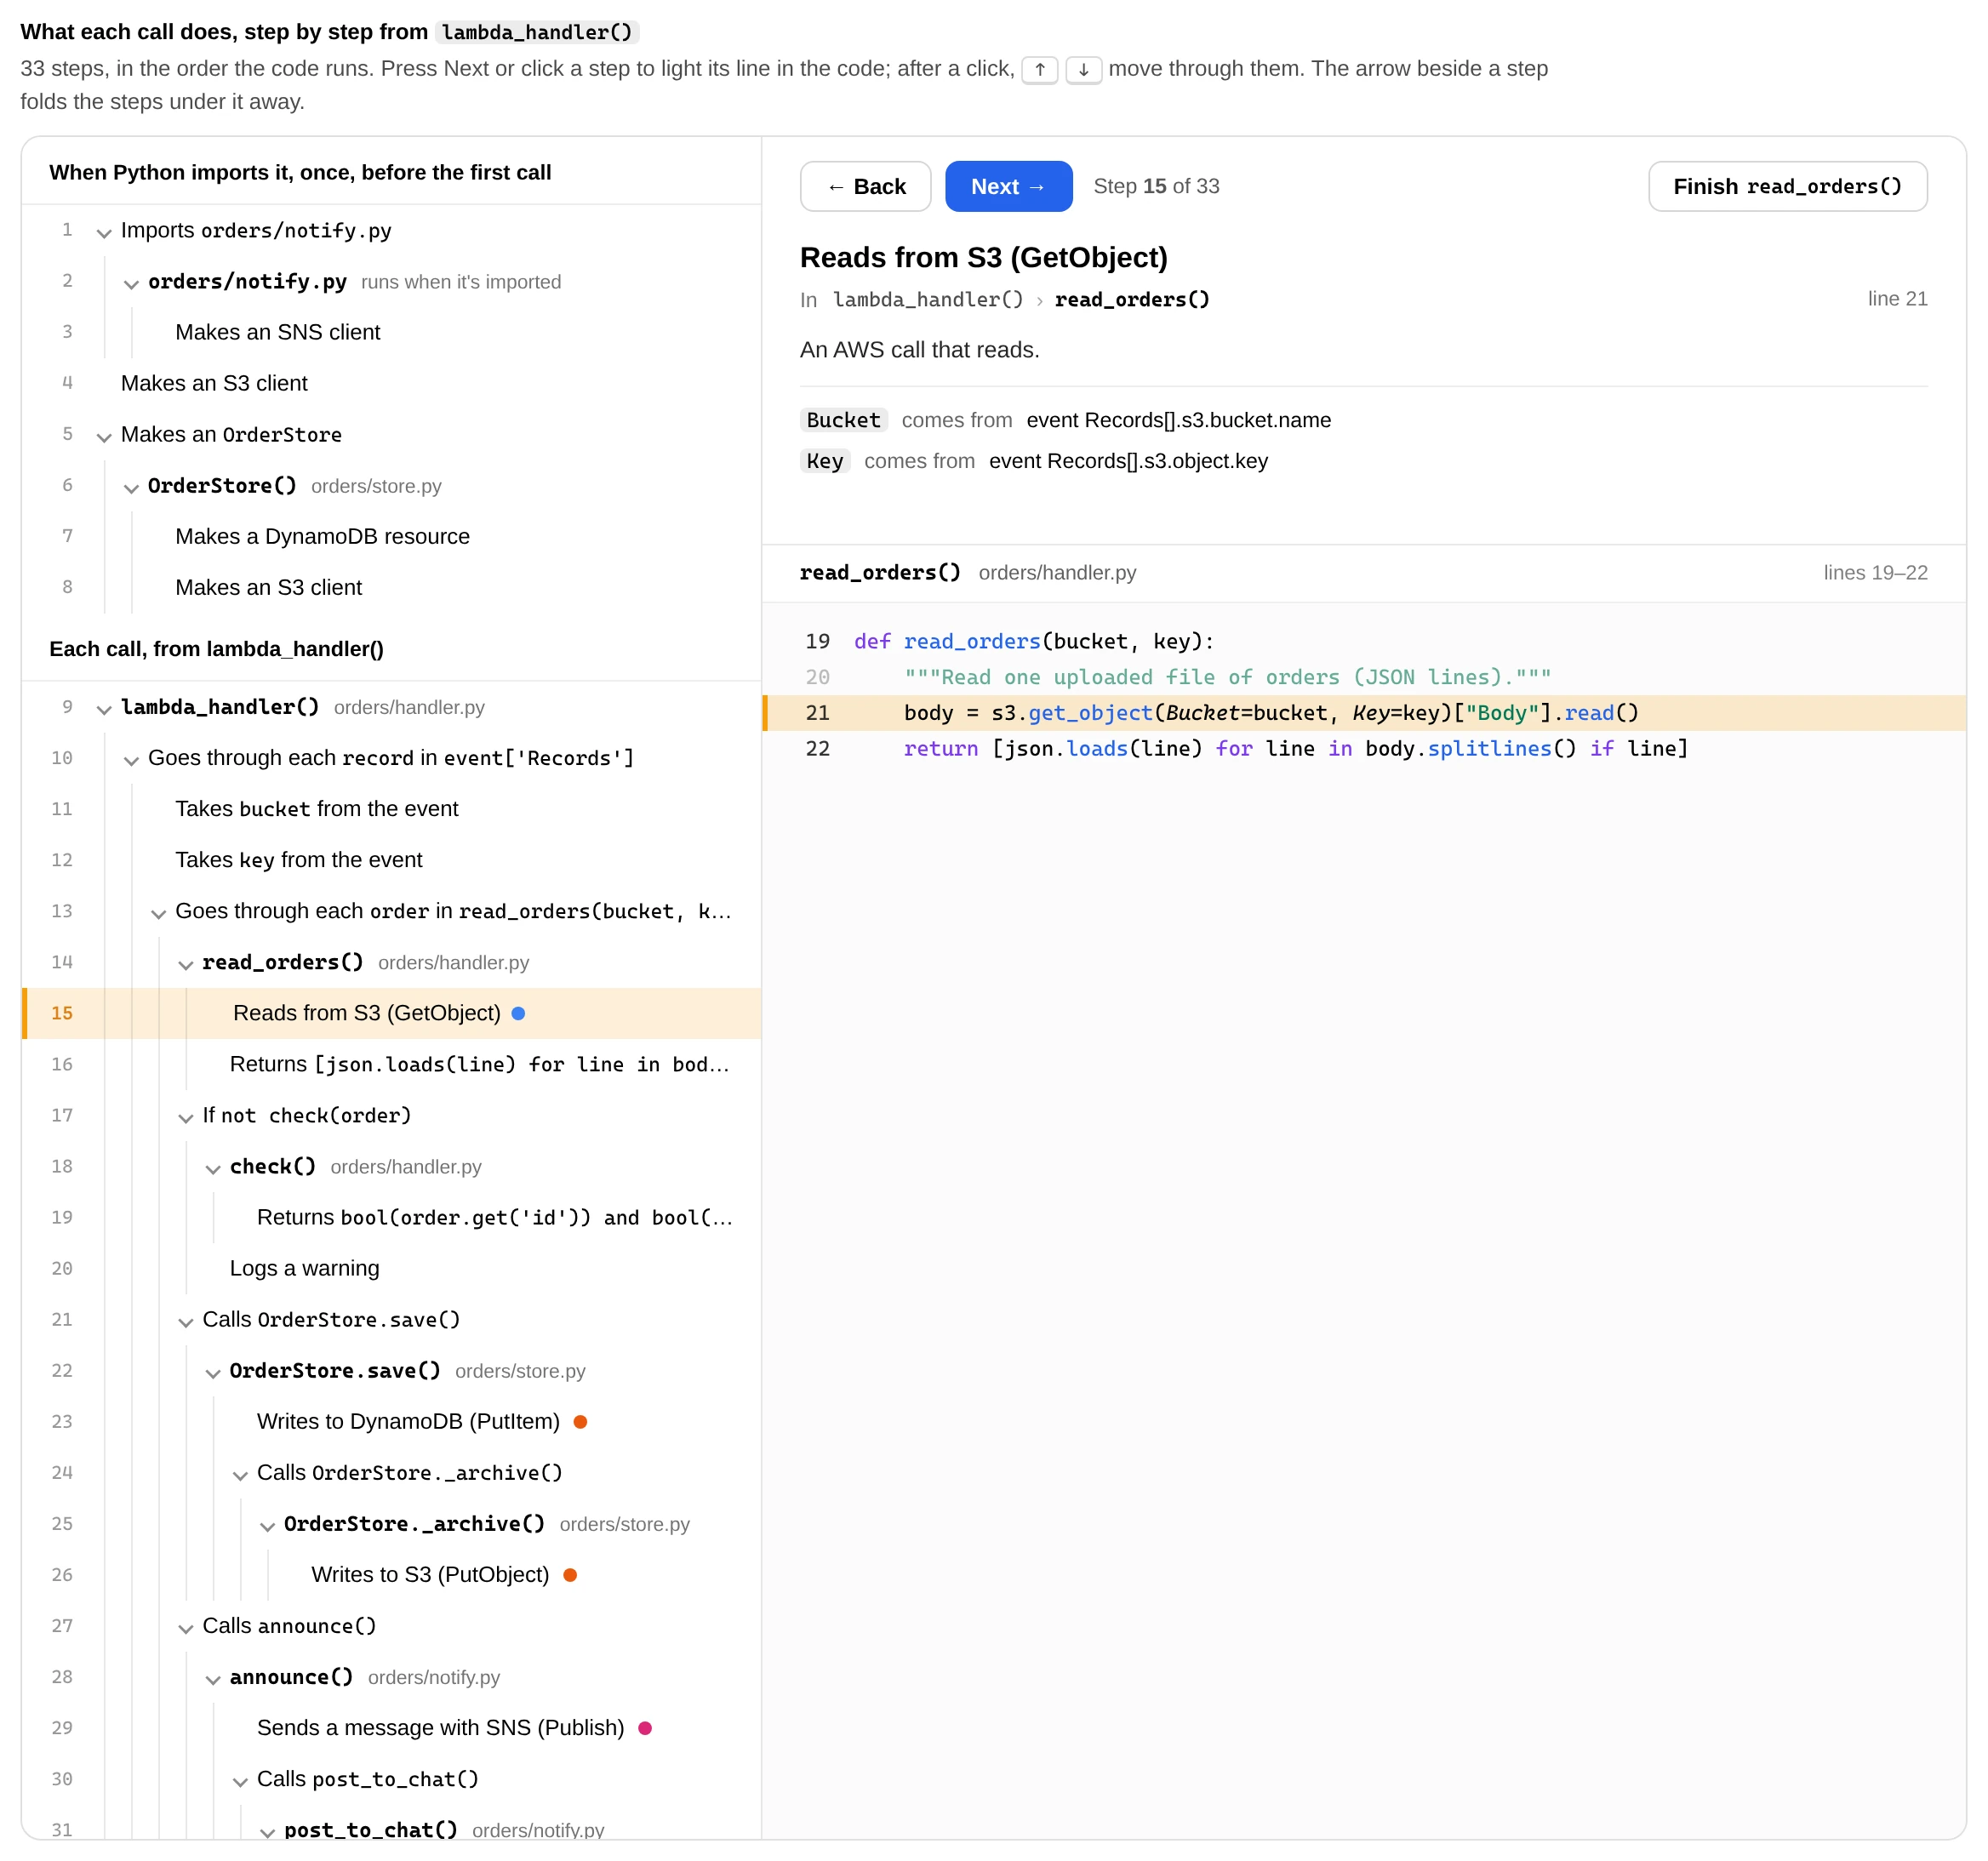
| 👣 Step by step | Walk the code in run order, like a debugger: Next, Skip call, Finish, arrow keys |
| 🔌 Plugins | boto3, Redis, SQL (sqlite3, psycopg, PyMySQL, asyncpg, SQLAlchemy), MongoDB, OpenAI, Anthropic |
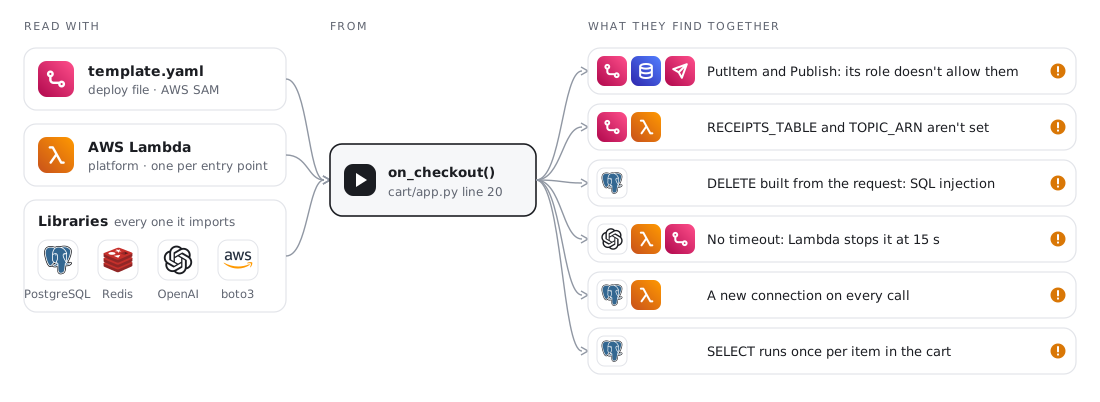
| 📄 Deploy checks | Reads SAM template.yaml / serverless.yml: unset variables, IAM calls the role won't allow, timeouts that don't fit |
| 🚨 Findings | SQL or shell commands built from input, clients with no timeout, queries in loops |
| 🧜 Mermaid | Paste the graph into Markdown, a wiki or a PR |
| 🔁 Live | --serve redraws on every save |
Usage
code-node                              # find entry points and pick one
code-node --list                       # just list them
code-node src/app/main.py:run          # start from a function
code-node src/app/store.py:Store.save  # ...or a method
code-node -e save                      # part of a name
code-node --serve                      # live page on localhost:8765
code-node --mermaid                    # print the graph as Mermaid
Entry points it finds
Console scripts in any pyproject.toml (monorepos too), functions named in SAM / Serverless files, Lambda handlers,
FastAPI / Flask routes, Django urls.py files, Typer commands, if __name__ == "__main__": blocks, and functions named
main. Test files are skipped. A web app's routes are read as called with the request, so SQL built from a query
string is flagged.
All options
| Option | What it does |
|---|---|
path |
Folder to read, or a file to start from (main.py, main.py:function) |
-e, --entry |
module.function, module.Class.method, file.py[:function], or part of a name |
-l, --list |
List entry points and stop |
--plugins |
List platforms, libraries and deploy files and stop |
--all |
Draw every function (default: 24 functions, 5 calls deep) |
--depth N, --functions N |
Your own limits |
--serve, --port N |
Serve on localhost, redraw on change |
--mermaid |
Print the graph as Mermaid |
-o, --out, --no-open |
Where to save (default ~/.cache/code-node/), and whether to open it |
--platform NAME, --lambda |
Run a platform's checks on any entry point |
--editor vscode|cursor|none |
Editor the line links open (default vscode, WSL-aware) |
From Python
from code_node import code_graph, map_code, read_project

project = read_project(".")
cmap = map_code(project.files, "pkg.cli.main", libraries=project.libraries())
print([call.label for call in cmap.aws])
print(code_graph(cmap).mermaid())
Plugins that mix
One platform, any number of libraries and deploy files, checked together. On
examples/cart-service:
Limits
It can't follow values from outside the code (a client a library hands back, a function picked from a registry at
run time), installed libraries' own code, or getattr with a computed name. A page can miss calls, but everything
it shows is in the code.
Develop
make install    # .venv with the dev tools (needs uv)
make check      # everything CI runs
make shots      # remake screenshots (needs Chrome)
python makefile.py <task> does the same on any OS.
Extracted from aws-analyzer's how_it_works(). Apache 2.0.
1 maintainer

Metadata
1 maintainer
Release files for code-node-graph 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| code_node_graph-0.1.0.tar.gz | 259.0 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| code_node_graph-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 573.1 kB
Release files / code_node_graph-0.1.0.tar.gz
| Download URL | code_node_graph-0.1.0.tar.gz |
|---|---|
| Size | 259.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
a10bba324fa8a1be782a5f950ef0d8d1eb2037e09f513d2e9361cb0f2a51bc89
|
|
BLAKE2b-256 checksum How to use checksums |
daa6fdc6bb2834c69047d5bb5d1d99bc20e4e9f00caa0333c00dffc04f992e39
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logRelease files / code_node_graph-0.1.0-py3-none-any.whl
| Download URL | code_node_graph-0.1.0-py3-none-any.whl |
|---|---|
| Size | 314.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
190cbbe80b29e2a244493531743270e8779ddf468cf4dcf65c7c6ea5c7da5197
|
|
BLAKE2b-256 checksum How to use checksums |
2d9b79d586911b3ab266ade3547ebec8972adc31d5a89c6b415e3e7ff69d5cb5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logSecurity for code-node-graph 0.1.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for code_node_graph-0.1.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 20, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














