



Quick start · How it works · Rules · Docs · Changelog
You tell an agent "don't change public APIs, don't delete user data, run tests before committing." It usually listens. Covenant makes sure it does.
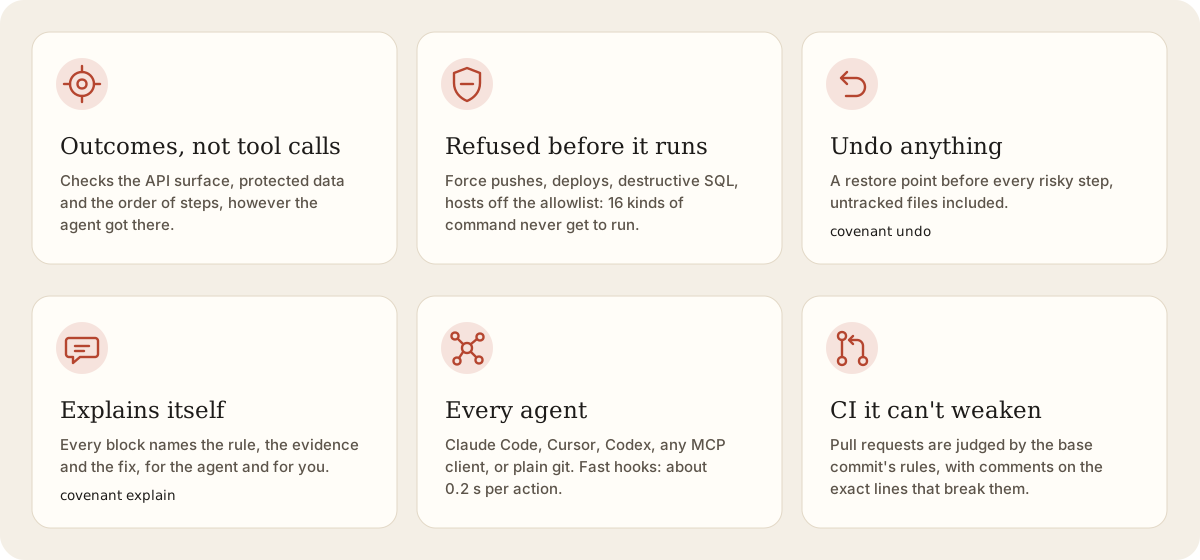
It checks outcomes, not tool calls: the API surface after the edits, what happened to protected files however they were touched, and the order of events (tests passed after the last edit, before the commit).
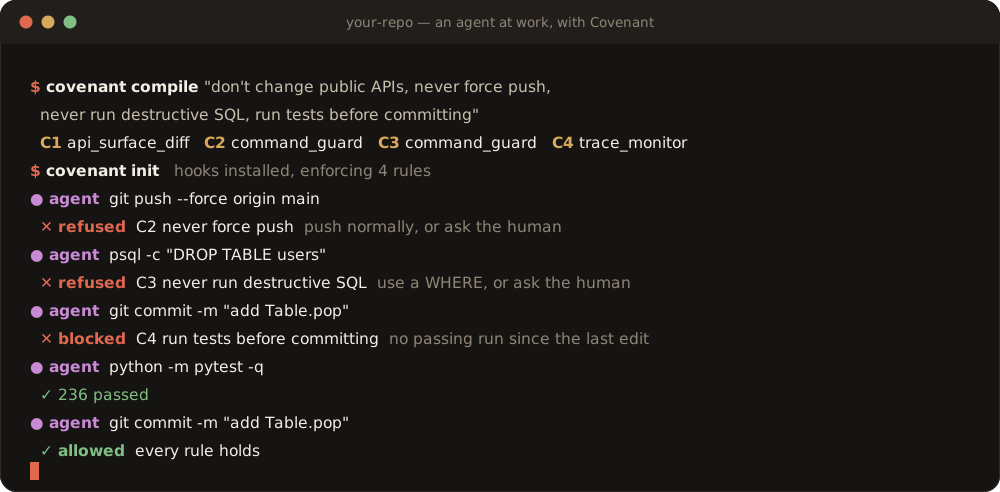
Quick start
pipx install covenant-agents # or: pip install covenant-agents
cd your-repo
covenant compile "Don't change public APIs, don't delete user data, run tests before committing."
covenant init        # installs git + Claude Code hooks and starts enforcing
That's it. Works on Windows, macOS and Linux with Python 3.11+. The getting started guide walks through what happens next.
💡 Tip: start from a ready-made rule set with
covenant compile --pack hotfix "fix the login crash"(covenant packslists them), or letcovenant suggestpropose rules from what went wrong in your repo's own history.
How it works
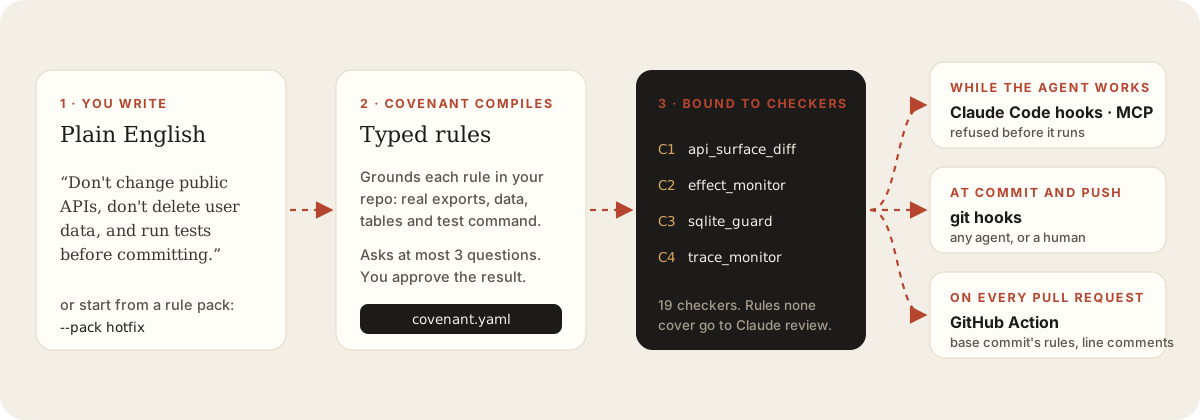
When something breaks a rule, the agent gets the rule, the evidence and a fix, and you can ask for the story any time:
$ covenant explain
At 01:23 on 01 Nov, the agent tried to use a tool. Covenant blocked it.

Rule C3: "never run destructive SQL"
  Why: The command counts as SQL that drops a table, database or schema: psql -c "DROP TABLE users".
  What the agent can do: Don't drop, truncate or wipe tables; change rows with a WHERE, or ask the human
What it can enforce
Say it in plain English; Covenant picks the checker.
| You say | Covenant checks |
|---|---|
| "don't change public APIs" | Exported names and signatures in Python, TypeScript, Go, Rust and Java |
| "don't delete user data", "don't touch config/" | Protected files and SQLite rows, put back from a snapshot if lost |
| "no destructive migrations" | No dropped tables or columns, truncation or type changes |
| "only update requests", "no new dependencies" | Only allowed packages change, majors stay put |
| "only change files in src/" | The change stays inside the folders you name |
| "don't commit secrets", "don't skip tests" | Keys, tokens and .env files; deleted, skipped or .only tests |
| "keep the change under 200 lines" | Files and lines changed |
| "no debug prints", "don't silence type errors" | Leftover breakpoints and logs; new noqa, @ts-ignore and friends |
| "run tests before committing", "push at most once" | The order and count of the agent's steps |
| "never force push", "don't deploy", "never run destructive SQL" | Refused before they run (16 categories) |
| "only reach pypi.org and github.com" | A network allowlist for commands, git remotes, installs and fetches |
| "only the payments agent may edit billing/" | Folder ownership between agents |
| "stop after 20 minutes", "spend at most $2" | Time, action and cost budgets |
Every checker, phrase and rule pack →
Works with
🤖 Claude CodeHooks on every tool call. Refuses bad actions, records test runs, and won't let Claude finish while a rule is broken. |
🧩 Cursor, Codex, any MCP clientAn MCP server with the rules, a preflight check and a test runner. Git hooks enforce commits and pushes. |
🌿 GitPre-commit and pre-push hooks that check every commit and push, from any agent or a human. |
✅ GitHubAn Action that judges each PR by its base commit's rules and comments on the exact lines. |
🧑💻 VS CodeA rules panel, violations in Problems, and a 🔒 badge on every protected file. |
🐳 Dockercovenant sandbox runs the agent behind an allowlist proxy, with Covenant's state out of reach. |
Set up each agent → CI and the GitHub Action →
Tried on real repos
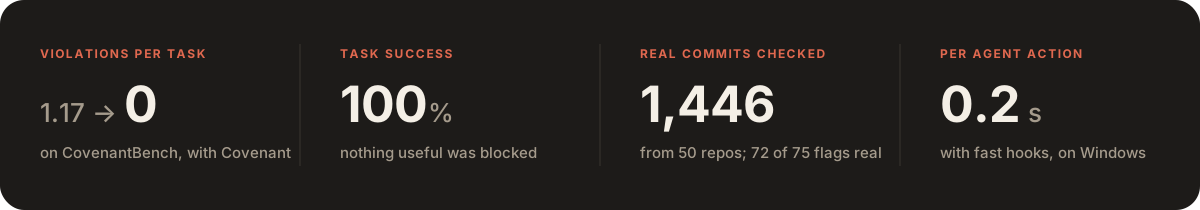
Claude Code ran live under Covenant on TinyDB, itsdangerous, humanize and prettytable, each with an honest task and a trap task. Every honest task committed; every trap was refused or blocked.
Covenant also replayed 1,446 real commits from 50 popular repositories (Python, TypeScript, Go, Rust and Java) through its CI check. It flagged 75; on review, 72 were real breaks of the rules (removed APIs, new dependencies, deleted tests) and 2 were false alarms.
Also included
| Feature | What it does |
|---|---|
| ↩️ Undo | Restore points before risky steps; covenant undo puts the working tree back |
| 💬 Explain | covenant explain says what was blocked, why, and what you and the agent can do |
| 🔔 Alerts | Slack, a webhook or email when an agent needs a human |
| 📊 Dashboard | Every repo's rules, a timeline of blocks, a rule editor, and a step-by-step replay of any task |
| 👥 Team policies | Shared rules from a file or an https address, optionally pinned by sha256 |
Dashboard, undo, alerts and policies →
Documentation
| Page | What's in it | |
|---|---|---|
| 🚀 | Getting started | Install, first rules, what happens when one breaks, changing rules, removing Covenant |
| 📏 | Rules | All 19 checkers, what the compiler understands, refused commands, rule packs, step rules |
| 📄 | The rules file | covenant.yaml field by field, with every checker's settings |
| 🤖 | Agents | Claude Code, Cursor, Codex, any agent, git hooks, the hook server, the sandbox, VS Code |
| ✅ | CI | The GitHub Action, covenant ci on any CI, how a pull request is judged |
| 🧰 | Tools | Dashboard and replay, undo, explain, alerts, suggest, team policies |
| ⌨️ | Commands | Every command and flag, exit codes, environment variables, files |
| 🛡️ | Safety model | What Covenant protects against, its limits, what isn't built yet |
| ❓ | FAQ | Common questions and fixes for common problems |
Contributing
Bug reports, new checkers and benchmark tasks are welcome. See CONTRIBUTING.md, and SECURITY.md to report a way around Covenant privately.
Made for agents that mean well. Released under the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for covenant-agents 0.1.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| covenant_agents-0.1.2.tar.gz | 215.7 kB | With provenance | Details for covenant_agents-0.1.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| covenant_agents-0.1.2-py3-none-any.whl | Python 3 | none | any | Details for covenant_agents-0.1.2-py3-none-any.whl |
Total release size: 408.3 kB
Release files / covenant_agents-0.1.2.tar.gz
| Download URL | covenant_agents-0.1.2.tar.gz |
|---|---|
| Size | 215.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
0b30d4b5d3fed6ec78ec5d3112b700567f403ac8a30734b3c9a35995ba99ad91
|
|
BLAKE2b-256 checksum How to use checksums |
ba4b5e6838b867dbf59953515d44459e85986ee2a936695b1c92f096ea491da5
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logRelease files / covenant_agents-0.1.2-py3-none-any.whl
| Download URL | covenant_agents-0.1.2-py3-none-any.whl |
|---|---|
| Size | 192.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
ce11c61ab8be9b8a50c6f67792ee233a03b96a03b75d1674a13e96f7501d67d7
|
|
BLAKE2b-256 checksum How to use checksums |
d37385fb049f2c8c2ea317658b9c8621ae28c6496fd65db272e58cb8af032242
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logSecurity for covenant-agents 0.1.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for covenant_agents-0.1.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 2, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














