
Cursor Secret Scan
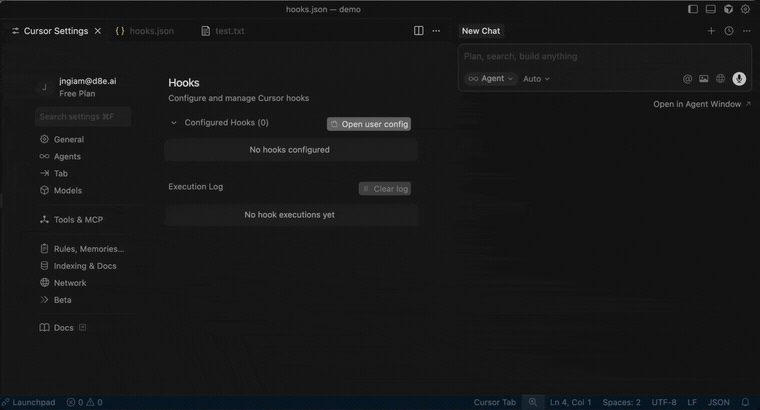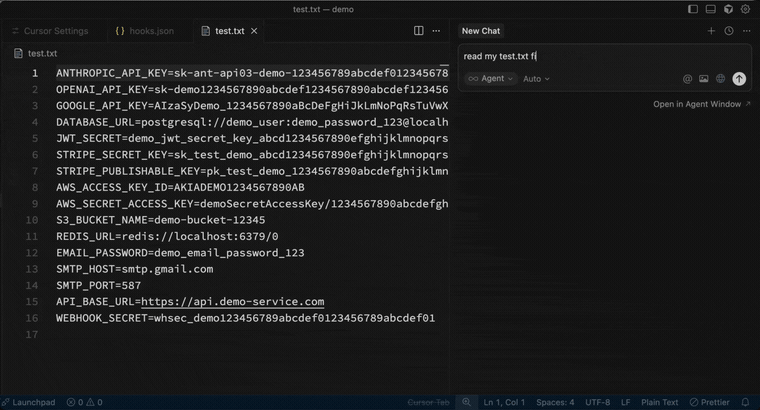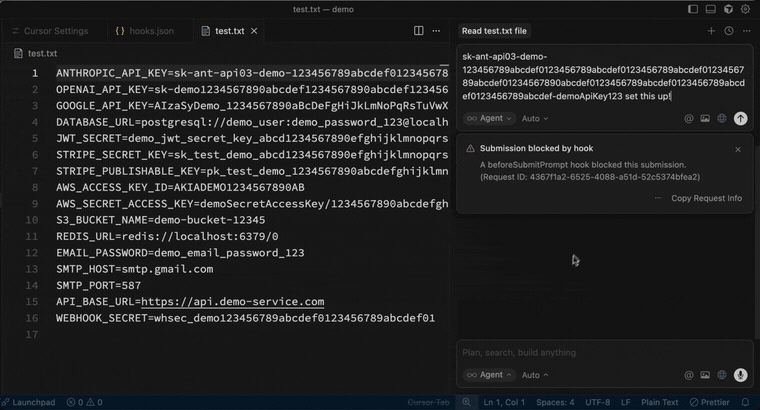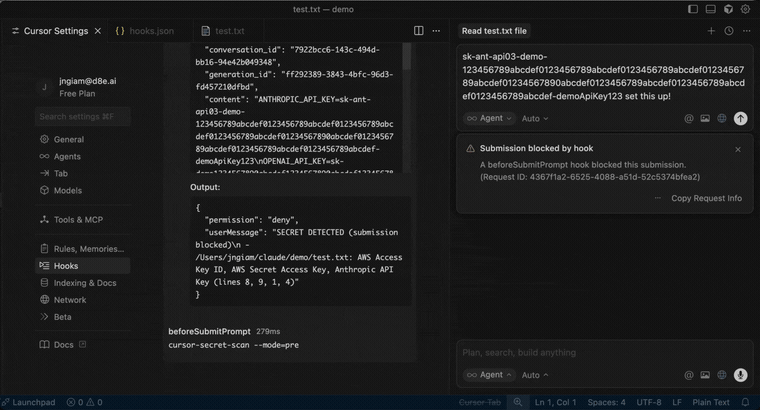
Secret scanning CLI for Cursor. Blocks or warns on common credentials (cloud, source control, payment, collaboration) using local regex matching.
Install
- pipx (recommended):
pipx install cursor-secret-scan
- pip (user):
python3 -m pip install --user cursor-secret-scan
Hook Setup (Cursor)
Add to ~/.cursor/hooks.json:
{
  "version": 1,
  "hooks": {
    "beforeReadFile": [{"command": "cursor-secret-scan --mode=pre"}],
    "beforeSubmitPrompt": [{"command": "cursor-secret-scan --mode=pre"}]
  }
}
CLI Usage
- Pre mode (blocks on detection):
echo '{"hook_event_name":"beforeSubmitPrompt","prompt":"hello"}' | cursor-secret-scan --mode=pre
- Post mode (warns on detection):
echo '{"hook_event_name":"afterShellExecution","stdout":"OPENAI_API_KEY=...T3BlbkFJ..."}' | cursor-secret-scan --mode=post
How It Works
- Regex-based scanner implemented in this project.
- Reads only from hook JSON input or file paths provided by the hook.
- Binary-aware scanning with size limits; local-only execution.
Notes
- Pre hooks block; post hooks print warnings.
Links
- Source, docs, and examples: https://github.com/mintmcp/agent-security
1 maintainer

Metadata
1 maintainer
Release files for cursor-secret-scan 0.1.14
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| cursor_secret_scan-0.1.14.tar.gz | 2.4 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| cursor_secret_scan-0.1.14-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 5.3 kB
Release files / cursor_secret_scan-0.1.14.tar.gz
| Download URL | cursor_secret_scan-0.1.14.tar.gz |
|---|---|
| Size | 2.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
074645d75b99d890f56576e17e0a3ede4aff8696b066f7974e37fcf2babe0035
|
|
BLAKE2b-256 checksum How to use checksums |
cea6dc90a1a5edb2007b9e90762d52765ea42936995b3e5af9d2f4bffada49c9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2025.
Transparency logRelease files / cursor_secret_scan-0.1.14-py3-none-any.whl
| Download URL | cursor_secret_scan-0.1.14-py3-none-any.whl |
|---|---|
| Size | 2.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
554f971e49d0a0121f8f5efa9440965a7895daa7d8e44af34cc18aef0e9d5673
|
|
BLAKE2b-256 checksum How to use checksums |
0ea6fa0d2470d4c13c0fe06629b459bc40e3a98820bf2e7a656b33dec415b423
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2025.
Transparency log













