


Common Web Application Vulnerability Scanner. [python Version]
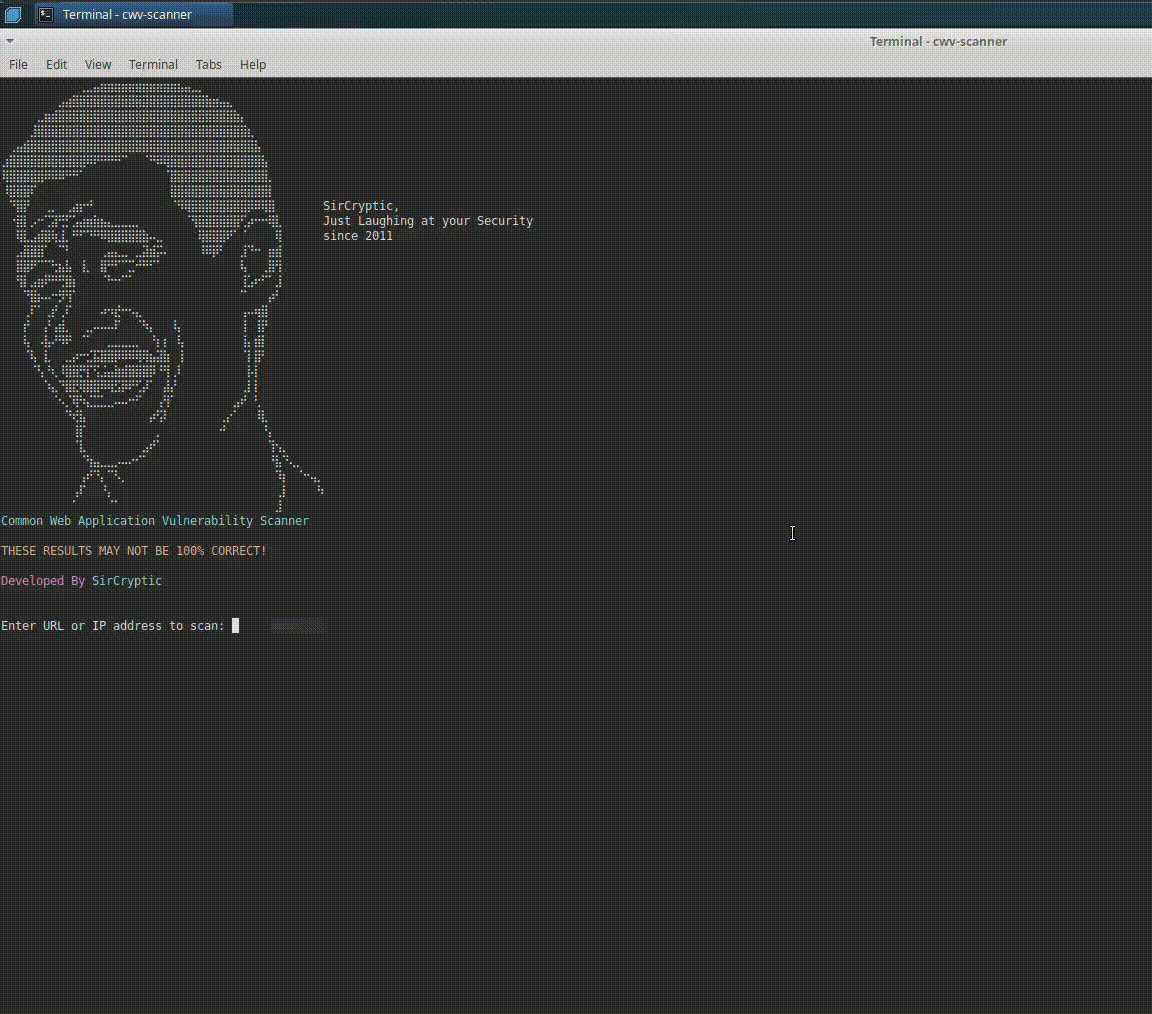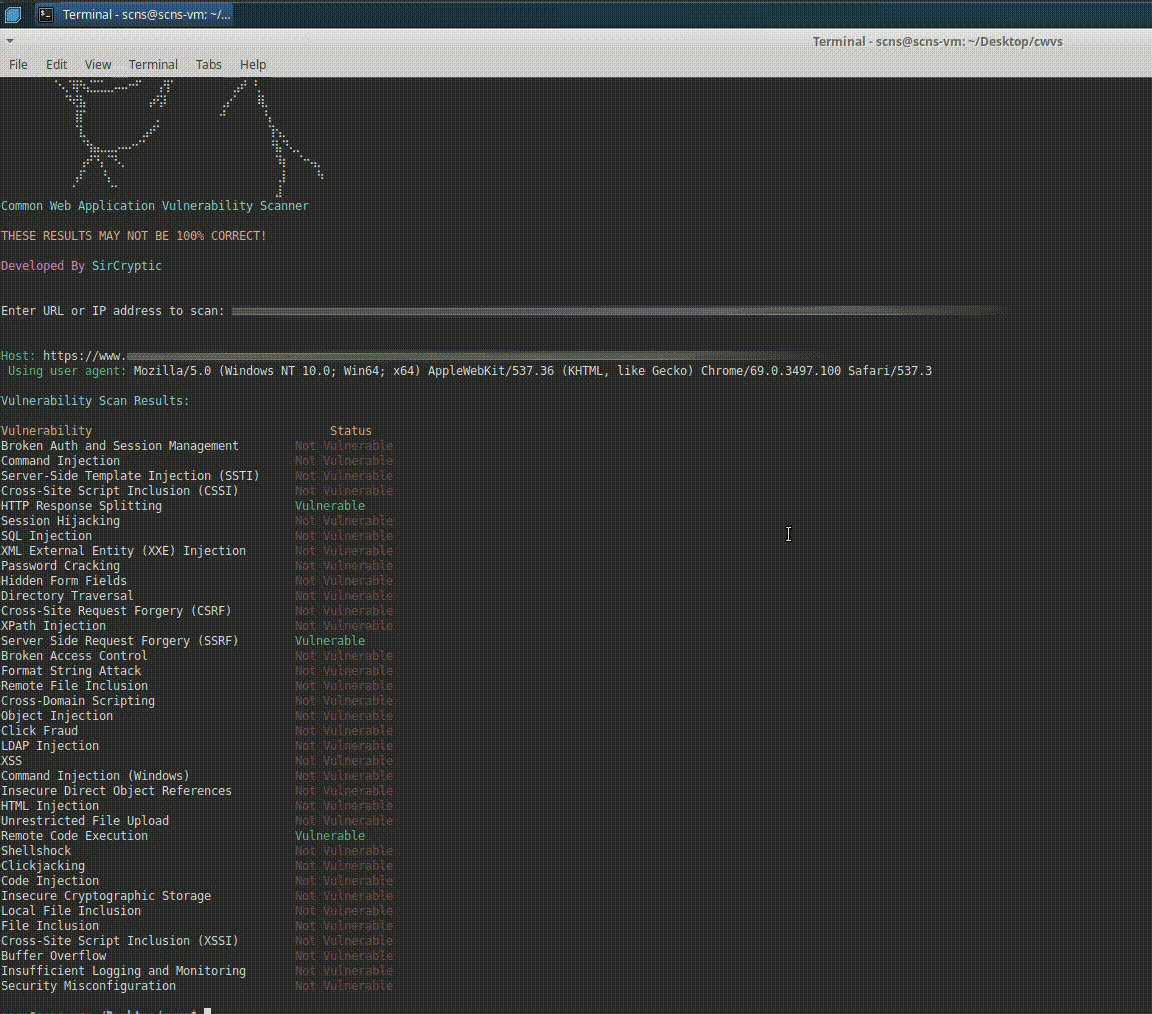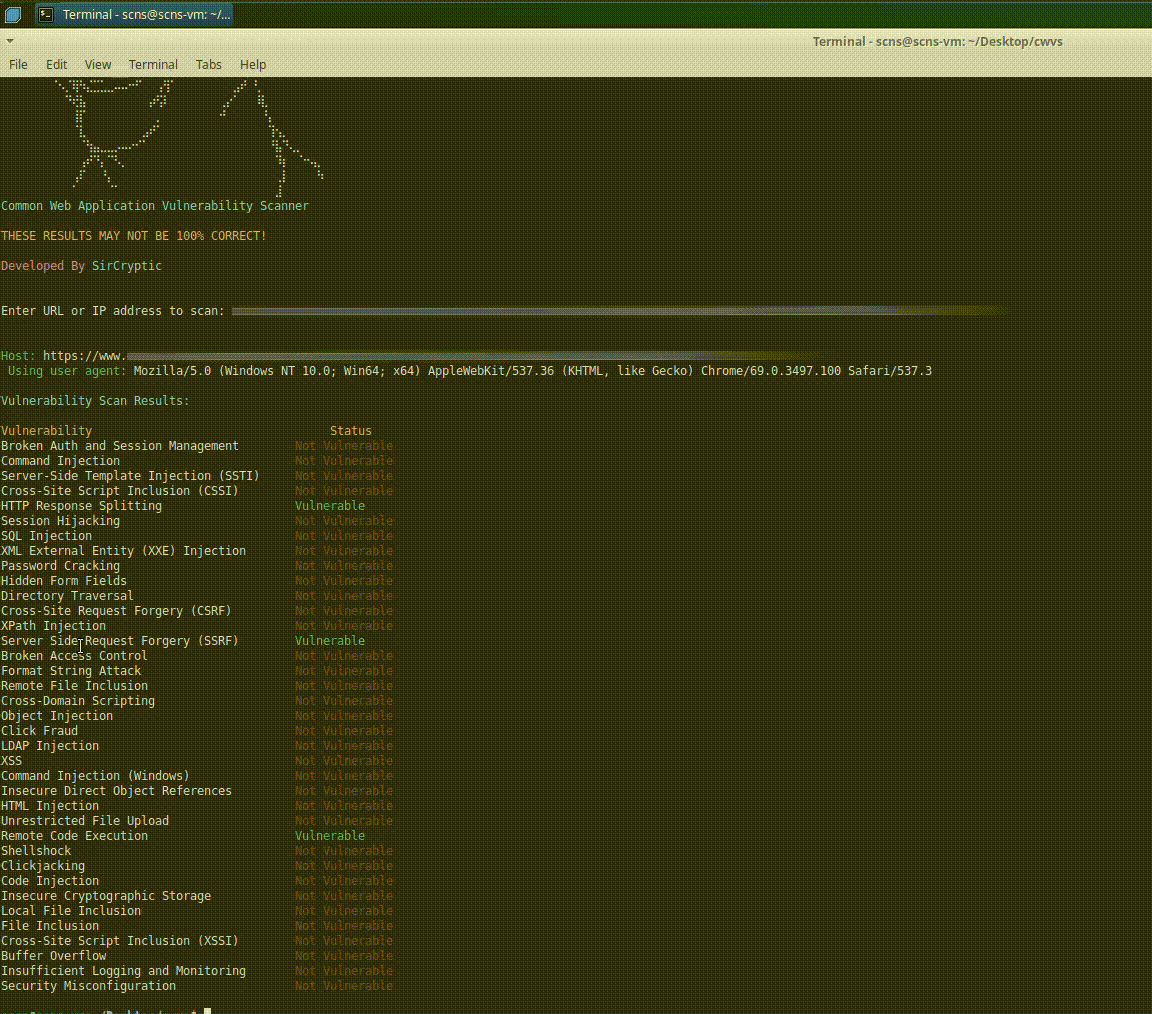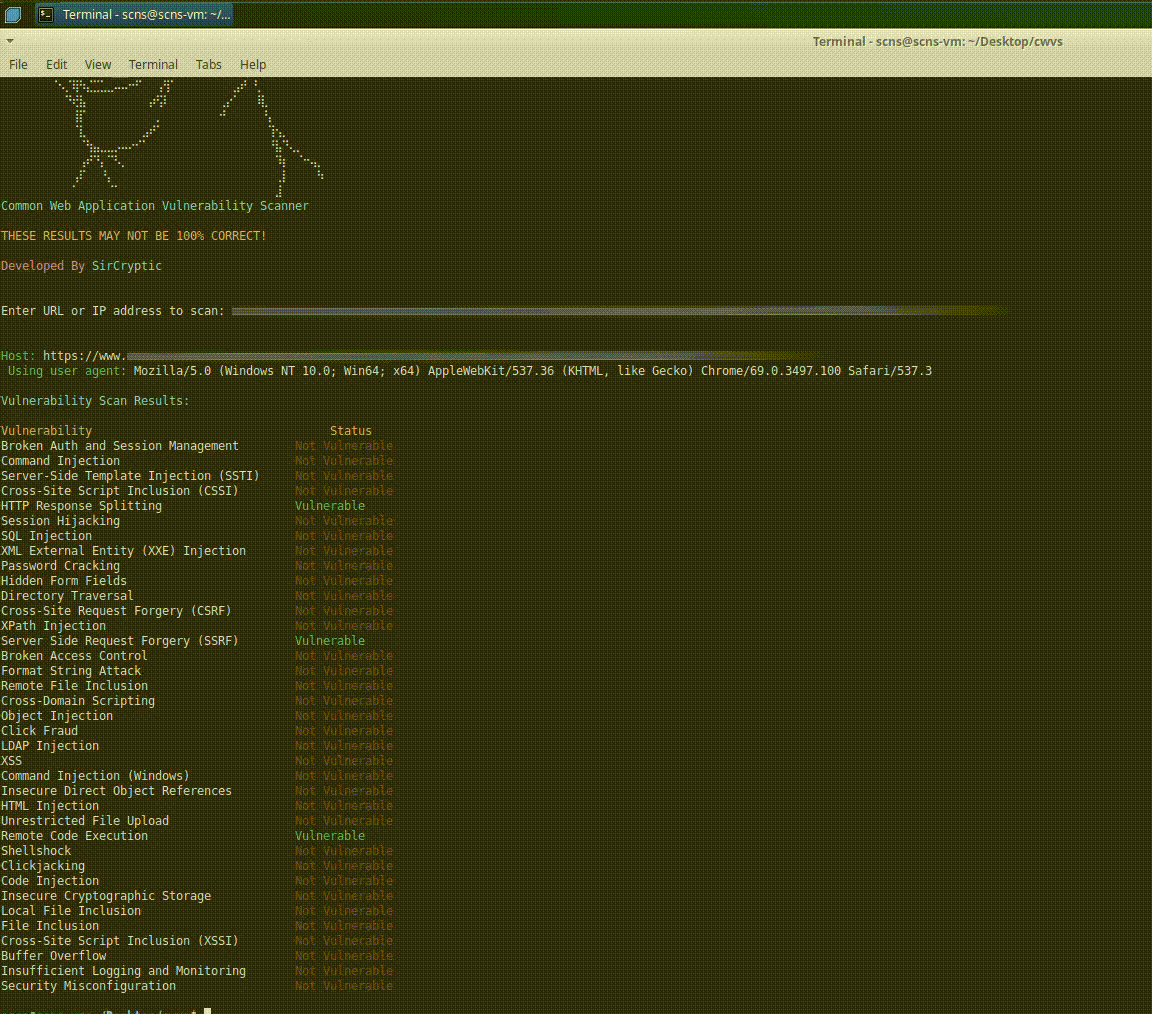
This is a simple web application vulnerability scanner that checks if a given URL or IP address is vulnerable to common web application security vulnerabilities. The tool is designed to help website owners and security researchers identify vulnerabilities in their web applications that can be exploited by attackers.
Installation
pip install cwv-scanner
Usage
cwv-scanner example.com
Vulnerabilities Checked by cwv-scanner
The scanner checks for the following 36 vulnerabilities:
| Vulnerability | Description |
|---|---|
| SQL Injection | Injecting malicious SQL code into inputs to manipulate database queries. |
| XSS (Cross-Site Scripting) | Injecting malicious scripts into web pages viewed by users. |
| File Inclusion | Loading unauthorized files due to unsanitized user input. |
| Directory Traversal | Accessing restricted directories via manipulated input paths. |
| Remote File Inclusion | Including malicious code from remote servers via user input. |
| Command Injection | Executing arbitrary commands by injecting malicious input. |
| Cross-Site Request Forgery (CSRF) | Tricking users into submitting unauthorized requests. |
| Unrestricted File Upload | Uploading malicious files that can be executed on the server. |
| Password Cracking | Exploiting weak passwords to gain unauthorized access. |
| Session Hijacking | Stealing session IDs to impersonate authenticated users. |
| Broken Auth and Session Management | Bypassing authentication or hijacking sessions due to poor implementation. |
| Remote Code Execution | Executing arbitrary code on the server via malicious input. |
| Local File Inclusion | Loading local files that should not be accessible via user input. |
| Server Side Request Forgery (SSRF) | Sending unauthorized requests to internal/external servers. |
| XML External Entity (XXE) Injection | Exploiting XML parsing to access sensitive data or execute code. |
| Cross-Site Script Inclusion (XSSI) | Loading external JavaScript to execute malicious code in the browser. |
| Server-Side Template Injection (SSTI) | Injecting malicious code into server-side templates for execution. |
| HTML Injection | Injecting malicious HTML to steal data or manipulate page content. |
| XPath Injection | Manipulating XPath queries to access unauthorized data. |
| Code Injection | Injecting executable code into the application to run on the server. |
| Object Injection | Manipulating serialized objects to execute arbitrary code. |
| Cross-Domain Scripting | Injecting scripts from external domains to steal browser data. |
| HTTP Response Splitting | Injecting newlines into HTTP headers to manipulate responses. |
| Buffer Overflow | Exploiting buffer overruns to execute arbitrary code. |
| Format String Attack | Exploiting format string vulnerabilities to execute code. |
| Command Injection (Windows) | Injecting commands into Windows systems via malicious input. |
| Insecure Cryptographic Storage | Exploiting weak encryption to access sensitive data. |
| Insecure Direct Object References | Accessing unauthorized resources via unvalidated input. |
| Insufficient Logging and Monitoring | Failing to log or monitor security events, enabling undetected attacks. |
| Security Misconfiguration | Exploiting misconfigured server or application settings. |
| Cross-Site Script Inclusion (CSSI) | Including external stylesheets that could be controlled by attackers. |
| Click Fraud | Generating fake ad clicks to manipulate revenue or budgets. |
| Broken Access Control | Bypassing access controls to gain unauthorized access to resources. |
| Clickjacking | Tricking users into clicking disguised malicious elements. |
| Hidden Form Fields | Submitting unexpected data via hidden form fields to bypass validation. |
| Shellshock | Exploiting Bash vulnerabilities to execute arbitrary code. |
Credits
FootNote/s
- Results cannot be 100% Gaurenteed
1 maintainer

Metadata
1 maintainer
Release files for cwv-scanner 1.0.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| cwv_scanner-1.0.2.tar.gz | 28.1 kB | With provenance | Details for cwv_scanner-1.0.2.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| cwv_scanner-1.0.2-py3-none-any.whl | Python 3 | none | any | Details for cwv_scanner-1.0.2-py3-none-any.whl |
Total release size: 55.6 kB
Release files / cwv_scanner-1.0.2.tar.gz
| Download URL | cwv_scanner-1.0.2.tar.gz |
|---|---|
| Size | 28.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
7c825b3fb7357ac23685e1dd7d37e3b3b44cba6b946b42bd20b8b5a61d7e3047
|
|
BLAKE2b-256 checksum How to use checksums |
8bf4639a94d5071e45f63dcb3a08144898e9eb2bc3ca218742b965903efcb8d1
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Dec 7, 2025.
Transparency logRelease files / cwv_scanner-1.0.2-py3-none-any.whl
| Download URL | cwv_scanner-1.0.2-py3-none-any.whl |
|---|---|
| Size | 27.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
43a2ff9cdd239f6eb11f267594d69f5d33ffecac2fd8ec51bf6198b7f57bb01d
|
|
BLAKE2b-256 checksum How to use checksums |
c23af4c1ee79bcab6fdab90d27b7ac45b4d13cf0ee4fd4eb9ad06d9c9b7dc41e
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Dec 7, 2025.
Transparency logSecurity for cwv-scanner 1.0.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for cwv_scanner-1.0.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Dec 7, 2025.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














