
DBF_Anonymizer
Stable 1.0 contract (clean-slate architecture); the package version is
1.0.0 (stable). Repository metadata alone does not prove public
availability: PyPI publication is performed only by the privileged release
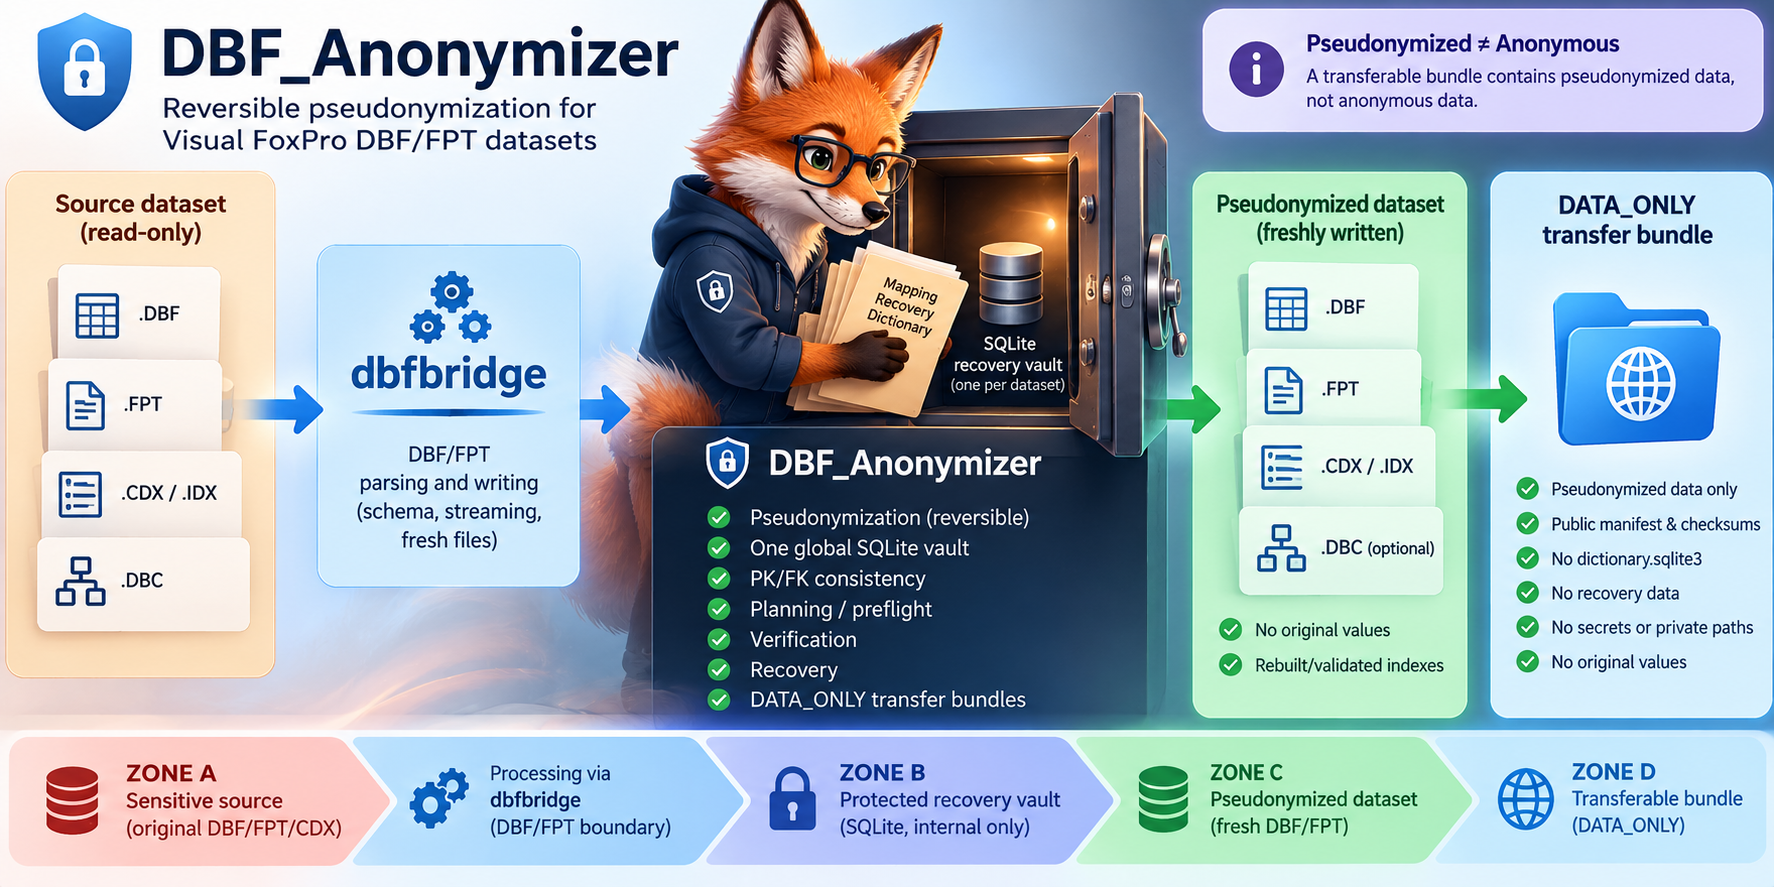
workflow. DBF_Anonymizer pseudonymizes
Visual FoxPro DBF/FPT datasets while keeping one protected, reversible SQLite
recovery vault inside the internal environment, and produces transferable
pseudonymized data-only bundles.
- Distribution:
dbf-anonymizer - Import package:
dbf_anonymizer - Version:
1.0.0(stable) - DBF/FPT boundary: the public
dbfbridge[write]>=1.1.0,<2distribution (Direct Read + Direct Write); DBF_Anonymizer implements no DBF/FPT parsing or writing of its own.
The 1.0 line has no compatibility obligation toward the historical 0.3 API, CLI, JSONL pipeline, salt-based generator or legacy recovery formats; see docs/migration-1.0-clean-slate.md.
The public 1.0-line operation surface (the frozen stable 1.0 contract) is the
synchronous, transport-neutral
package root dbf_anonymizer (capabilities, build_plan, preflight,
pseudonymize, verify_dataset, recover, create_transfer_bundle,
verify_transfer_bundle) plus the standalone dbf-anonymizer console script
with exactly nine commands: capabilities, plan, preflight,
pseudonymize, verify, recover, export-bundle, verify-bundle,
self-test. DBF_Anonymizer is not an MCP server: it ships no transport, no
authentication/authorization and no job orchestration — those belong to the
downstream host (see
docs/mcp-integration.md).
Pseudonymized is not anonymous. Reversible data with a protected recovery vault is pseudonymized data; DATA_ONLY output removes direct recovery material but is still not anonymized. See docs/pseudonymization-vs-anonymization.md.
Installation
The stable version is 1.0.0. Public availability on the approved package
index is established ONLY by the privileged release workflow — repository
metadata alone does not prove it. If the version is not yet available from
the approved index, install from a built wheel; after publication, the
approved published distribution is the supported route:
python -m build
python -m pip install --no-cache-dir dist\dbf_anonymizer-1.0.0-py3-none-any.whl
For the internal-network offline installation (pinned wheelhouse, --no-index,
--find-links, no runtime downloads), see
docs/operations.md.
5-minute quick start
The complete public API is the package root dbf_anonymizer. Replace the
placeholder paths with YOUR OWN authorized dataset paths (the fully
executable synthetic version of this workflow is
examples/basic_workflow.py):
from pathlib import Path

import dbf_anonymizer as public

source = Path("<your-source-dataset>")  # read-only input (trusted environment)
output = Path("<your-pseudonymized-output>")  # written by pseudonymize
vault = Path("<protected>/recovery.sqlite3")  # ONE protected vault per dataset (trusted)

plan = public.build_plan(source, output, vault)
preflight_result = public.preflight(plan)
if not preflight_result.ready:
    raise RuntimeError("preflight refused the plan; nothing was executed")

result = public.pseudonymize(plan)
verification = public.verify_dataset(result, source=source, vault=vault)
if verification.status is not public.VerificationStatus.PASS:
    raise RuntimeError("dataset verification did not reach PASS")
Failures are typed, privacy-safe, registry-controlled objects — never parse exception text:
try:
    plan = public.build_plan(source, output, vault, policy={"schema_version": 99})
except public.PolicyError as error:
    payload = error.to_dict()  # versioned JSON contract, no private material
    if error.code is not public.ErrorCode.POLICY_INVALID:
        raise RuntimeError("unexpected error code") from error
Executable recipes (synthetic data, progressive complexity) live in examples/README.md; the authoritative detailed guide is docs/operations.md.
Safety model
SOURCEstays in the trusted internal environment and is never modified.- Exactly ONE protected
VAULTspans the whole dataset. The vault is what makes the output recoverable — it belongs to the trusted environment and must NEVER be transferred or published. DATA_ONLYtransfer bundles are the only transferable artifact: verified, standalone, free of vault/recovery material — pseudonymized data, NOT anonymous data.
Documentation
English-first operational and security documentation (validated by
tests/test_p7_documentation_contract.py, including executable examples):
- examples/README.md — the executable example recipes (synthetic data, progressive complexity, downstream-consumer adapter).
- docs/operations.md — internal-network offline installation, one-vault-per-dataset operation, policy configuration, relationship configuration, pseudonymization, verification, recovery, and DATA_ONLY transfer bundles, with executable examples.
- docs/limits-and-integrity.md — index/VFP/DBC limitations, the VFP_INDEXED backend-evidence requirement and the authoritative-metadata boundaries.
- docs/external-vfp-metadata-contract.md — the package-owned, producer-independent external VFP relationship/index metadata consumer contract (versioned JSON Schema shipped with the wheel).
- docs/mcp-integration.md — how a downstream host (mcp-vfp9sp2-toolchain) wraps the synchronous public API.
- docs/threat-model.md — protected/transferable assets, trust boundaries, attack/failure classes.
- docs/pseudonymization-vs-anonymization.md — the pseudonymized-vs-anonymous distinction.
- docs/public-models-1.0.md — public model contract.
- docs/errors-1.0.md — public error contract.
- docs/public-contract-1.0.md — frozen 1.0 contract matrix and semantic-versioning rules.
- docs/release-acceptance.md — the one-command REQ-P8-002 release-acceptance entry point and evidence manifest.
- docs/vault-protection.md — protected vault security notes.
- docs/migration-1.0-clean-slate.md — 1.0 clean-slate reset.
Development
python -m pip install -e ".[dev]"
python -m pip install -r requirements/p0-dbfbridge-tested.txt
python -m pytest
python -m build
The P0 acceptance environment uses the exact public dbfbridge artifact pinned
in requirements/p0-dbfbridge-tested.txt (REQ-P0-002); the runtime metadata
range stays dbfbridge[write]>=1.1.0,<2.
P0 boundary evidence lives in tests/ (dependency contract, public dbfbridge
capability contract, architecture boundary, root public API regression) and is
proven from a clean environment by .github/workflows/p0-package-boundary.yml.
Operational release evidence (reproducible distributions, SBOM, tamper-evident
manifest) is produced by tools/build_release_evidence.py and validated by
.github/workflows/p7-release-evidence.yml.
1 maintainer

Metadata
1 maintainer
Release files for dbf-anonymizer 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| dbf_anonymizer-1.0.0.tar.gz | 703.9 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| dbf_anonymizer-1.0.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 1.0 MB
Release files / dbf_anonymizer-1.0.0.tar.gz
| Download URL | dbf_anonymizer-1.0.0.tar.gz |
|---|---|
| Size | 703.9 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
602f47056511b731e47a75b867e70908f79011d1360db2432e4cdbfaf44a2d95
|
|
BLAKE2b-256 checksum How to use checksums |
9b06e6846c45ba0b506bfbb94242c48f067d0f26fb6907d4fca5095ea380e369
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency logRelease files / dbf_anonymizer-1.0.0-py3-none-any.whl
| Download URL | dbf_anonymizer-1.0.0-py3-none-any.whl |
|---|---|
| Size | 302.9 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f26a97120d55756212b3bedc25a1e95dbc2920c89a09fa20cdf4a9e6aee7c5aa
|
|
BLAKE2b-256 checksum How to use checksums |
4f22c4ce8573b72a5e0e20287fc0bb8bb2e187ac5adb66c419785076c54fb740
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.12.9
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency log












