
depsweep


Find supply-chain risks in your npm and pip dependency files.
Most malicious packages don't need you to call them. They run a script the
moment you npm install, or they ride in on a name one letter off a package you
trust. depsweep reads package.json, requirements.txt, lockfiles and installed
node_modules manifests and flags the risks you can see without running anything.
Runs offline. No registry calls, nothing leaves your machine.
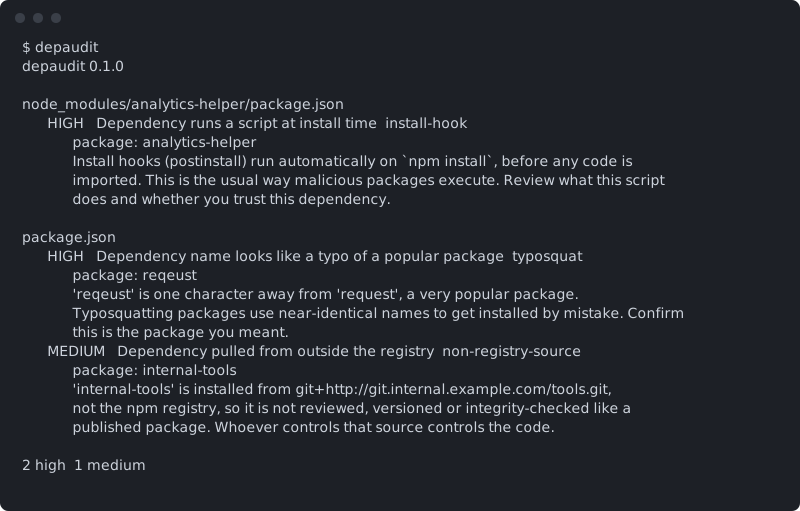
Install
pip install depsweep
Usage
depsweep                 scan the current directory
depsweep path            scan a directory
depsweep --min high      only high and critical findings
depsweep --json          machine-readable output
Exit status is 0 when clean, 1 when there is a finding at or above the fail
level (--fail-on, default high), and 2 on error.
pre-commit
repos:
  - repo: https://github.com/ReazGan/depsweep
    rev: v0.1.0
    hooks:
      - id: depsweep
GitHub Action
- uses: actions/checkout@v4
- uses: ReazGan/depsweep@v0.1.0
What it checks
| Check | Severity | What it finds |
|---|---|---|
install-hook |
high | A dependency under node_modules that runs a script on install (preinstall/install/postinstall). The usual malware entry point. |
typosquat |
high | A dependency whose name is one edit (incl. a letter swap) from a very popular package. |
insecure-source |
high | A dependency or lockfile entry fetched over plain http. |
non-registry-source |
medium | A dependency pulled from a git repo or URL instead of the registry. |
A project's own postinstall is not flagged (you wrote it); only dependencies
are. Known real packages that happen to sit next to a popular name (tslint,
preact, ...) are not reported as typosquats.
Run it after npm install to see dependency install hooks; run it on the repo
alone to check manifests and lockfiles.
License
MIT
1 maintainer

Metadata
1 maintainer
Release files for depsweep 0.1.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| depsweep-0.1.0.tar.gz | 9.6 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| depsweep-0.1.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 19.0 kB
Release files / depsweep-0.1.0.tar.gz
| Download URL | depsweep-0.1.0.tar.gz |
|---|---|
| Size | 9.6 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
bf69f33717bcfdd09a3b78e1834119b61bc43206dabfd9d24ce98905523dc289
|
|
BLAKE2b-256 checksum How to use checksums |
f451f391e2c428b1bcaa009ebd79fdcce88a527f523344233e56f0c224236541
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency logRelease files / depsweep-0.1.0-py3-none-any.whl
| Download URL | depsweep-0.1.0-py3-none-any.whl |
|---|---|
| Size | 9.4 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
5fa5f756bffc6e798b79bdf6795f33e45c0e605d8dee062e046a81f71ed4b84b
|
|
BLAKE2b-256 checksum How to use checksums |
c37106c44d6b5a8857b84d09b4a6b7179036baf9cb9d05d60f5da333142d27fb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 5, 2026.
Transparency log












