
An API time machine for Python libraries, built for coding agents.



When an agent hits ImportError, AttributeError or "unexpected keyword argument" in a fast-moving library, one call to DepTime says what changed, in which release, and what to use instead. Answers are computed from static diffs of every indexed release, not from docs or model memory.
Free, open source (MIT), and local: your code and errors never leave your machine.
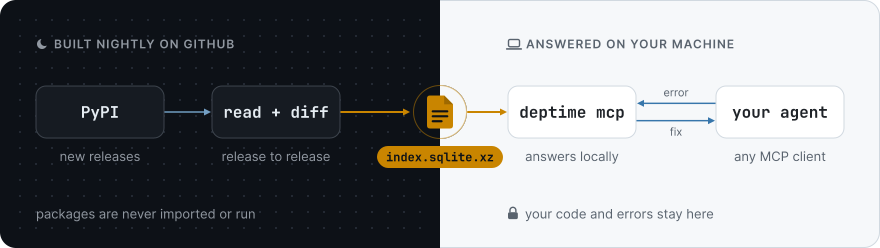
Every night, GitHub Actions reads each new release's public API with griffe, which parses the source without running it, diffs it against the previous release, and publishes the result as one file, index.sqlite.xz, on this repo's Releases. On your machine, deptime mcp checks that file's sha256 and schema before swapping it in, then answers every question locally in milliseconds. The full design is in docs/04-architecture.md, and the decisions are in docs/adr/.
TypeError: Client.__init__() got an unexpected keyword argument 'proxies'
{
  "symbol": "httpx.Client.__init__(proxies)",
  "issue": "param_removed",
  "installed_version": "0.28.1",
  "last_version_with": "0.27.2",
  "first_version_without": "0.28.0",
  "deprecated_in": "0.26.0",
  "replacements": [
    {"target": "proxy", "confidence": 0.8, "source": "deprecation_message"},
    {"target": "mounts", "confidence": 0.79, "source": "deprecation_message"}
  ],
  "pin_to_restore": "httpx<=0.27.2",
  "confidence": "high"
}
That's the real explain_error answer from the published index, trimmed. The full answer also quotes the deprecation message DepTime found in httpx's own source, and adds a one-sentence explanation for your agent to pass on.
Status: alpha. The prebuilt index is rebuilt nightly. Known gaps are tracked in BACKLOG.md.
Install
Requires uv.
# Claude Code. Cursor, Codex, VS Code and Claude Desktop take the same
# command (uvx deptime mcp) in their MCP config.
claude mcp add deptime -- uvx deptime mcp
On first launch DepTime downloads its prebuilt index (one file from this repo's GitHub Releases) in the background, then checks for a newer one at most once a day. Set DEPTIME_OFFLINE=1 to never touch the network.
Claude Code users can also install the plugin in integrations/claude-code with /plugin marketplace add cschmertz/deptime, then /plugin install deptime@deptime. It adds a skill and a local hook that suggests DepTime when a Python version-change error appears in a command's output.
First launch timing out? uvx installs DepTime the first time a client starts it. On macOS with an x86_64 uv (an Intel Mac, or Intel Homebrew on Apple silicon), one dependency, cryptography, has no prebuilt wheel and is compiled, which can take longer than a client waits for a server to start. Run uvx deptime --help once beforehand.
Client compatibility
Checked 2026-11-05 with deptime 0.1.4 (details):
| Client | Result |
|---|---|
| Claude Code 2.1.318 | ✅ |
| Codex CLI 0.166.0 | ✅ |
MCP Python SDK clients 1.0–1.30 and TypeScript SDK clients 1.0–1.32 (protocols 2024-11-05 to 2025-11-25), over stdio and against deptime serve |
✅ |
| Cursor, VS Code, Claude Desktop | not checked yet; they take the same uvx deptime mcp command |
Tools
| Tool | Use it when |
|---|---|
explain_error(traceback, installed_versions?, pip_freeze?) |
An import or call into a library just failed |
symbol_history(package, path) |
Before trusting an API you remember |
check_symbols(package, version, symbols[{path, kwargs}]) |
Pre-flight check of the symbols and kwargs you're about to use |
diff_versions(package, from_version | date, to_version?, used_symbols?) |
Upgrading, or "what changed since my training cutoff?" |
coverage() |
What's indexed (52 fast-moving packages: AI/agent stack + libraries with known breaking changes) |
Every answer carries evidence and a confidence level. If a package isn't covered, DepTime says so instead of guessing. The contracts are in docs/03-product-spec.md.
CLI
uvx deptime explain --installed httpx==0.28.1 < traceback.txt
uvx deptime history httpx Client.__init__
uvx deptime check httpx 0.28.1 'httpx.Client:proxies,proxy'
uvx deptime diff httpx 0.27.2 0.28.1
uvx deptime diff pydantic 2024-06-01              # everything since a date
uvx deptime index status | pull
Hosting (optional)
Local mode covers coding agents. For web clients that only accept a URL, run deptime serve (MCP at /mcp, JSON at /v1/*) on any container host. The repo includes a Dockerfile and fly.toml, and the server applies anonymous rate limits. See docs/05-self-hosting.md.
Prior art and credits
- griffe does the static analysis.
- since-cutoff diffs your pinned dependencies against a model's training cutoff, locally and on demand. DepTime differs by shipping a prebuilt cross-version index and starting from a traceback.
- Context7 and Ref serve version-specific docs. DepTime answers symbol-level "when and what replaced it" questions.
Contributing
The most useful contributions are wrong-answer reports, which become benchmark cases. See CONTRIBUTING.md. Development setup:
uv sync && uv run pytest
# build a small local index from real PyPI wheels
uv run deptime ingest httpx --versions 0.27.2 0.28.1
Docs
Product spec · Architecture · Self-hosting · Risks & spikes · Privacy & security
License
1 maintainer

Metadata
1 maintainer
Release files for deptime 0.1.5
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| deptime-0.1.5.tar.gz | 222.7 kB | With provenance | Details for deptime-0.1.5.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| deptime-0.1.5-py3-none-any.whl | Python 3 | none | any | Details for deptime-0.1.5-py3-none-any.whl |
Total release size: 371.2 kB
Release files / deptime-0.1.5.tar.gz
| Download URL | deptime-0.1.5.tar.gz |
|---|---|
| Size | 222.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
cd0ab04e60c0874b5ffd52e5d209c3d32a1f47d6aa1b7521b537b531706d3d2b
|
|
BLAKE2b-256 checksum How to use checksums |
7a475c7f6e2481b6343837e31997aafcffc69cb2c929415a1e3051ff8d835658
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / deptime-0.1.5-py3-none-any.whl
| Download URL | deptime-0.1.5-py3-none-any.whl |
|---|---|
| Size | 148.6 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
98aa4a603b003e17b82b56b11f6c30160acd6a2a1c77a93cfaa3ba04e3c7df4a
|
|
BLAKE2b-256 checksum How to use checksums |
2fe55dd29e21d8beddf7fbd9b69f6b1db27a6d321bee54d4d42e097ac746c8d2
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logSecurity for deptime 0.1.5
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for deptime-0.1.5.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














