
dev-ready


繁體中文導覽:https://github.com/MoofonLi/dev-ready/blob/main/README.zh-TW.md
Scaffold a production-grade, AI-development-ready FastAPI + React project in one command:
uvx dev-ready init my-app
What a generated project receives
| Layer | Contents |
|---|---|
| Base | Every generated project is FastAPI, React, PostgreSQL, and Docker Compose at a pinned commit of fastapi/full-stack-fastapi-template. |
| Canonical Content | AGENTS.md and skills under .agents/skills/. Standard-compliant agents read those paths directly. |
| Engineering Flow | One named method, chosen first: mattpocock, superpowers, or addyosmani. --yes selects mattpocock. |
| Enhancements | Optional items by Category — Dev, Security, Quality, Design, Token Optimize. The Default Set selects none. |
| Agent Targets | Skill Links at each selected agent's native path, plus a .dev-ready.json stamp. Links are machine-local; upgrade recreates them. |
Quickstart
uvx dev-ready init my-app
cd my-app
Then ask your coding agent to run /setup-project before the first start.
Engineering Flows
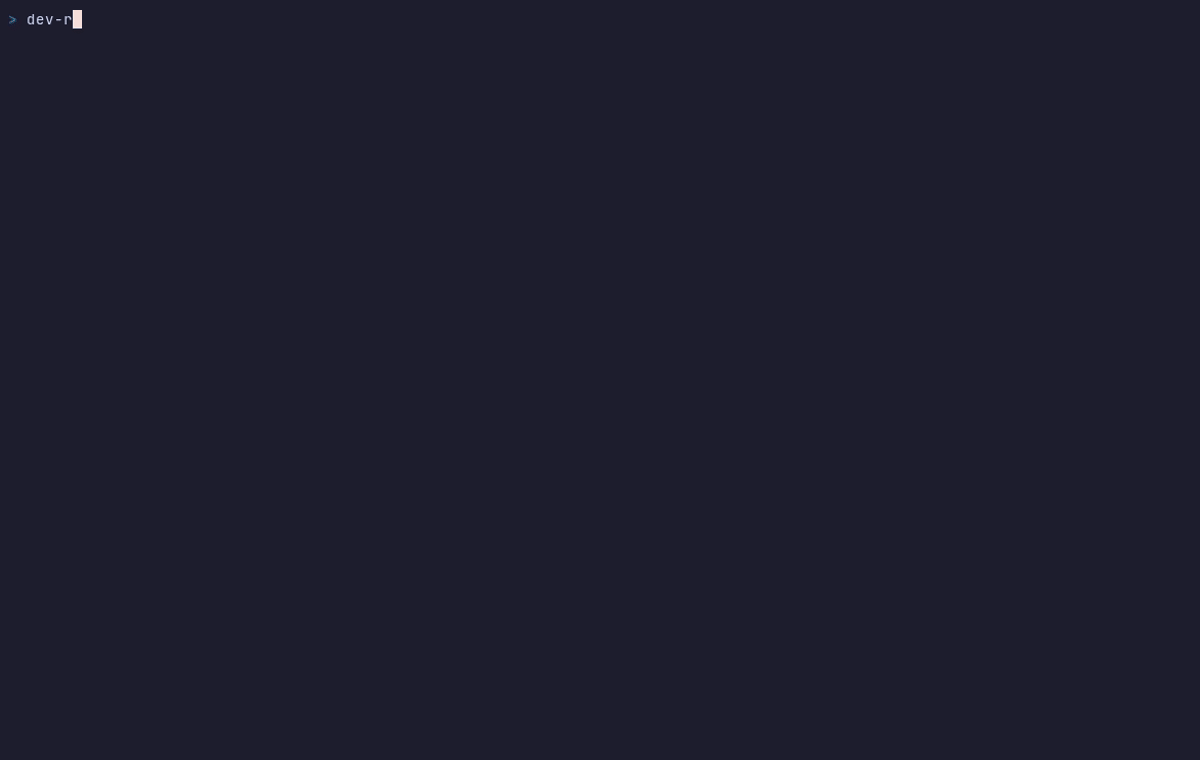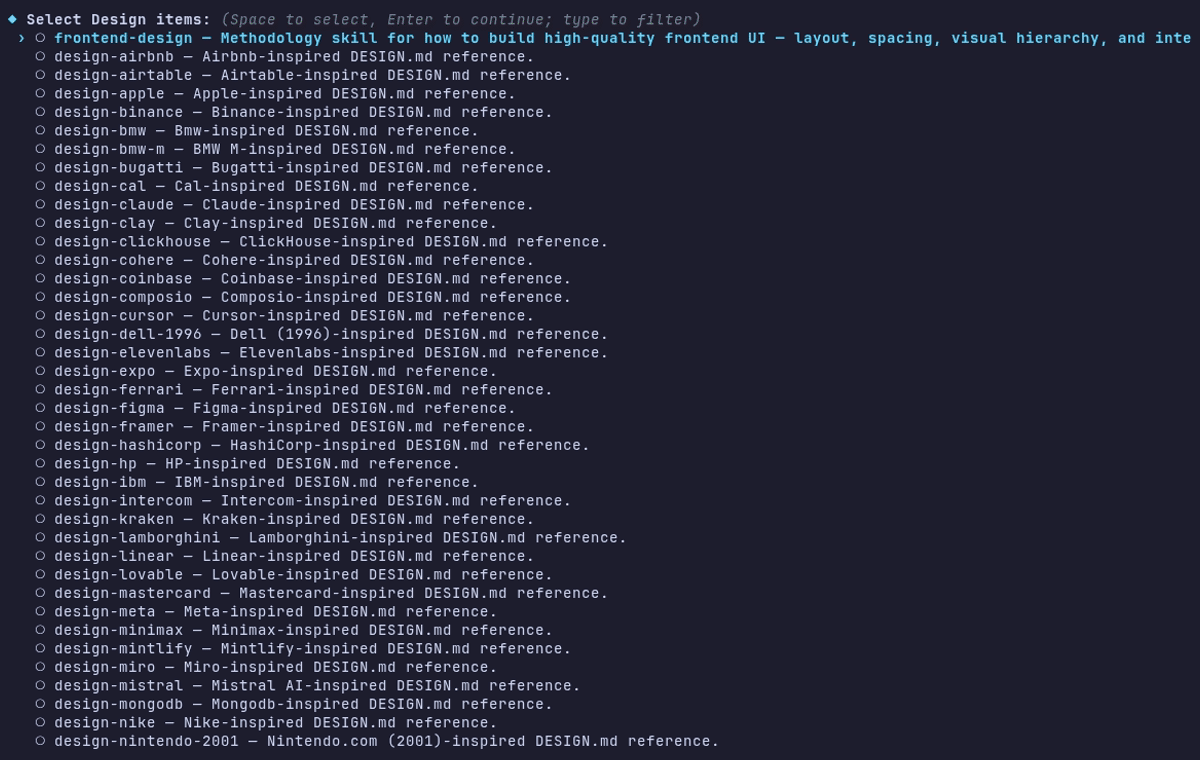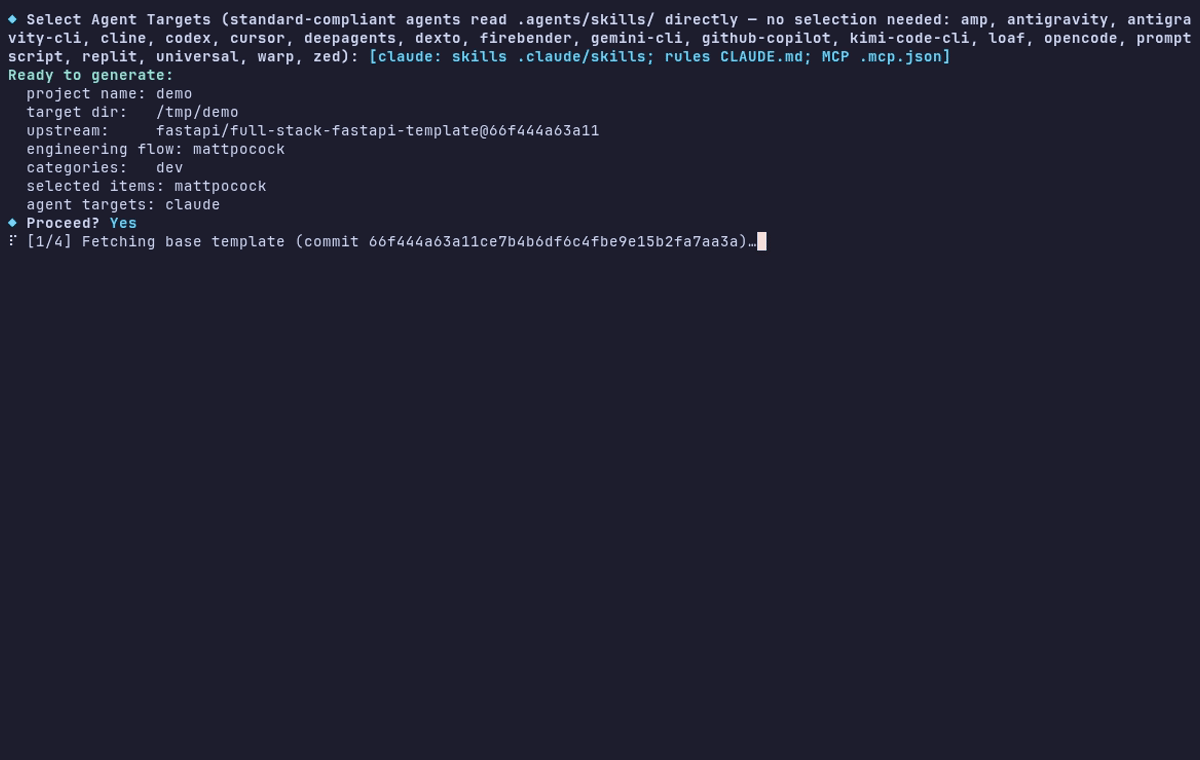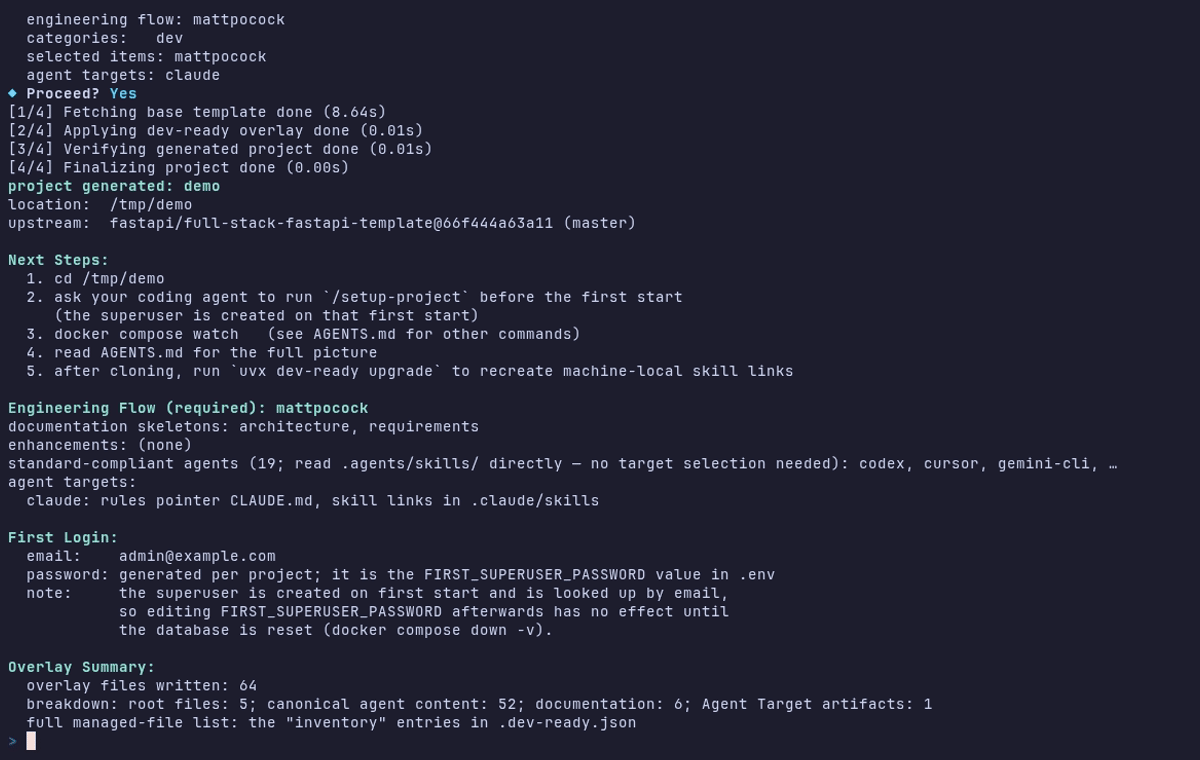
Interactive init shows this comparison, then Category prompts, a confirmation, fetch → overlay → verify → finalize, and a report.
Matt Pocock's skills — A user-driven Engineering Flow whose steps stay in one working session.
- Choose this flow when you want to start each
chainentry yourself. - Choose it when the work's shape needs
grill-with-docs,grilling, ordomain-modelingbefore specification. - Choose it when one session should carry the work through
to-spec,to-tickets, andimplement.
Superpowers — A model-driven Engineering Flow whose implementation can fan out across fresh subagents.
- Choose this flow when its model-driven
invocationshould start each chain entry after setup. - Choose it when implementation should fan out through
subagent-driven-developmentorexecuting-plans. - Choose it when
verification-before-completionshould run before work is declared complete.
Addy Osmani's Agent Skills — A model-driven Engineering Flow spanning specification, implementation, production readiness, and shipping.
- Choose this flow when
spec-driven-developmentshould produce a written spec before any code exists. - Choose it when the work runs to production and wants
security-and-hardening,performance-optimization, andobservability-and-instrumentationbeside the build steps. - Choose it when its
chainshould end atshipping-and-launchrather than at a finished branch.
Requirements
Python 3.12+, git, network to github.com during generation, and a filesystem that can hold links unless no Agent Target is selected. Docker is only needed to run the generated project.
Install the agent skill
npx skills add MoofonLi/dev-ready --skill dev-ready
The source is skills/dev-ready/SKILL.md. Inspect discoverable skills first:
npx skills add MoofonLi/dev-ready --list
Then ask your agent: “Scaffold a FastAPI project with dev-ready named my-app.” Also as a plugin: /plugin marketplace add MoofonLi/dev-ready then /plugin install dev-ready@dev-ready, or codex plugin marketplace add MoofonLi/dev-ready. Problems: open an issue.
Development
uv sync --dev
uv run pytest
uv run ruff check .
See AGENTS.md. Full CLI contract: docs/cli-spec.md. Version overview: v0.13 overview.
License
MIT — see LICENSE. Generated projects include third-party content; see THIRD_PARTY_NOTICES.md.
1 maintainer

Metadata
1 maintainer
Release files for dev-ready 0.13.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| dev_ready-0.13.0.tar.gz | 2.6 MB | With provenance | Details for dev_ready-0.13.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| dev_ready-0.13.0-py3-none-any.whl | Python 3 | none | any | Details for dev_ready-0.13.0-py3-none-any.whl |
Total release size: 3.7 MB
Release files / dev_ready-0.13.0.tar.gz
| Download URL | dev_ready-0.13.0.tar.gz |
|---|---|
| Size | 2.6 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
641e429790605ece3fc4c949a80b0a4f5d2f1fa7b63208268cfd4f01f1dcf540
|
|
BLAKE2b-256 checksum How to use checksums |
c84476d78697000fe51a4d063f017c16572dbcbf41c32c662e3d28e8c4e6ef5b
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency logRelease files / dev_ready-0.13.0-py3-none-any.whl
| Download URL | dev_ready-0.13.0-py3-none-any.whl |
|---|---|
| Size | 1.2 MB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
80fbed8bab9c31665e90c61fc26bd099f6067de7477ec669e01291e90bb5b5a9
|
|
BLAKE2b-256 checksum How to use checksums |
2389f1d359a1994eea94432b093b4504d7d2996bb530c8b8d8541c19b7b9bf48
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency logSecurity for dev-ready 0.13.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for dev_ready-0.13.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Aug 31, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














