
deviant-scan
Find the one thing in your code that breaks the pattern.
Deviant learns your project's own conventions, flags the exceptions, and shows the git history you need to judge them. You write no rules, and finding the exceptions needs no AI, no API key and no network.
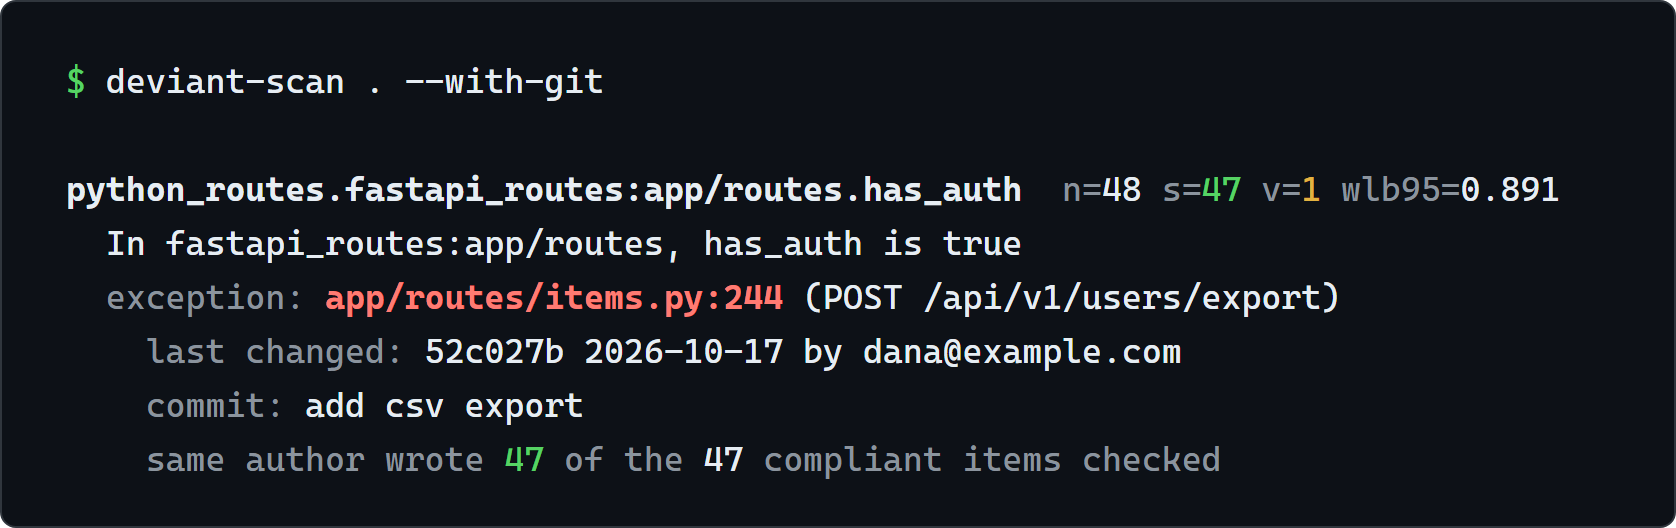
Picture a project with 48 API routes. 47 of them check who is calling. The 48th doesn't, and it exports every user's data. Nobody noticed. Deviant counts what your code already does, picks out the rare item that breaks the pattern, and shows the git history behind it.
Use it
pip install deviant-scan
deviant-scan path/to/your/project --with-git
Or without installing it: uvx deviant-scan path/to/your/project --with-git.
It checks FastAPI routes and GitHub Actions workflows today. Add --json for machine-readable
output. Everything runs on your machine. It reads your files and never runs your code.
In Claude Code
A plugin judges each exception as a bug, intentional or unsure, with proof:
/plugin install deviant --marketplace ImalkaPerera/deviant
Learn more
Licensed under either the MIT license or the Apache License 2.0, at your option.
1 maintainer

Metadata
1 maintainer
Release files for deviant-scan 0.3.2
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| deviant_scan-0.3.2.tar.gz | 103.0 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| deviant_scan-0.3.2-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 156.1 kB
Release files / deviant_scan-0.3.2.tar.gz
| Download URL | deviant_scan-0.3.2.tar.gz |
|---|---|
| Size | 103.0 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b78c0c50da3545745cea0b7f550dd4883a0d9d60033ceb6fb9b750763b11412b
|
|
BLAKE2b-256 checksum How to use checksums |
4cfca740b5ed17af7a01d5393be17262dc7805a5a42f3ea99e984d077832572c
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logRelease files / deviant_scan-0.3.2-py3-none-any.whl
| Download URL | deviant_scan-0.3.2-py3-none-any.whl |
|---|---|
| Size | 53.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
579a766ad9256cf3cd674ef07bc0cea645b80661848c5d90cee1a66e0c5c131b
|
|
BLAKE2b-256 checksum How to use checksums |
5a7347537c7663124608f59afc4b97cefde77566f227ef8132722541c61f4e64
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logSecurity for deviant-scan 0.3.2
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for deviant_scan-0.3.2.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 21, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.














