
django-launch-editor



Open files from Django’s debug error page in your editor.
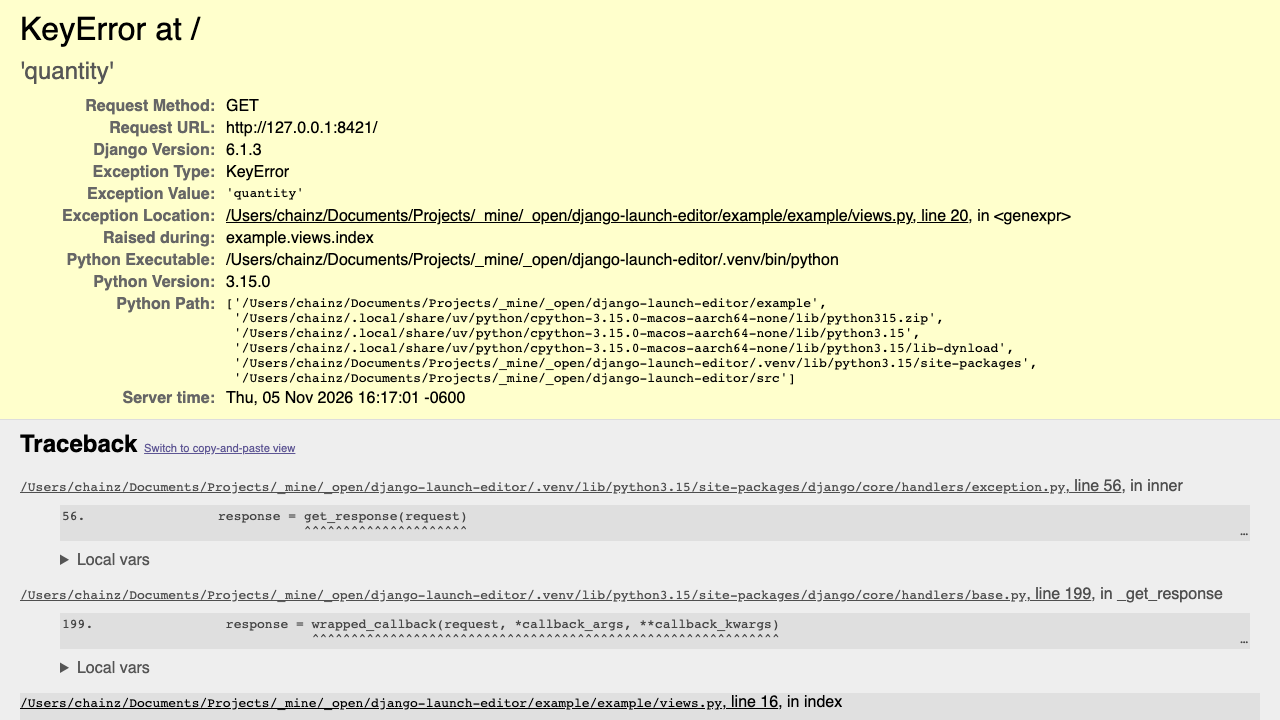
Makes the file locations on Django’s debug error page, like “/path/to/views.py, line 8”, into links that open the file at that line in your editor, using launch-editor-py.
Improve your Django and Git skills with my books.
Requirements
Python 3.11 to 3.15 supported.
Django 5.2 to 6.1 supported.
Installation
Install with pip:
python -m pip install django-launch-editorSet Django’s exception reporter class, in your settings file:
DEFAULT_EXCEPTION_REPORTER = "django_launch_editor.LaunchEditorExceptionReporter"If you already use a custom exception reporter, make it subclass LaunchEditorExceptionReporter.
Include the app URLs in your root URLconf:
from django.urls import include, path

urlpatterns = [
    ...,
    path("__launch_editor__/", include("django_launch_editor.urls")),
]
You can use another prefix if required.
That’s it! 🎉
Trigger an error while you have DEBUG = True, and click the file location of any traceback frame, or template error, to open it in your editor. Where Python knows it, the editor opens at the column of the expression that failed, too.
Editor selection
django-launch-editor attempts to detect a running non-terminal editor with launch-editor-py. If none is detected, it falls back to showing a dialog for copying the clicked file path to your clipboard.
Because django-launch-editor runs within the Django server, it can only launch an editor when you run Django on your development machine, not in a container or on a remote server. Similarly, it must skip terminal editors like Vim, since they would take over the terminal running Django.
For information on how the editor is picked, or how to override it, see the launch-editor-py documentation.
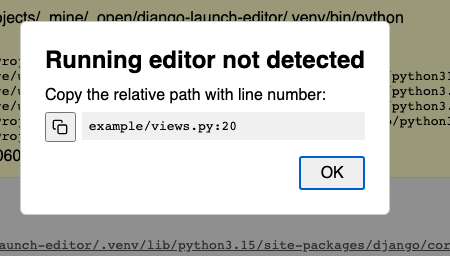
If no editor is found, django-launch-editor falls back to showing a dialog headed “Running editor not detected”, and copying the file location to your clipboard:
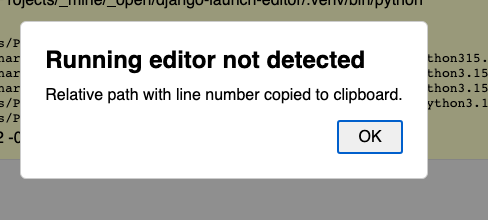
The location has the form path:line, such as myapp/views.py:8.
If the browser blocks the automatic copy, the dialog shows a copy icon button to the left of the location:
Security
Opening files runs a program on the server, so the package takes several precautions:
The whole process only works when DEBUG is True.
Links are never added to error emails.
The view only accepts POST requests from pages on the same origin, checked with the Sec-Fetch-Site or Origin headers that browsers send. This blocks cross-site request forgery without relying on CsrfViewMiddleware’s cookie, which may not be set on the error page.
The view doesn’t accept arbitrary file paths. Instead, each link carries a token, signed with your SECRET_KEY, for a file and line that appeared on a debug page. Tokens are only made for files that exist, and expire after 24 hours.
Example project
To try django-launch-editor, there is an example project included in the repository. Open the example/ directory, follow the instructions in its README, and try it out.
How it works
LaunchEditorExceptionReporter extends Django’s ExceptionReporter to add a small script to the HTML debug page, along with signed tokens for each traceback frame. The script turns file locations into buttons, styled as links, that POST a token to the view, which checks it and calls launch_editor().
1 maintainer

Metadata
1 maintainer
Release files for django-launch-editor 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| django_launch_editor-1.0.0.tar.gz | 11.4 kB | With provenance | Details for django_launch_editor-1.0.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| django_launch_editor-1.0.0-py3-none-any.whl | Python 3 | none | any | Details for django_launch_editor-1.0.0-py3-none-any.whl |
Total release size: 23.7 kB
Release files / django_launch_editor-1.0.0.tar.gz
| Download URL | django_launch_editor-1.0.0.tar.gz |
|---|---|
| Size | 11.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
b9ed59615fed3bbcb37cc140aca8b65d1582c5d93024651575c13524532265f6
|
|
BLAKE2b-256 checksum How to use checksums |
a97d66aaa4847c27a6cb185b57d2c962d0780744f16e4dc59dccf429747082cc
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logRelease files / django_launch_editor-1.0.0-py3-none-any.whl
| Download URL | django_launch_editor-1.0.0-py3-none-any.whl |
|---|---|
| Size | 12.2 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
94cbc2f23dbd071d6e25369716c75ad4a82fe2f8a2804e409bf8d6b5222137ce
|
|
BLAKE2b-256 checksum How to use checksums |
69f5af5e71be8fe47d9e0e2425866c28e856860de64e0a252f60b70b130e5d95
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.13
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logSecurity for django-launch-editor 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for django_launch_editor-1.0.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 5, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













