
django-mjml-templates
Email that's just another Django template. MJML is a markup that compiles
to responsive email HTML. Write it in .mjml files with {% extends %}, {% url %} and your own
tags and filters, and get back a message ready to send: the HTML, a plain-text part, a subject and
absolute links, with no Node or server needed. Swap a line in TEMPLATES and everything else
keeps rendering as normal.
Setup
uv add django-mjml-templates # or pip install
Swap the backend:
TEMPLATES = [{
    "BACKEND": "mjml_templates.django.DjangoTemplates",  # was django.template.backends.django.DjangoTemplates
    ...
}]
Only templates ending in .mjml are treated as email; every other template renders as before.
MJML is compiled by mjml-python (a prebuilt Rust port) and the
plain-text part comes from html2text.
Write an email
A Django template first ({% extends %}, {% url %}, autoescaping), then
MJML for the layout. <mj-title> is the subject.
{# templates/email/welcome.mjml #}
<mjml>
  <mj-head><mj-title>Welcome to Paperplane, {{ user.first_name }}</mj-title></mj-head>
  <mj-body>
    <mj-section><mj-column>
      <mj-text>Hi {{ user.first_name }}, your account is ready.</mj-text>
      <mj-button href="{% url 'start' %}">Get started</mj-button>
    </mj-column></mj-section>
  </mj-body>
</mjml>
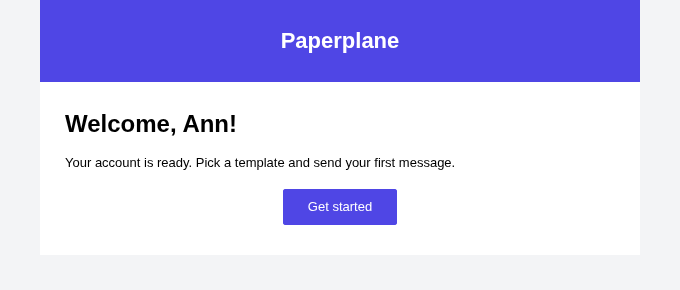
The styled version in the screenshot below
<mjml>
  <mj-head>
    <mj-title>Welcome to Paperplane, {{ user.first_name }}</mj-title>
    <mj-attributes><mj-all font-family="Helvetica, Arial, sans-serif" /></mj-attributes>
  </mj-head>
  <mj-body background-color="#f3f4f6">
    <mj-section background-color="#4f46e5">
      <mj-column>
        <mj-text align="center" color="#ffffff" font-size="22px" font-weight="bold">Paperplane</mj-text>
      </mj-column>
    </mj-section>
    <mj-section background-color="#ffffff">
      <mj-column>
        <mj-text font-size="24px" font-weight="bold">Welcome, {{ user.first_name }}!</mj-text>
        <mj-text>Your account is ready. Pick a template and send your first message.</mj-text>
        <mj-button href="{% url 'start' %}" background-color="#4f46e5">Get started</mj-button>
      </mj-column>
    </mj-section>
  </mj-body>
</mjml>
Send it
from django.template.loader import get_template

template = get_template("email/welcome.mjml")
message = template.render_email(
    {"user": user},
    request,
    to=[user.email],
)
message.send()
get_template is Django's own loader, so it finds .mjml files the same way it finds any
template, and the one it hands back also has render_email. That returns an unsent
EmailMultiAlternatives: the subject from <mj-title>, the HTML from the MJML, and a plain-text
part made for you. Attach files, set reply_to, or send it from a Celery task like any other
Django message. Links are made absolute from the request, or from MJML_BASE_URL when there isn't
one.
With the styled template, the reader gets:
Documentation
- Get started: the template, the view and a preview view
- How-to: a simple design, sending from a task, testing, a shared layout, absolute links, previewing, customising the preview
- Reference: API, plain-text fallback, preview
- Explanation: why this, how a render works, how the preview is designed
1 maintainer

Metadata
1 maintainer
Release files for django-mjml-templates 1.3.1
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| django_mjml_templates-1.3.1.tar.gz | 208.4 kB | With provenance | Details for django_mjml_templates-1.3.1.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| django_mjml_templates-1.3.1-py3-none-any.whl | Python 3 | none | any | Details for django_mjml_templates-1.3.1-py3-none-any.whl |
Total release size: 226.7 kB
Release files / django_mjml_templates-1.3.1.tar.gz
| Download URL | django_mjml_templates-1.3.1.tar.gz |
|---|---|
| Size | 208.4 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
ecd14ea01ee13189bce21d34e9a492bc37bb889051af000c9b66fa4168f27087
|
|
BLAKE2b-256 checksum How to use checksums |
fbba4138d5bc575f03580b63f382a37a94070d12d1b64b785e25f30cf5588eee
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logRelease files / django_mjml_templates-1.3.1-py3-none-any.whl
| Download URL | django_mjml_templates-1.3.1-py3-none-any.whl |
|---|---|
| Size | 18.3 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
42a9148724c62f29f1b63f86b118dbeb120edf7de7e5740d462eddd3b622bf78
|
|
BLAKE2b-256 checksum How to use checksums |
5060dbf0e51f97f3c593e0409f384f1ed051541c0f28aae4890252879f570f7f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logSecurity for django-mjml-templates 1.3.1
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
Both files in this release have been uploaded with provenance metadata.
Attestation for django_mjml_templates-1.3.1.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 18, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














