
🔍 What is Dool?
Dool is a command line tool to monitor many aspects of your Linux system: CPU, Memory, Network, Load Average, etc. It also includes a robust plug-in architecture to allow monitoring other system metrics.
Dool is a Python3 compatible fork of Dstat.
📦 Installation:
- Download the latest release archive file or clone the Git repo
- Copy
doolinto your$PATH - Copy
plugins/*to~/.dool/(optional)
✨ Usage:
dool [--preset] [--plugin] [delay]
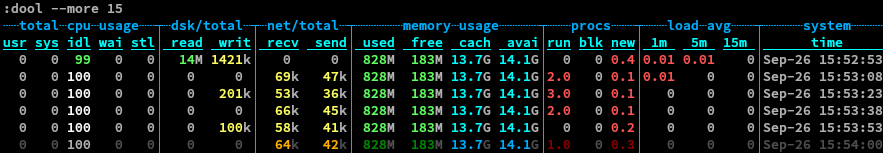
My most common usage of Dool is:
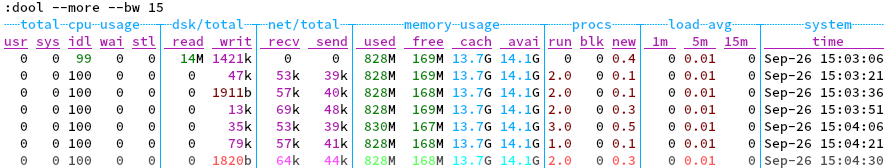
dool --more 15
which uses the --more preset and outputs data every 15 seconds. Available
presets are --defaults, --more, or --all. If no delay is specified,
Dool will default to outputting every second.
🖼️ Screenshots:
Dark mode (default)
Light mode
🔌 Plugins:
Dool ships with many plug-ins to configure the output to your taste.
dool --cpu --net --time --full # Show CPU usage, and each network interface
dool --disk -D total,sda,sdd   # Show the total disk IO, and /dev/sda and /dev/sdd
dool --net -N eth0,eth1        # Show the network traffic for eth0 and eth1
A list of available plug-ins are available when you run dool --version
🎨 Colors:
Dool expects a 256 color compatible terminal. Most modern terminal emulators
support this automatically. A --color16 option is available if you only have
a 16 color terminal.
📈 Bits vs Bytes:
One of the changes in dool is measurement of network and disk bandwidth in
bits instead of bytes. This can be confusing if you're used to seeing
lower numbers in dstat. If you would rather see bandwidth reported in bytes
you can use the --bytes option.
🧰 Other tools similar to Dool:
🌿 Pull Requests and Branches
The latest stable release (plus bugfixes) will live on the master branch.
Development of new features will occur on the next branch. Please have
pull requests target the next branch.
Various feature/bug branches may come and go as we work on more complex functionality, but those can be safely ignored.
Do you want to write your own plugin? Check out the skel plugin which should be well documented and serve as a good starting point.
👨 Team
| Username | Role |
|---|---|
| @scottchiefbaker | Primary author |
| @dagwieers | Original dstat author |
| @raylu | Pip release manager |
1 maintainer

Release files for dool 1.3.8
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | |
|---|---|---|---|
| dool-1.3.8.tar.gz | 83.5 kB | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| dool-1.3.8-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 220.2 kB
Release files / dool-1.3.8.tar.gz
| Download URL | dool-1.3.8.tar.gz |
|---|---|
| Size | 83.5 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
36d3ddb6022697c4fa78320dc5fbd139da7e6e63c550c1dd7b992914348218c6
|
|
BLAKE2b-256 checksum How to use checksums |
3c274216346e7cee341b0697a6f9d8408ccce05b27d6c87dd735a3700bafbc9f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 4, 2025.
Transparency logRelease files / dool-1.3.8-py3-none-any.whl
| Download URL | dool-1.3.8-py3-none-any.whl |
|---|---|
| Size | 136.8 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
468a1ceea156820c3a929daa8d2b98296dcc78dfd619fd57633d1cf887fddb73
|
|
BLAKE2b-256 checksum How to use checksums |
02cf975b0e133bd3fe751f959f7ed3d70b98f86dfc314a54d05a3c8644babe6f
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.7
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Sep 4, 2025.
Transparency log













