
envira
Set up a development machine from a declarative catalog: zsh with oh-my-zsh and the mzz-ys theme, language toolchains (Rust, Go, Node.js, Python), modern terminal tools, editors, coding agents and monitors. About 100 tools and 20 configs.
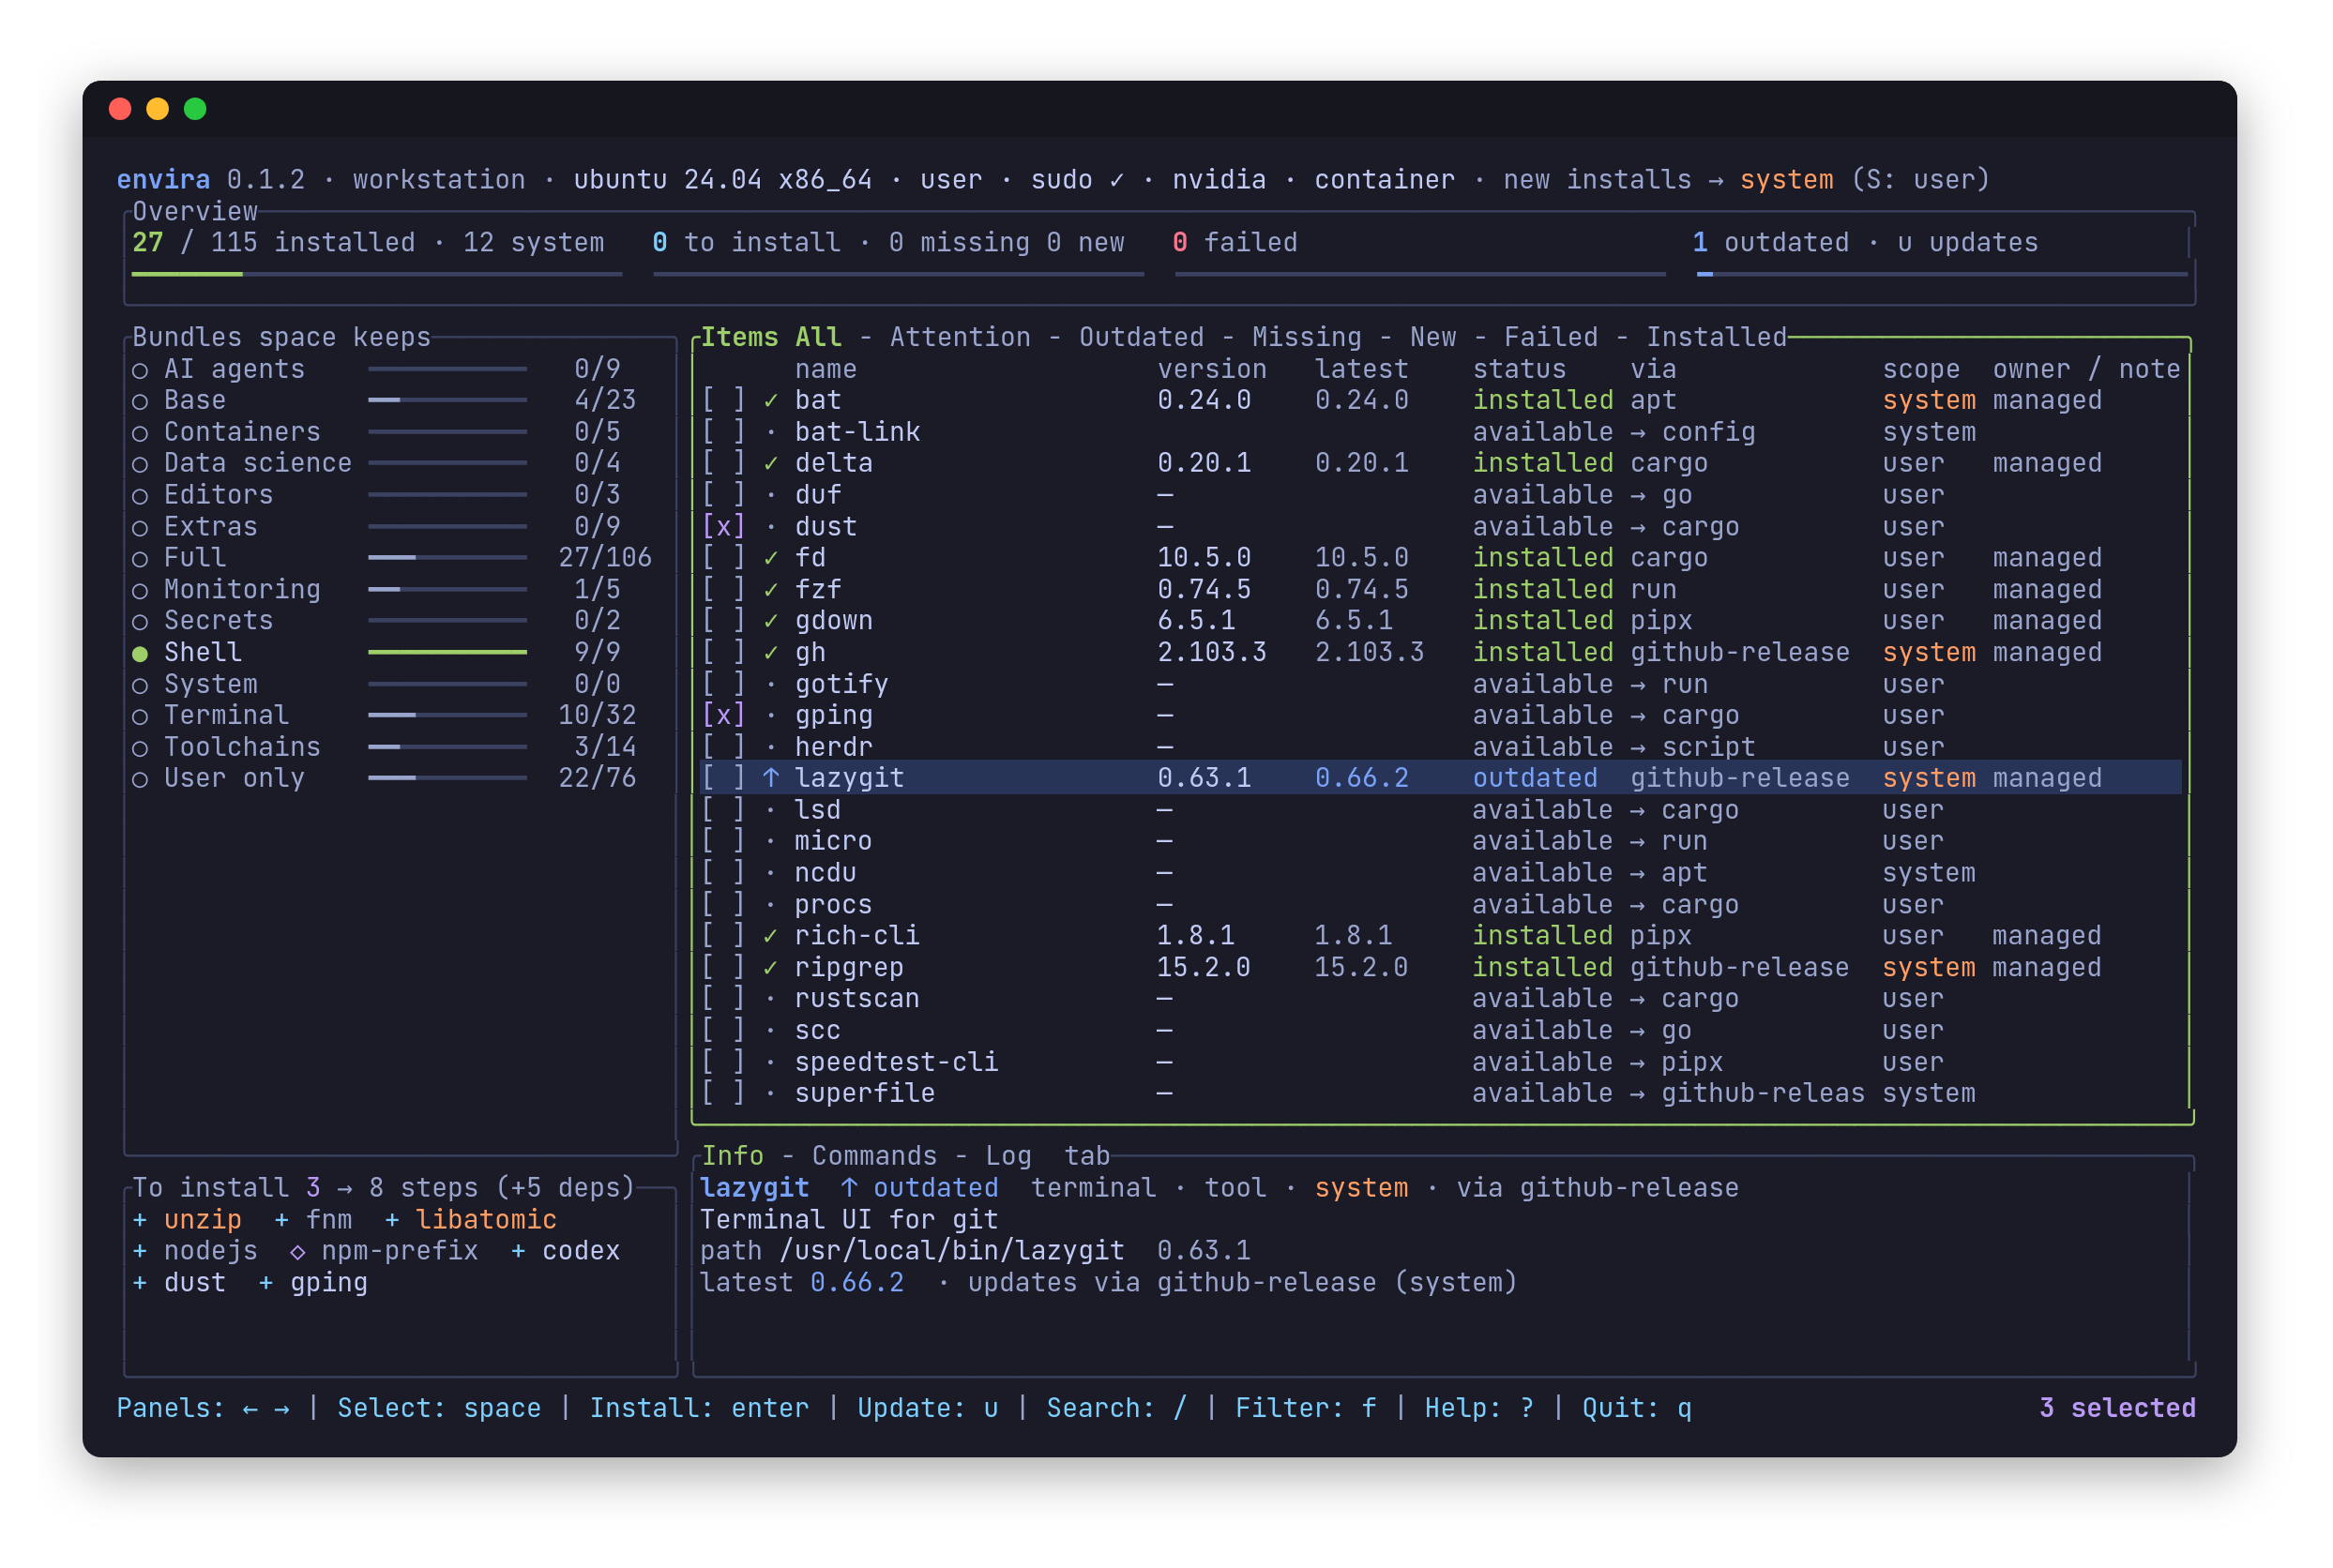
envira shows what is installed, missing, outdated or drifted, installs what is missing with its dependencies, updates tools in place, and applies or reverts configs. It runs as a TUI or as plain commands for scripts and Dockerfiles.
- Linux x86_64 and aarch64: Ubuntu/Debian, Fedora/RHEL, Arch/Manjaro, openSUSE. A single static binary with no dependencies.
- macOS on Apple Silicon, with Homebrew.
- With or without sudo: without it, envira picks user-scope routes.
Install
# install into ~/.local/bin (checks its SHA-256) and open envira
curl -fsSL https://boot.controlnet.space/envira | bash
# install and run a command instead, e.g. in a Dockerfile or CI (no terminal needed)
curl -fsSL https://boot.controlnet.space/envira | bash -s -- install full -y
# or from PyPI
pipx install envira        # or: uv tool install envira
# or from crates.io: the release binary, or a build from source (Rust 1.93+ and a C compiler)
cargo binstall envira      # or: cargo install --locked envira
envira self-update updates envira itself, the same way it was installed (release binary,
pipx, uv, pip or cargo). envira mentions a newer release after commands and in the TUI header
(U there updates it); it never updates on its own. ENVIRA_NO_UPDATE_CHECK=1 turns the
check off, and it is skipped in CI.
Use
envira                     # the TUI: pick bundles, review the plan, watch it run
envira status              # what is installed, missing, outdated or drifted
envira install full        # a bundle: installs it, and this machine keeps it
envira install             # later: whatever the kept bundles miss (new catalog items too)
envira install bat yazi    # some tools or configs, with their dependencies (not kept)
envira plan                # what `envira install` would do, without doing it
envira update              # update outdated tools in place
envira retry               # retry what failed or was blocked in the last run
envira self-update         # update envira itself (--check, --version 0.1.1 to go back)
envira log / explain <id>  # logs of the last run; why an item has its status
envira doctor              # machine facts, catalog layers, PATH, shell integration
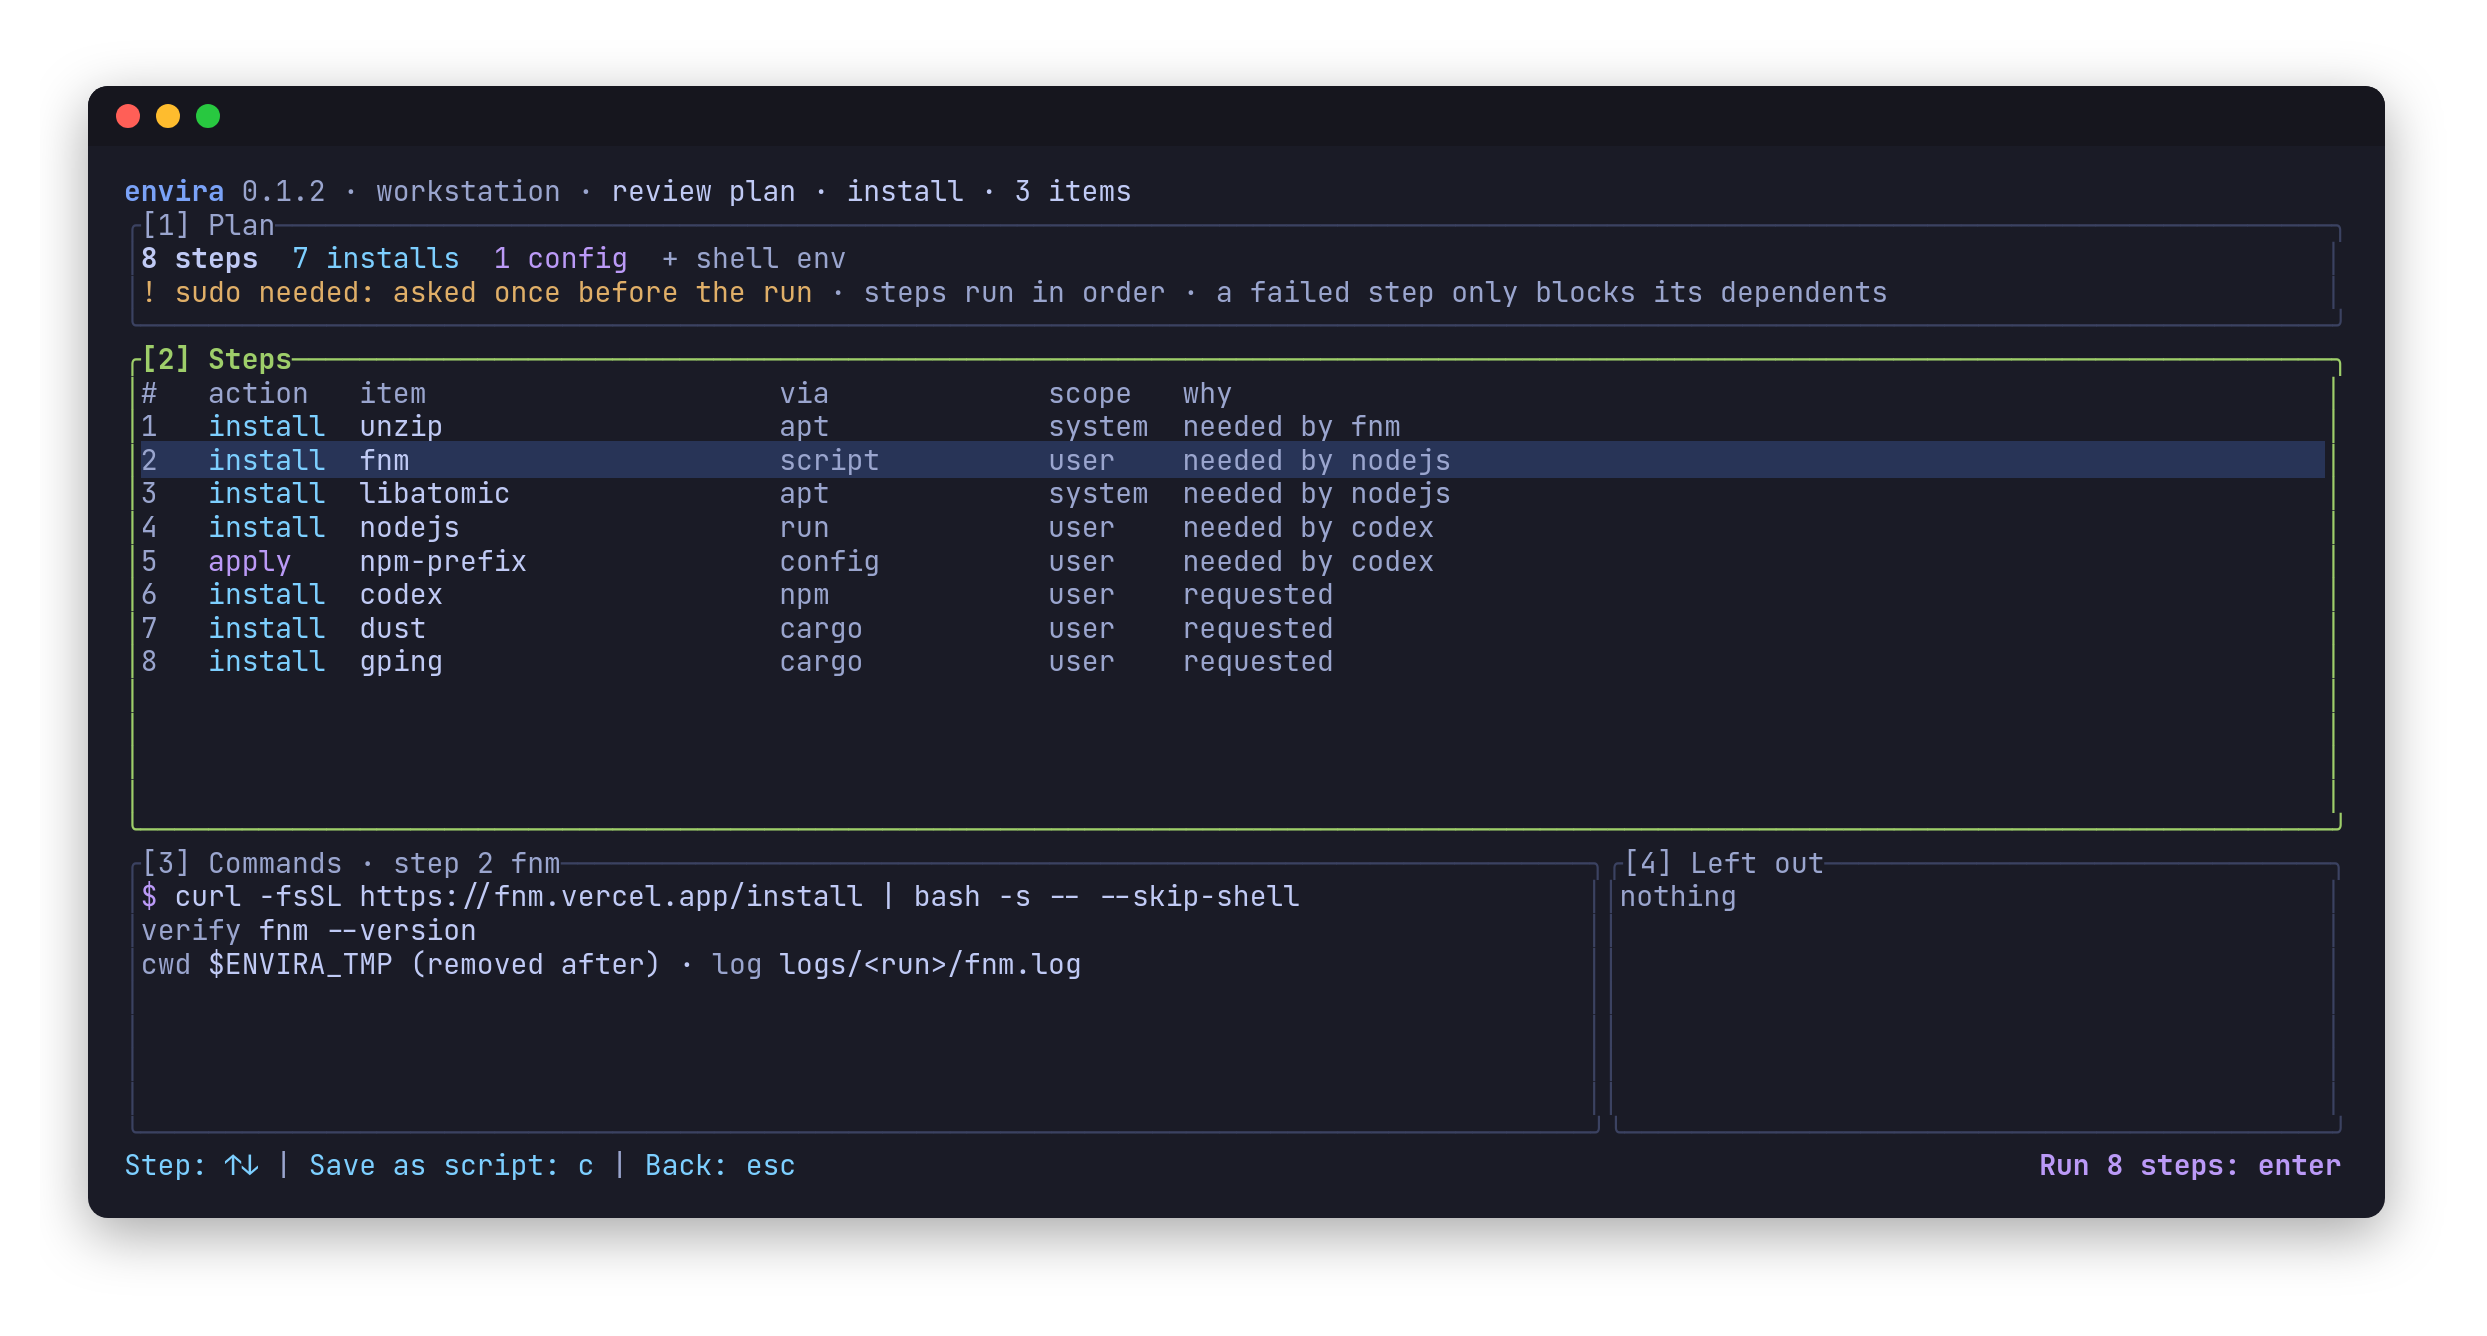
Before anything runs, the plan lists each step, why it is there, and the exact commands:
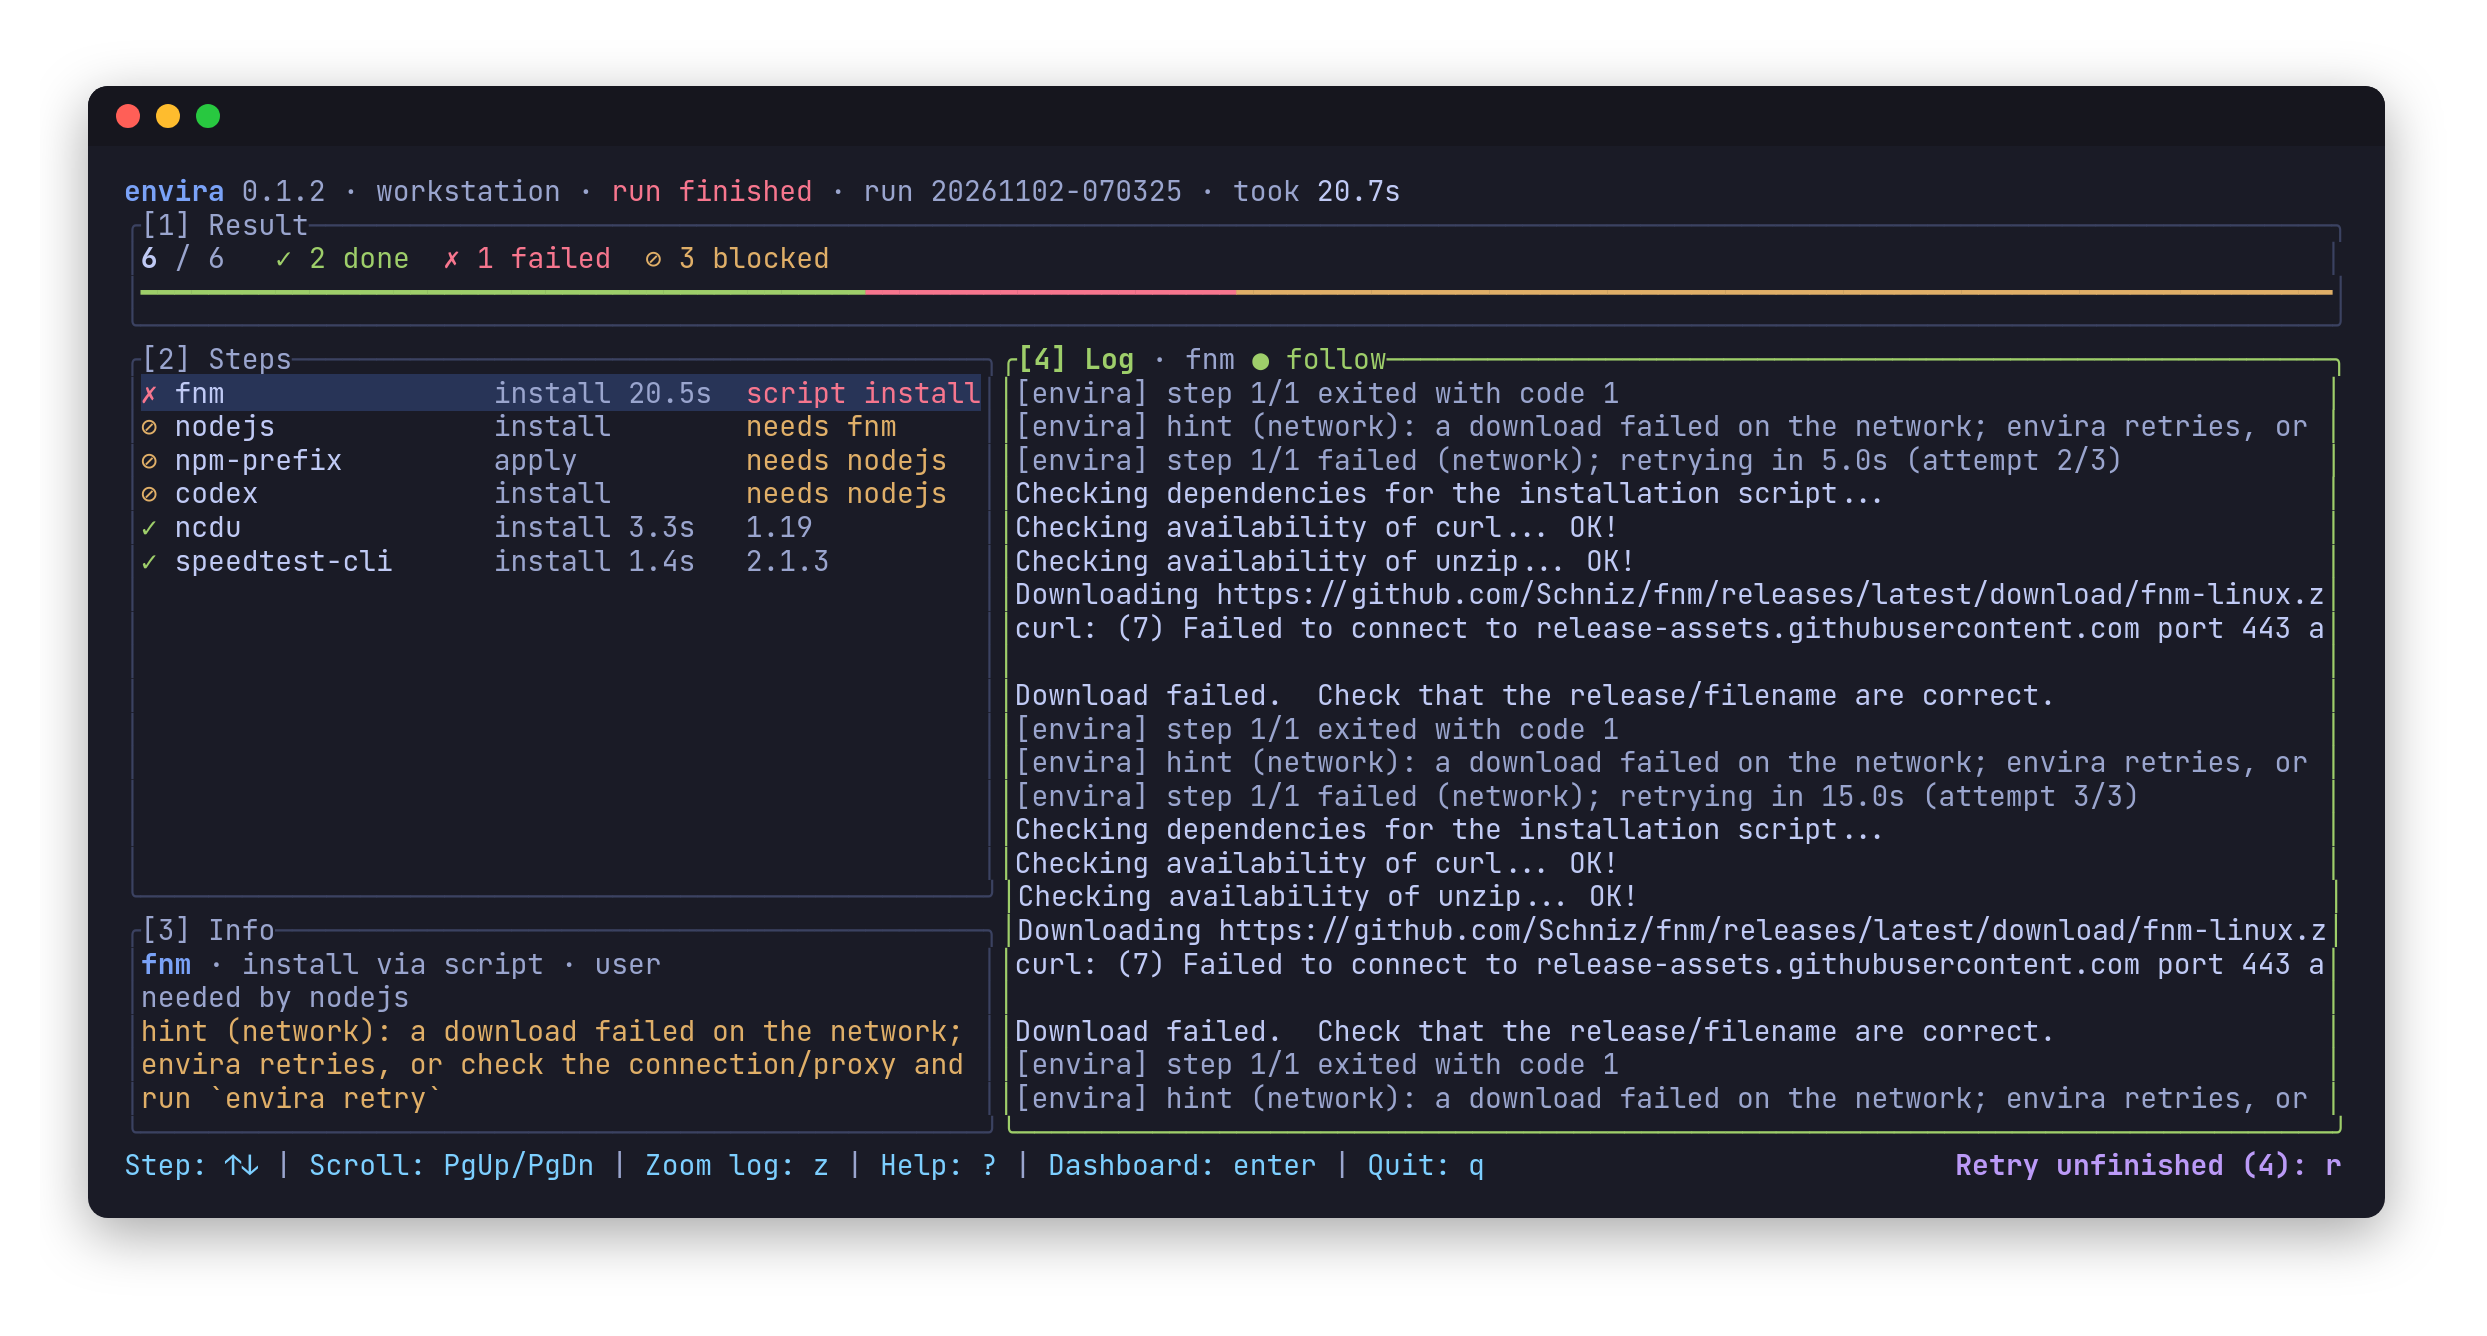
A failed step only blocks what depends on it. Network failures are retried, and r (or
envira retry) runs what is left once the cause is fixed:
Bundles (envira install <bundle>):
| Bundle | What it covers |
|---|---|
full |
Everything the legacy run.sh sets up (all bundles below except extras) |
user |
What the legacy run_user.sh sets up without sudo |
base |
Distribution packages every machine gets |
shell |
zsh, oh-my-zsh, theme, plugins, tmux and git settings |
toolchains |
Rust, Go, Node.js, Python and JavaScript toolchains |
terminal |
Daily terminal tools (bat, fzf, lazygit, ripgrep, yazi, zoxide, …) |
editors |
Neovim, clipboard bridge and LaTeX language server |
ai-agents |
Coding agents and their settings |
monitoring |
System, GPU and network monitors |
containers |
Docker, its setup and container tools |
data-science |
Miniconda, Jupyter and the Hugging Face CLI |
secrets |
Infisical CLI and ienv |
system |
Kernel and system settings |
extras |
Older or redundant tools from the legacy scripts |
- With sudo, packages go system-wide; without it, envira picks user-scope routes. When a plan
needs sudo and sudo asks for a password, envira asks for it before the plan runs (in the TUI,
a dialog over the plan), with Use user mode next to it: the plan made again without sudo.
Items that have a user-scope route take it (bat from its GitHub release into
~/.local/bininstead of apt), the others are left out, and no password is asked. An update of a tool installed system-wide puts a user-scope copy ahead of it onPATH. --scope useris user mode from the start;--scope systemuses sudo without offering it (also where envira cannot tell that sudo is allowed, e.g. a sudoers rule for one user). The password is asked on the terminal also with-yor piped input (curl … | bash); only where there is no terminal at all (CI, cron) envira plans in user mode, unless--scope systemis given.- macOS: install Homebrew first; envira uses it for most tools and does not install it itself. Without it, only tools with another route (cargo, pipx, npm, vendor scripts) are available. Linux-only items (Docker, the default-shell and sysctl configs) show as n/a. Intel Macs are not supported yet.
- envira uses the catalog published at
boot.controlnet.space/envira/catalog.toml, so new tools arrive without a new release. It is cached for an hour, and it falls back to the cache and then to the catalog built into the binary.--no-remoteuses only the built-in one. - Your own items go in
~/.config/envira/catalog.d/*.toml.envira catalog schemaprints the format, andenvira catalog checkvalidates it. - Variables for the install script:
ENVIRA_VERSION=v0.2.0pins a release,ENVIRA_INSTALL_DIRchanges where it puts the binary, andENVIRA_NO_LAUNCH=1only installs.
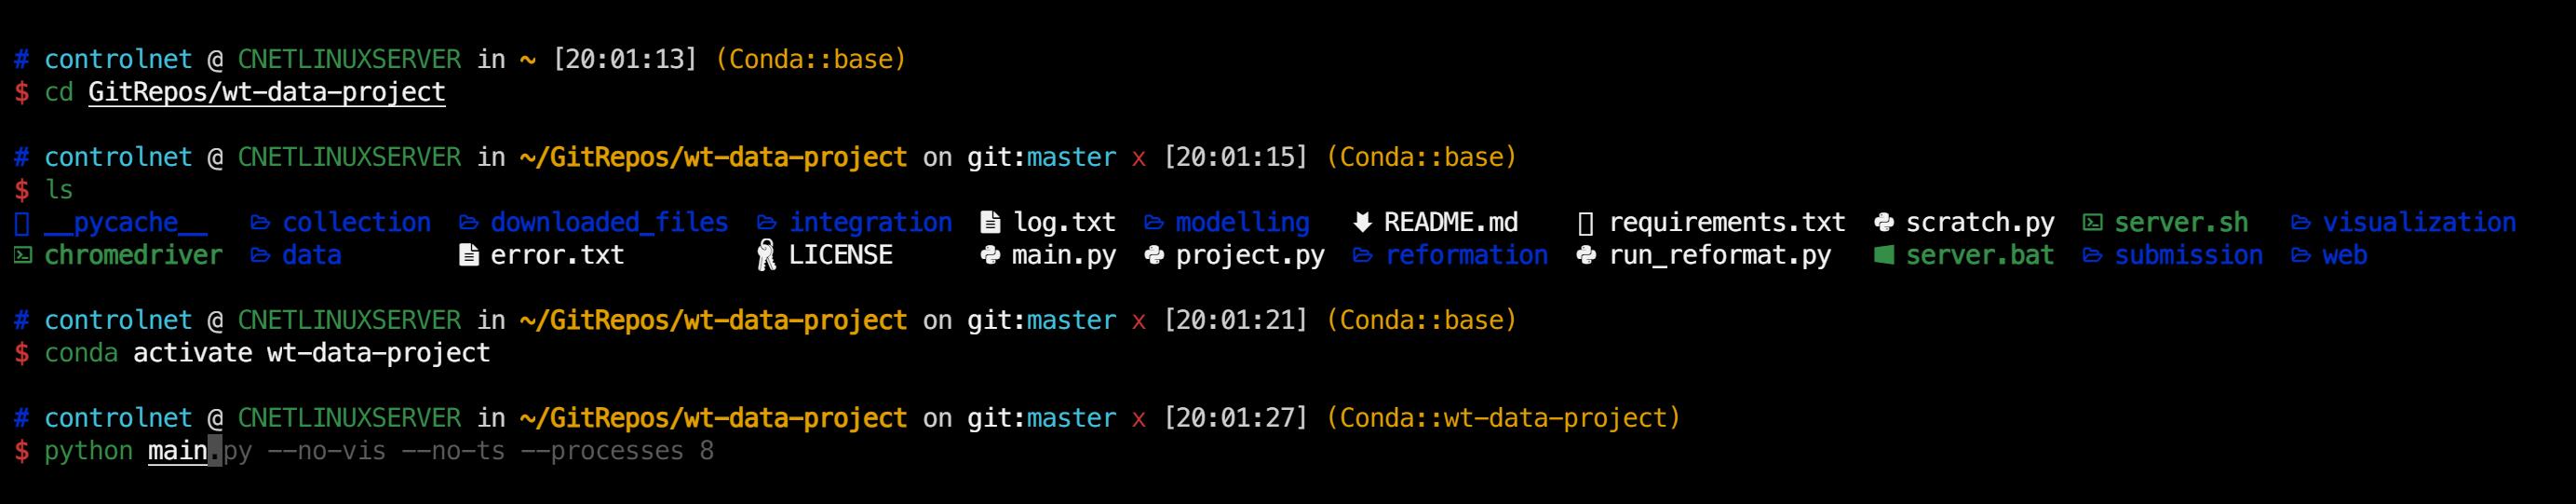
The prompt that shell sets up (the mzz-ys theme):
Docker
FROM ubuntu:24.04

RUN apt-get update \
 && DEBIAN_FRONTEND=noninteractive apt-get install -y --no-install-recommends ca-certificates curl sudo zsh \
 && rm -rf /var/lib/apt/lists/* \
 && useradd -m -s /bin/zsh user \
 && echo "user ALL=(ALL) NOPASSWD: ALL" > /etc/sudoers.d/user

USER user
WORKDIR /home/user
RUN curl -fsSL https://boot.controlnet.space/envira | bash -s -- install full -y

CMD ["/bin/zsh"]
This is the setup the CI integration tests use: a normal user with passwordless sudo. For a user
without sudo, drop sudo and the sudoers line and install user instead.
Legacy scripts
The shell scripts envira replaces. They still work and are still served.
curl -fsSL https://boot.controlnet.space/ | bash        # if you have sudo permission
curl -fsSL https://boot.controlnet.space/user | bash    # if you don't have sudo permission
curl -fsSL https://boot.controlnet.space/verify | bash  # verify the installation
Full tools and configurations in Docker with the legacy scripts:
FROM ubuntu:22.04

WORKDIR /root

RUN apt-get update -y
RUN DEBIAN_FRONTEND=noninteractive TZ=Etc/UTC apt-get install -o DPkg::Options::="--force-confnew" -y tzdata
RUN DEBIAN_FRONTEND=noninteractive apt-get install -y iputils-ping net-tools python3-venv apt-utils make openssh-server gedit vim git git-lfs curl wget zsh gcc make perl build-essential libfuse2 python3-pip screen fzf tmux ncdu bat pipx xsel screenfetch neofetch p7zip-full unzip tigervnc-standalone-server tigervnc-common tigervnc-xorg-extension

RUN curl -fsSL https://boot.controlnet.space/user | bash

CMD ["/bin/zsh"]
Minimal oh-my-zsh setup without extra tools:
# Setup environment
RUN sh -c "$(wget -O- https://github.com/deluan/zsh-in-docker/releases/download/v1.1.5/zsh-in-docker.sh)" -- \
    -t robbyrussell \
    -p https://github.com/zsh-users/zsh-autosuggestions \
    -p https://github.com/zsh-users/zsh-syntax-highlighting

# download theme
RUN curl -fsSL https://raw.githubusercontent.com/ControlNet/my-zsh-theme-env/main/files/mzz-ys.zsh-theme > /root/.oh-my-zsh/themes/mzz-ys.zsh-theme

# modify the .zshrc file to change the theme and add plugins
RUN cat /root/.zshrc | sed 's/ZSH_THEME=\"robbyrussell\"/ZSH_THEME=\"mzz-ys\"\nZSH_DISABLE_COMPFIX=\"true\"/' \
    | sed 's/plugins=(git)/plugins=(git zsh-autosuggestions zsh-syntax-highlighting)/' > /root/temp.zshrc
RUN mv /root/temp.zshrc /root/.zshrc

# setup git alias
RUN git config --global alias.lsd "log --graph --decorate --pretty=oneline --abbrev-commit --all"

# hide conda prefix
RUN echo "changeps1: false" >> /root/.condarc
What run.sh does, step by step:
- Checks the Linux distribution and installs a set of common development tools using the appropriate package manager.
- Installs pipx, a tool for installing and running Python applications in isolated environments.
- Downloads and installs bat, a cat clone with syntax highlighting and Git integration.
- Installs Node.js using nvm (Node Version Manager).
- Downloads and installs ctop, a top-like interface for container metrics.
- Installs neofetch, a command-line system information tool.
- Sets up tmux with a specific color scheme.
- Installs oh-my-zsh, a framework for managing Zsh configuration.
- Changes the default shell to Zsh.
- Downloads a specific Zsh theme and modifies the .zshrc file to use this theme and add plugins.
- Disables oh-my-zsh auto-update notifications.
- Installs additional Zsh plugins for autosuggestions and syntax highlighting.
- Sets up Git history visualization and credential storage.
- Installs Miniconda, a free minimal installer for conda.
- Sets up the Rust programming language and Go programming language environments.
- Installs lazygit, a simple terminal UI for git commands.
- Installs neovim, a highly configurable text editor.
- Sets up LunarVim, a distribution of Neovim.
- Installs a faster solver for conda.
- Installs the Meslo font.
- Installs Docker and sets up the user to run Docker commands without sudo.
- Installs lazydocker, a simple terminal UI for Docker.
- Installs lemonade, a remote operation utility.
- Installs ZeroTier, a global P2P VPN.
- Installs several utilities (lsd, git-delta, duf, dust, fd, ripgrep, gping, procs, xh, uv, speedtest-cli, gdown, zoxide, micro, scc, viu, pm2) and sets up aliases for some of them.
- Installs several system monitoring tools (bottom, nvitop, bpytop, bandwhich).
If your sudo credential times out during a long installation, run.sh refreshes sudo credentials
in the background after the first sudo prompt.
License
AGPL 3.0 - see LICENSE file for details.
1 maintainer

Metadata
1 maintainer
Release files for envira 0.1.4
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Built distributions (wheels)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| envira-0.1.4-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.musllinux_1_1_x86_64.whl | Python 3 | none | Linux glibc 2.17+ x86-64, Linux musl 1.1+ x86-64 | Details for envira-0.1.4-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.musllinux_1_1_x86_64.whl |
| envira-0.1.4-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.musllinux_1_1_aarch64.whl | Python 3 | none | Linux musl 1.1+ ARM64, Linux glibc 2.17+ ARM64 | Details for envira-0.1.4-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.musllinux_1_1_aarch64.whl |
| envira-0.1.4-py3-none-macosx_11_0_arm64.whl | Python 3 | none | macOS 11.0+ ARM64 | Details for envira-0.1.4-py3-none-macosx_11_0_arm64.whl |
Total release size: 16.2 MB
Release files / envira-0.1.4-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.musllinux_1_1_x86_64.whl
| Download URL | envira-0.1.4-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.musllinux_1_1_x86_64.whl |
|---|---|
| Size | 5.8 MB |
| Tags | Linux glibc 2.17+ x86-64 Linux musl 1.1+ x86-64 Python 3 |
|
SHA-256 checksum How to use checksums |
895512f52116d110a098ebcf3bdba54b5e5147e3499255e10a60faf59157b9ca
|
|
BLAKE2b-256 checksum How to use checksums |
1abffa87235f549248b95ff4885b0c84d36c0dedd1eefcf0b361e238ae7e3596
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / envira-0.1.4-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.musllinux_1_1_aarch64.whl
| Download URL | envira-0.1.4-py3-none-manylinux2014_aarch64.manylinux_2_17_aarch64.musllinux_1_1_aarch64.whl |
|---|---|
| Size | 5.3 MB |
| Tags | Linux glibc 2.17+ ARM64 Linux musl 1.1+ ARM64 Python 3 |
|
SHA-256 checksum How to use checksums |
ee88198e45807a1247605cd0acf8b0a684b10916750fc7abe376ce9086f582c0
|
|
BLAKE2b-256 checksum How to use checksums |
b422c1bd05a42fcf2e7c995b43f517d4978f1b00de1f0429853b5148c501a343
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logRelease files / envira-0.1.4-py3-none-macosx_11_0_arm64.whl
| Download URL | envira-0.1.4-py3-none-macosx_11_0_arm64.whl |
|---|---|
| Size | 5.2 MB |
| Tags | Python 3 macOS 11.0+ ARM64 |
|
SHA-256 checksum How to use checksums |
7cedfe370c0b1d415d25856b09c7ec1268b9451ebb874f75dff954707dc464b0
|
|
BLAKE2b-256 checksum How to use checksums |
57d176a81f9aeff521574c4425f606dc7e17cc782f26e3b37b9accd2c1845f63
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logSecurity for envira 0.1.4
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 3 files in this release have been uploaded with provenance metadata.
Attestation for envira-0.1.4-py3-none-manylinux2014_x86_64.manylinux_2_17_x86_64.musllinux_1_1_x86_64.whl
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Nov 7, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














