
This release is a pre-release and may not be stable for production use.
EvidentLoop
Turn local Git diffs into evidence-backed, traceable audit reports.


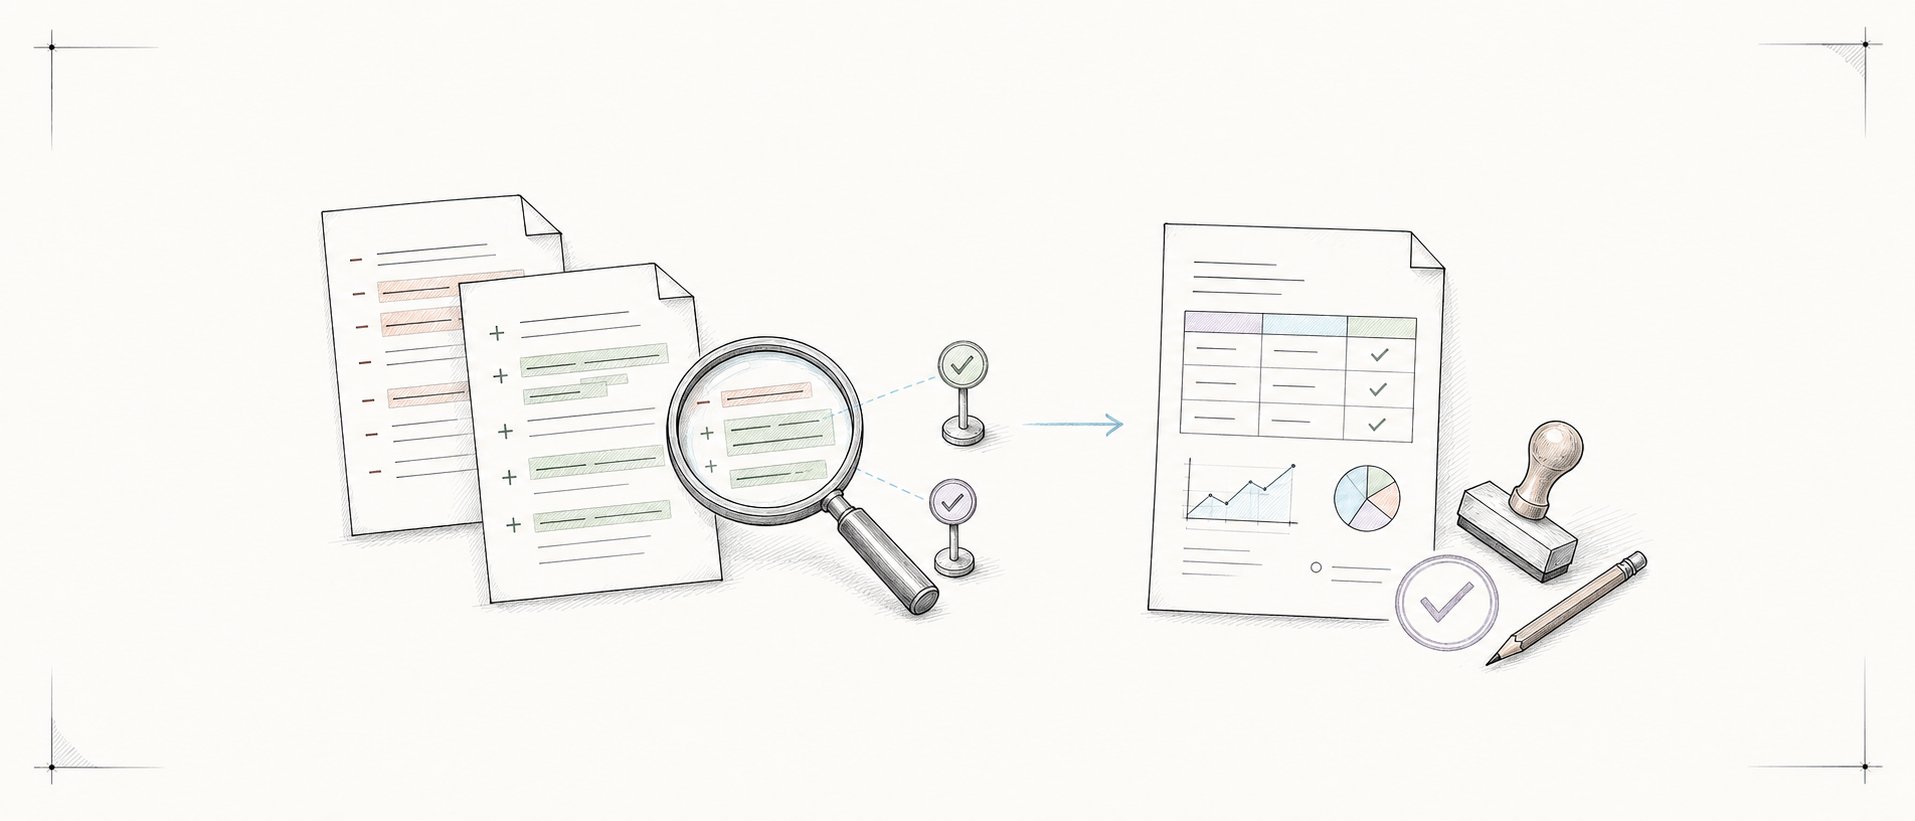
Use EvidentLoop to inspect a local Git diff, trace each finding to the changed lines, record a human decision, and explicitly verify a later fix.
Your coding agent makes the judgment. EvidentLoop validates the result and saves the evidence in a self-contained HTML report with its JSON record. The result stays traceable without being presented as proof that the code is safe.
Prefer to see the report first? Jump to the real audit evidence.
Quick start
Requirements: Git, Python 3.10 or newer, uv, Node.js/npx for Skill installation, and a coding agent with Skill support.
# Try the bundled offline demo
uvx evidentloop demo

# Install the CLI and Skill
uv tool install evidentloop
npx skills@latest add evidentloop/evidentloop --skill evidentloop -g
evidentloop doctor
pipx install evidentloop is the CLI fallback.
Inside the Git repository to inspect, ask your coding agent:
Use EvidentLoop to audit my staged changes and generate the HTML report.
Real audit evidence
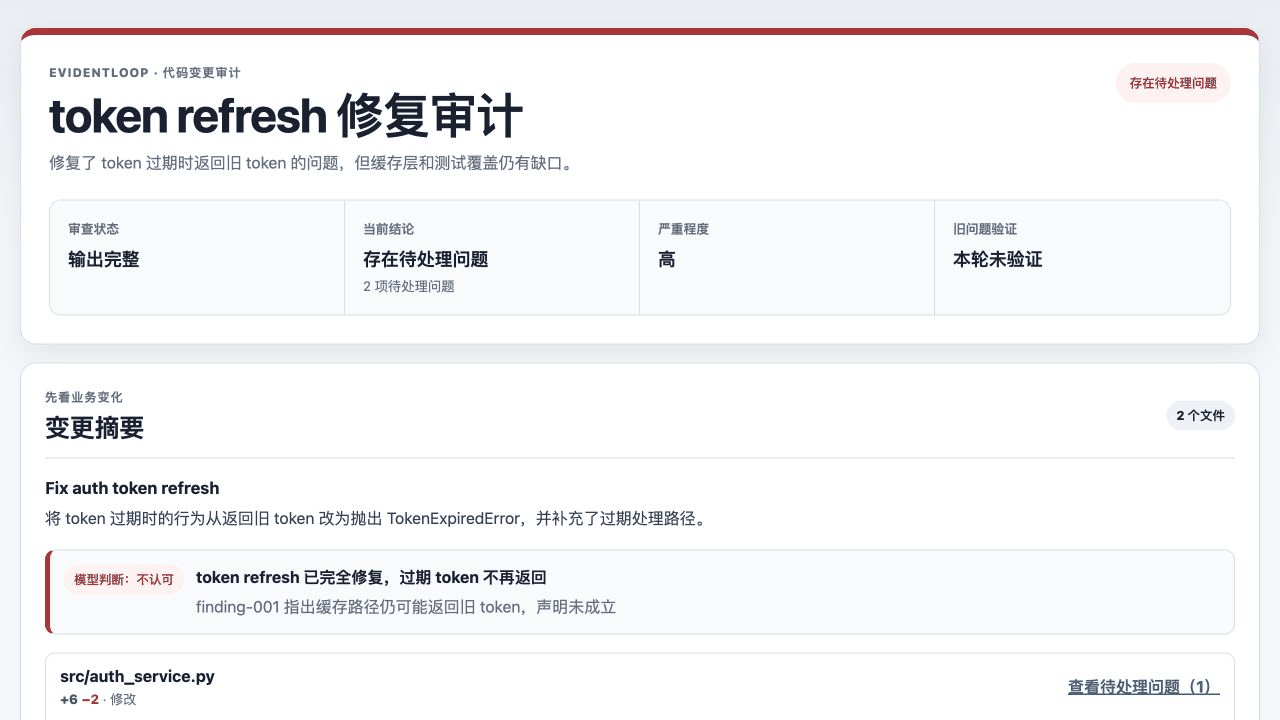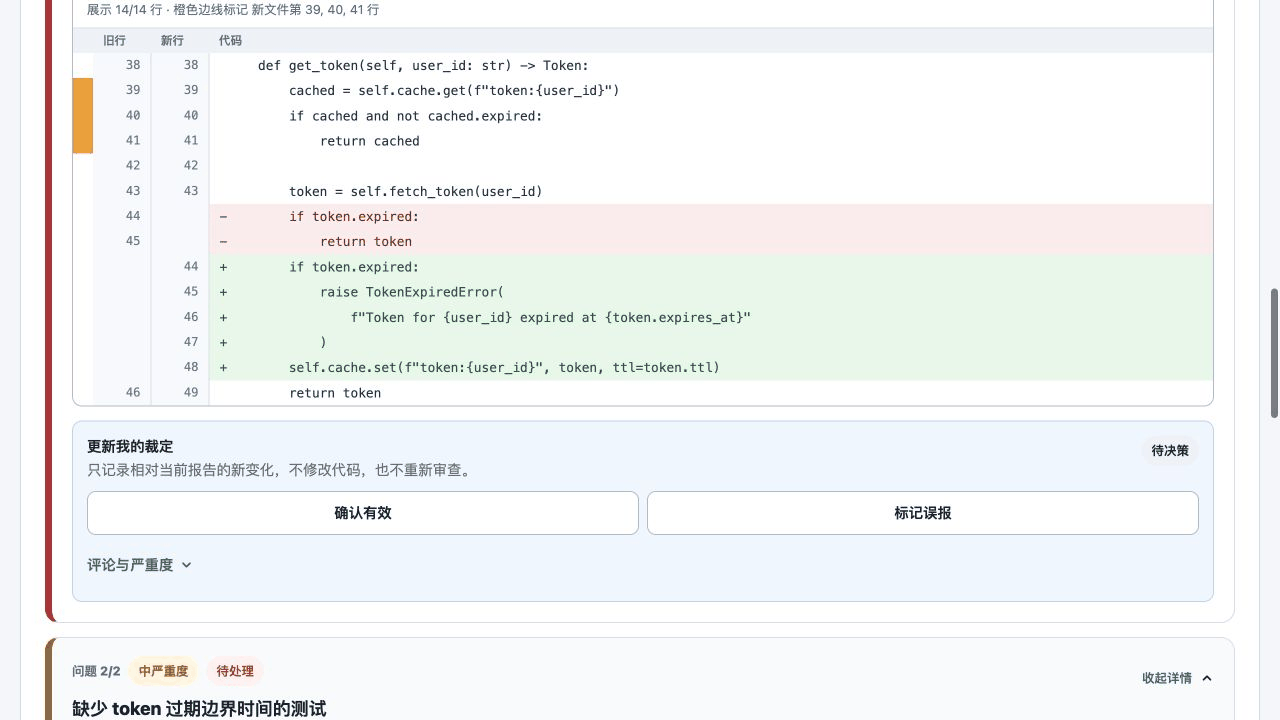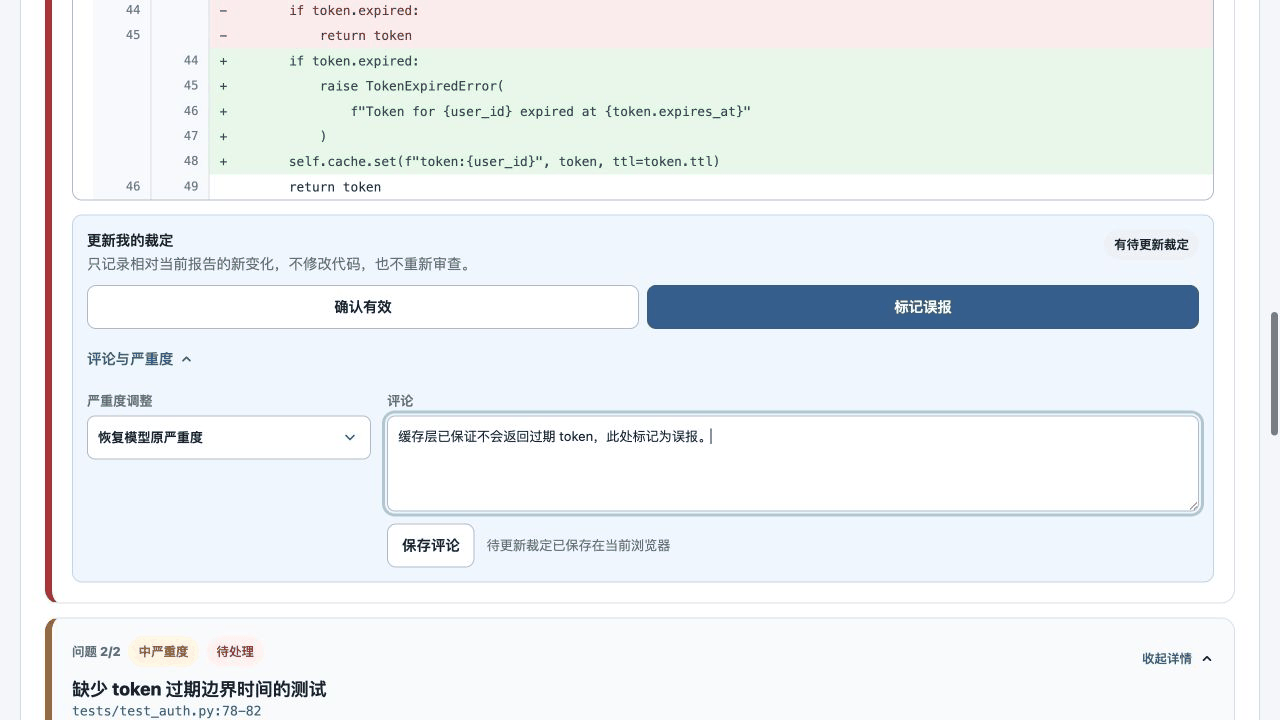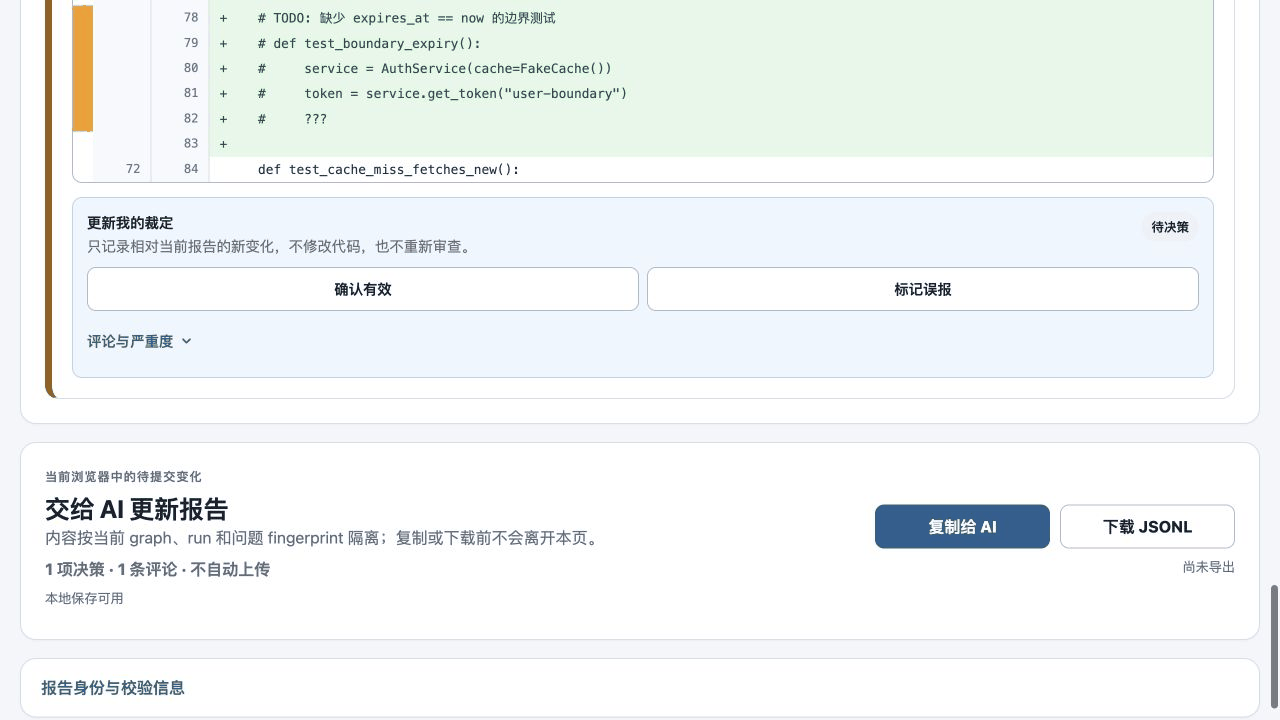
Representative schema 0.5 report · decision and comment · Alpha UI in Simplified Chinese
The animation uses a representative schema 0.5 report generated by the current renderer to show a finding, its complete diff, and a local decision with a comment. The separate self-audit report covers 43/43 files and ends complete / pass_candidate with 0 findings. It proves report generation, validation, and rendering for that range. The public evidence does not yet include a real two-diff fix-verification run.
How it works
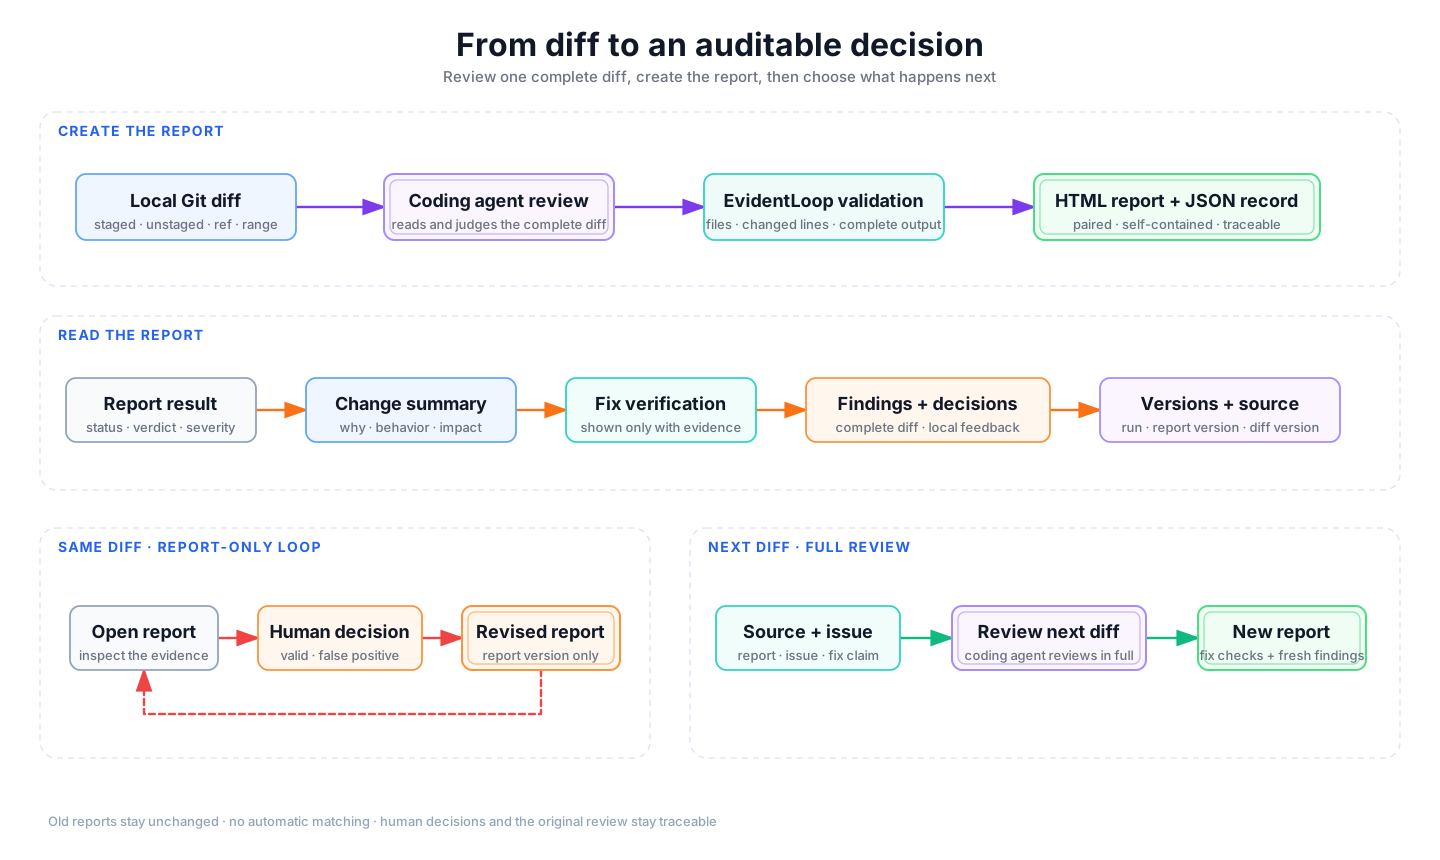
- Review a complete diff. Your coding agent returns its judgment; EvidentLoop validates the result and renders one self-contained report.
- Revise the report, not the code. Feedback on the same diff updates only the existing report and JSON record without asking the model to review again.
- Verify a later diff explicitly. A source report, chosen finding, and claim start a new full-diff review. Old reports remain unchanged and EvidentLoop does not guess finding matches.
Output
| File | Purpose |
|---|---|
audit.json |
Validated audit record linking Git changes, findings, decisions, and report lineage. |
audit.html |
Self-contained report showing the result, relevant diff, and browser-local decisions. |
audit-feedback.jsonl |
Optional machine-readable decision export for a coding agent. |
Pending feedback stays in each viewer's browser until copied or downloaded. The HTML can be shared after redaction, but it is not a multi-user review service.
Alpha scope
| Supported | Not supported |
|---|---|
| Local Git staged, unstaged, ref, and range diffs | Folder diffs, file-only review, or remote PR URLs |
| Added, modified, deleted, renamed, and binary-file metadata | Automatic fixes or command execution |
Schema 0.5, exact changed-line evidence, and same-diff report revision |
Automatic model re-review from feedback |
| Explicit next-diff verification from a source report, finding, and claim | Automatic finding matching or inferred repair from disappearance |
| Complete, partial, failed, and inconclusive states | Silent stale-feedback merging or cross-workspace report search |
Integration and development
Use EvidentLoop through the Skill as a standalone product; no other workflow is required. Integrators can follow the prepare -> external review -> finalize path in AI host integration, use the public API in evidentloop.api, and rely on diff_version plus report_version for artifact identity.
For local development:
python -m pip install -e '.[dev]'
python -m pytest -q
python -m ruff check .
python -m build
References: Pages · V0 scope · Data model · AI host integration
Alpha feedback and bug reports are welcome in GitHub Issues.
License
Licensed under the MIT License.
1 maintainer

Metadata
1 maintainer
Release files for evidentloop 0.1.0a3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| evidentloop-0.1.0a3.tar.gz | 125.7 kB | With provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| evidentloop-0.1.0a3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 227.2 kB
Release files / evidentloop-0.1.0a3.tar.gz
| Download URL | evidentloop-0.1.0a3.tar.gz |
|---|---|
| Size | 125.7 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
3677759a6b393a8df102b2c2fd17f2c98e7a58aba51592402f24354edeb356f9
|
|
BLAKE2b-256 checksum How to use checksums |
650de121dc5a72bac2bfec8b26a72aec6be2b0395c808155d73dda3148b7e0fa
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 24, 2026.
Transparency logRelease files / evidentloop-0.1.0a3-py3-none-any.whl
| Download URL | evidentloop-0.1.0a3-py3-none-any.whl |
|---|---|
| Size | 101.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
280ffbc28805bc16985036609d2aa6a81319acea0995d88c144fcb7cebfc5a3c
|
|
BLAKE2b-256 checksum How to use checksums |
7762ecddb326daae909f03e748ea9841a77ca6619875d7e68c433bfedc9210c6
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/6.1.0 CPython/3.13.14
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 24, 2026.
Transparency logSecurity for evidentloop 0.1.0a3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for evidentloop-0.1.0a3.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Jul 24, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














