


FastAPI Feature Flags
Very simple implementation of feature flags for FastAPI.
- Minimum configuration required
- No unnecessary dependencies
- Does its job
Installing
To install the package from pip, first run:
pip install fastapi-featureflags
Usage
A simple example of feature flags:
from fastapi_featureflags import FeatureFlags, feature_flag, feature_enabled

FeatureFlags(conf_from_url="https://pastebin.com/raw/4Ai3j2DC")
print("Enabled Features:", FeatureFlags.get_features())


@feature_flag("web_1")
def web_1_enabled():
    print("Feature Should be enabled: web_1")

web_1_enabled()

if feature_enabled("web_2"):
    print("Feature Should be disabled: web_2")
You can get FF (feature flags) from a File, URL, Dictionary or ENV Variables:
FeatureFlags.load_conf_from_url("https://pastebin.com/raw/4Ai3j2DC")
FeatureFlags.load_conf_from_json("tests/features.json")
FeatureFlags.load_conf_from_dict({"web_1": True, "web_2": False})

FeatureFlags.reload_feature_flags()
There is also a handler that recognizes if the "@feature_flag" wrapper is used and the flag is not registered in the config. This way you can also use FF at runtime. Defaults to False, so it's safer if you forget the feature flag in the code.
Function get_features returns a list of all registered FF
You can enable or disable functions on the fly with enable_feature or enable_feature
When needed you can reload all feature flags with reload_feature_flags,
this is useful when you want to read and change features from URL.
All unregistered or on-the-fly created FF, that are not in the configuration will be omitted.
For non-production testing, a router is available,
so you can see the paths in swagger-ui docs.
Use include_in_schema=False when defining the router for public deployments
from fastapi_featureflags import router as ff_router
app.include_router(ff_router, prefix="/ff", tags=["FeatureFlags"])
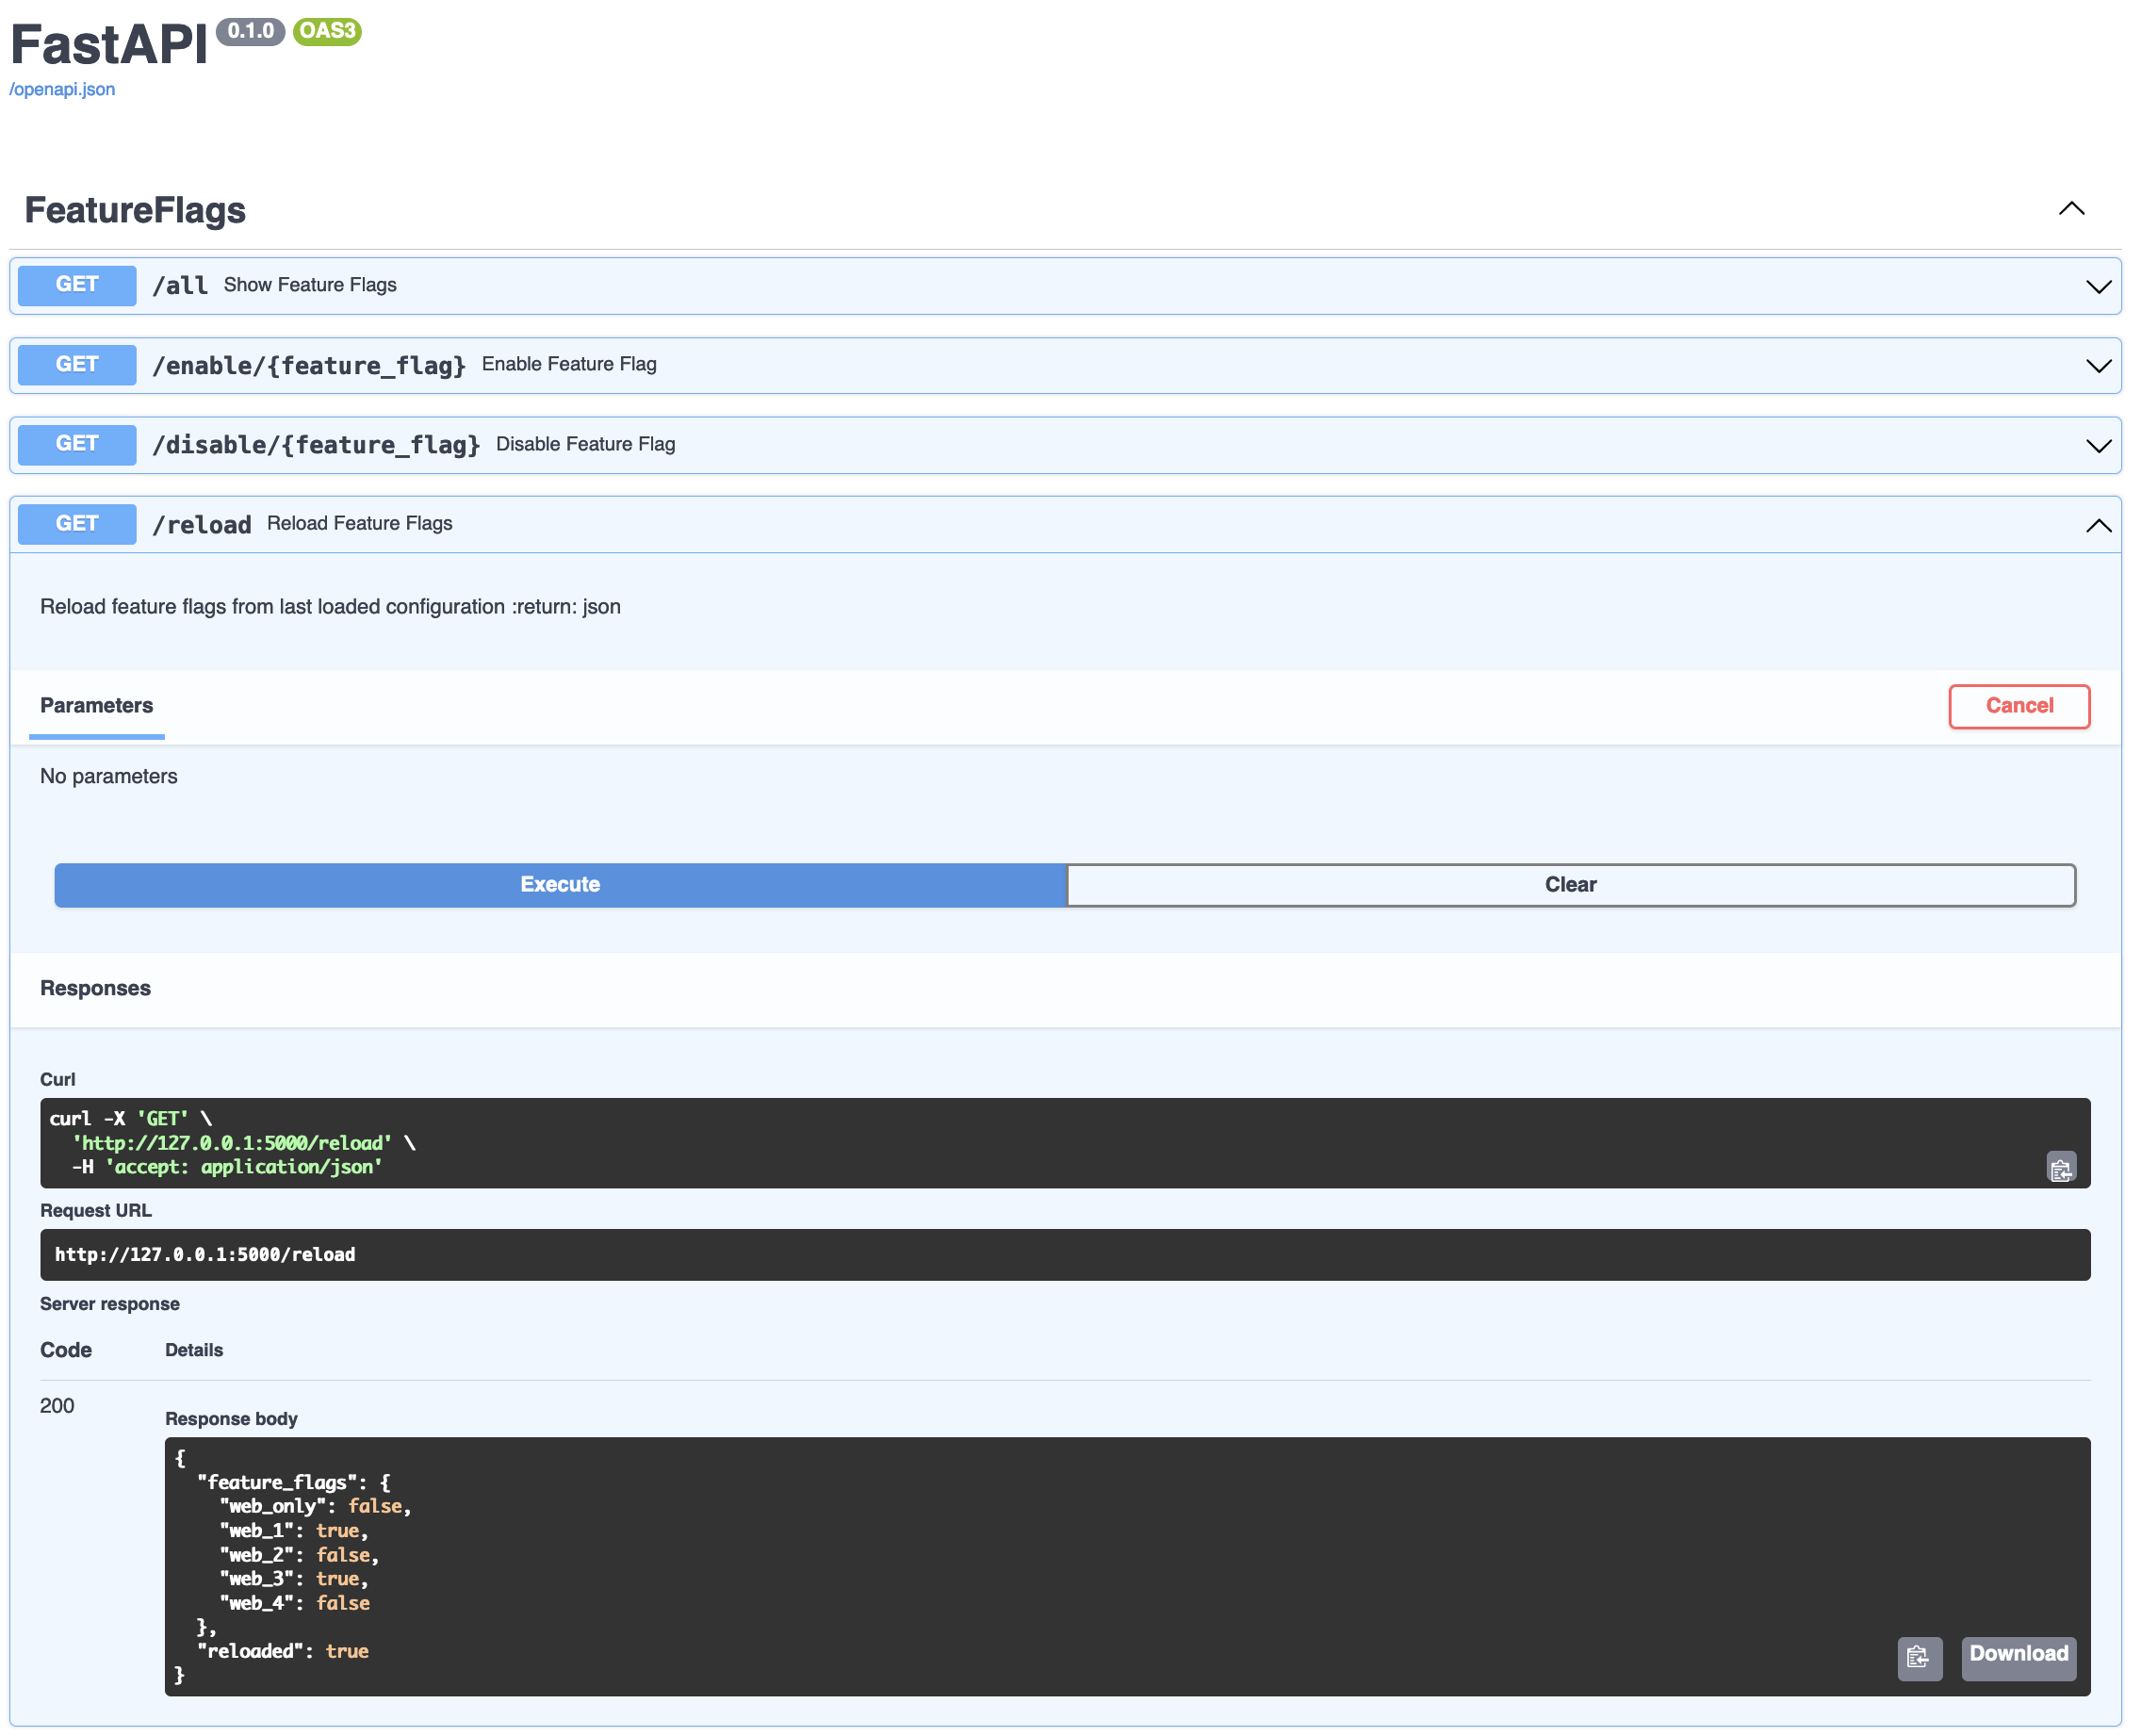
Contributing and Code of Conduct
Contributing to fastapi-featureflags
As an open source project, fastapi-featureflags welcomes contributions of many forms.
Please read and follow our Contributing to fastapi-featureflags
Code of Conduct
As a contributor, you can help us keep the fastapi-featureflags project open and inclusive.
Please read and follow our Code of Conduct
1 maintainer

Metadata
1 maintainer
Release files for fastapi-featureflags 0.4.9
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| fastapi_featureflags-0.4.9.tar.gz | 4.8 kB | Without provenance | Details for fastapi_featureflags-0.4.9.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| fastapi_featureflags-0.4.9-py3-none-any.whl | Python 3 | none | any | Details for fastapi_featureflags-0.4.9-py3-none-any.whl |
Total release size: 10.3 kB
Release files / fastapi_featureflags-0.4.9.tar.gz
| Download URL | fastapi_featureflags-0.4.9.tar.gz |
|---|---|
| Size | 4.8 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
acfef5875a7f0320681351d509ed29573dc31704ca43579731a68d5c32872eb4
|
|
BLAKE2b-256 checksum How to use checksums |
0ec91b0da963a4bf8e055787b1cb6ca122d39d79d82dc0567a755a77daaf43d9
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.9.18
|
Release files / fastapi_featureflags-0.4.9-py3-none-any.whl
| Download URL | fastapi_featureflags-0.4.9-py3-none-any.whl |
|---|---|
| Size | 5.5 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
544ad2a1004e060fe78a45946227bad8079ad206bee5e60877e7b051f5ab9eb5
|
|
BLAKE2b-256 checksum How to use checksums |
caff660f524381d18eb8ec8ed782c41e1ccd4061c27faf665c0947feb9c6e171
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/5.0.0 CPython/3.9.18
|
Security for fastapi-featureflags 0.4.9
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














