
FFLocker
Locking files/folders [FF] in GNU/Linux via text-based user interface (TUI).
The most important part of the algorithm is that during the locking process, your password is never saved on the computer and only displayed in the terminal for you to save it.
Description
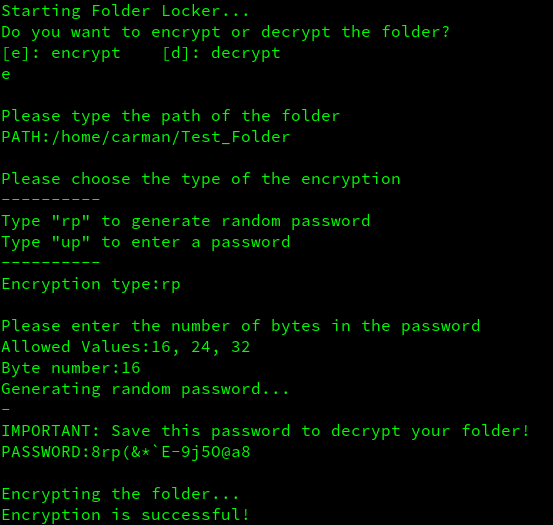
FFLocker uses AES encryption. You can either create a password with 16, 24, and 32 characters (which corresponds to 128, 192, and 256 bits, respectively) or generate a random password with the help of the secrets.choice.
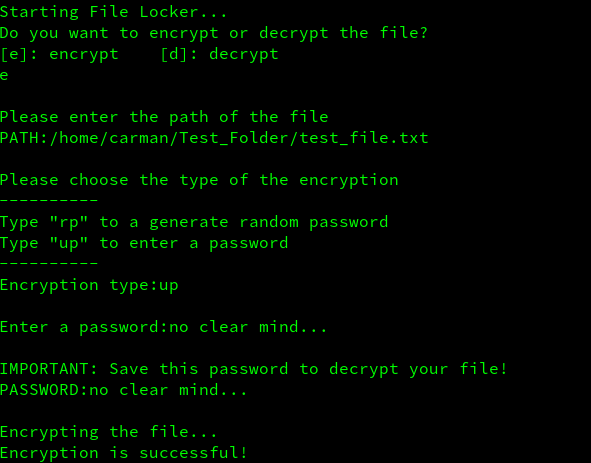
After you lock the file/folder, the program will change the binary data and overwrite it. To read/open the encrypted file/folder, you have to enter the password.
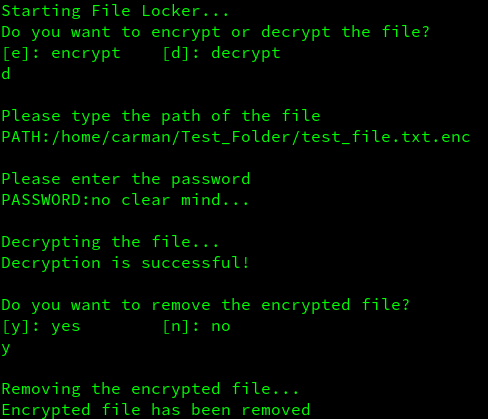
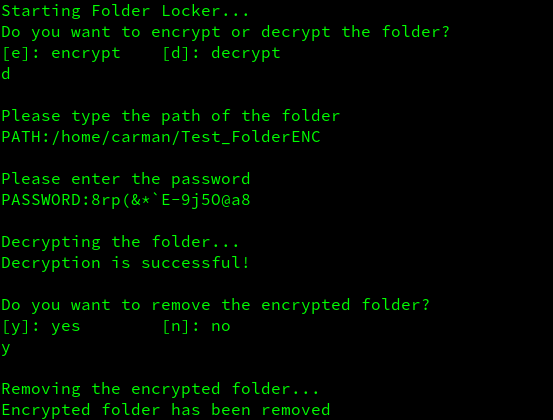
I have written the program in such a way that when you decrypt the file/folder, a new file/folder will be created as a precaution against entering the wrong password. At the end of the decryption process, you can permanently delete the encrypted file/folder via a single command (see the WARNING subsection).
Additionally, every file and folder receives .enc and ENC extensions at the end of the encryption process. If your pathname does not contain these extensions, the decryption process does not begin. Similarly, you cannot encrypt the file/folder if it has a .enc or ENC extension.
WARNING
Even if your password is wrong, the program will decrypt the file/folder and produce a result if it has a sufficient number of characters (bytes). In this case, be careful about deleting the encrypted file/folder since the decrypted one will be unreadable due to the wrong password. As for advice, always open and read the decrypted file/folder before you delete the encrypted one.
Installation
You can install the FFLocker via pip
python3 -m pip install fflocker
or by directly cloning to your desired directory
git clone https://github.com/camarman/FFLocker.git
Requirements
FFLocker requires pycryptodome, which can be installed by running
python3 -m pip install pycryptodome
User Guide
To start the file locking process run
python3 -m fflocker.file_locker
Similarly, to start the folder locking process run
python3 -m fflocker.folder_locker
from the terminal.
Overview
| Encryption process of a file | Decryption process of a file |
|---|---|
 |
 |
| Encryption process of a folder | Decryption process of a folder |
|---|---|
 |
 |
Upcoming Features
I am thinking to implement a command line interface (CLI), and it will probably look like this:
$ fflocker -Fe [path]
$ fflocker -De [path]
$ fflocker -Fd [path]
$ fflocker -Dd [path]

-F --File
-D --Directory
-e --encrypt
-d --decrypt
1 maintainer

Metadata
1 maintainer
Release files for fflocker 1.3
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| fflocker-1.3.tar.gz | 6.1 kB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| fflocker-1.3-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 13.8 kB
Release files / fflocker-1.3.tar.gz
| Download URL | fflocker-1.3.tar.gz |
|---|---|
| Size | 6.1 kB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
32597ec9342d071e929e494b7df7a1bcf378016508ebcc8619639da6c116cb51
|
|
BLAKE2b-256 checksum How to use checksums |
2619dd1e678763a66168551ace60d8503b57256bcbb7cd31f918117c7eefe493
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.11.3
|
Release files / fflocker-1.3-py3-none-any.whl
| Download URL | fflocker-1.3-py3-none-any.whl |
|---|---|
| Size | 7.7 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
6b42bcbd08f7a6992c64a494cbc907d06c4f6a4e4c0f6e0b62c54b7f075d43e9
|
|
BLAKE2b-256 checksum How to use checksums |
0a243de8c06b9ed55c5d08ac58bb3a1a9e962f9de2aa859ab446f2b9e3e06517
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/4.0.2 CPython/3.11.3
|
Security for fflocker 1.3
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














