
finledgerpoli
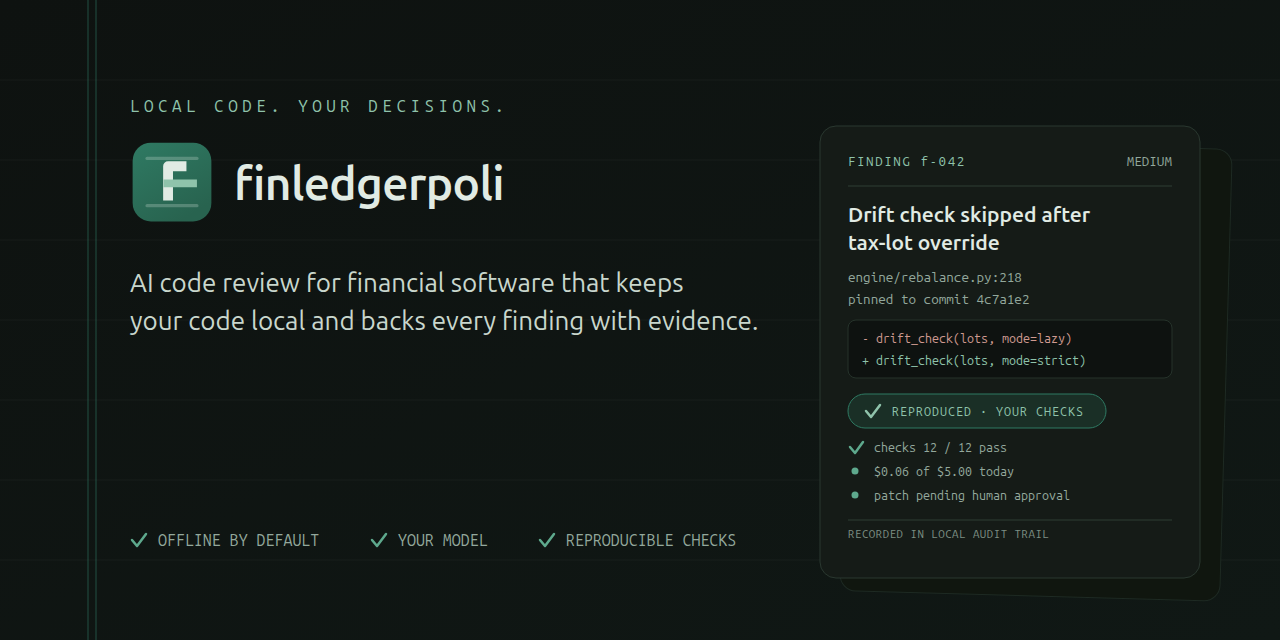
AI code review for financial software that keeps your code local and backs every finding with evidence.


Why finledgerpoli
- Hosted AI reviewers need your source; finledgerpoli runs on your machine and is offline by default. You approve anything that leaves it.
- AI findings can be wrong; reproduce them with your own checks and tie each one to the exact code version.
- AI spend is easy to lose track of; it enforces daily and monthly limits locally and shows spend against them.
- Suggested fixes can be risky; every patch needs your approval and can be rolled back. Nothing merges, deploys or trades by itself.
Who it's for
Built for developers of institutional financial software — rebalancers, optimizers, risk and tax-lot engines — where a one-cent rounding error or an unexpected change in trades is a real incident.
| When you... | finledgerpoli helps you... |
|---|---|
| Change an optimizer or rebalancing rule | Review the exact commit with a finance or quant review profile, then reproduce each finding with your own tests before acting on it |
| Worry about rounding, units and edge cases | Run your configured, repeatable checks for cents, basis points vs percent and boundary values, so findings have evidence you can inspect |
| Want AI review without exposing client data | Stay offline by default, screen content before anything leaves your machine, approve every outgoing request, or use a local model through Ollama |
| Need to show reviewers what changed and why | Keep a tamper-evident local log of what was reviewed, found, fixed and approved: audit evidence for your change records |
| Use several AI providers on a budget | Switch between OpenAI, Anthropic, Gemini or local models, with daily and monthly limits and a usage dashboard |
| Let an AI agent suggest fixes | Approve each patch before it applies, with rollback. Nothing merges, deploys or trades by itself |
Why not a general AI code reviewer? Hosted reviewers ask you to send your code and trust their retention policies. finledgerpoli keeps review state and evidence on your machine, ties findings to the exact code version, and tracks estimated spend and unresolved charges locally. Remote providers receive the requests you explicitly approve.
Quick start
Python 3.11+ is required; Git is needed for source workflows. Install with pipx:
pipx install finledgerpoli
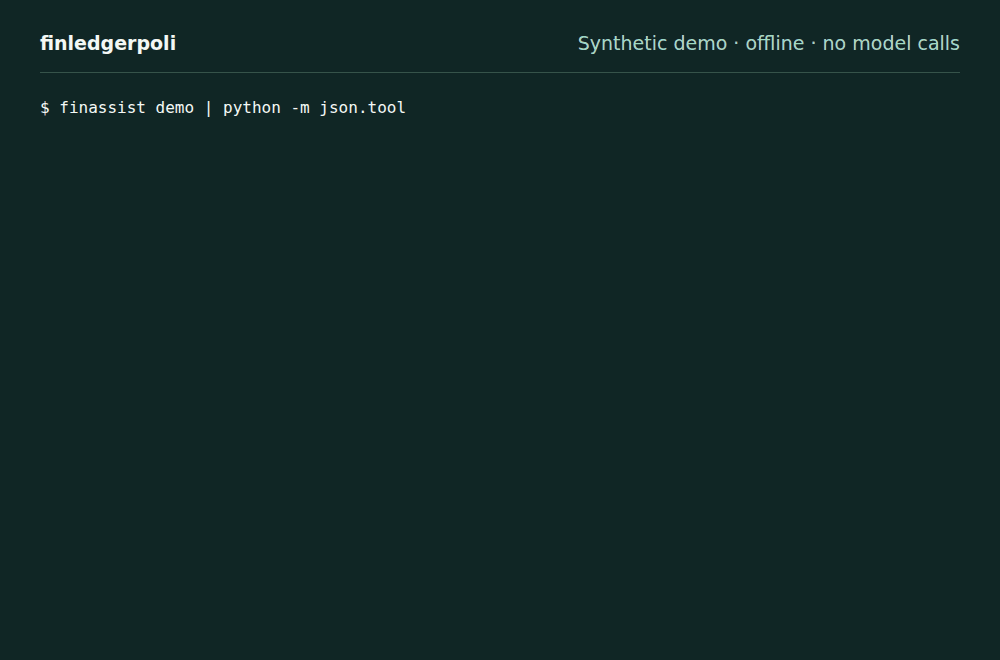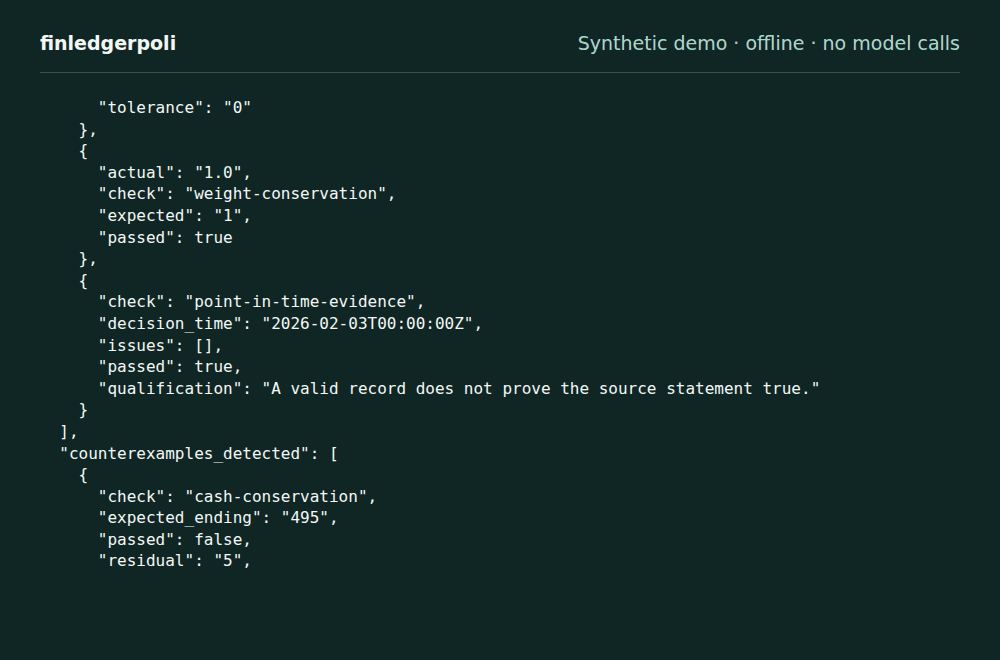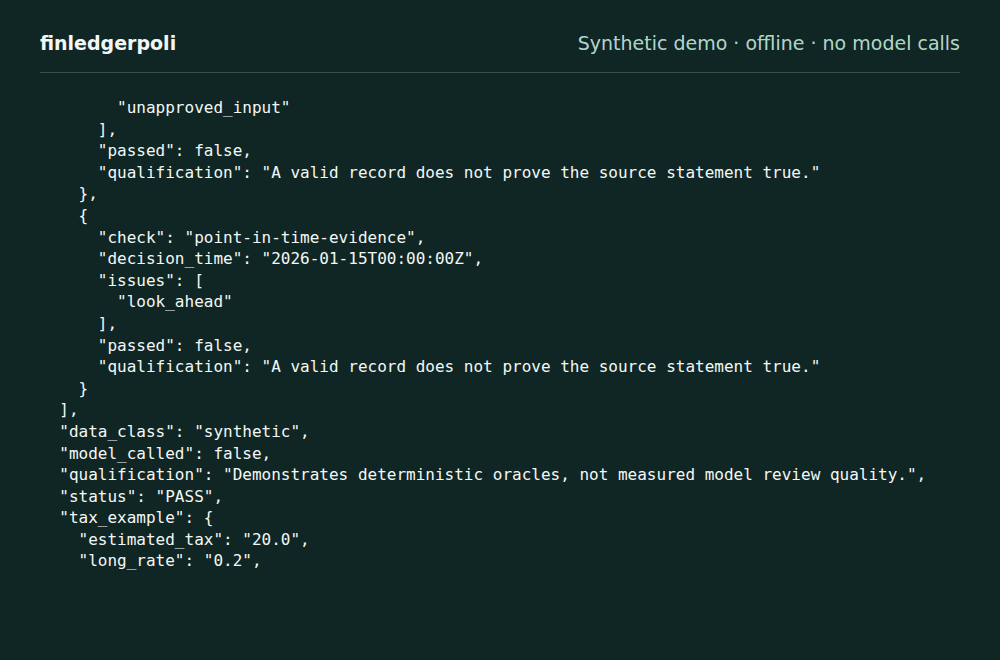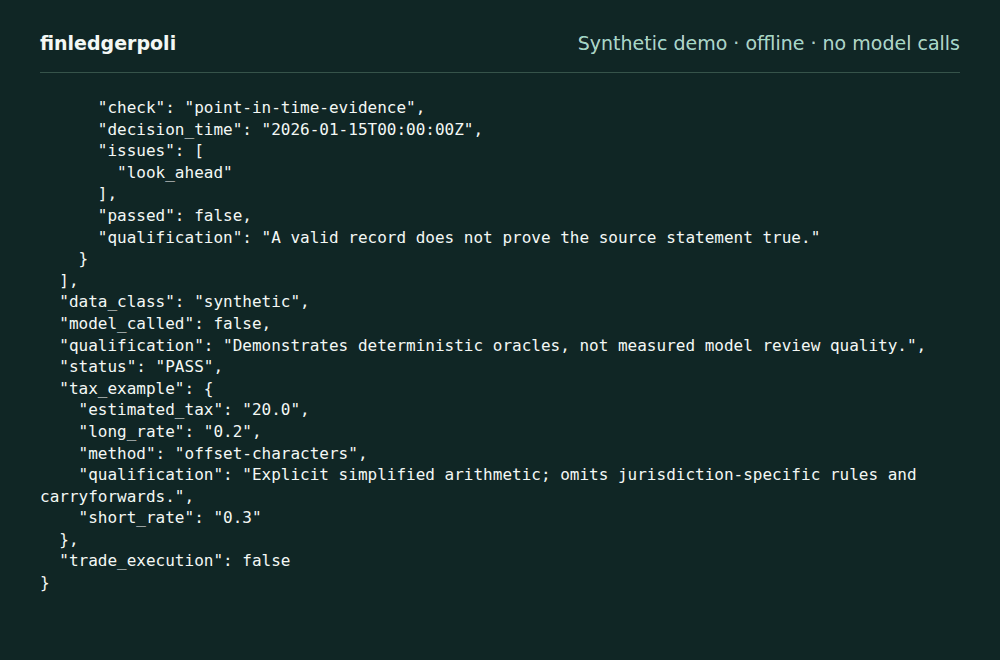
finassist demo
finassist init
finassist dashboard
The package is finledgerpoli, the command is finassist (finledgerpoli also works).
For an existing Python environment, pip install finledgerpoli is also supported.
The demo needs no key, model download or container; it runs fictional finance checks,
not a model-quality benchmark. The dashboard ships prebuilt, makes no external requests
and binds only to 127.0.0.1; Node is needed only for frontend development.
From source
git clone https://github.com/EleutheroiEdge/finance-dev-assistant.git
cd finance-dev-assistant
python3 -m venv .venv
.venv/bin/python -m pip install .
.venv/bin/finassist demo
.venv/bin/finassist init
.venv/bin/finassist dashboard
On Windows PowerShell, use py -3 -m venv .venv, then
.\.venv\Scripts\python.exe -m pip install . and
.\.venv\Scripts\finassist.exe demo. No activation or execution-policy change
is required. macOS/Linux use the commands above. See platform setup
for UTF-8, permissions, Git modes and Docker Desktop details.
How it works
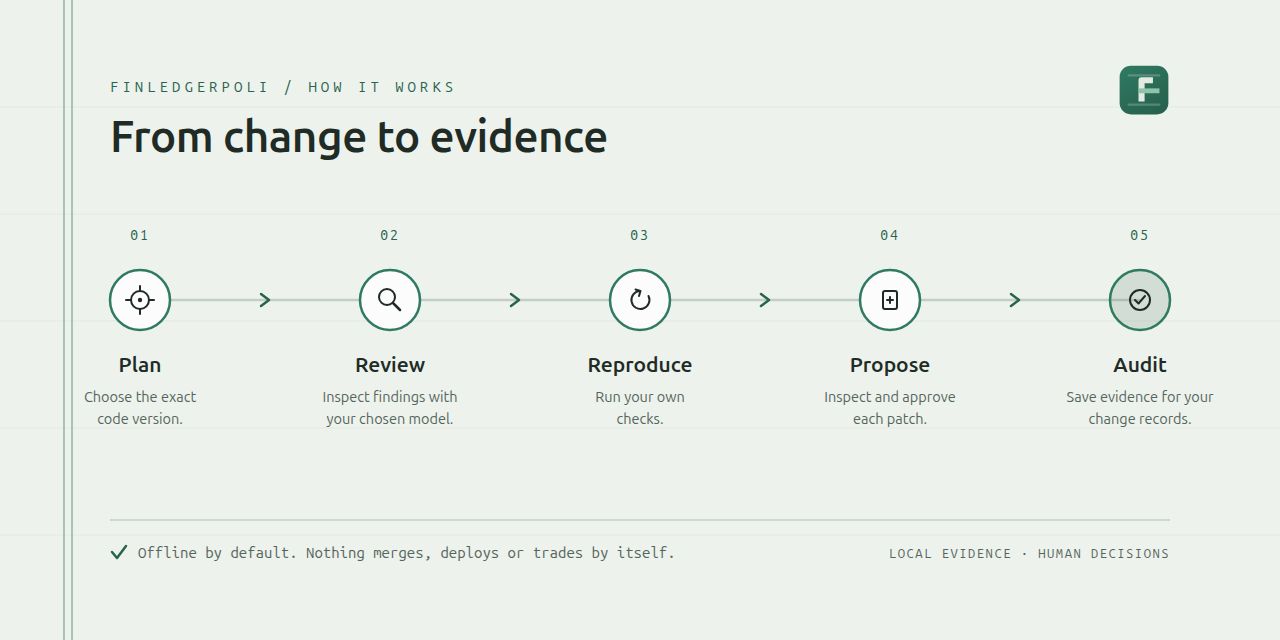
- Plan: choose the exact commits, screen source and inspect what will be reviewed.
- Review: use a finance, quant or custom checklist with your chosen model, or inspect risks offline.
- Reproduce: run your approved checks against the committed source and compare the evidence.
- Propose: inspect the exact patch, approve it and keep a guarded recovery copy.
- Audit: save evidence for your change records, including approvals, spend and unknown outcomes.
Start offline from the repository you want to review, after inspecting its configuration and source policy:
finassist --config finassist.json plan --repo . --base main --head HEAD \
  --output .finassist/context.json
finassist --config finassist.json review --packet .finassist/context.json \
  --output .finassist/offline-review.json
Offline analysis does not claim a model review or test execution. Remote model use
requires an explicit provider, model, endpoint, price assumptions, named key environment
variable, network permission and approval of the exact outgoing request.
There is no automatic provider fallback. See provider setup.
Download the original terminal recording
and play it locally with asciinema play docs/images/demo.cast.txt; no hosting account is needed.
Dashboard
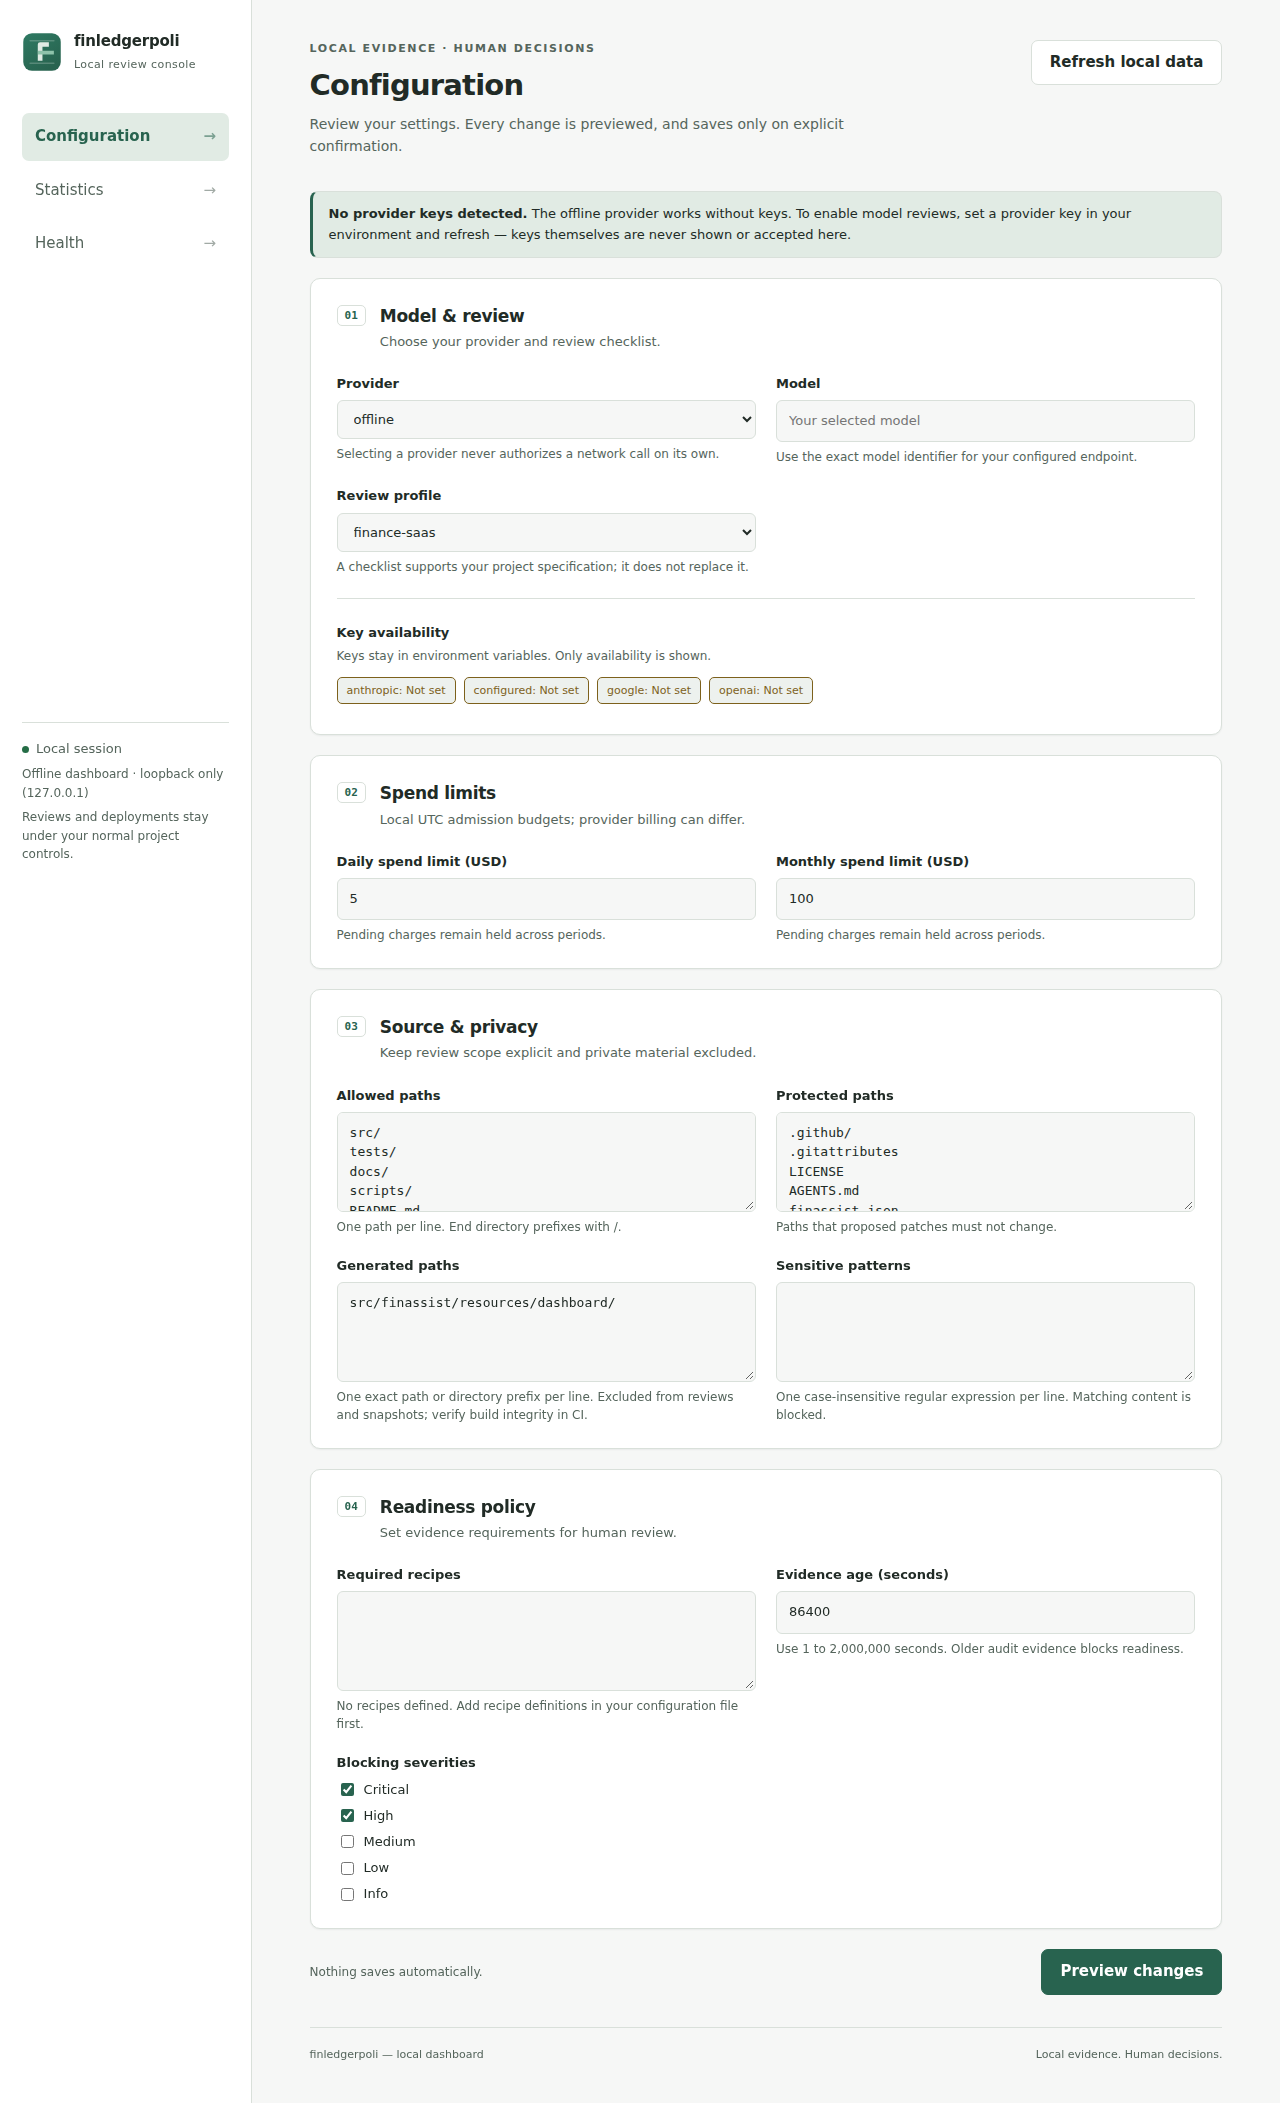
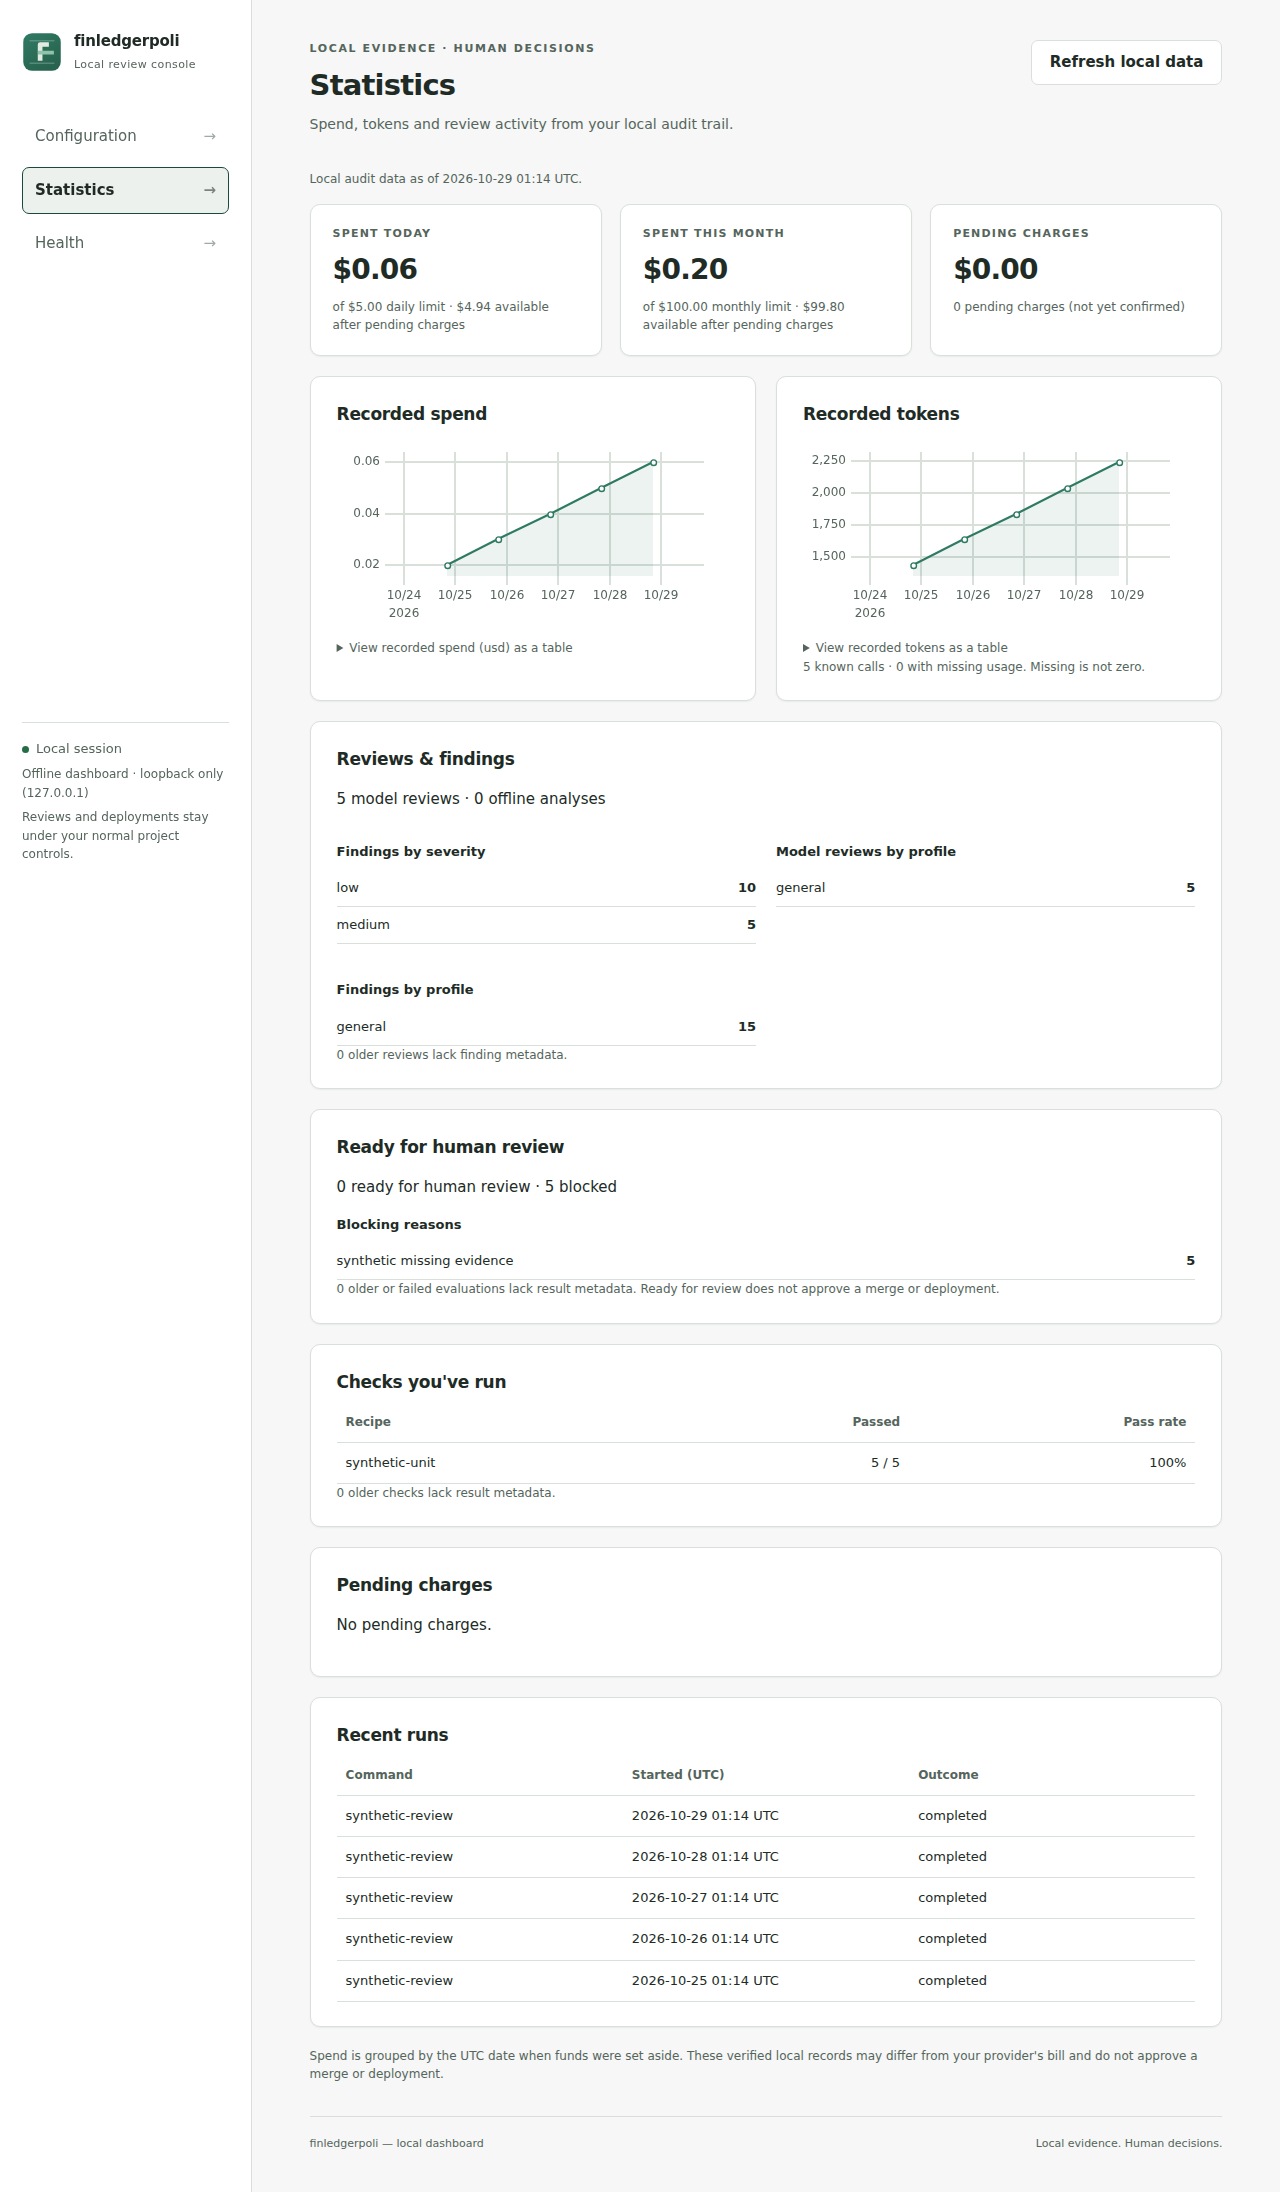
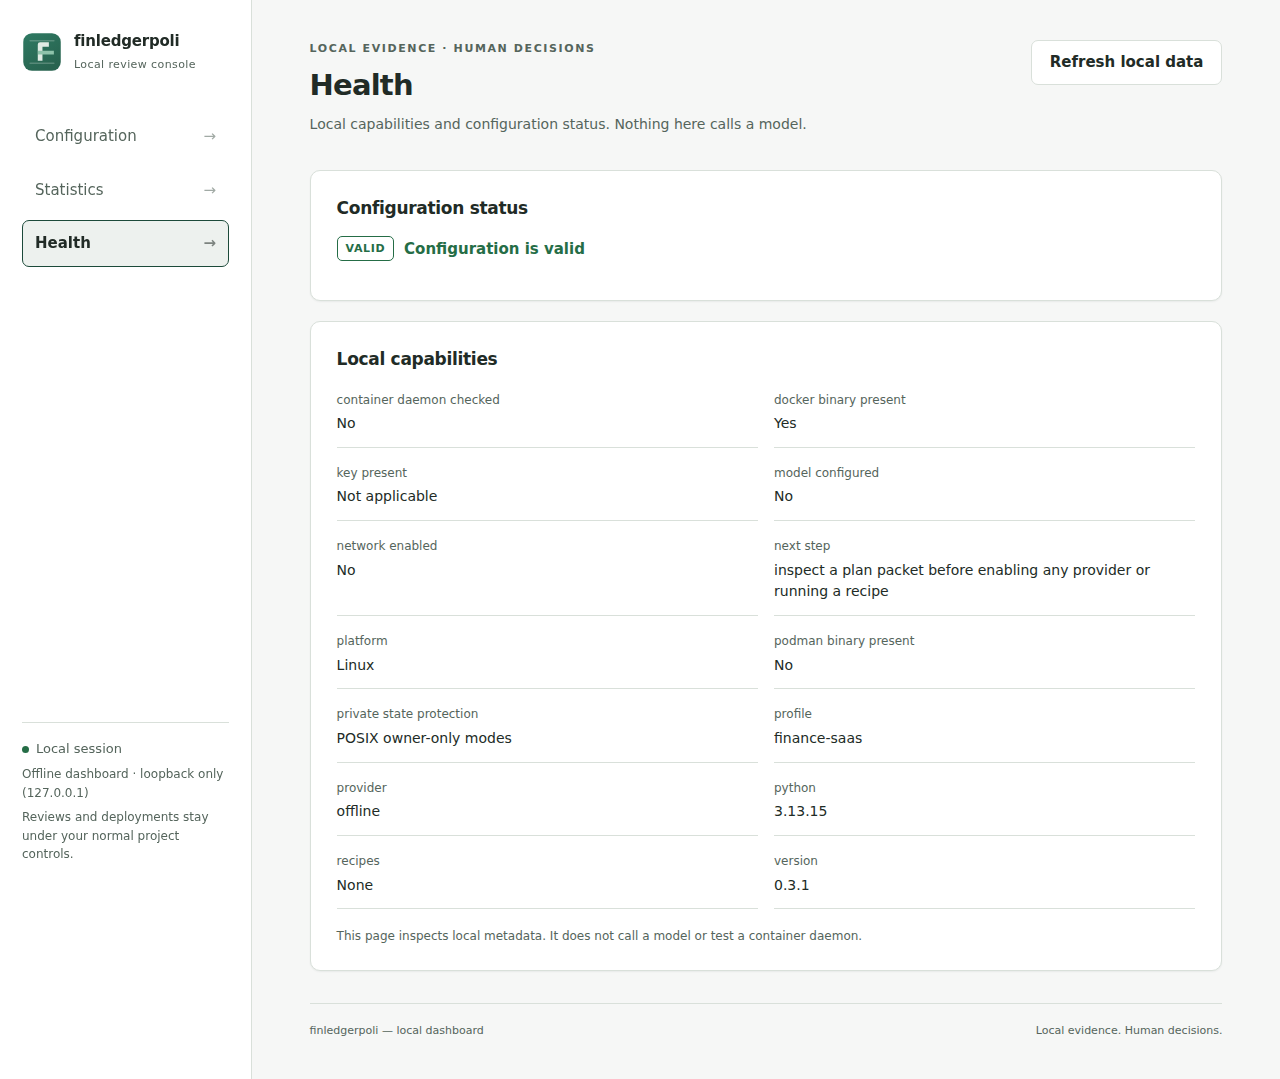
All displayed spend, tokens, findings and review activity are fictional; these light-theme screenshots use an isolated synthetic fixture and call no provider.
Preview configuration changes before explicitly confirming a save; keys are shown only as present or absent.
See recorded spend against daily and monthly limits, pending charges, checks and review activity.
Inspect local configuration and capabilities without calling a model or testing a container daemon.
Use it with AI agents
Use the portable instructions with Claude Code, Codex and Cursor: agent guide.
Point an agent at llms.txt to find the public guides.
Run finassist guide agents for offline help; your project's rules and approvals still apply.
Guides
For unattended PR validation, use the GitHub Actions check gate. It runs approved isolated checks under a pinned policy from the PR's base revision and publishes a reduced job summary. This first CI mode reports deterministic checks; policies requiring model review remain blocked.
| Goal | Guide |
|---|---|
| Configure profiles, paths and budgets | Configuration, workflow packs, examples |
| Choose a model | Providers |
| Plan, review, check and recover | Workflows, workflow plans, durable execution, auditing and readiness |
| Use the local dashboard | Dashboard |
| Automate command results | Exit codes and JSON contracts |
| Evaluate findings or manage evidence | Evaluation, research inputs |
| Integrate your coding agent | AI agents, templates, evidence-review skill |
| Adapt to your team | Fork and customize |
| Understand protection and design | Threat model, security policy, security design, design principles |
| Maintain and release a fork | Repository settings, releasing |
Safety and limits
- Advisory only. A valid report, plausible citation or matching hash does not prove a defect, correctness or professional suitability. Your project's specifications and authorized people own financial rules and approvals. Profiles guide reviews; they do not train model weights or confer professional credentials.
- Local-first, no telemetry. Offline is the default, regardless of existing keys. Uncommitted work is excluded. Remote reviews and GitHub inspection require explicit configuration and approval. Protocol compatibility tests use fake transports; not every model or service has been live-tested.
- Inspect outgoing content. Screening conservatively rejects common private, binary and sensitive formats, but cannot prove confidentiality. Inspect every outgoing request. There is no guard-bypass switch. Keep
.finassist/, keys, client data and private artifacts out of Git. - Execution needs a reviewed check. Container isolation depends on the image, daemon and host. Instructions and Python checks are not security sandboxes. Local execution requires explicit opt-in and has no OS filesystem isolation. The dashboard cannot run reviews, checks, shell commands, merges or deployments.
- Budgets are local estimates. Prices come from your configuration; limits are not provider-enforced billing caps. Unknown charges remain reserved across days and months and are not retried automatically. Missing usage is unknown, not zero. Pending charges and incomplete runs block a ready-for-review result.
- Evidence has limits. Review prerequisites grant no merge, deployment or financial authority. Local audit hashes cannot defeat a malicious rewrite of all state by the same user. Generated files need independent build verification; a green result cannot prove vulnerability absence.
- Recovery is guarded. Rollback refuses to overwrite later edits. Interrupted changes need reconciliation from the saved backup; multi-file changes and configuration saves are not atomic against other same-user writers. The local dashboard does not protect against other processes running as you.
Contribute
python -m pip install -r requirements-dev.lock
python -m pip install --no-deps --no-build-isolation -e .
python -m pytest -q
ruff check src tests scripts
finassist demo
finassist scan --repo .
Use synthetic fixtures and fake provider transports. See contributing, architecture and media reproduction. Forks must update repository links and maintainer settings. Posture badges describe repository settings; they do not establish vulnerability absence.
License
MIT licensed. See LICENSE.
1 maintainer

Metadata
1 maintainer
Release files for finledgerpoli 0.4.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | Actions |
|---|---|---|---|---|
| finledgerpoli-0.4.0.tar.gz | 2.3 MB | With provenance | Details for finledgerpoli-0.4.0.tar.gz |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Actions Reset |
|---|---|---|---|---|
| finledgerpoli-0.4.0-py3-none-any.whl | Python 3 | none | any | Details for finledgerpoli-0.4.0-py3-none-any.whl |
Total release size: 2.6 MB
Release files / finledgerpoli-0.4.0.tar.gz
| Download URL | finledgerpoli-0.4.0.tar.gz |
|---|---|
| Size | 2.3 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
9a6fc1fef0d307cb336d81cf0117293debd3e35a1fce51e0a018cb0d93d1f055
|
|
BLAKE2b-256 checksum How to use checksums |
0fa5a7c4ff3e61ef07a47368220d007d106e12d236153fb13036e13366e4b8ae
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.


PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 29, 2026.
Transparency logRelease files / finledgerpoli-0.4.0-py3-none-any.whl
| Download URL | finledgerpoli-0.4.0-py3-none-any.whl |
|---|---|
| Size | 301.1 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
f56db4445dab9e0abb5ea0010d1768f3688a0e448a1882a05a8720b0e67e9e1c
|
|
BLAKE2b-256 checksum How to use checksums |
057a268287cccb5cd3ebb3959b46a5152a00cb35159cb932eb5ae26d88212e95
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
Yes |
| Uploaded via |
twine/7.0.0 CPython/3.13.16
|
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 29, 2026.
Transparency logSecurity for finledgerpoli 0.4.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
Full provenance
All 2 files in this release have been uploaded with provenance metadata.
Attestation for finledgerpoli-0.4.0.tar.gz
PyPI Publish Attestation
PyPI verified that this artifact, at this checksum, originated from the publisher listed below.
Signed by GitHub Actions, verified by PyPI on Oct 29, 2026.
Transparency logA note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.














