
Sound static analysis and LLM reasoning, in one security agent


Frame finds vulnerabilities by following attacker data through your code, across functions, files and layers, and proves each finding with a solver instead of pattern-matching. An optional LLM layer adds recall, then exploits and fixes what was found.
Why Frame?
- Five languages: Python, JavaScript/TypeScript, Java, C# and C/C++.
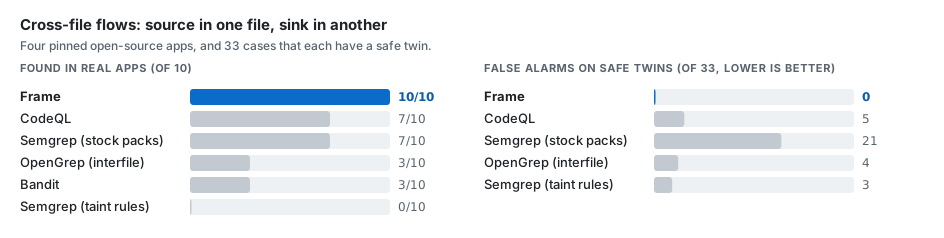
- Cross-file by default: a request that enters a controller and reaches a query three files away is one finding.
- 70+ framework packs: Flask to Spring to ASP.NET to Express, plus your own stack in one TOML file.
- Built for guardrails: scan only what changed, baseline what you accept, verify that a fix removed the bug.
- Its own separation logic engine on Z3: entailment, frame inference, bi-abduction and countermodels.
- Runs on open models, local or hosted, for detection, triage, exploitation and fixing.
Quick start
pip install "frame-security[scan]"
frame scan src/
A three-file Flask app, where the request enters in app.py and the query runs in services/orders.py:
# shop/app.py
@app.route("/orders")
def list_orders():
    customer = request.args.get("customer", "")
    return jsonify(orders.for_customer(customer))

# shop/services/orders.py
def for_customer(name):
    cur.execute("SELECT * FROM orders WHERE customer = '" + name.strip() + "'")
$ frame scan benchmarks/exemplars/quickstart --root benchmarks/exemplars/quickstart
1. [CRITICAL] 🔴 sql_injection
   Location: benchmarks/exemplars/quickstart/shop/services/orders.py:8:4
   Description: Tainted data from 'customer' flows to sql sink
   CWE: CWE-89
   Data flow: shop/app.py:11 -> shop/services/orders.py::for_customer(name)
...
Scanned 4 files: 2 findings (2 critical)
Use a placeholder query, or wrap the value in int(), and the finding goes away.
Benchmarks
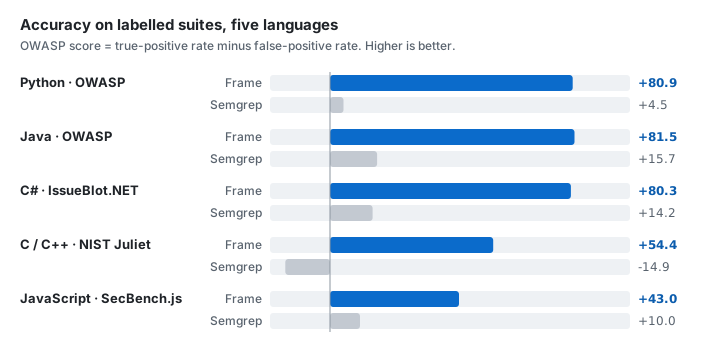
| Benchmark | What it measures | Frame | Comparison |
|---|---|---|---|
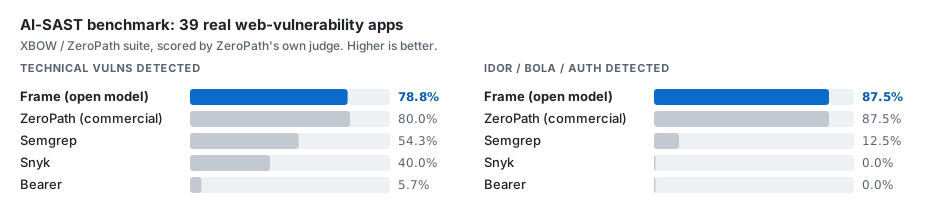
| XBOW / ZeroPath | AI-SAST on 39 web-vuln apps | detect 78.8%, FP 26.3% | ZeroPath 80% / 25%, Semgrep 54% / 45% |
| Endor Labs corpus | 193 vulns in 5 production apps | recall 0.67, precision 0.51 | Semgrep 0.52 / 0.40 |
| RealVuln IDOR/BOLA | Broken authorization, 4 real apps | 6/8 found, precision 1.00 | 0 false positives on safe controls |
| CVE-Bench | Detect, exploit, fix on 10 live CVEs | 5 / 4 / 4 of 10 | each stage verified on a live target |
| SusVibes | 181 real-CVE Python pairs | recall 0.14, precision 0.56 | Semgrep 0.06 / 0.55 |
| Cross-file exemplars | Hand-labelled precision on 4 real apps | 98% | CodeQL 95% |
Methods and every suite, including SL-COMP for the engine, are in benchmarks/README.md.
Documentation
| Usage | Scanning, GitHub Action and pre-commit hook, baselines and verify, suppressions, configuration, commands, Python API |
| Coverage | Cross-file resolution per language, supported frameworks, writing a pack, vulnerability classes |
| AI layer | Detect, triage, exploit and fix with any OpenAI-compatible model, including on-device |
| Separation logic engine | The prover under the scanner: capabilities, syntax, CLI, Python API, SL-COMP results |
| Examples | The quickstart app, a vulnerable and safe app per framework, and the cross-file comparison |
Contributing
pip install -e ".[dev]"
python -m pytest tests/ -n auto
ruff check frame tests benchmarks
CLAUDE.md is the engineering map of the codebase. To add a framework, write a pack under frame/sil/packs/data/<language>/ and a vulnerable/safe app pair under benchmarks/exemplars/frameworks/; the fixture test checks both.
License
1 maintainer

Metadata
1 maintainer
Release files for frame-security 1.0.0
For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation.
Source distribution (sdist)
| File | Size | Uploaded | Provenance | |
|---|---|---|---|---|
| frame_security-1.0.0.tar.gz | 1.1 MB | Without provenance | Details |
Built distribution (wheel)
| File | Interpreter | ABI | Platform | Reset |
|---|---|---|---|---|
| frame_security-1.0.0-py3-none-any.whl | Python 3 | none | any | Details |
Total release size: 2.0 MB
Release files / frame_security-1.0.0.tar.gz
| Download URL | frame_security-1.0.0.tar.gz |
|---|---|
| Size | 1.1 MB |
| Tags | Source |
|
SHA-256 checksum How to use checksums |
59626968479c4f972ba8b44b0b863e48afa498b189040011f6585b1b8d05749a
|
|
BLAKE2b-256 checksum How to use checksums |
4a479ec52a19d68375462d00c1ba01b9197a1076fc2a7075b73b54e6ad36b6eb
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.7
|
Release files / frame_security-1.0.0-py3-none-any.whl
| Download URL | frame_security-1.0.0-py3-none-any.whl |
|---|---|
| Size | 907.0 kB |
| Tags | Python 3 |
|
SHA-256 checksum How to use checksums |
7b62b8a1e67044f00f949285ec876c926094b352949fd221edaed5b81115d797
|
|
BLAKE2b-256 checksum How to use checksums |
ec2e4e3eb37e42c83cb2324d2c3a7dde5a0a6cd8da7c6e7f1f7ad3872f584a57
|
| Upload date | |
|
Uploaded using Trusted Publishing? What is trusted publishing? |
No |
| Uploaded via |
twine/7.0.0 CPython/3.13.7
|
Security for frame-security 1.0.0
Provenance
Provenance describes where a file came from. On PyPI, provenance is shared via attestations, which provide a verifiable record of the build or publishing details. View details, limitations and caveats.
No provenance found
None of the files in this release were uploaded with provenance metadata.
A note on package security
PyPI is a repository for distributing packages, not a service for auditing them. While third-party security researchers and our staff do their best to detect and remove malicious packages, PyPI cannot guarantee the quality, security or suitability of any given package.
To learn more about protecting yourself from malicious actors, visit our package security documentation.













